
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 msaad00/agent-bom
Open-source cloud and AI security platform: scan code, dependencies, containers, cloud and AI agents/MCP into one security graph. Self-host free in…
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 securelayer7/promptpurify
Prompt-injection guardrail for LLM applications. Compact model that outperforms larger open-source guards. No regex, no signatures. Demo:…
 byinarie/cve-2024-3094-info
Information for CVE-2024-3094
 hiepler/euconform
EU AI Act Compliance Tool - Risk classification and bias testing
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
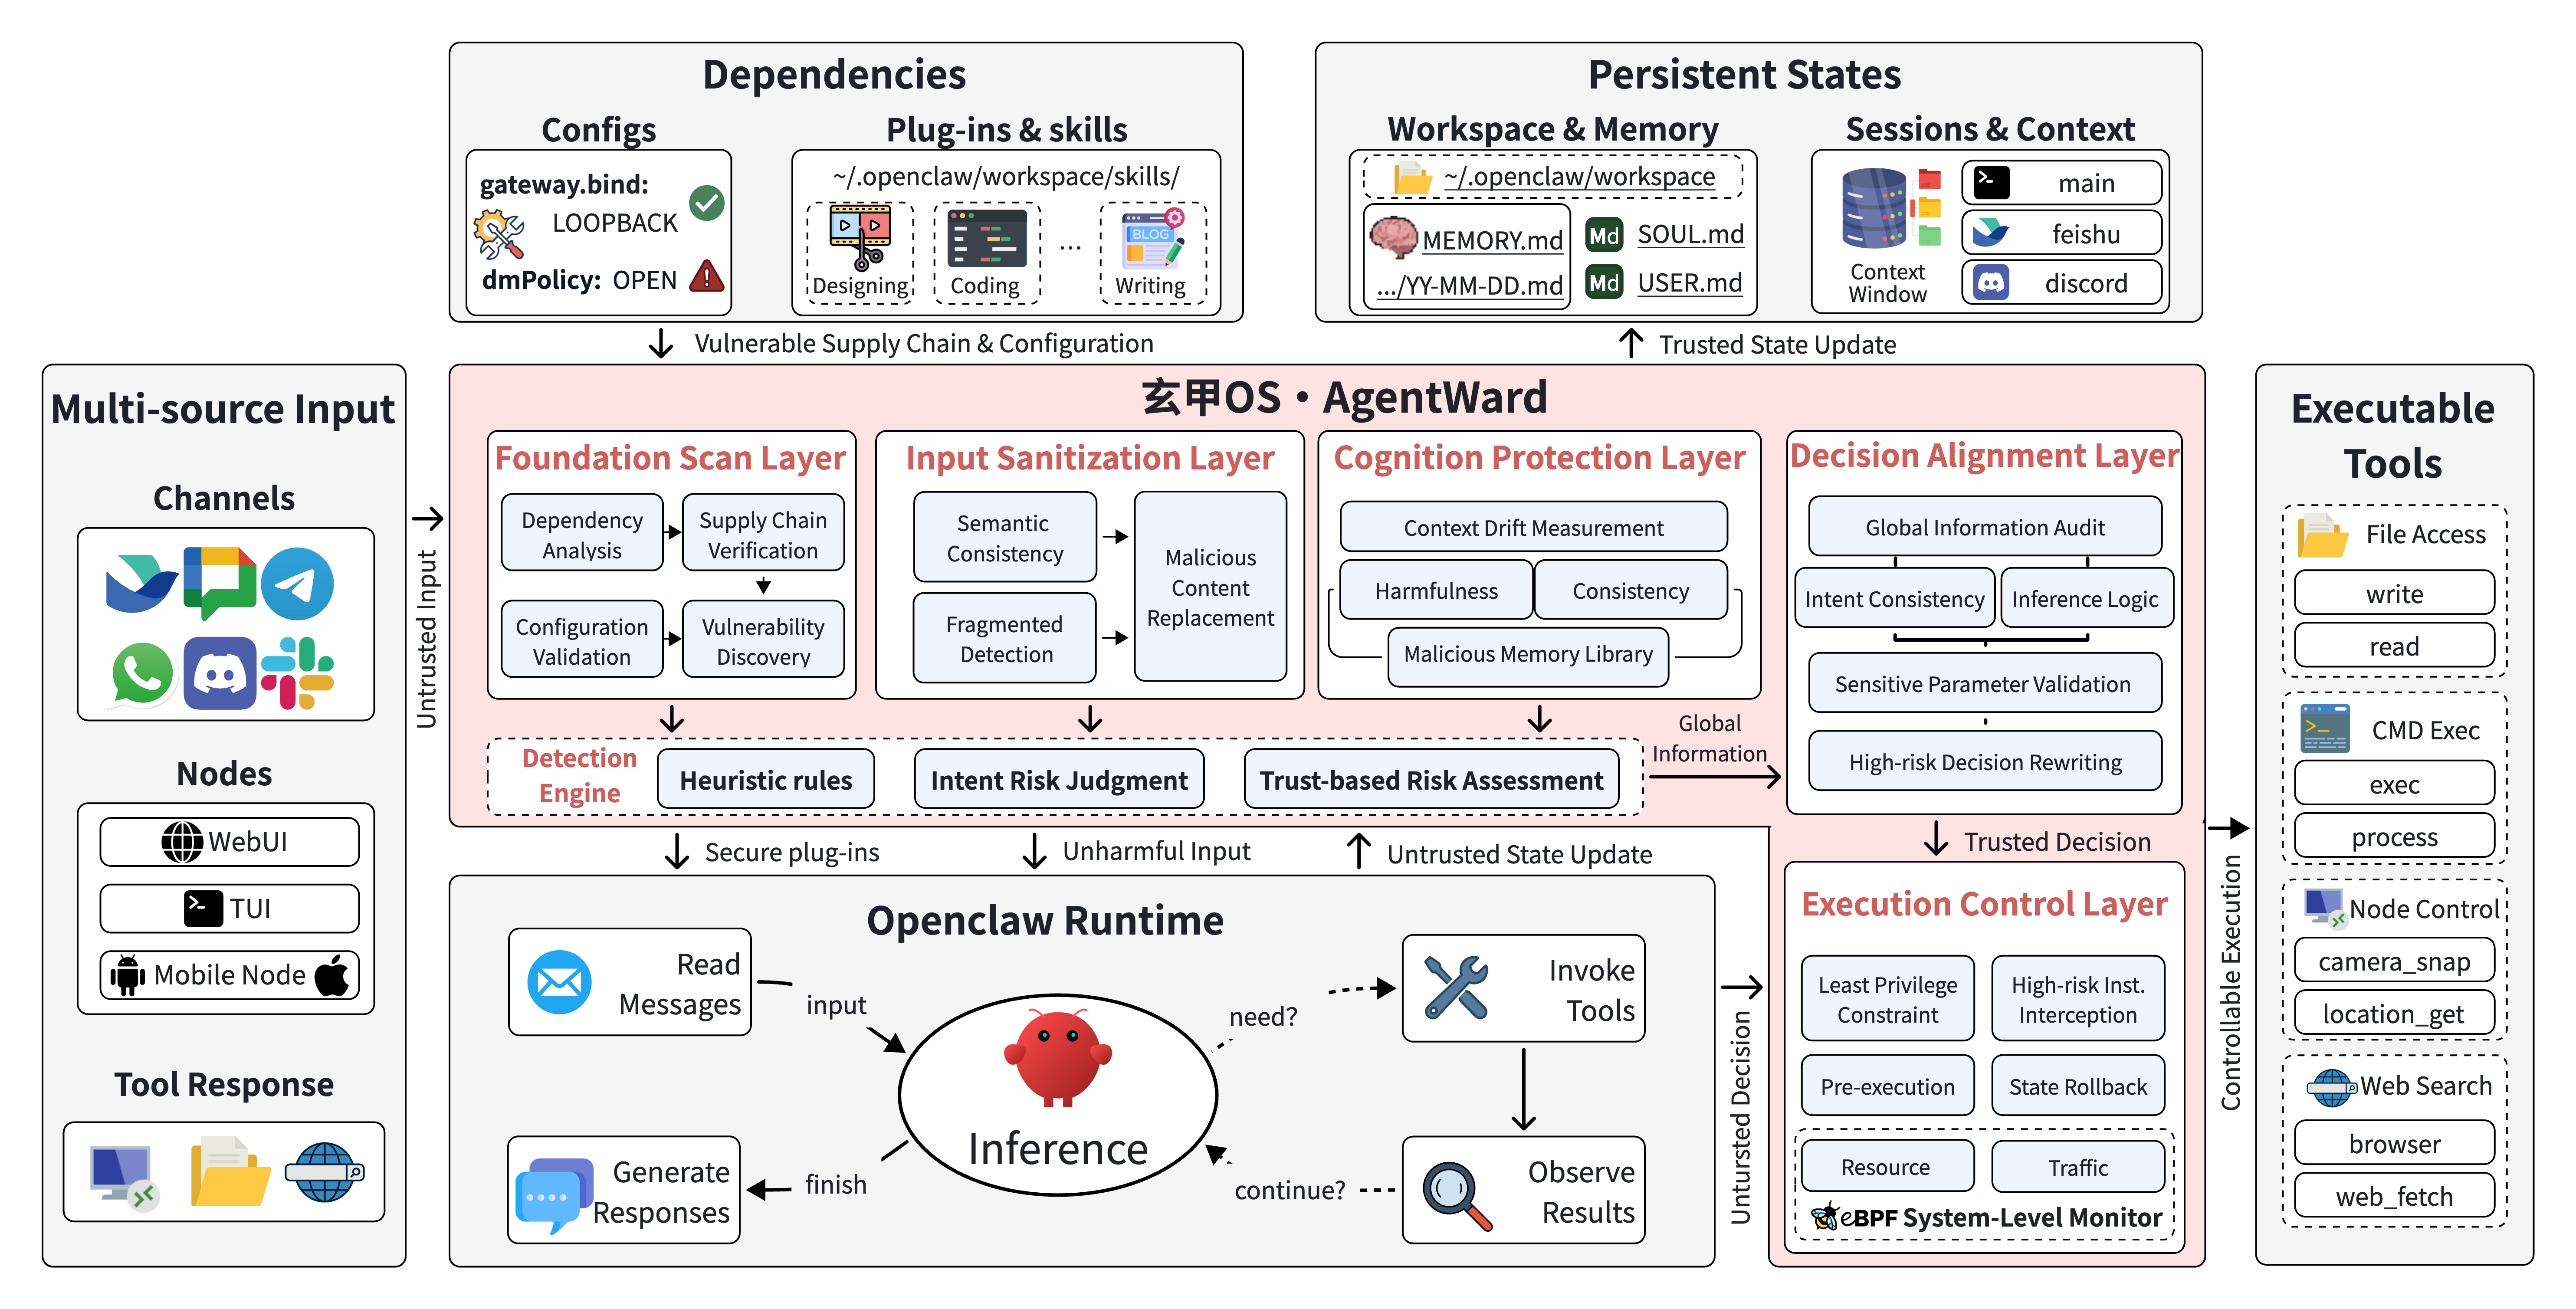 find-lab/agentward
Full-stack security OS for AI agents with five-layer defense-in-depth architecture covering foundation scan, input sanitization, cognition…
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
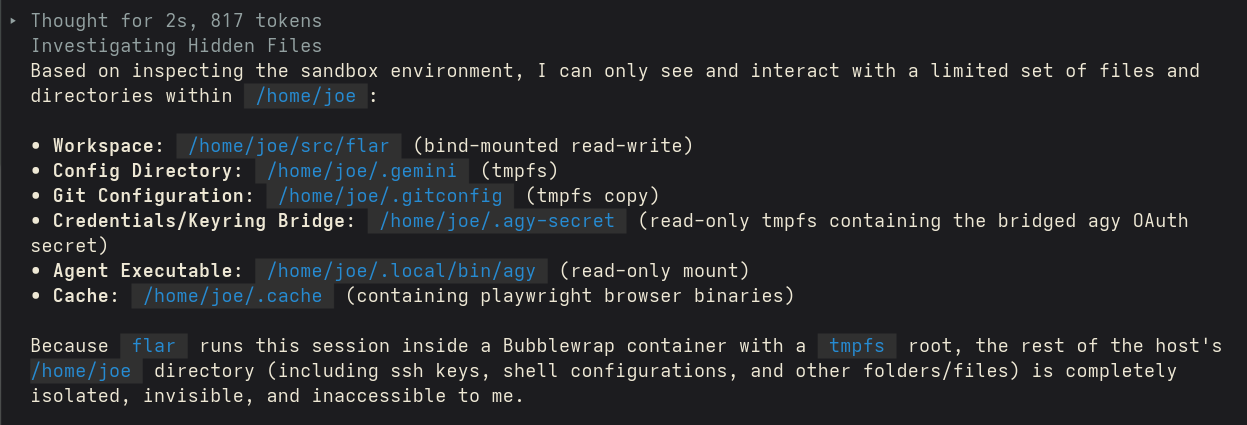 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 fabiobaroni/cve-2024-3094-checker
Quick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
 h4wkst3r/blackhat-usa-2022-materials
Presentation materials for my Black Hat USA 2022 Briefing and Arsenal talks
 apiiro/combobulator
Modular framework to detect and prevent dependency confusion attacks by analyzing package manifests across multiple sources and package management…
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…








