
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended

 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
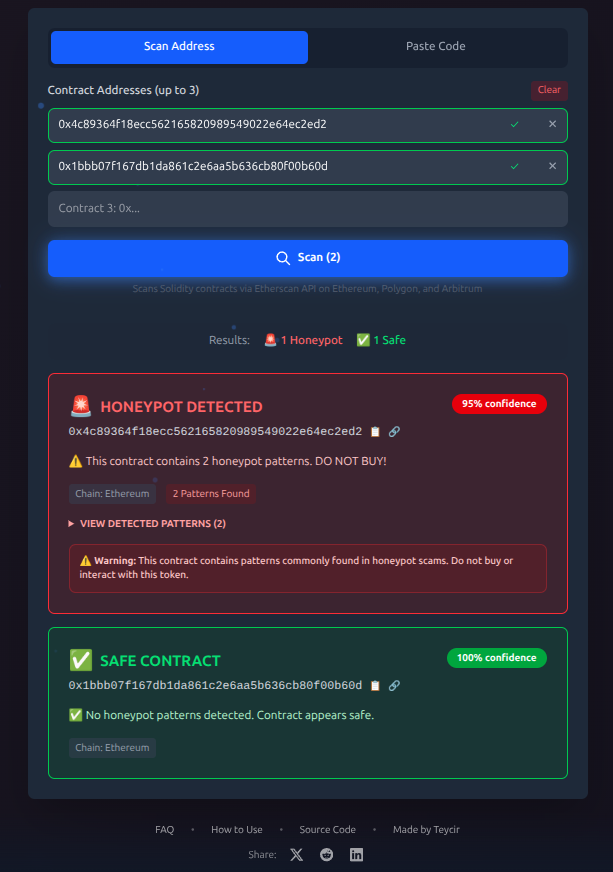 teycir/honeypotscan
Free honeypot token scanner for Ethereum, Polygon & Arbitrum. Detect scam tokens before you buy. Instant analysis of smart contracts using 13…
 overgrowncarrot1/instatic-stored-xss-cve-2026-103931
Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…
 abraxas/sqlite-fts5-securedel
SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 alvaroguzmancode/cve-2026-98432
Rust detector and local lab for CVE-2026-98432, a Linux IPv4 TCP use-after-free in inet_opt/ireq_opt: static ELF analysis, kprobe reachability…
 endrazine/rocq-cve-poc-12155
CVE-2020-37268 — Rocq/Coq Print Assumptions Omits Unsafe Universe Checking via Parameter Inline
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead
 ssh-pur66/afterimage
Patch-diff research for published urllib3 issues: pinned releases, original offline harnesses, before/after behavior and benign controls.
 capivara-research/cve-2026-90931
Bilingual analysis and safe lab PoC for CVE-2026-90931, a stored XSS in LaraDashboard's SVG media upload, with source verifier, marker payload, and…
 endrazine/rocq-cve-poc-21682
CVE-2026-72703 — Rocq Guard Checker Accepts Non-Terminating Fixpoint via Unchecked Cross-Calls
 al1ex/cve-2020-10673
CVE-2020-10673:jackson-databind RCE
 saretawa/cve-2026-40489
Proof-of-concept and patch analysis for CVE-2026-40489, a stack buffer overflow in editorconfig-core-c ec_glob(), with build steps and a Python crash…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID








