
 #1
Tools for examining malware binaries and code without executing them (e.g., disassemblers, unpackers).
Kitploit recommended

 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
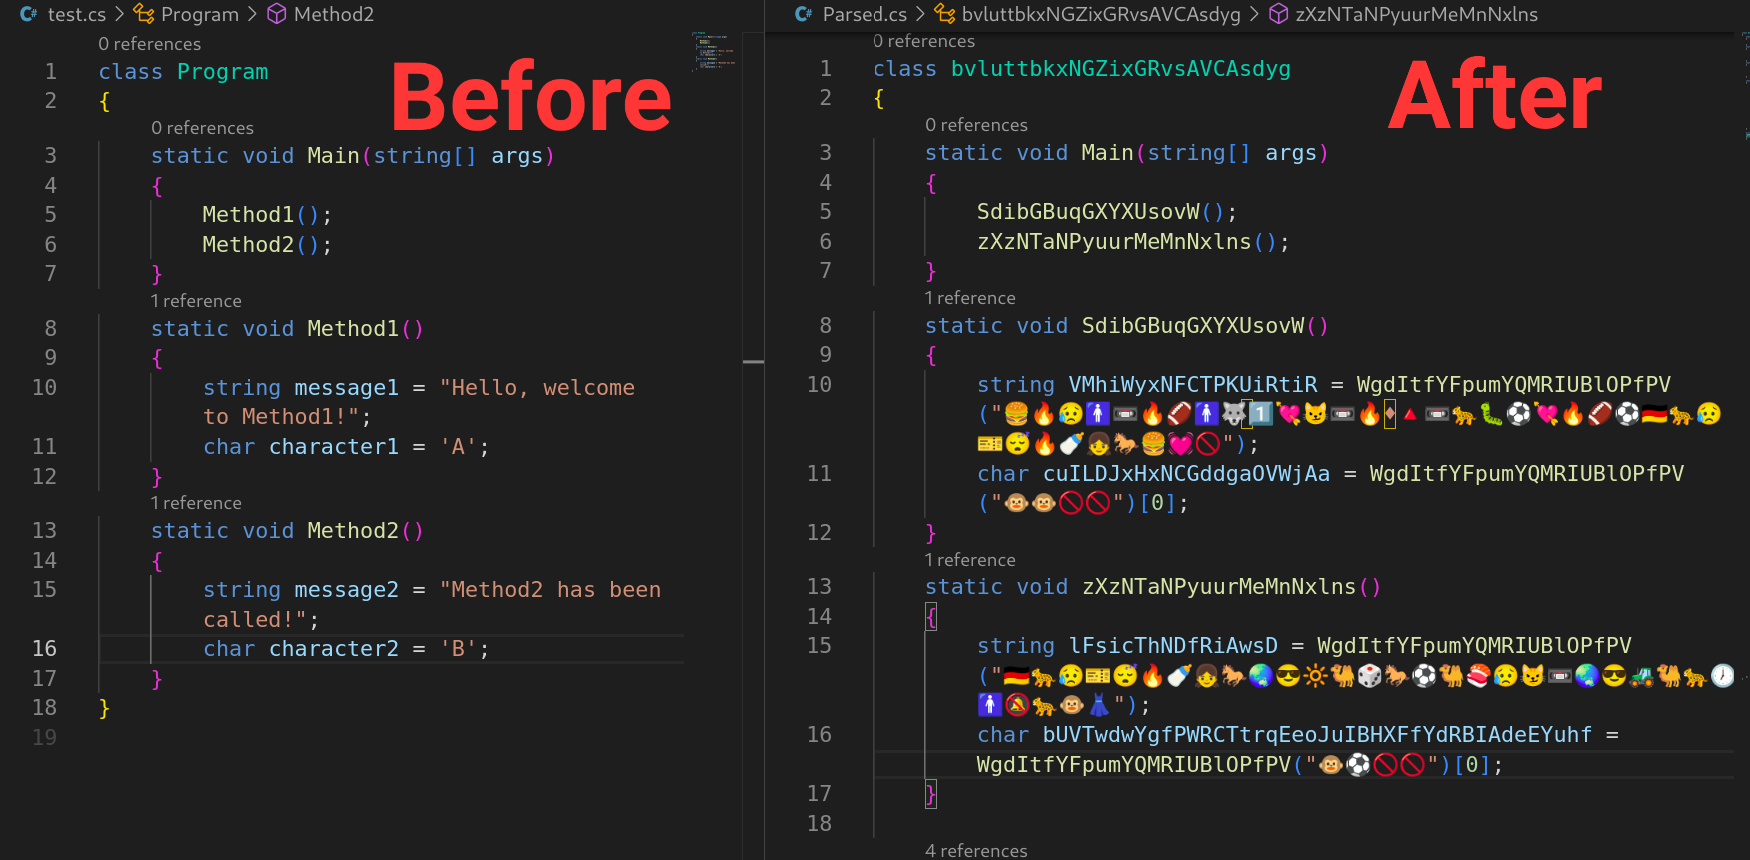 tomiwa-ot/emojify
C# source-code obfuscator that replaces character and string literals with emojis and randomizes class, interface, method, and variable names using…
 federiconbaez/cortex9-jumpserver-yaml-jinja-sandbox-model
Offline educational model of CVE-2026-31864 (JumpServer YAML Jinja sandbox)
 abtonc/next-cve-2025-66478
Scans local projects for CVE-2025-66478 vulnerability and reports affected instances without fixing them.
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 borewit/svg-sanitizer
Java library that sanitizes SVG files by stripping JavaScript, inline event handlers, and script tags while blocking external resource loading to…
 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 t3ft3lb/2026-100daysofyara
Writing and sharing one YARA rule daily for 100 days
 al1ex/cve-2019-12814
CVE-2019-12814:Jackson JDOM XSLTransformer Gadget
 farhadalimohammadi-dir/vulnrepro-benchmark
Benchmark measuring AI models' ability to detect vulnerabilities in source code via real bug bounty cases with balanced recall and false-positive…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 bitnesswise/jquery-prototype-pollution-fix
A fix for CVE-2019-11358 (prototype pollution in jquery)
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 rustynoob-619/100-days-of-yara-2026
The 100 Days of YARA Challenge to write YARA rules consistently








