
 #1
Tools and libraries for automating security tasks, workflows, and custom tool development.
Kitploit recommended

 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
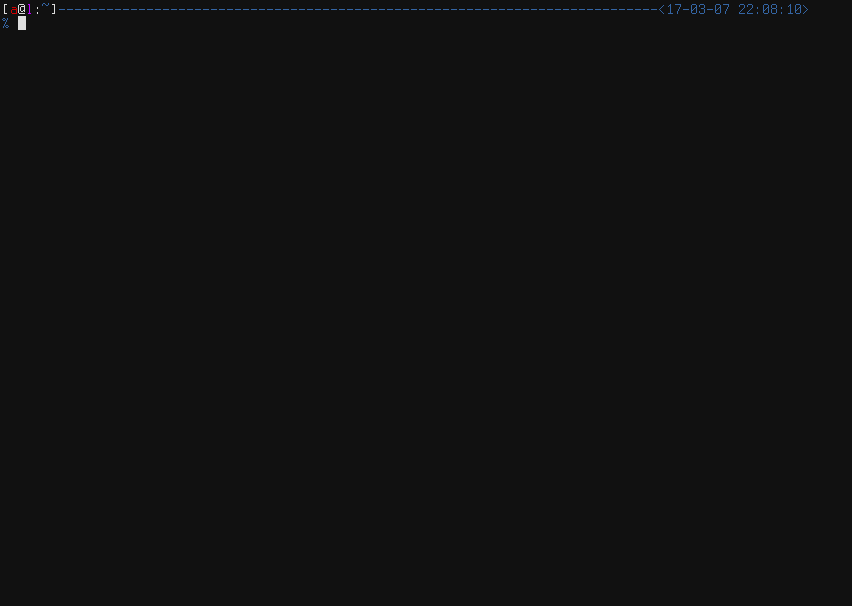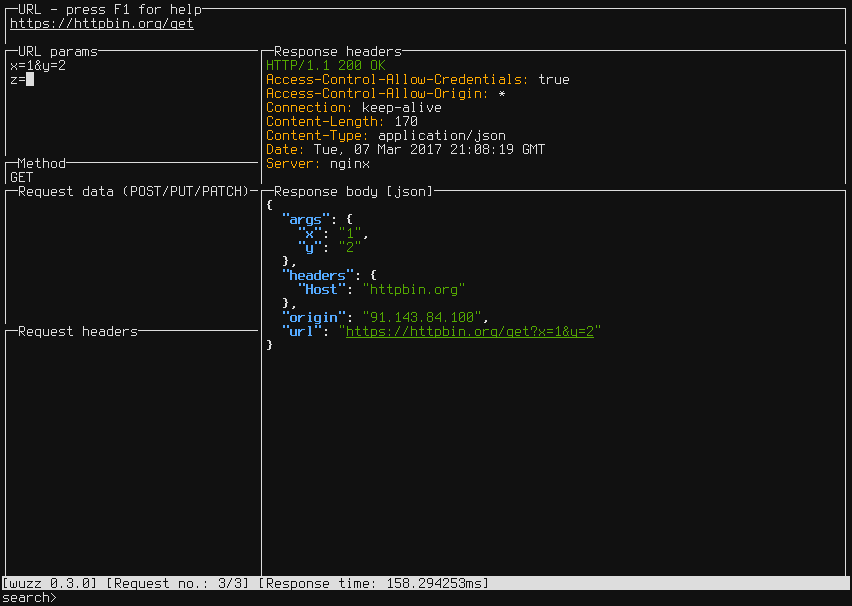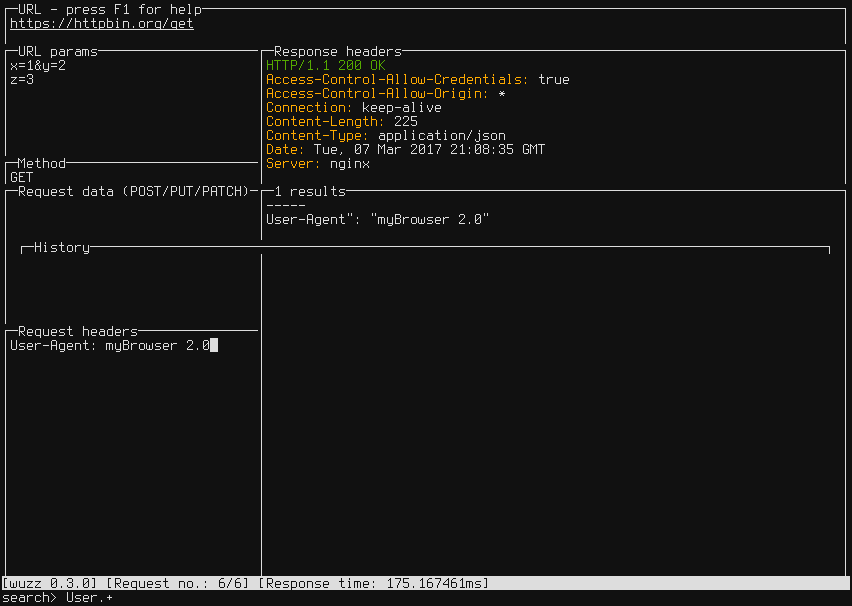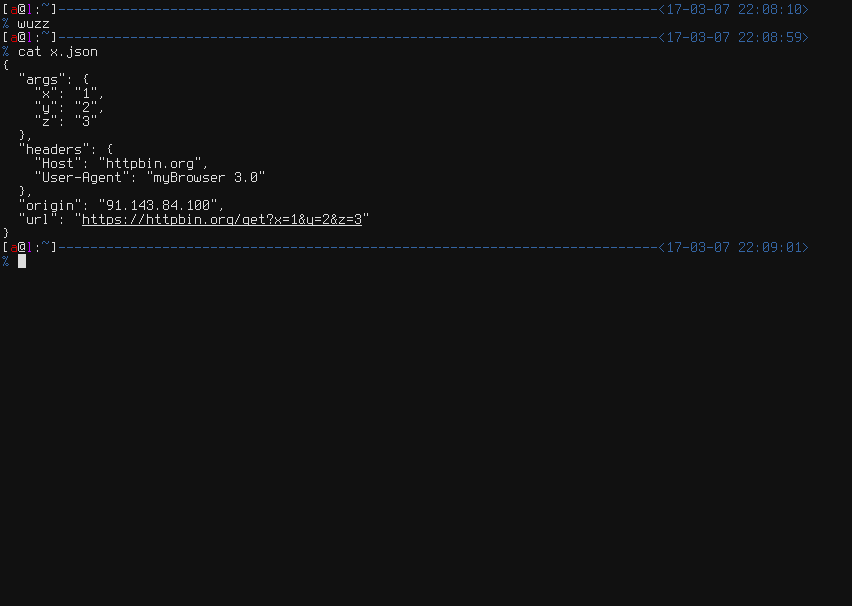 asciimoo/wuzz
Interactive cli tool for HTTP inspection
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
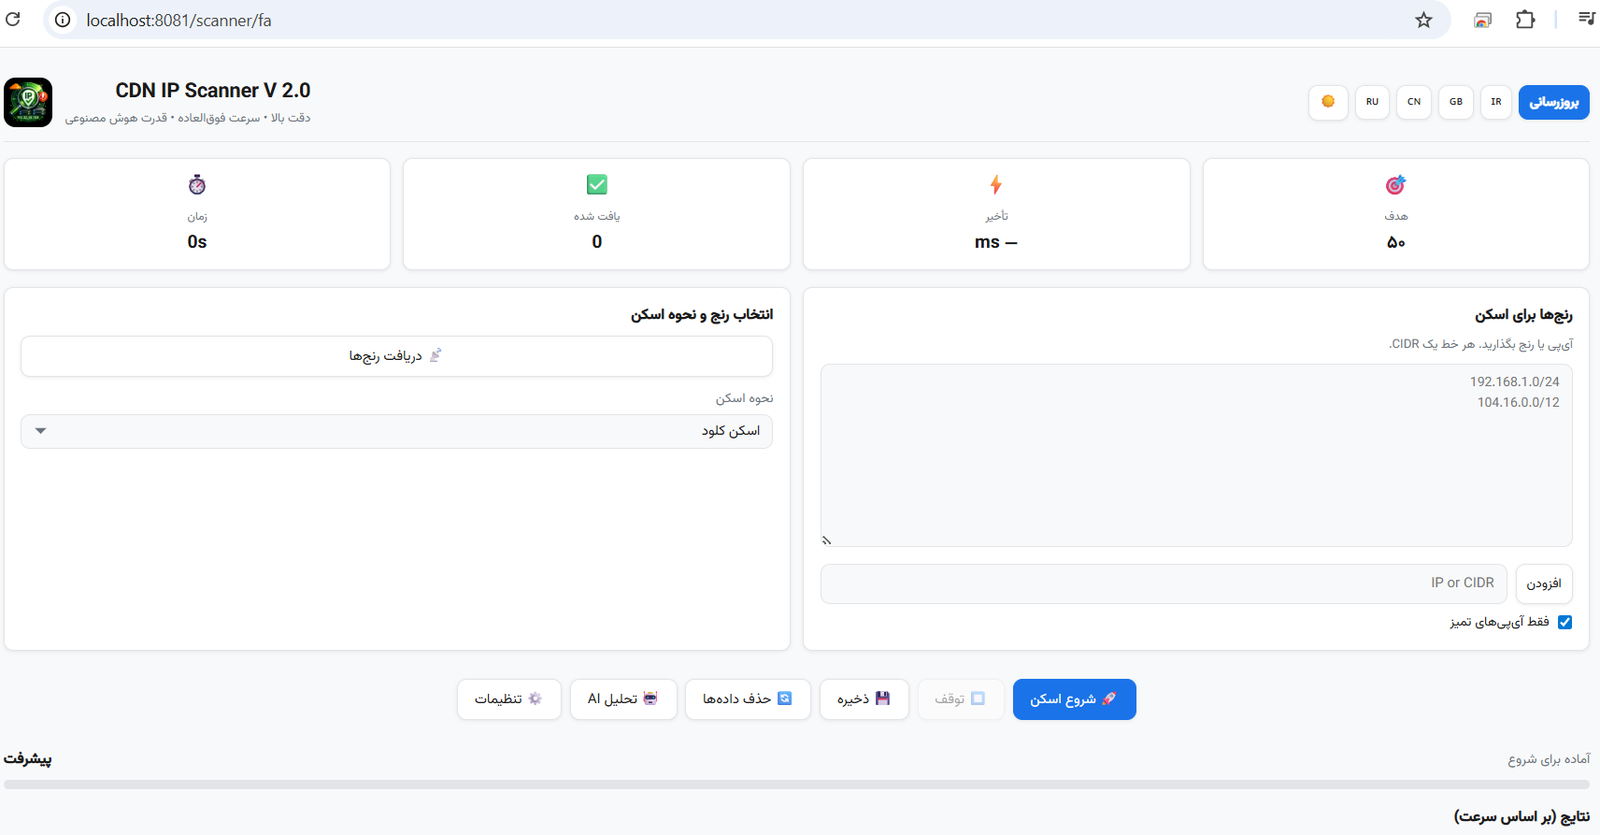 shahinst/cdn-ip-scanner
Web-based scanner that discovers fast, low-latency CDN IP addresses from Cloudflare, Fastly and other providers using multi-threaded 5-attempt…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
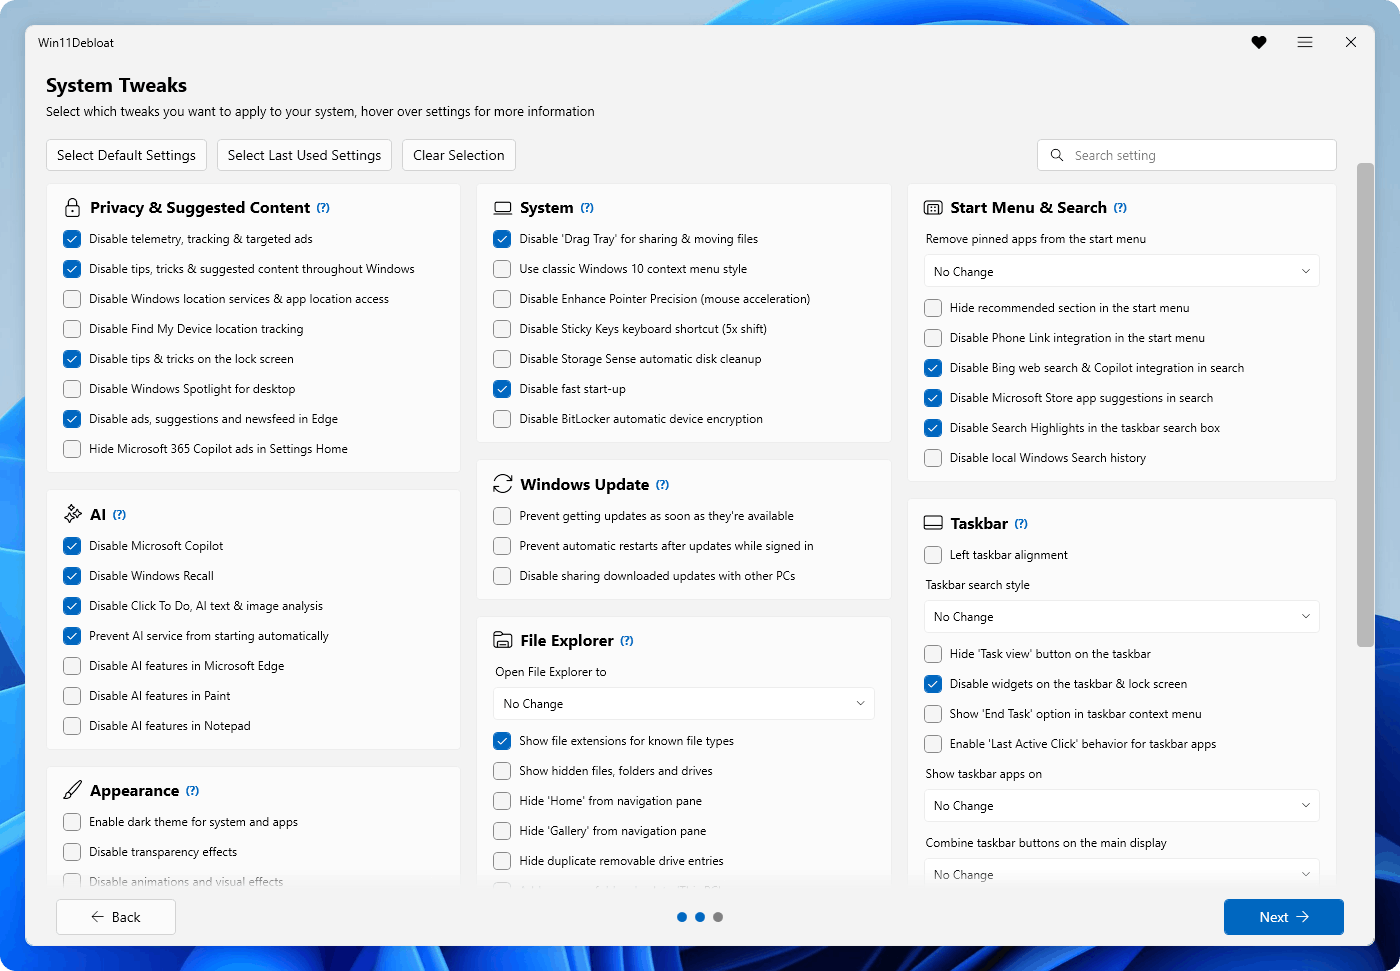 raphire/win11debloat
A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
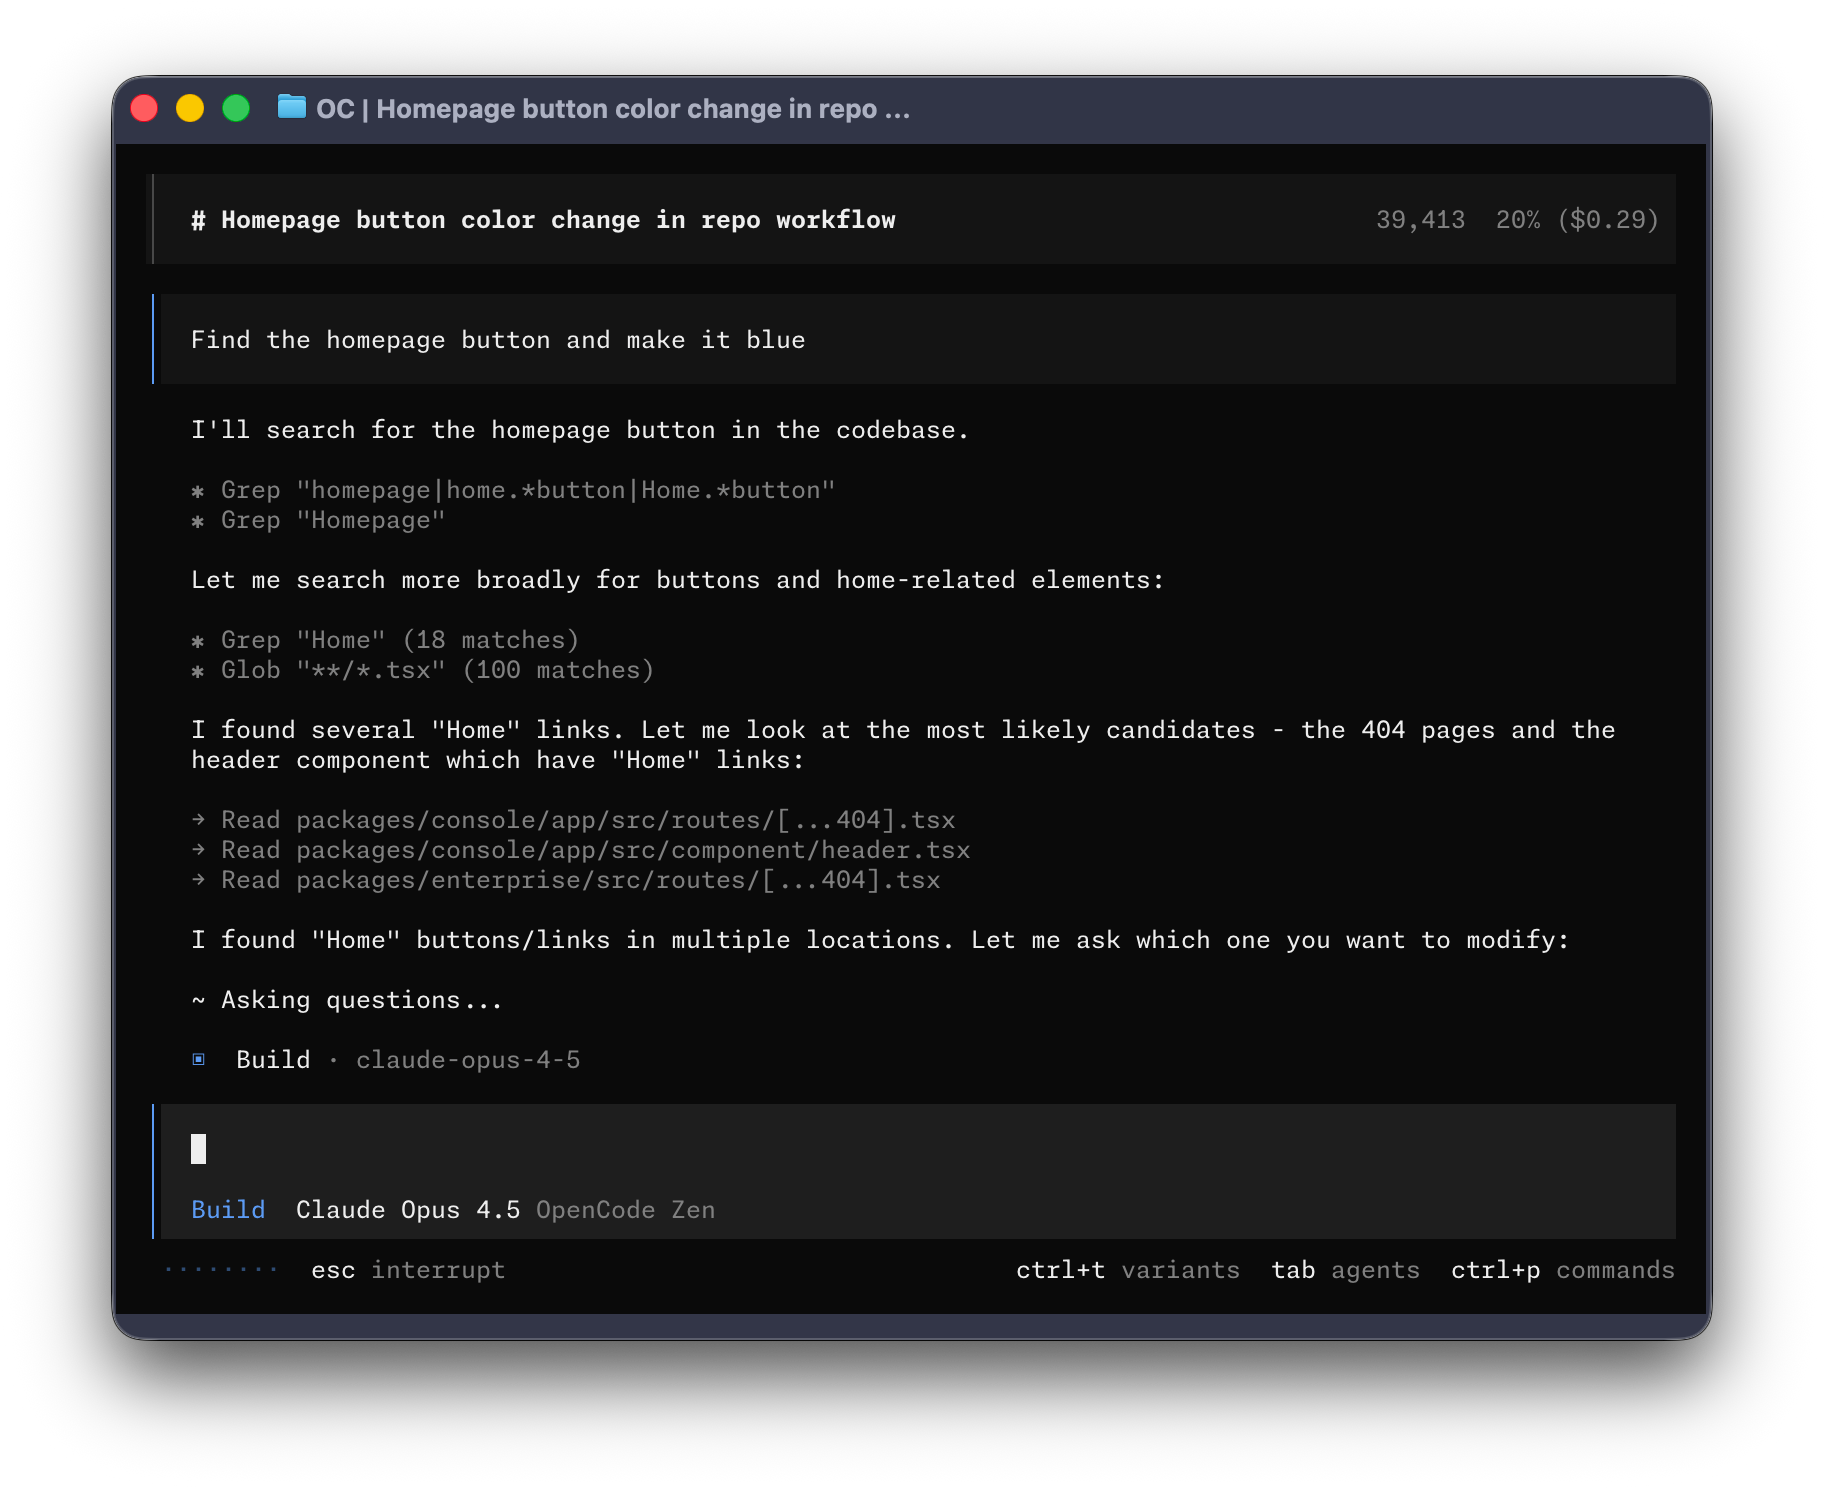 anomalyco/opencode
The open source coding agent.
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
six2dez/reconftwreconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…





