#1
Tools and libraries for automating security tasks, workflows, and custom tool development.
Kitploit recommended
 mrgoofydev/zx-ddos
Python-based DDoS stress testing tool for educational and authorized network security evaluation, supporting configurable workers and request counts.
 elsanose01/cve-2021-43798-grafana-path-traversal-tester
Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.
 gmh5225/evmbench-certora-agent-harness
Iterative agent harness that uses LLMs and Certora Prover to generate and refine smart-contract CVL specs, feeding verifier output back until success…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 google/artemis
Natural-language Android automation agent that drives real devices via ADB, captures Logcat and screenshots, and exposes an MCP server for AI IDEs…
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 gmh5225/f31
Tool for hiding Kali Linux on the network
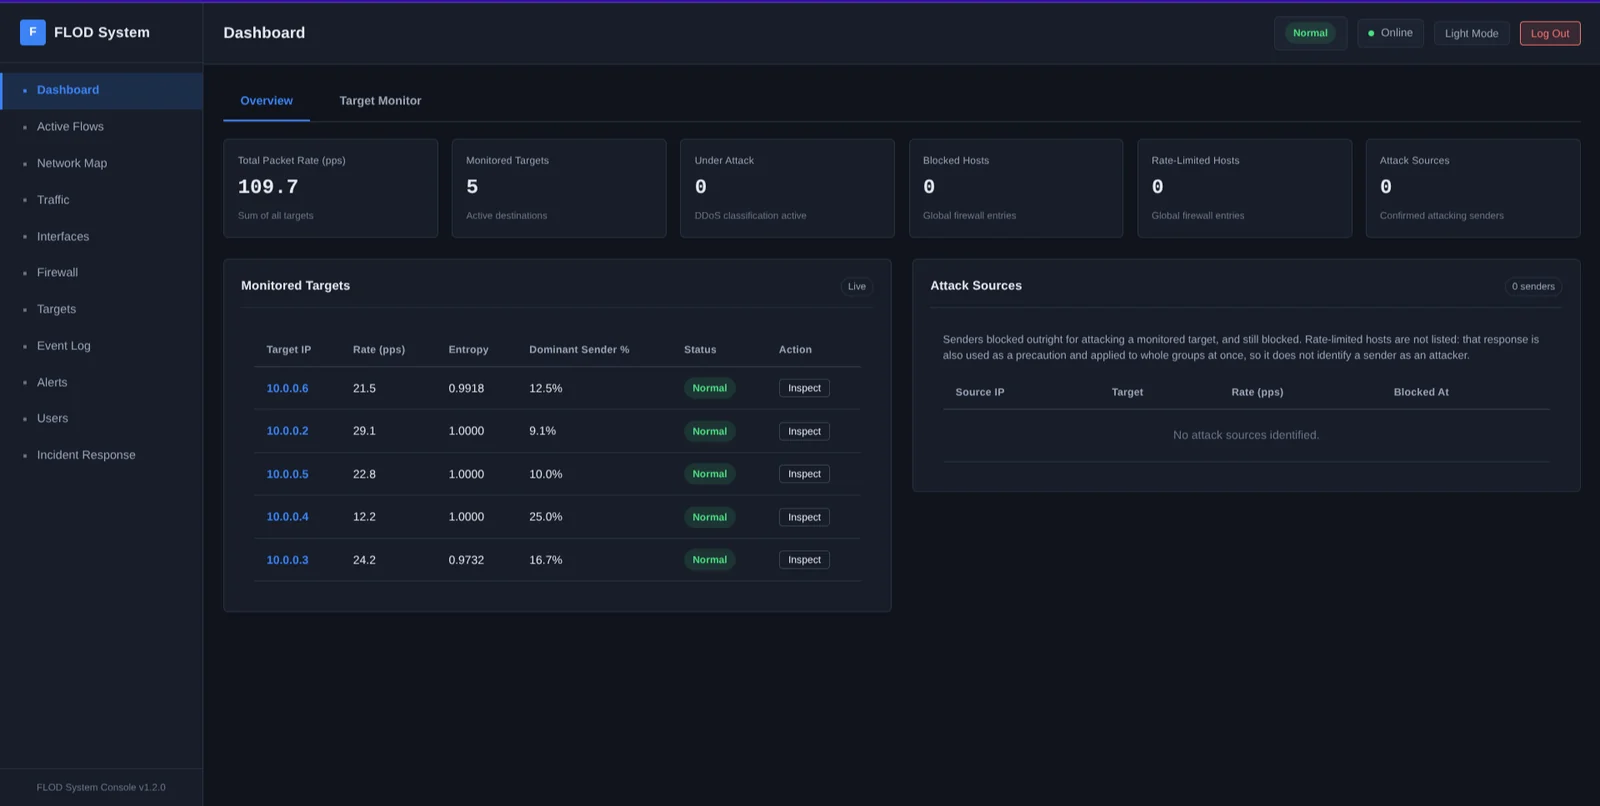 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 panniantong/agent-reach
Give your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 murrez/cve-2026-12793
Python PoC scanner and exploit for CVE-2026-12793, an unauthenticated privilege escalation in JetFormBuilder <=3.6.2 that creates WordPress admin…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
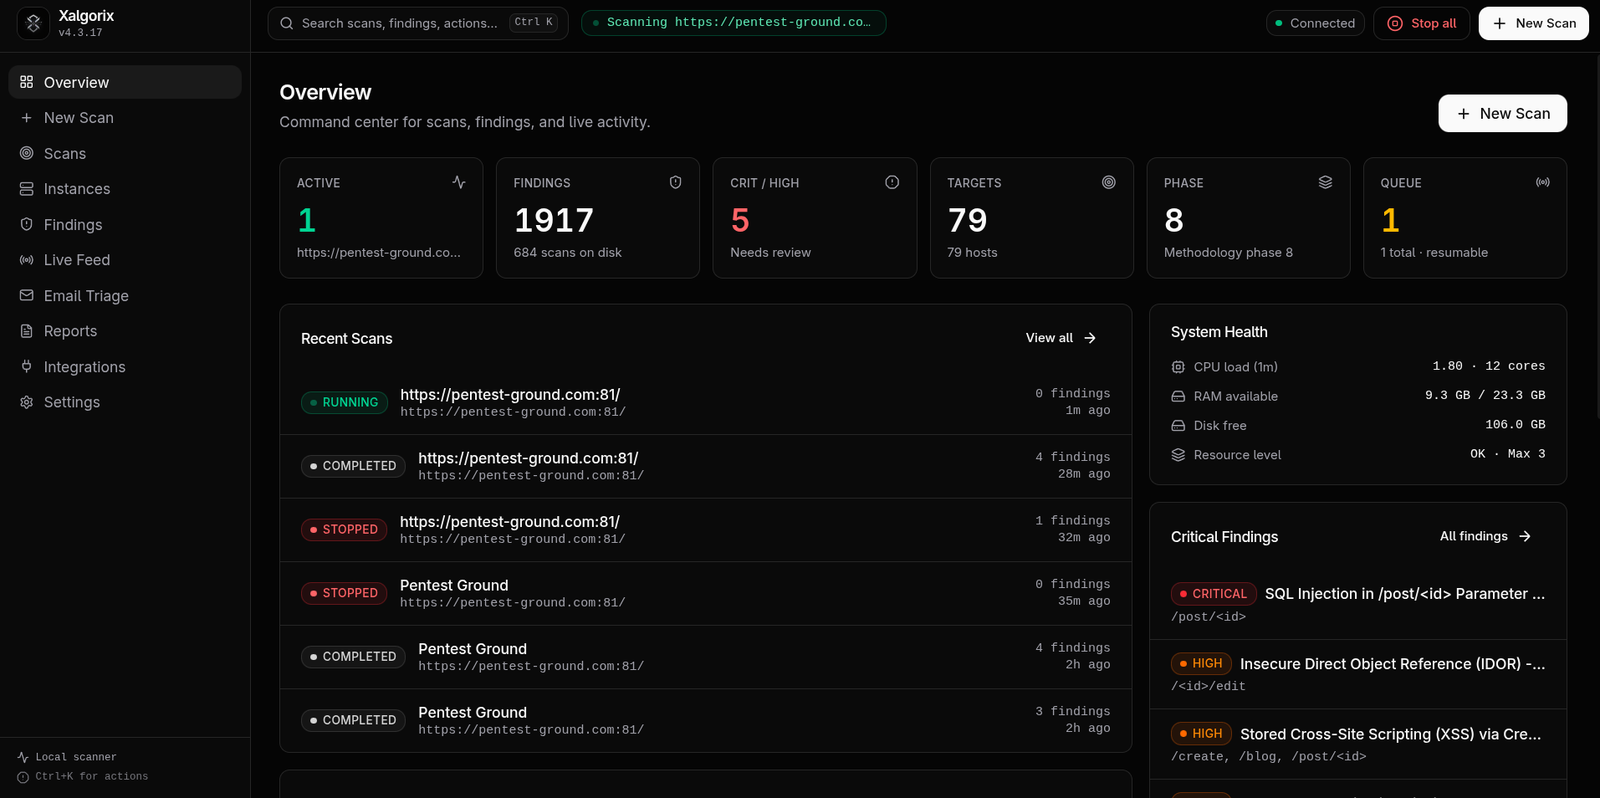 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 runewardd/runeward
Governed execution cells for AI agents.
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…