
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Reverse Engineering

Tools for decompiling, disassembling, and understanding malware internals and complex binaries.

Kitploit recommended
Top tools

10 selected
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1k6h 1m ago
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5k5h 31m ago
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4k3 days ago
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1k1 day ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k9 days ago
ImHex preview#6

ImHex

GitHubwerwolv/imhex
54.4k29 days ago
angr preview#7

angr

GitHubangr/angr
9.0k1 day ago
unicorn preview#8

unicorn

GitHubunicorn-engine/unicorn
9.2k8 months ago
capstone preview#9

capstone

GitHubcapstone-engine/capstone
8.9k2 days ago
keystone preview#10

keystone

GitHubkeystone-engine/keystone
2.7k3 months ago
NewestRelevanceMost popularRecently updated
1881 results
umbra preview

umbra

GitHubymsniper/umbra

External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
memory-forensicsexploitationreverse-engineering+1
181 month ago
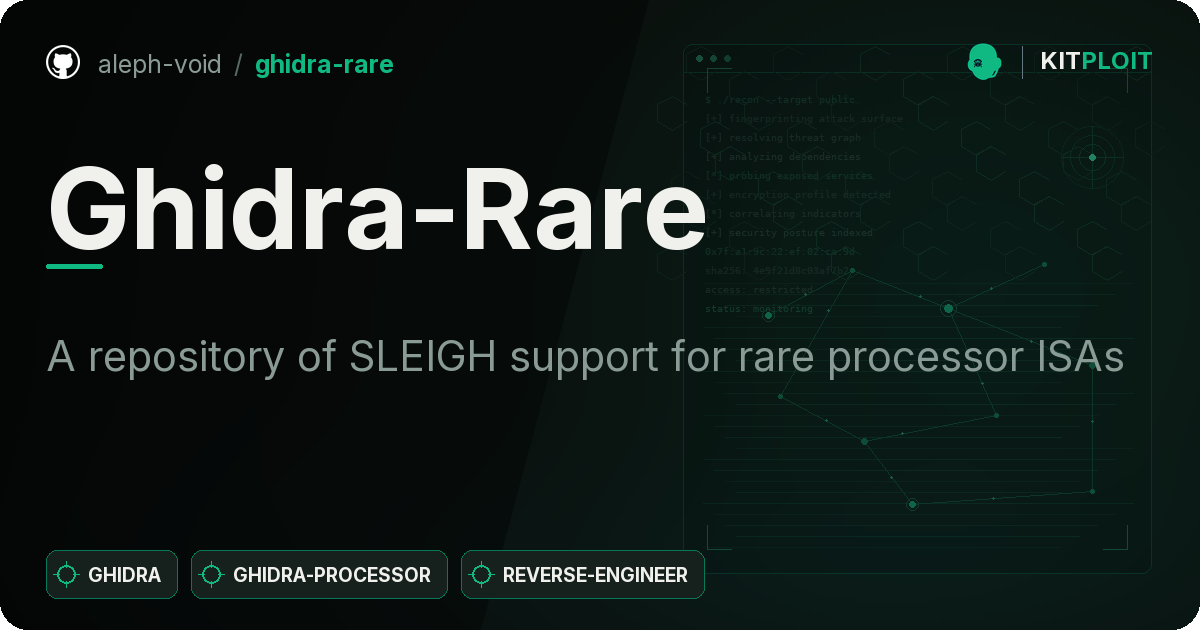
http-breakout-proxy preview

http-breakout-proxy

GitHubjbsouthe/http-breakout-proxy

HTTP Proxy Analysis for reverse engineering protocol communication
web-proxies-interceptionreverse-engineeringscripting-automation+5
6311 months ago
Ghidra-Rare preview

Ghidra-Rare

GitHubaleph-void/ghidra-rare

A repository of SLEIGH support for rare processor ISAs

embedded-systems-securitystatic-analysisreverse-engineering+4
212 days ago
pythia preview

pythia

GitHubnccgroup/pythia

A tool to extract RTTI information from Delphi executables, written in pure Python
reverse-engineeringmalware-analysisbinary-analysis
247 years ago
EUVA preview

EUVA

GitHubeuva-project/euva

A lightweight hex editor and decompiler to solve your binary file analysis problems.

static-analysisreverse-engineeringdebuggers+5
443 months ago
WhacAMole preview

WhacAMole

GitHubignacioj/whacamole

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
ioc-managementdynamic-analysis-sandboxingmemory-forensics+9
452 years ago
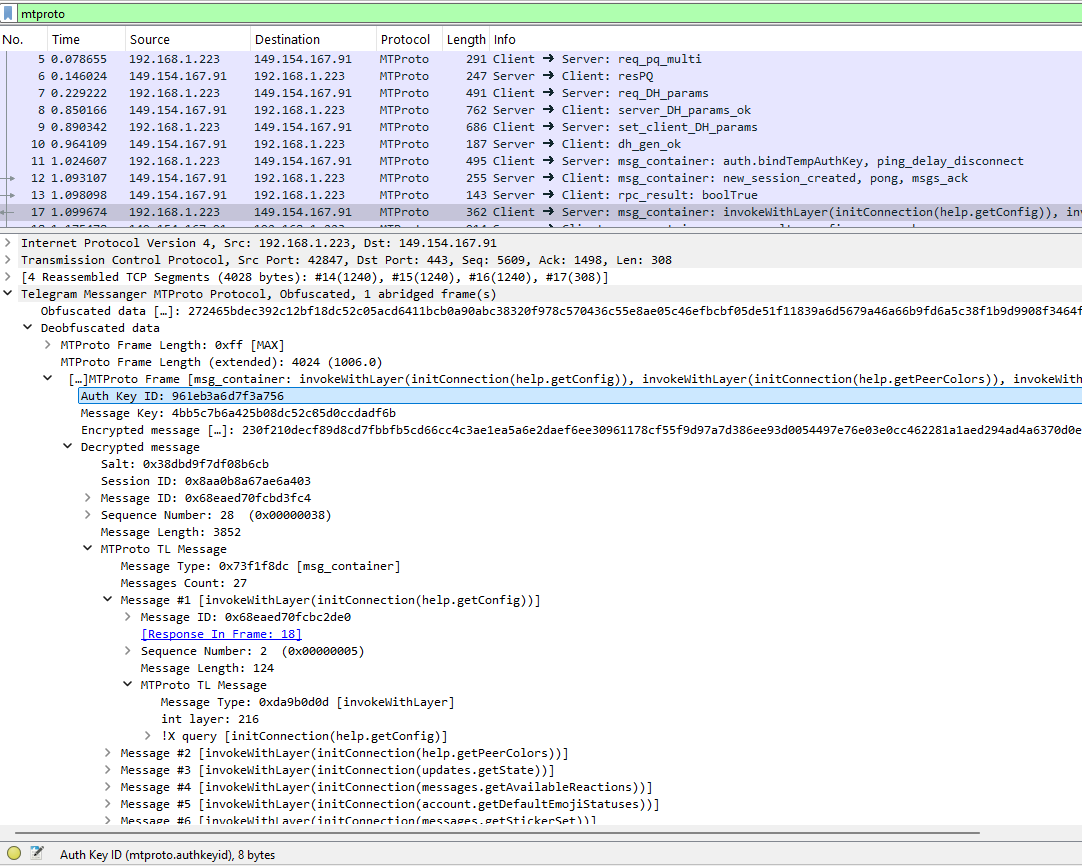
mtproto-dissector preview

mtproto-dissector

GitHubtomer8007/mtproto-dissector

Wireshark plugin for dissecting the Telegram protocol

packet-sniffing-analysisencryption-decryption-toolsreverse-engineering+2
407 months ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker
android-securityreverse-engineeringinformation-gathering+3
282 years ago
luadec-tplink preview

luadec-tplink

GitHubsuperkhung/luadec-tplink

Modified luadec version to decompile TP-Link Archer C7 LUA firmware.

embedded-systems-securitystatic-analysisiot-security+4
336 years ago
sony-vp-extract preview

sony-vp-extract

GitHubhelgesverre/sony-vp-extract

Decrypt and extract voice guidance MP3 prompts from Sony WH-1000XM4 encrypted voice packs. AES key extracted via Bluetooth firmware dump of the…
embedded-systems-securitybluetooth-securityencryption-decryption-tools+5
254 months ago
readable-thrift preview

readable-thrift

GitHubnccgroup/readable-thrift

Human-friendly Thrift encoder/decoder

web-proxies-interceptionreverse-engineeringweb-application-exploitation+2
244 years ago
drvtrace preview

drvtrace

GitHubeversinc33/drvtrace

WinDbg plugin to trace module transitions from a debugged driver.
reverse-engineeringdebuggersbinary-analysis
5410 months ago
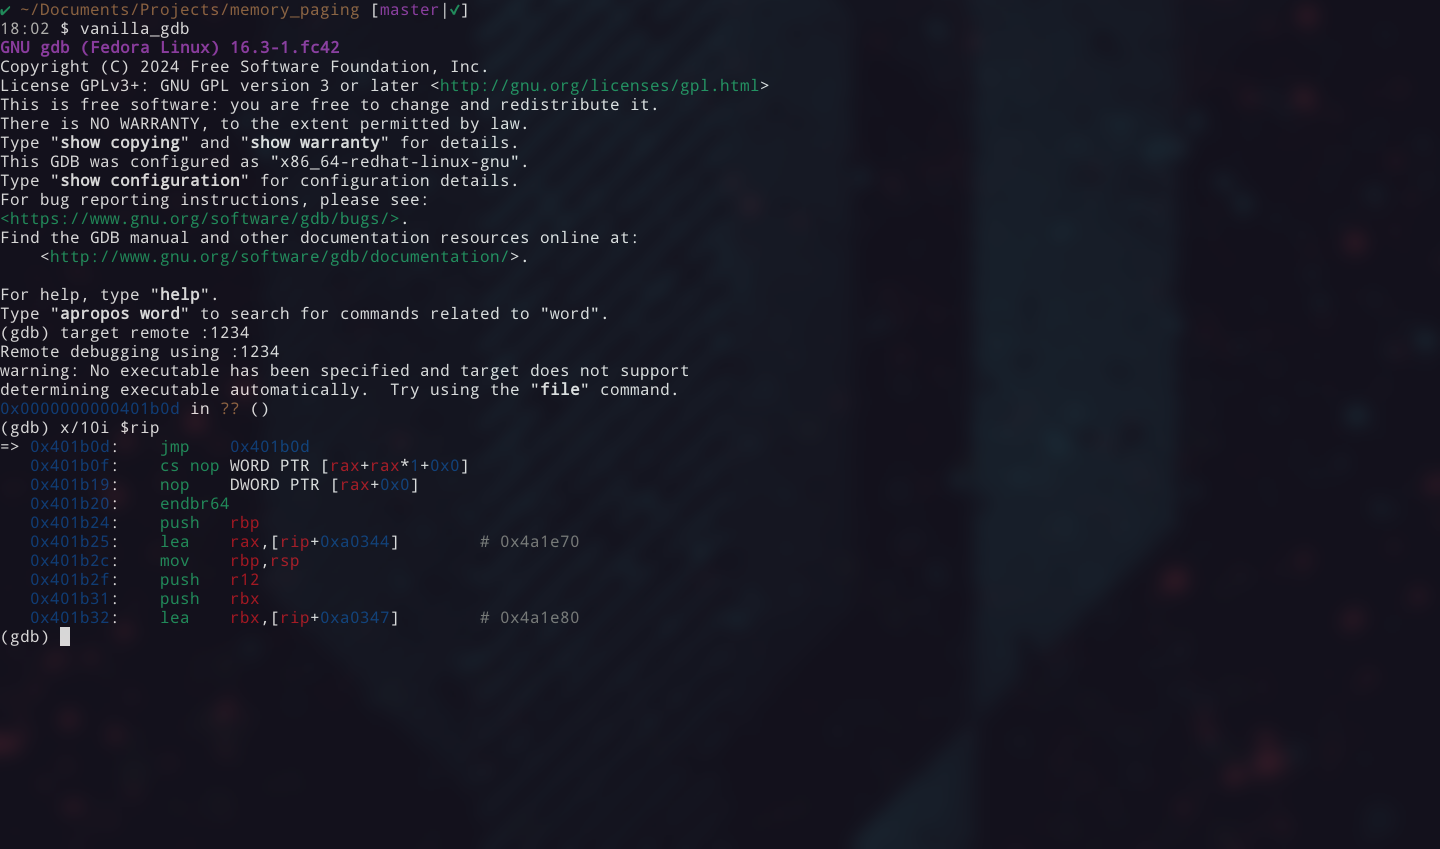
page_table_walk preview

page_table_walk

GitHubjazho76/page_table_walk

Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…

memory-forensicsreverse-engineeringdebuggers+4
288 months ago
witchcraft preview

witchcraft

GitHubcosmic-zip/witchcraft

WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
osintphishing-toolsreconnaissance+8
528h 36m ago
CVE-2026-87902-Toolkit preview

CVE-2026-87902-Toolkit

GitHubtc4dy/cve-2026-87902-toolkit

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

defensive-toolsvulnerability-scannerspayload-generation+8
1525 days ago
ida-pro-mcp preview

ida-pro-mcp

GitHubgrecandrei/ida-pro-mcp

Local-first, deterministic MCP server for IDA Pro/Home: 109 strict-schema reverse-engineering operations, evidence-backed findings, and policy-gated…
static-analysisreverse-engineeringscripting-automation+7
151 month ago
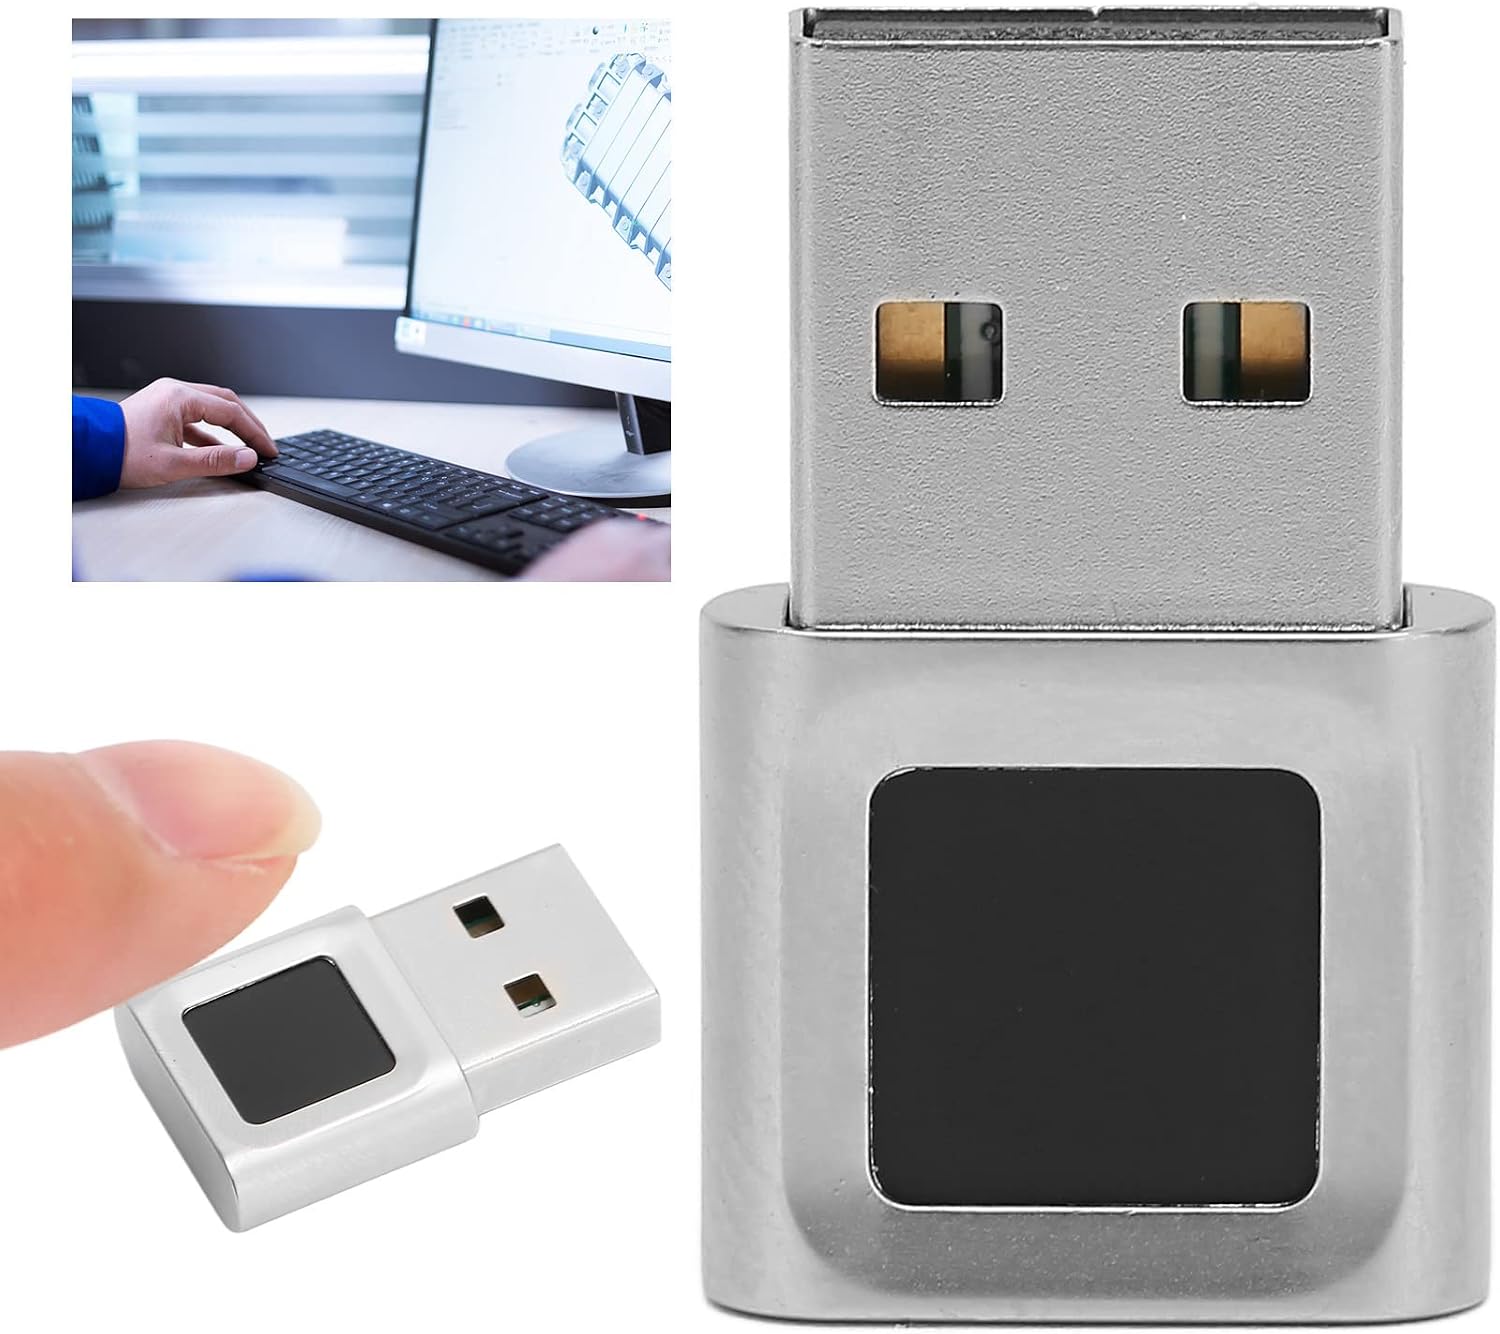
ft9201-libfprint preview

ft9201-libfprint

GitHubomgrant/ft9201-libfprint

Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
embedded-systems-securityreverse-engineeringhardware-hacking+4
213 months ago
hexcymatix preview

hexcymatix

GitHubxoreaxeaxeax/hexcymatix

Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…


static-analysisreverse-engineeringbinary-analysis
262 months ago
Previous1…606162…100Next







