
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended
 manjustice/datadome-vm-internals
Analysis of DataDome's custom obfuscated VM and bytecode format, revealing string encryption, S-box ciphers, and browser fingerprinting signals for…
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
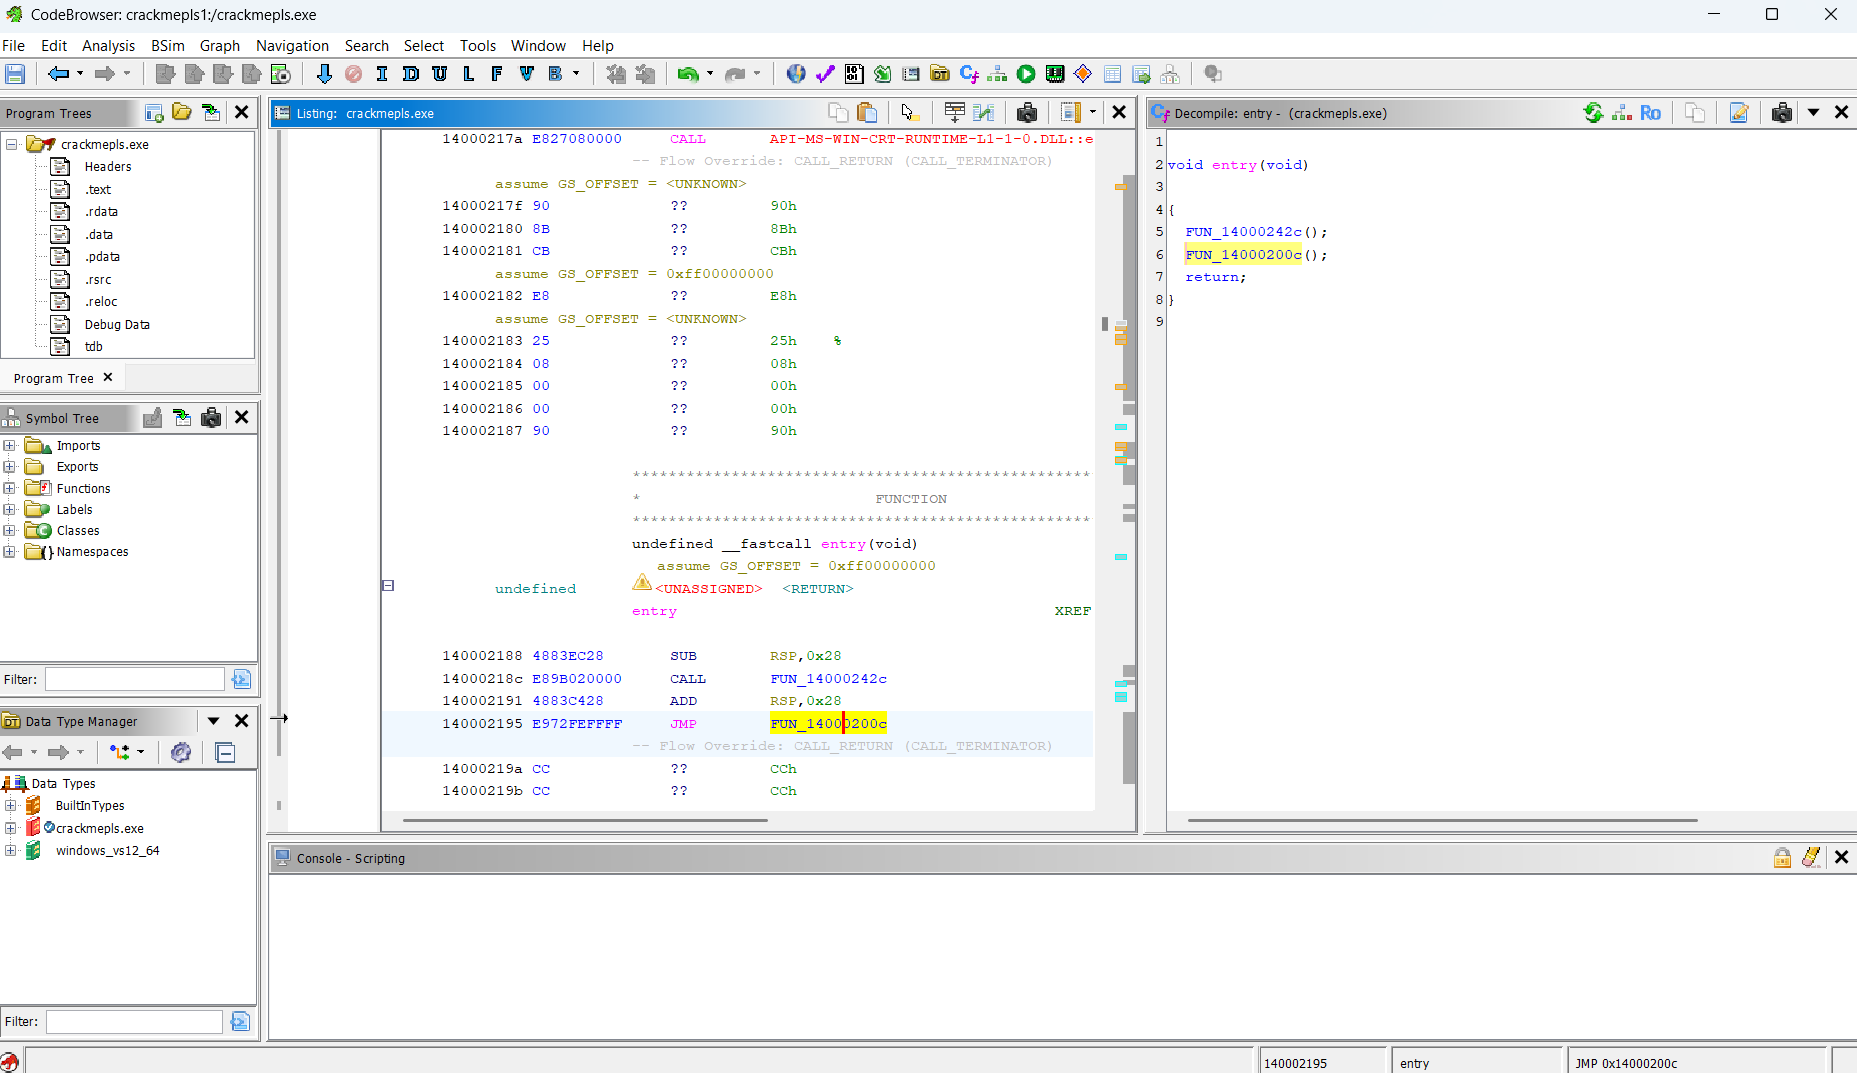 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 gmh5225/kli-ex
Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
 nccgroup/libdlmalloc
Heap analysis tooling for dlmalloc
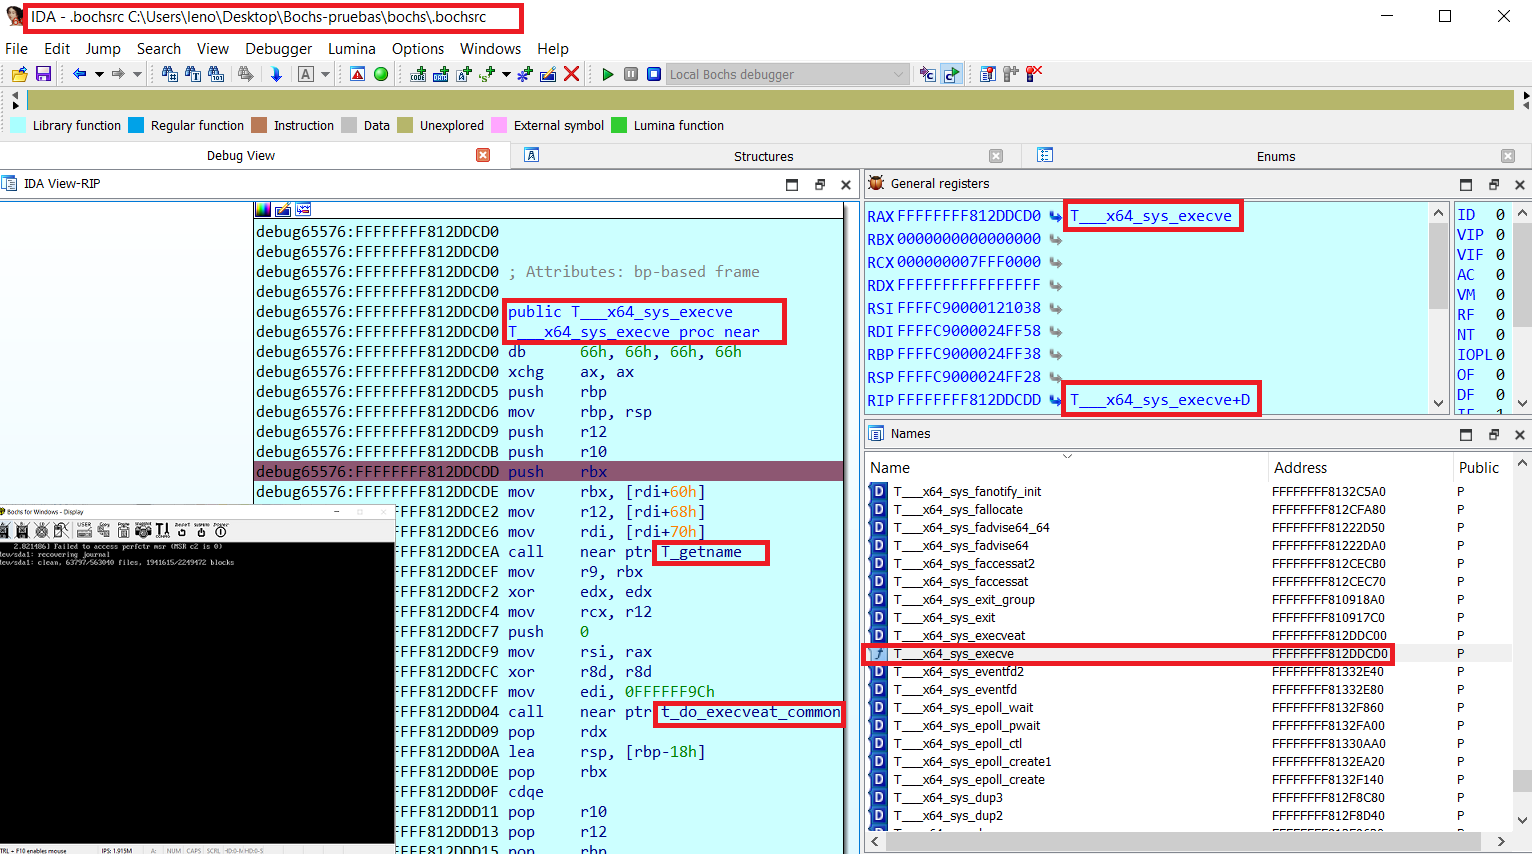 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 c0mposer/c-game-modding-utility
A game modding utility that makes injecting C/C++ code easier.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 kal1gh0st/whatsapphack-rce
Exploit for CVE-2019-11932, a remote code execution vulnerability in WhatsApp via malicious GIF files. Includes proof-of-concept code and technical…
 coremaze/me2-writeup
Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 synacktiv/amsi-bypass
Lists of AMSI triggers (VBA, JScript / VBScript)
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.








