
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
 redteamfortress/cve-2026-36425
CVE-2026-36425 OPSWAT AppRemover (ardrv.sys) improper access control advisory
 liji32/snatchbox
SnatchBox (CVE-2020-27935) is a sandbox escape vulnerability and exploit affecting macOS up to version 10.15.x
 badchemical/iot-vulnerability-research-public
Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.
 leandrofroes/malware-research
General malware analysis stuff
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 nccgroup/binja_sensei
A plugin that provides resources for beginners to learn reverse engineering using Binary Ninja. It automatically installs several other plugins, and…
 omair2084/msmq_re
Proof-of-concept exploit for the MSMQ QueueJumper RCE, crafting malformed packets to trigger unauthenticated remote code execution via the Message…
 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 reecdeep/hivev5_file_decryptor
Hive v5 file decryption algorithm
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
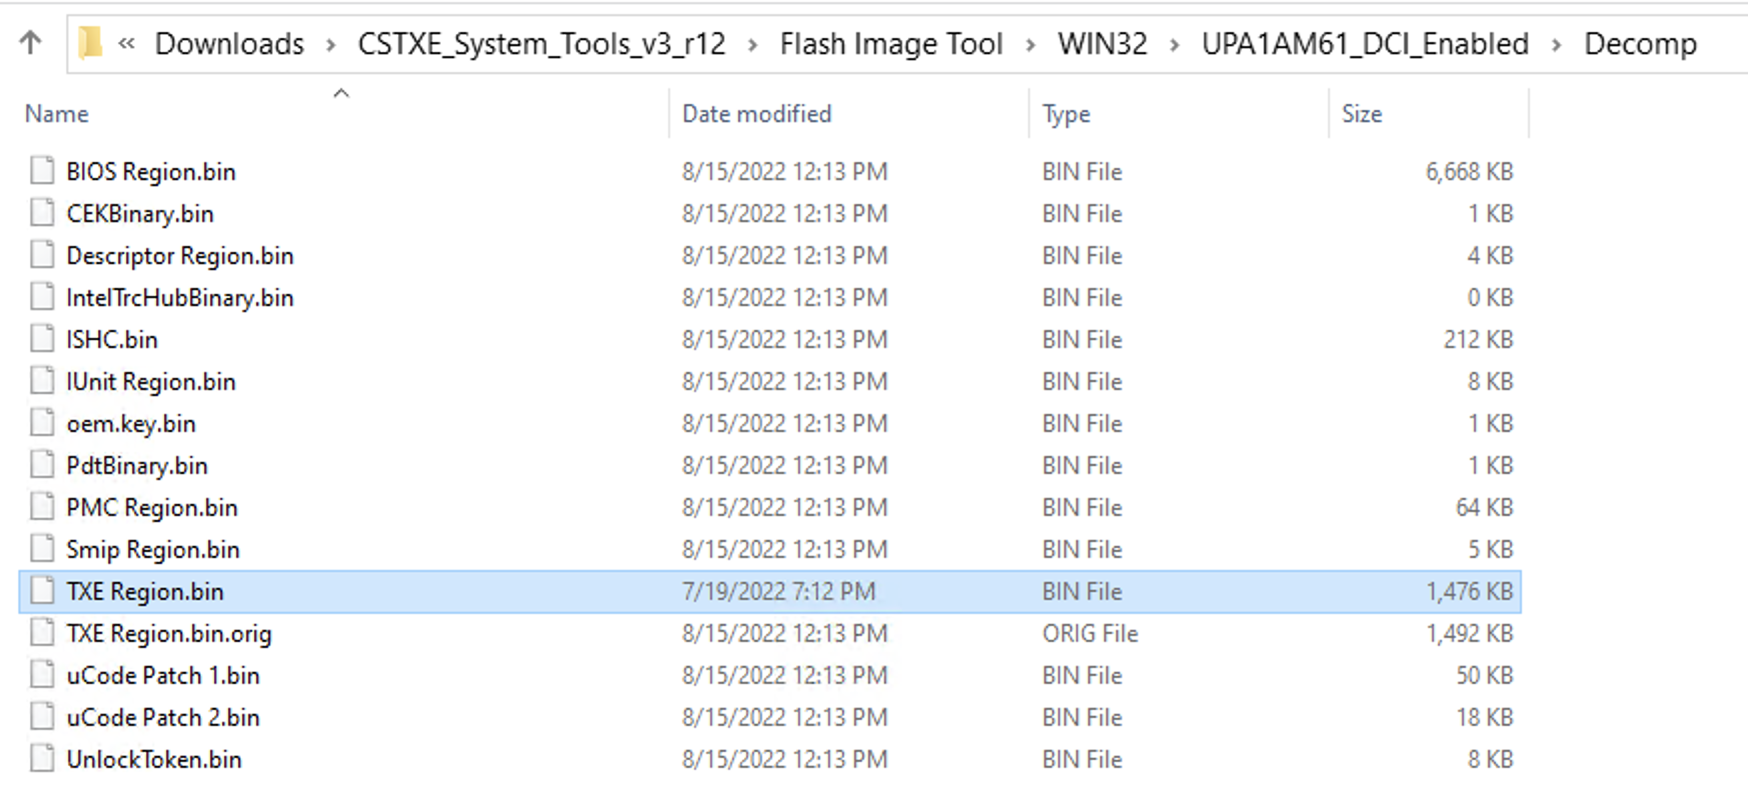 xenokovah/inteltxe-poc
Intel Management Engine JTAG Proof of Concept - 2022 Instructions
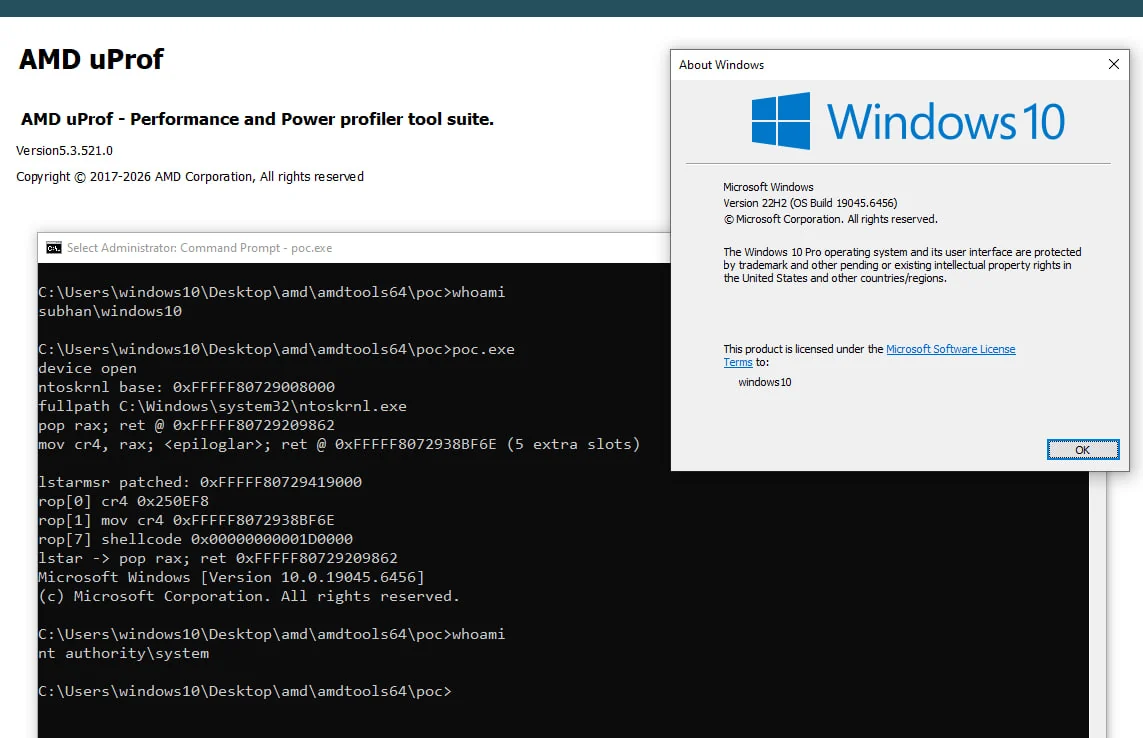 mein-0/mercilessamd
Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…








