
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 abstractengine/pentest-muse-cli
AI-powered assistant for penetration testers that generates payloads, analyzes code, performs reconnaissance, and executes command-line actions to…
 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 claroty/arya
Generates pseudo-malicious files from YARA rules to trigger AV/EDR detection, enabling malware research, rule QA, and network sensor pressure testing…
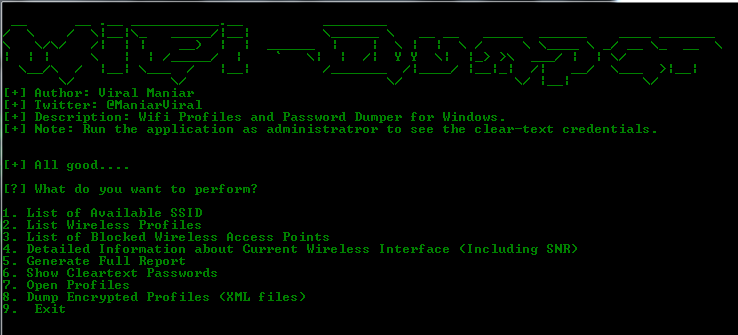 viralmaniar/wifi-dumper
This is an open source tool to dump the wifi profiles and cleartext passwords of the connected access points on the Windows machine. This tool will…
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 helixo32/nimblackout
Kill AV/EDR leveraging BYOVD attack
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 lloydlabs/wsb-detect
wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 dis0rder0x00/obex
Obex – Blocking unwanted DLLs in user mode
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 ustayready/sharphose
Asynchronous Password Spraying Tool in C# for Windows Environments
 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
 wh0amitz/bypasscredguard
Credential Guard Bypass Via Patching Wdigest Memory
 mordavid/donpwner
Advanced Domain Controller attack and credential analysis tool leveraging DonPAPI database
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…








