
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended
 temesgeny/ppsx-file-generator
ppsx file generator for cve-2017-8570 (based on bhdresh/cve-2017-8570)
 watchtowrlabs/fortijump-exploit-cve-2024-47575
Fortinet Fortimanager Unauthenticated Remote Code Execution AKA FortiJump CVE-2024-47575
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
 n0qword/win32k-callback-detouring
Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
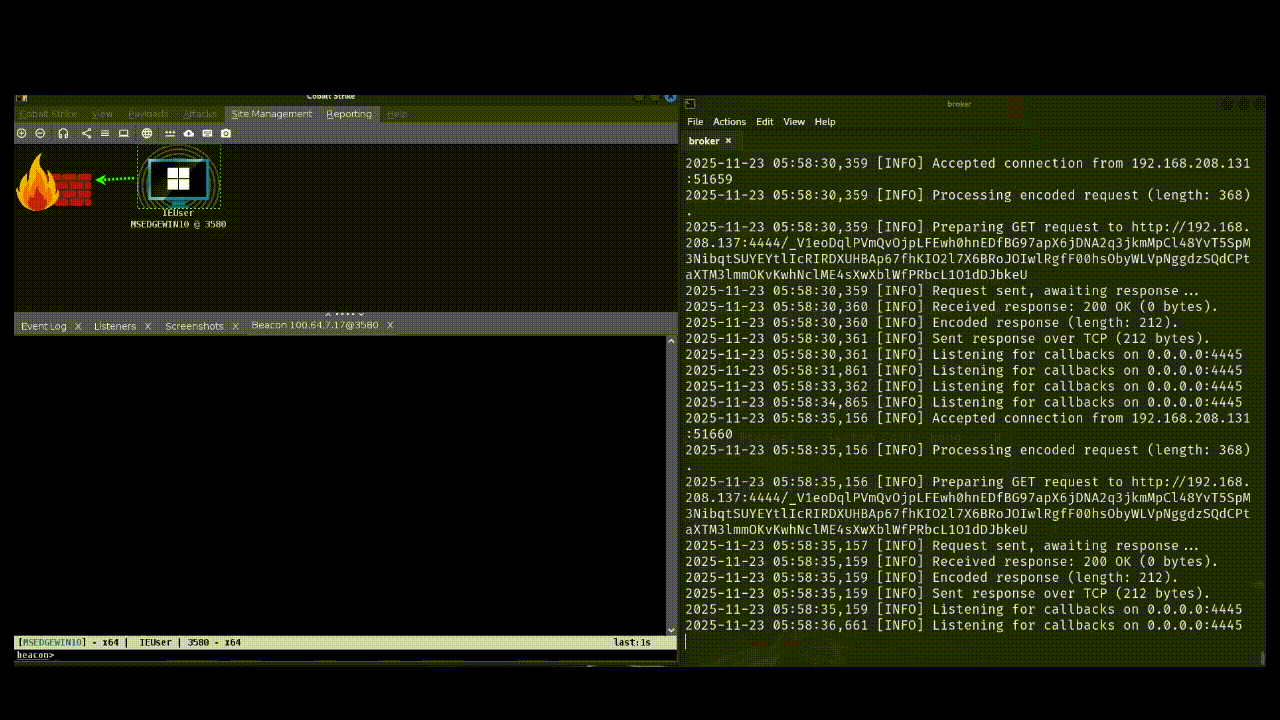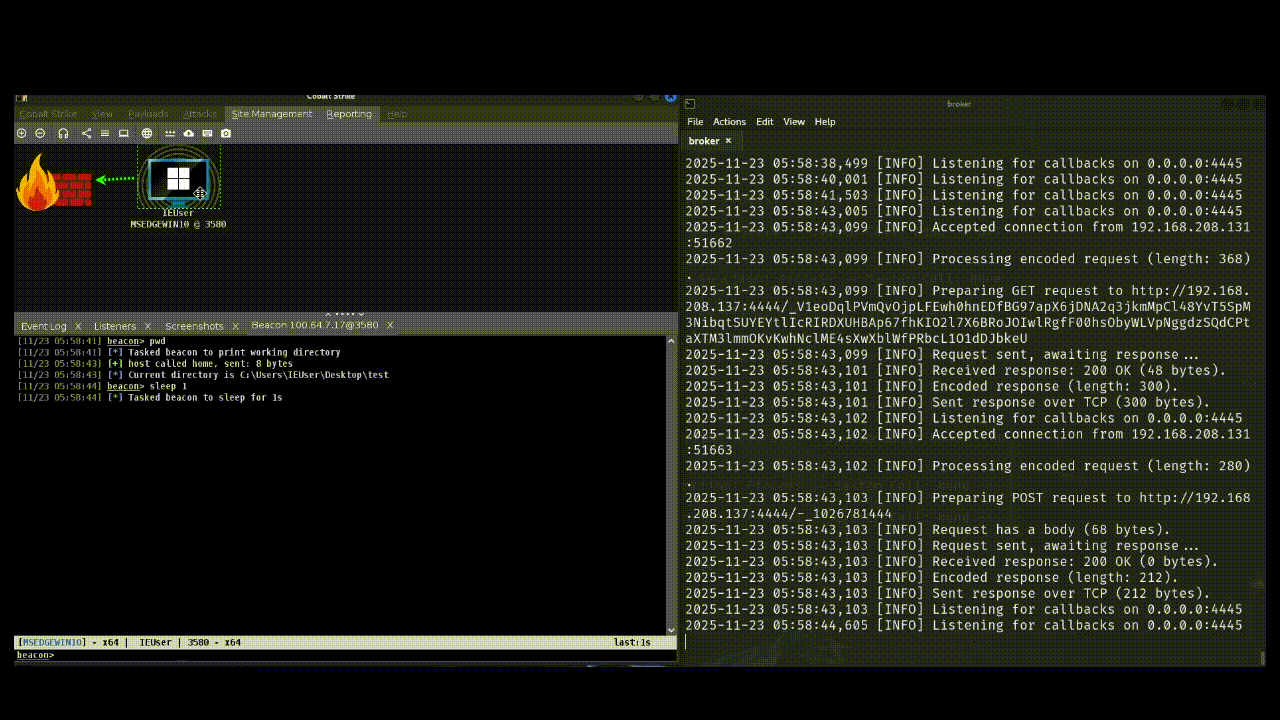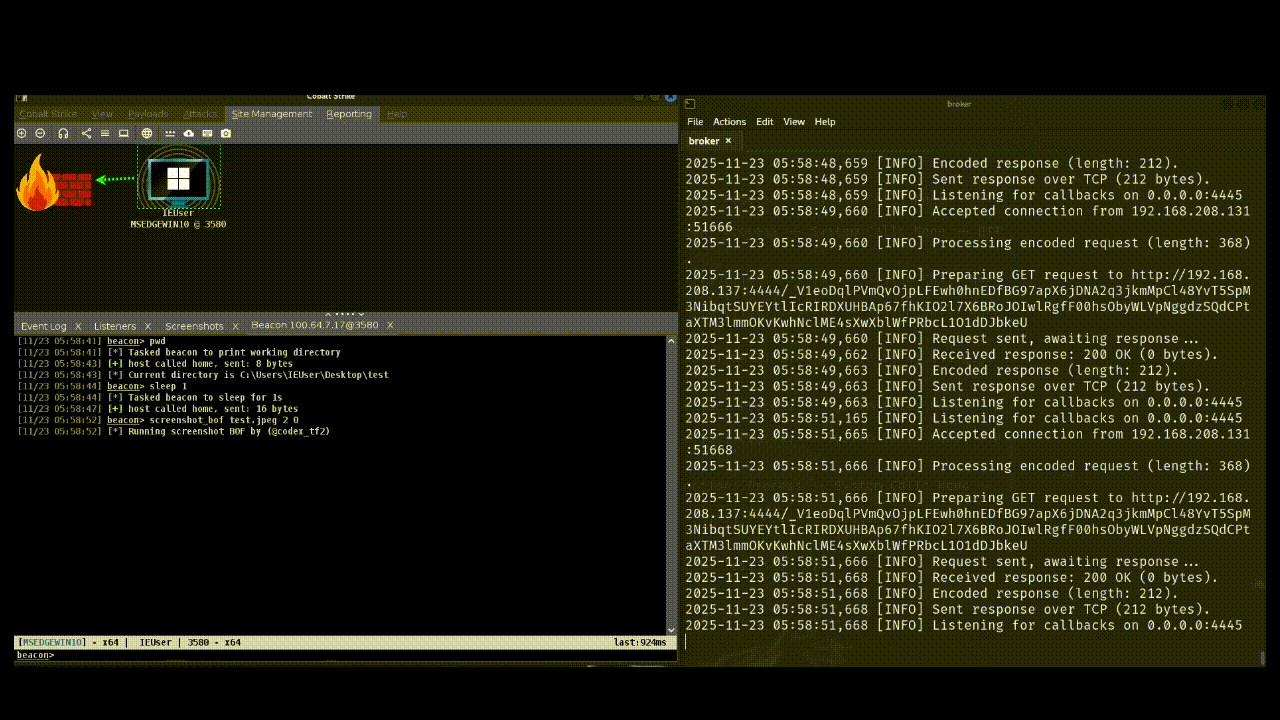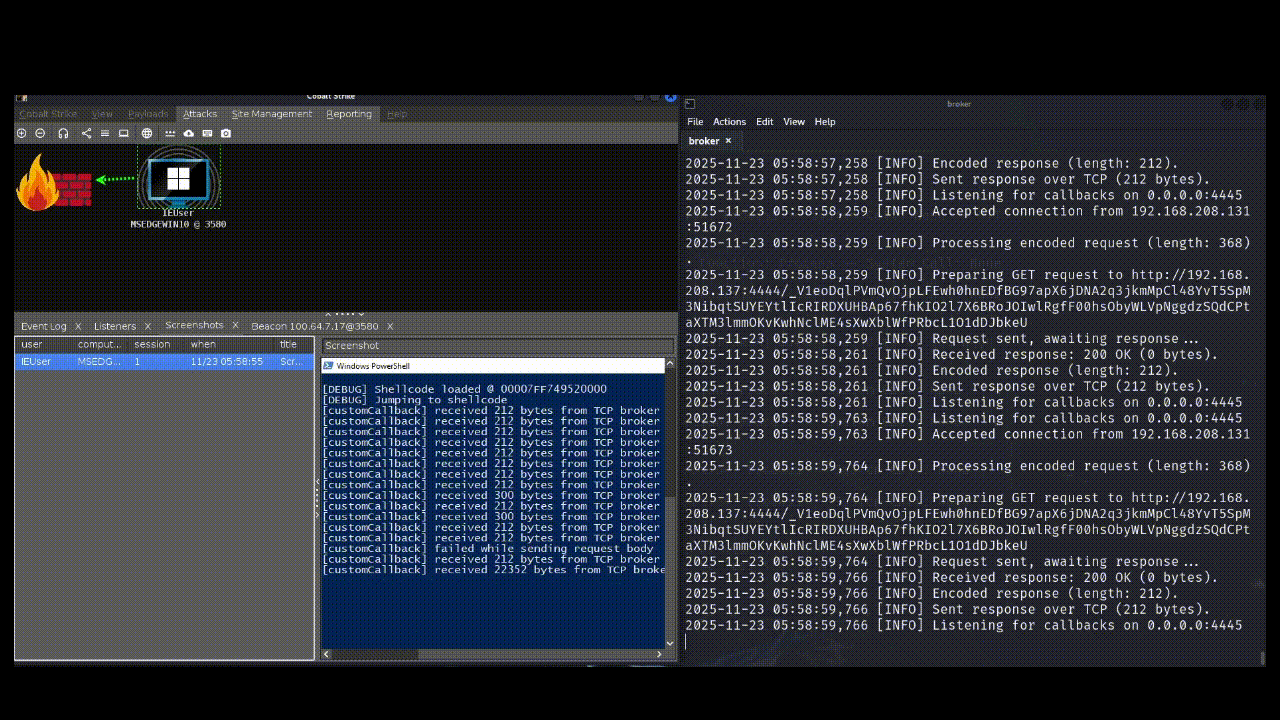 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 tarlogicsecurity/arecibo
Endpoint for Out-of-Band Exfiltration (DNS & HTTP)
 macmod/flashingestor
TUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…
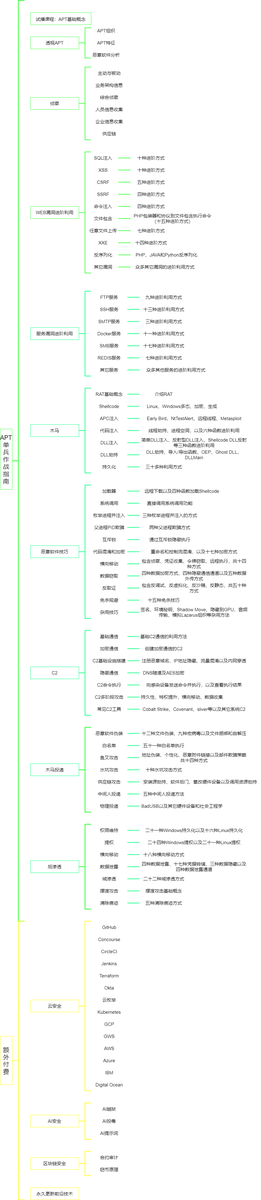 ghostwolflab/apt-individual-combat-guide
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…
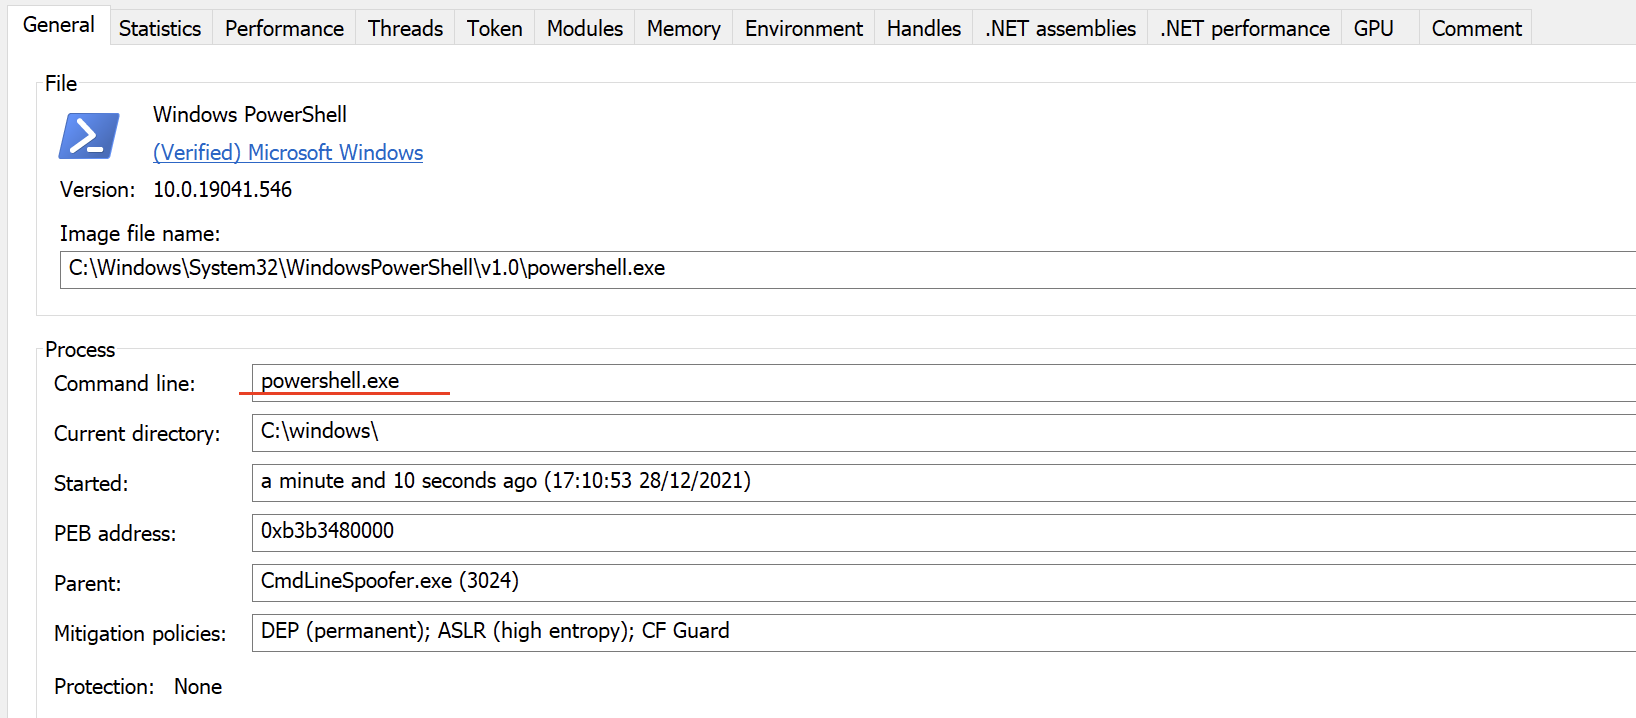 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 sh1n0g1/shinobot
RAT / Botnet Simulator for pentest / education
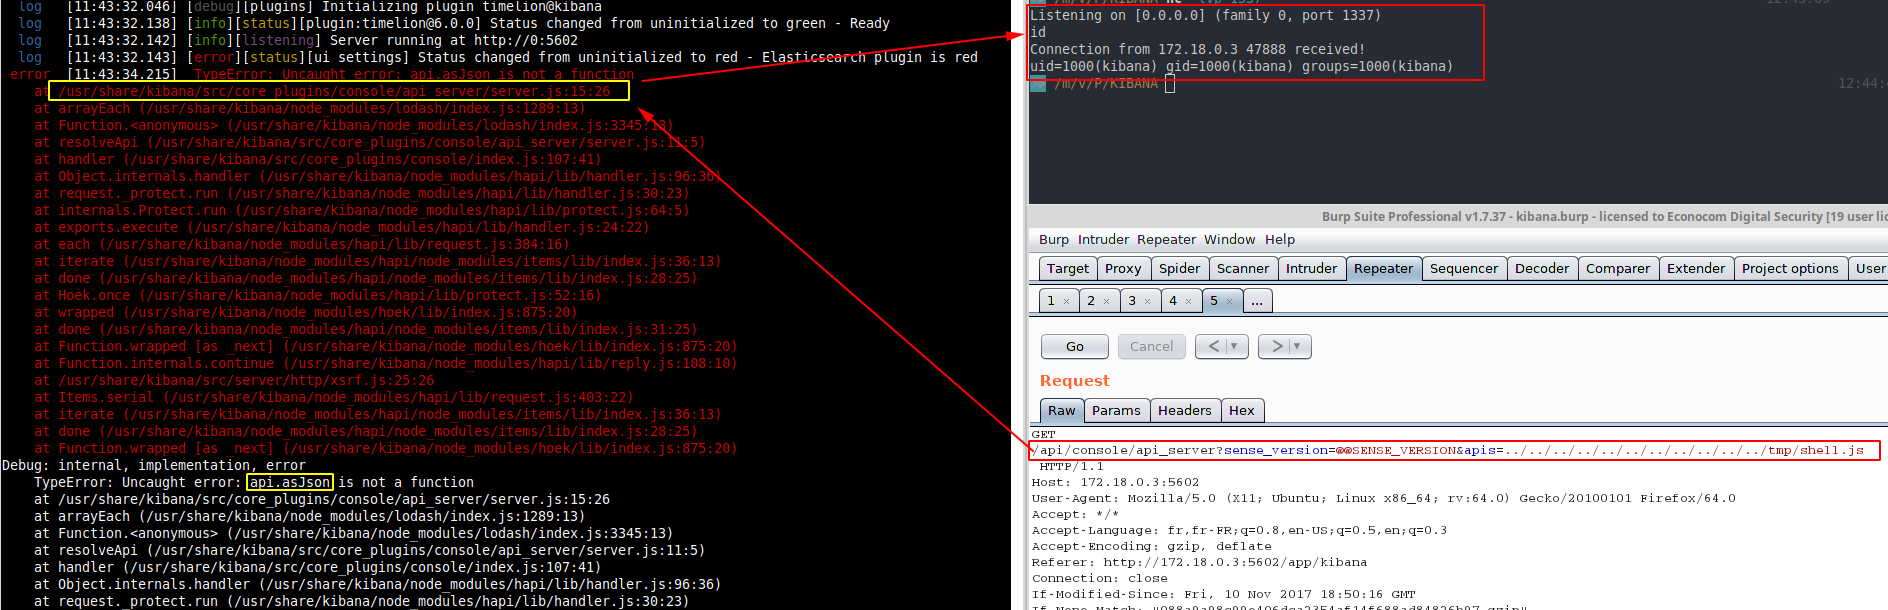 mpgn/cve-2018-17246
CVE-2018-17246 - Kibana LFI < 6.4.3 & 5.6.13
 k8gege/zimbraexploit
Zimbra邮件系统漏洞 XXE/RCE/SSRF/Upload GetShell Exploit 1. (CVE-2019-9621 Zimbra<8.8.11 XXE GetShell Exploit)
 benzamir/mitm6-kerberos-cname-abuse
Kerberos CNAME abuse PoC
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…








