
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
obex — Obex – Blocking unwanted DLLs in user mode | Kitploit

Tools/GitHubGitHub/dis0rder0x00/obex
IDS/IPS EvasionPost-ExploitationRed TeamingAdversarial Attack
GitHubdis0rder0x00/obex

obex

Obex – Blocking unwanted DLLs in user mode

View Repository
28137371 year agoReviewed by Kitploit
Share

Obex - DLL Blocking

Obex is a PoC tool/technique that can be used to prevent unwanted modules (e.g., EDR or monitoring libraries) from being loaded into a newly started process during process initialization or at runtime.

Features

  • Spawns any process with arguments under debug control.
  • Blocks a configurable list of DLLs by name.
  • Works both for startup DLLs and dynamically loaded DLLs (LoadLibrary*).
  • Written in plain C with no external dependencies.

Usage

obex.exe "<command with args>" [dll1.dll,dll2.dll,...]
  • If no DLL list is provided, a default blocklist is used (at the time of writing just amsi.dll).
  • DLL names are case-insensitive.

How Does It Work?

Besides parsing cli arguments the PoC does the following (in a rough overview):

For deeper understanding check code (obviously) or contact me on discord or twitter.

Screenshot

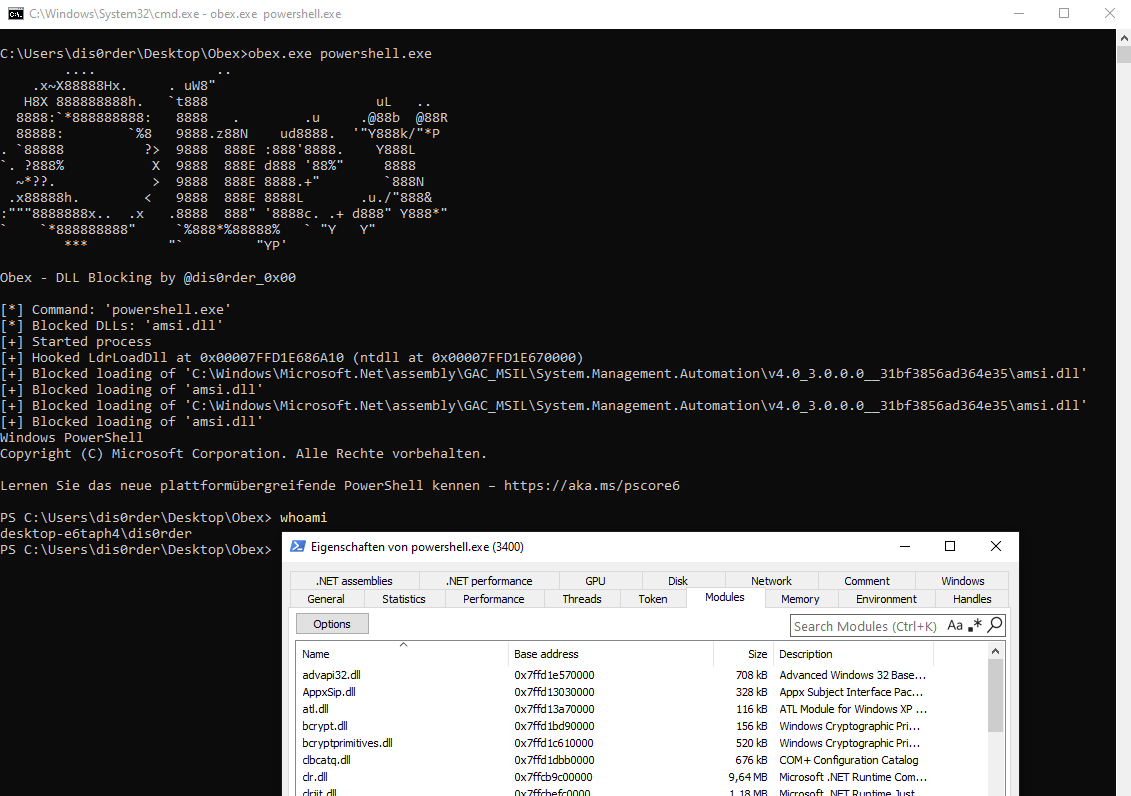
The screenshot shows obex spawning powershell.exe with the default blocklist (only amsi.dll). Additionally you can see the spawned process’s module list to verify that amsi.dll was not loaded.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    276

Explore all tools

Browse our collection of tools

View all tools →





