
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)
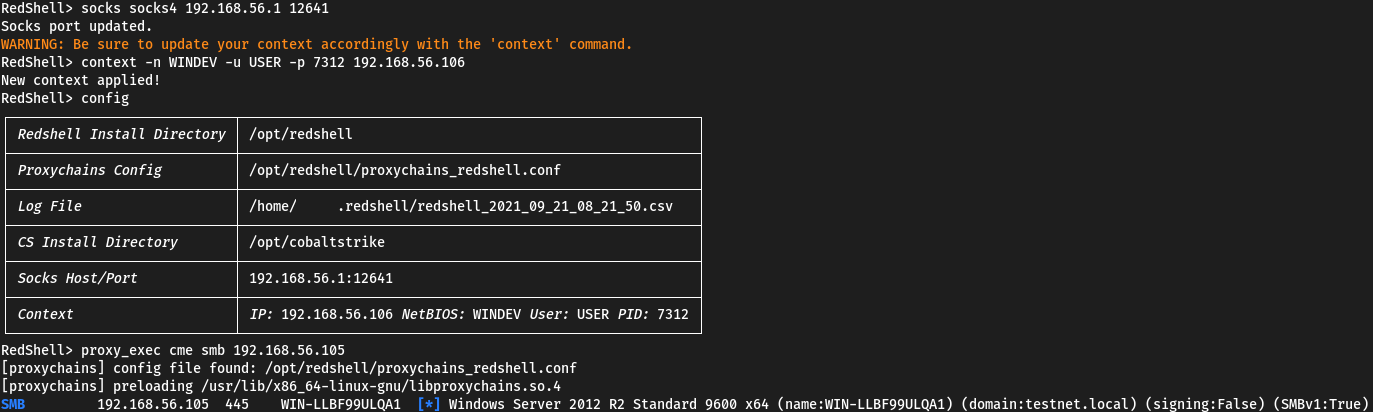 verizon/redshell
An interactive command prompt for red teaming and pentesting. Automatically pushes commands through SOCKS4/5 proxies via proxychains. Optional Cobalt…
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 kindtime/nosferatu
DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 kudaes/lolbits
** DISCONTINUED ** C2 framework that uses Background Intelligent Transfer Service (BITS) as communication protocol and Direct Syscalls + Dinvoke for…
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 vozec/cve-2023-7028
This repository presents a proof-of-concept of CVE-2023-7028
 shell-company/qrexfil
This tool is a command line utility that allows you to convert any binary file into a QRcode movie. The data can then be reassembled visually…
 vysecurity/cve-2017-8759
CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.
 sudonoodle/bof-coerce-ipp
Beacon Object File (BOF) to coerce machine account auth via IPP.








