
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 safebuffer/sam-the-admin
Exploiting CVE-2021-42278 and CVE-2021-42287 to impersonate DA from standard domain user
 cytopia/pwncat
pwncat - netcat on steroids with Firewall, IDS/IPS evasion, bind and reverse shell, self-injecting shell and port forwarding magic - and its fully…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
 uknowsec/sharpdecryptpwd
对密码已保存在 Windwos 系统上的部分程序进行解析,包括:Navicat,TeamViewer,FileZilla,WinSCP,Xmangager系列产品(Xshell,Xftp)。源码:https://github.com/RowTeam/SharpDecryptPwd
 insecurityofthings/jackit
Exploit tool for MouseJack vulnerability enabling keystroke injection and mouse hijacking over nRF24L01 wireless dongles. Supports multiple Microsoft…
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…
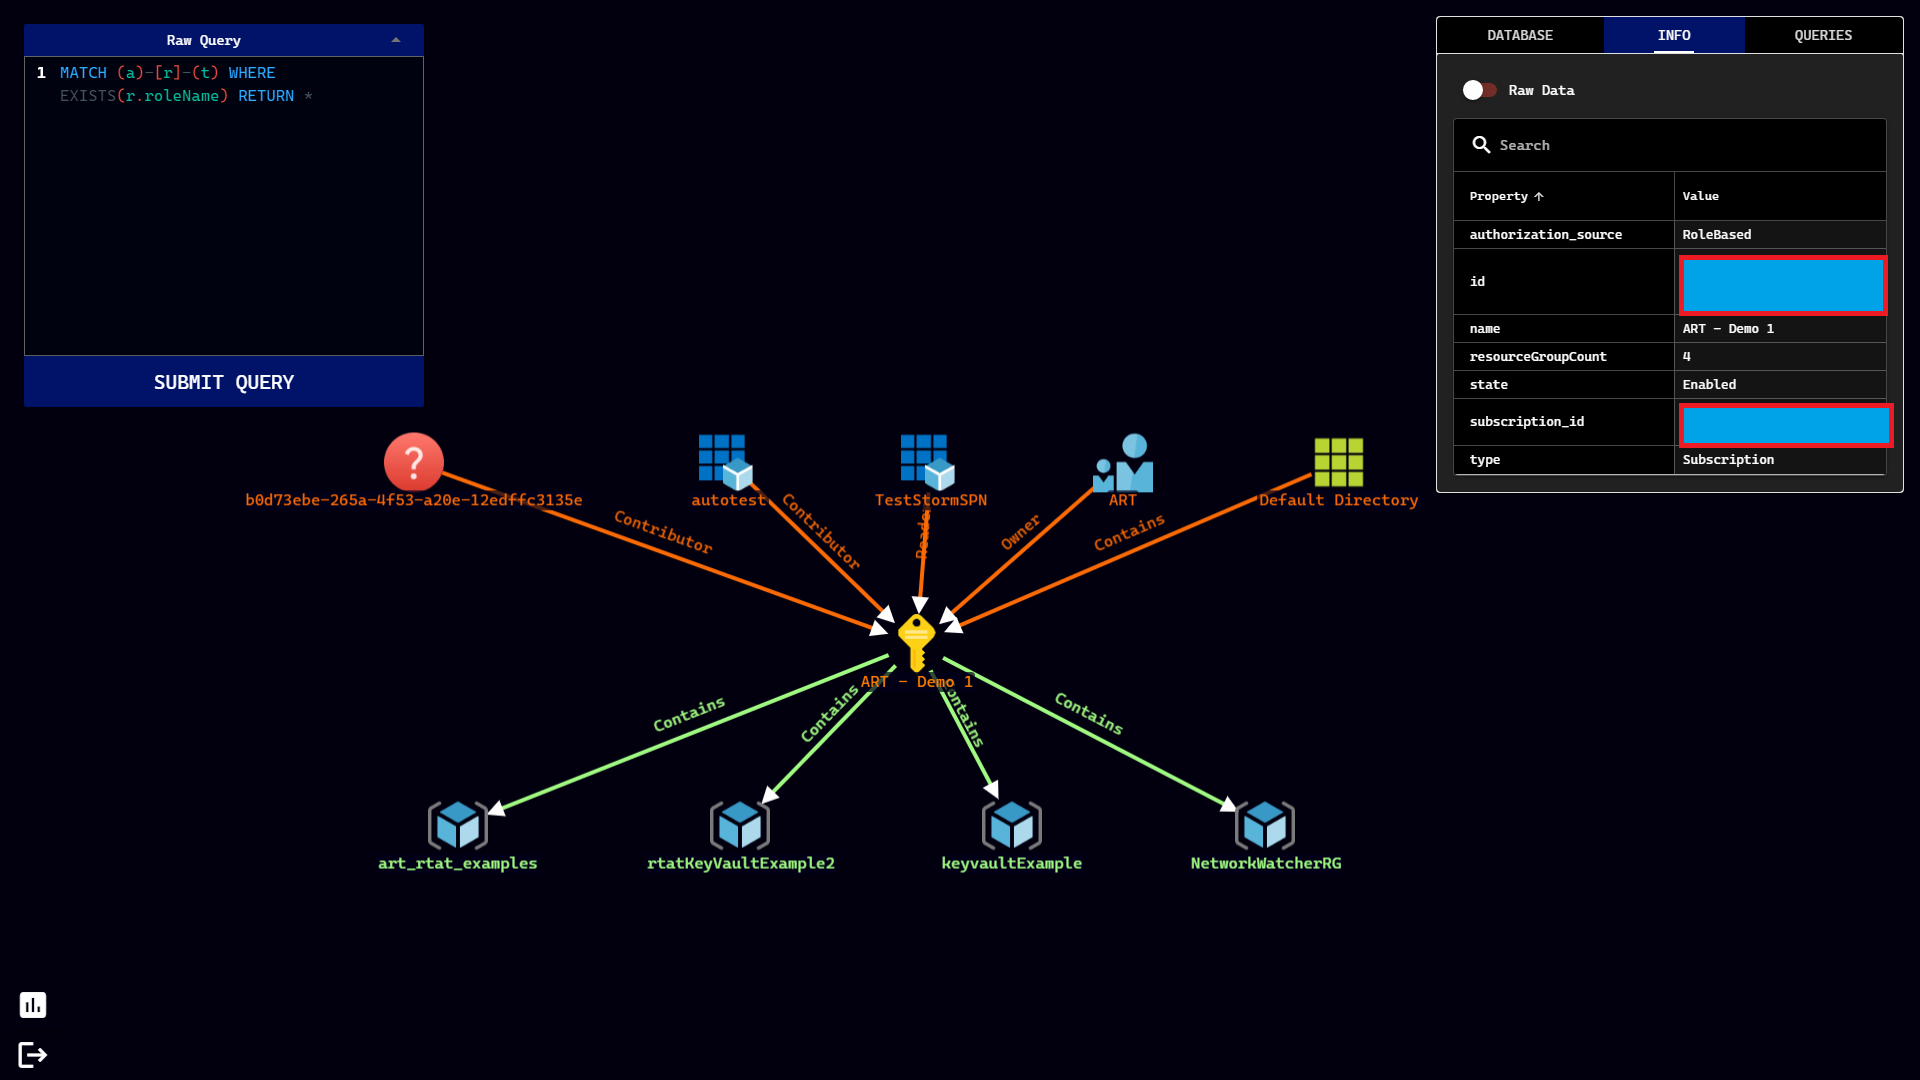 azure/stormspotter
Azure Red Team tool for graphing Azure and Azure Active Directory objects
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
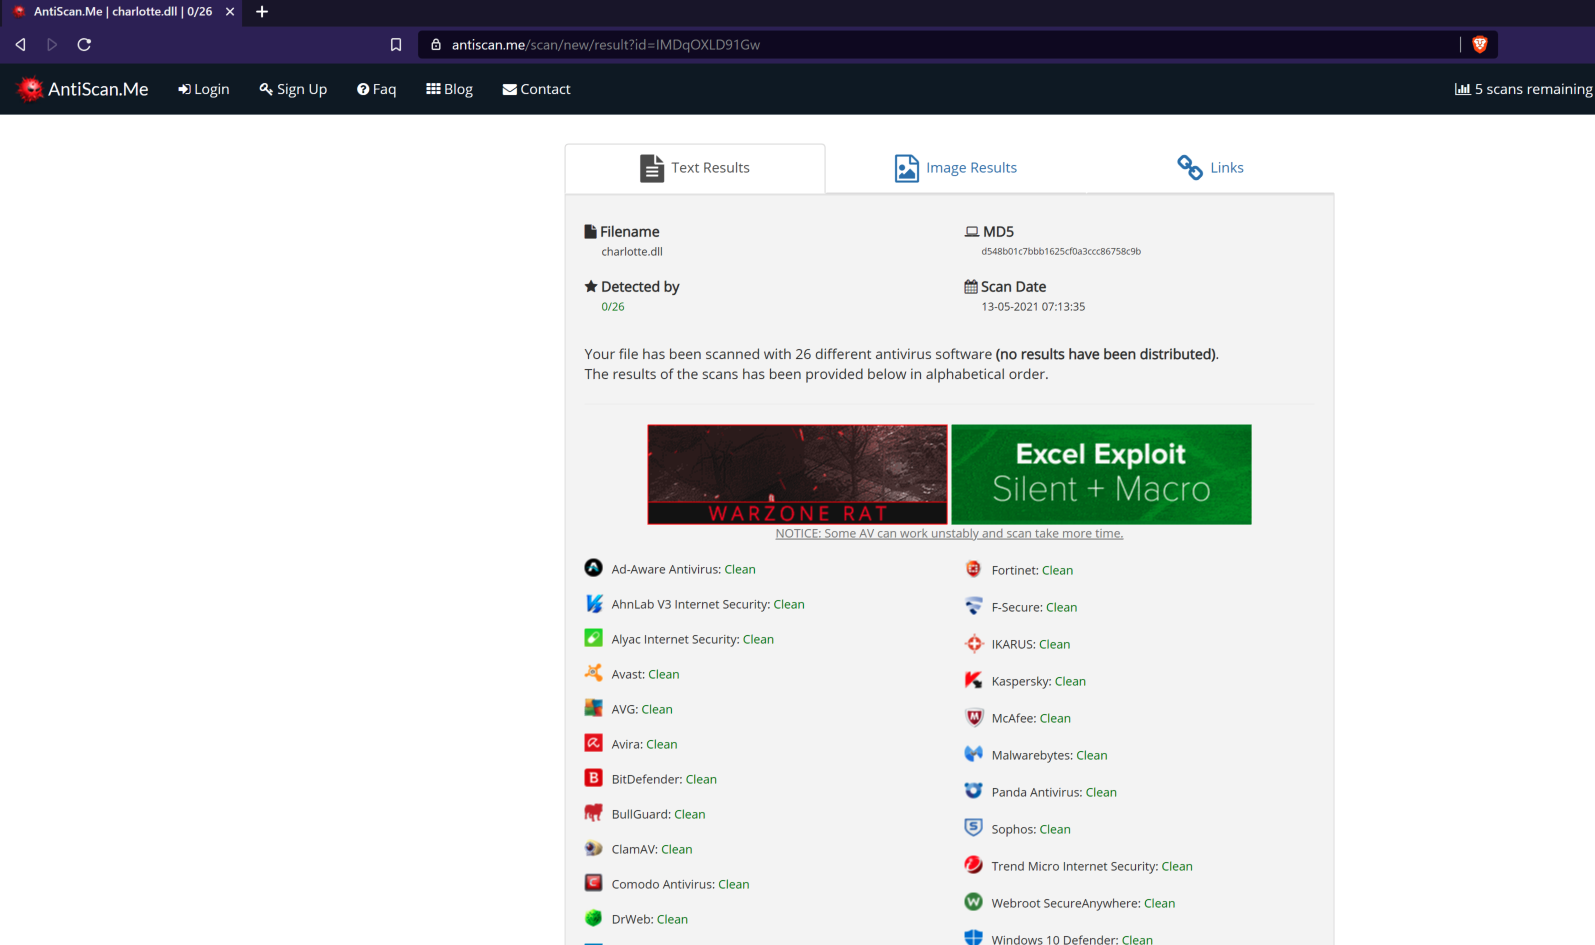 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 sensepost/dns-shell
DNS-Shell is an interactive Shell over DNS channel
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
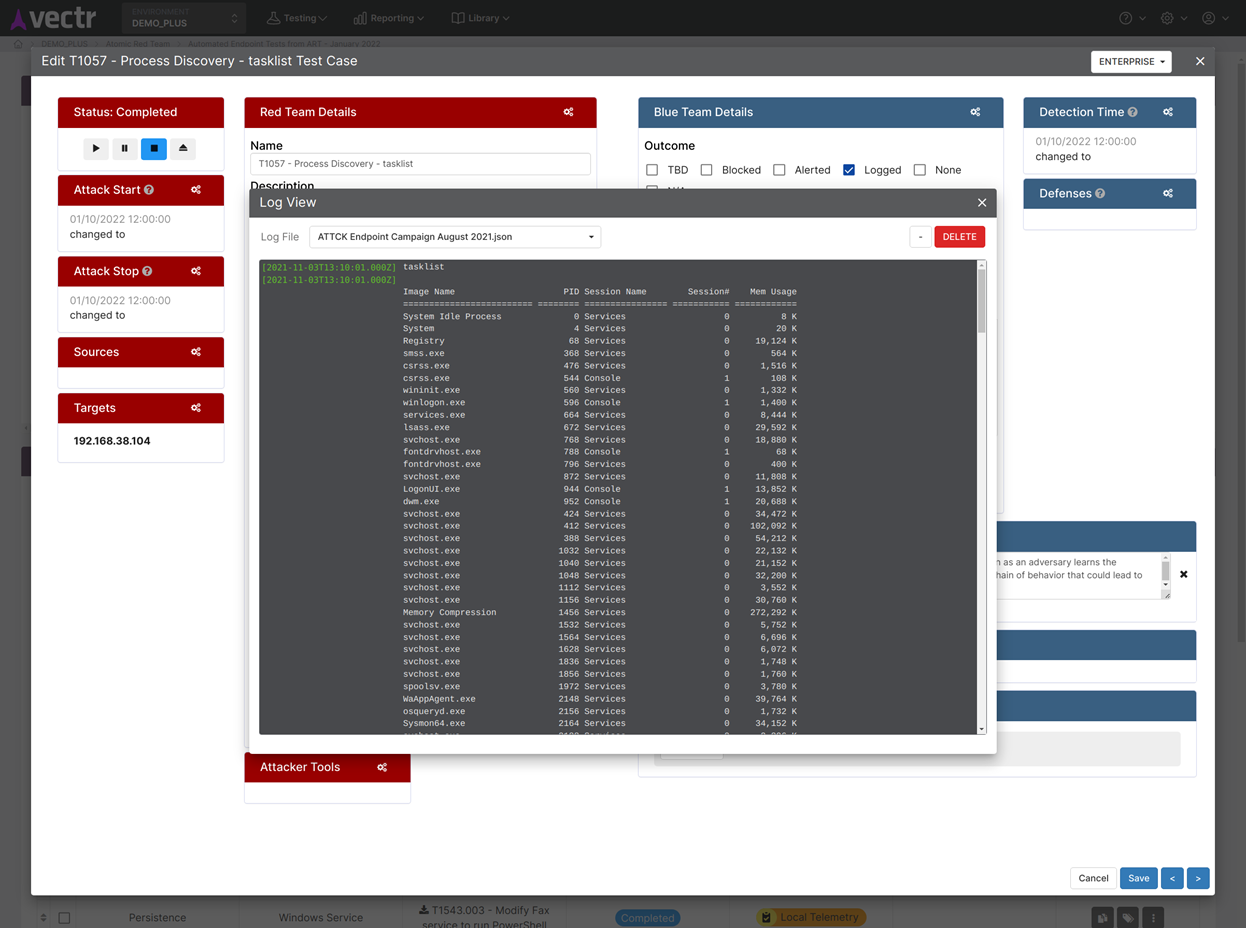 securityriskadvisors/vectr
Track red and blue team testing activities to measure detection and prevention capabilities across attack scenarios, with campaign management, TTP…
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 ccob/sharpblock
A method of bypassing EDR's active projection DLL's by preventing entry point exection
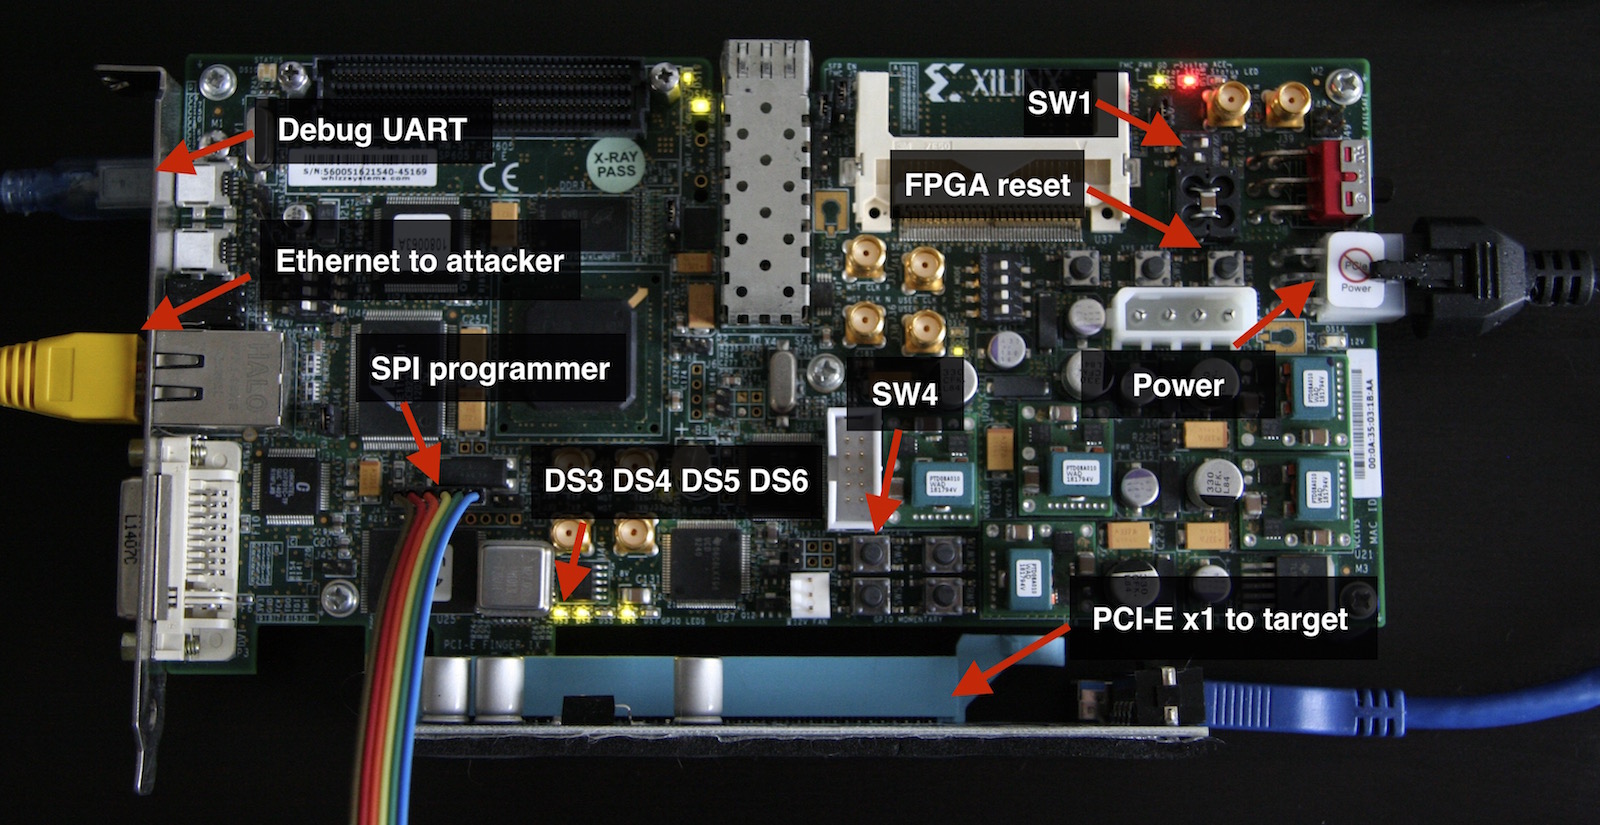 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info








