Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
VECTR — Track red and blue team testing activities to measure detection and prevention capabilities across attack scenarios, with campaign management, TTP replication, and resilience trending. | Kitploit
Tools/GitHubGitHub/securityriskadvisors/vectr
Penetration TestingThreat IntelligenceLearning & EducationRed TeamingLabs & Practice
GitHubsecurityriskadvisors/vectr

VECTR

Track red and blue team testing activities to measure detection and prevention capabilities across attack scenarios, with campaign management, TTP replication, and resilience trending.

View Repository
1.6k177371 year agoReviewed by Kitploit
Share

VECTR documentation: https://docs.vectr.io

VECTR Community Discord Channel: https://discord.gg/2FRd8zf728

VECTR is a tool that facilitates tracking of your red and blue team testing activities to measure detection and prevention capabilities across different attack scenarios. VECTR provides the ability to create assessment groups, which consist of a collection of Campaigns and supporting Test Cases to simulate adversary threats. Campaigns can be broad and span activity across the kill chain, from initial compromise to privilege escalation and lateral movement and so on, or can be a narrow in scope to focus on specific detection layers, tools, and infrastructure. VECTR is designed to promote full transparency between offense and defense, encourage training between team members, and improve detection & prevention success rate across the environment.

VECTR is focused on common indicators of attack and behaviors that may be carried out by any number of threat actor groups, with varying objectives and levels of sophistication. VECTR can also be used to replicate the step-by-step TTPs associated with specific groups and malware campaigns, however its primary purpose is to replicate attacker behaviors that span multiple threat actor groups and malware campaigns, past, present and future. VECTR is meant to be used over time with targeted campaigns, iteration, and measurable enhancements to both red team skills and blue team detection capabilities. Ultimately the goal of VECTR is to make a network resilient to all but the most sophisticated adversaries and insider attacks.
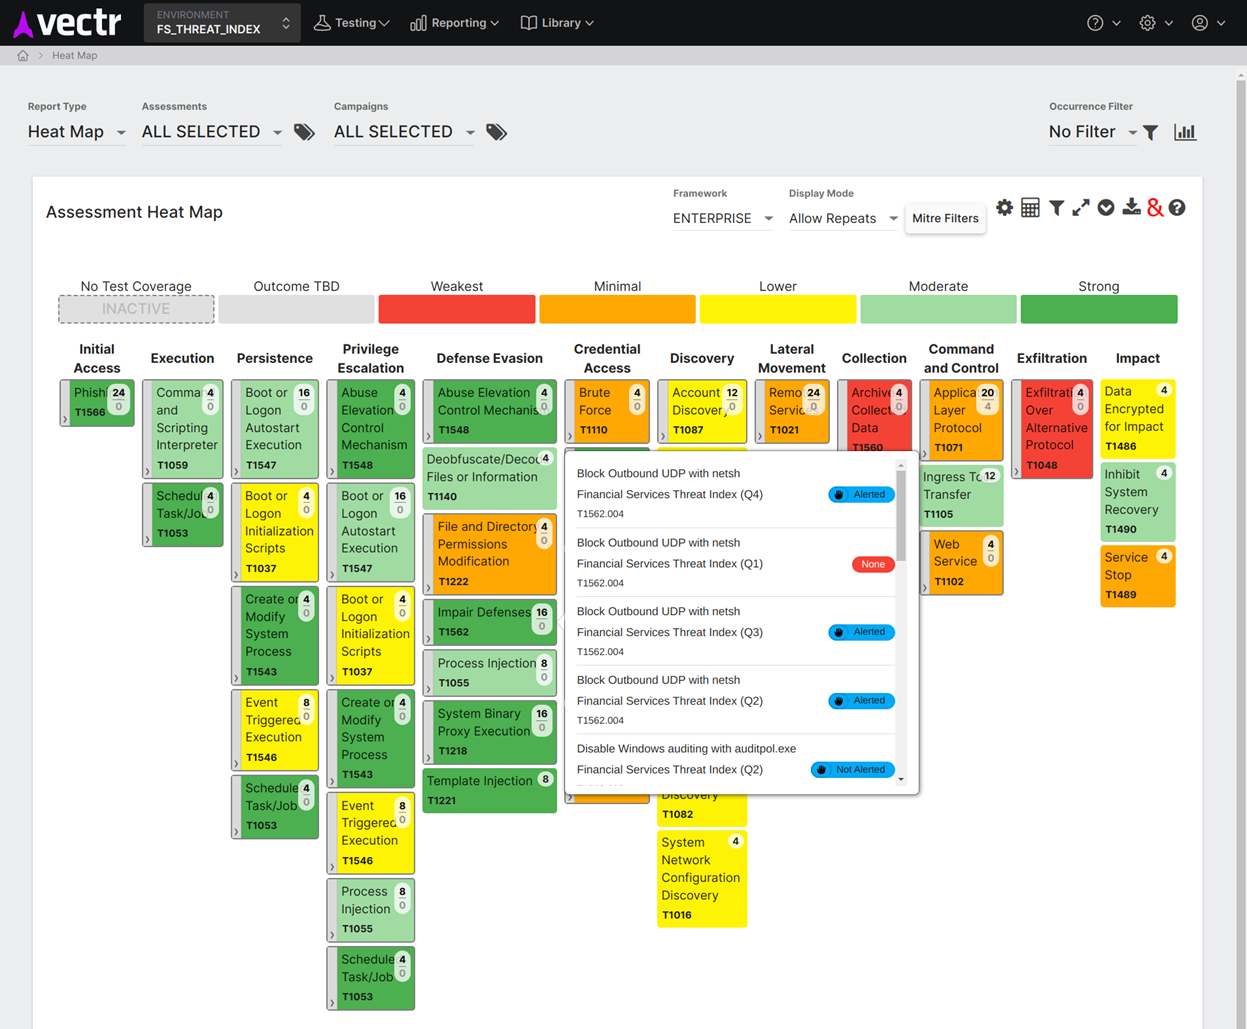
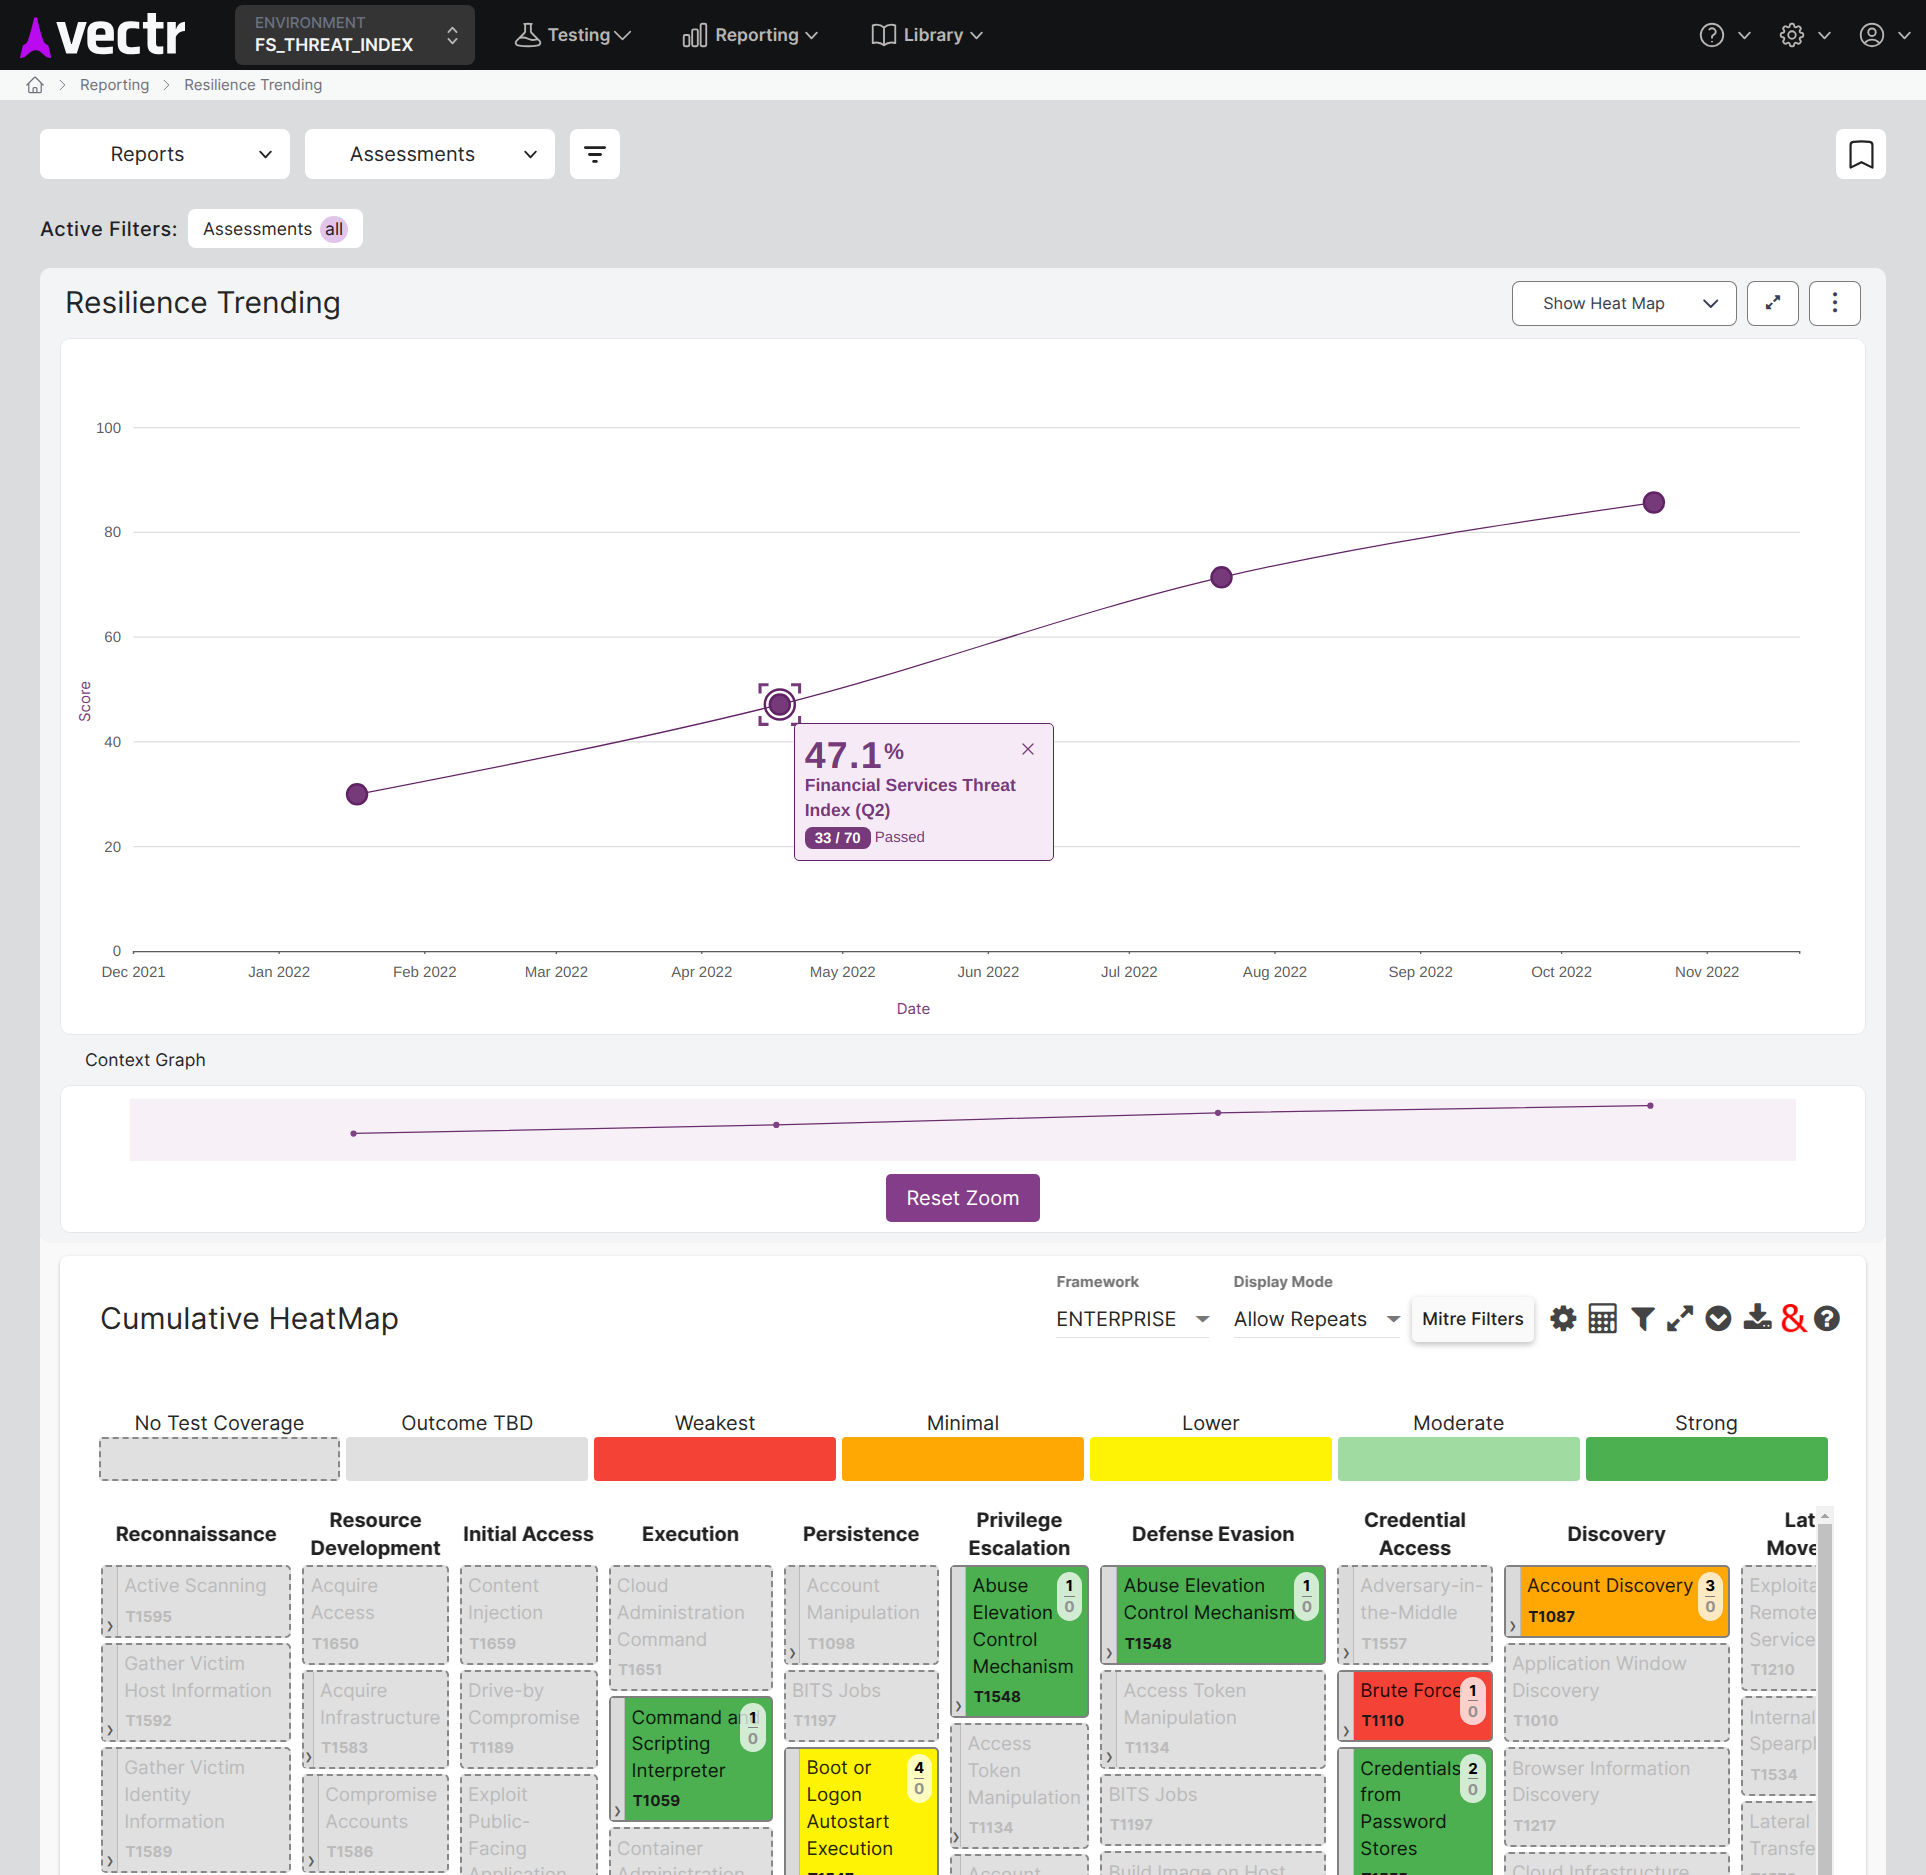
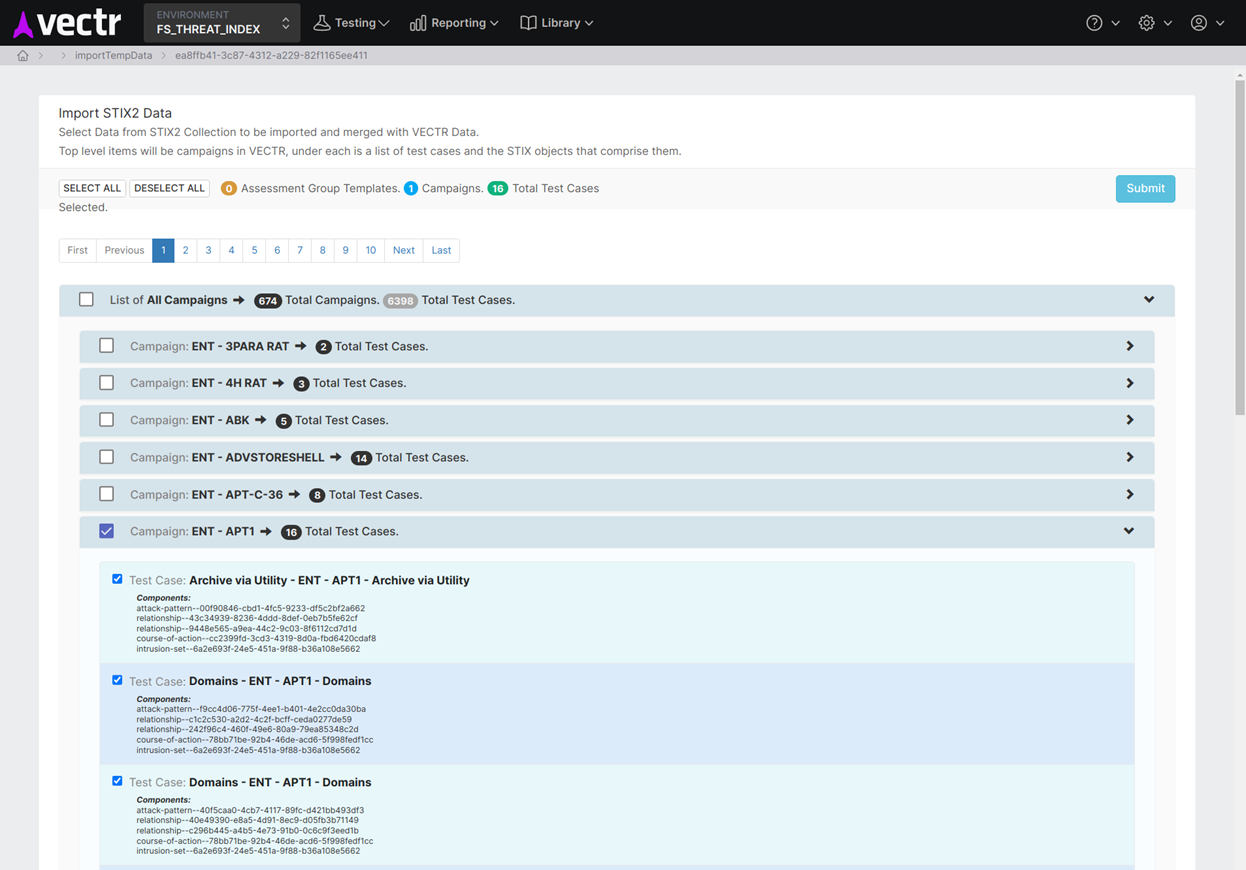
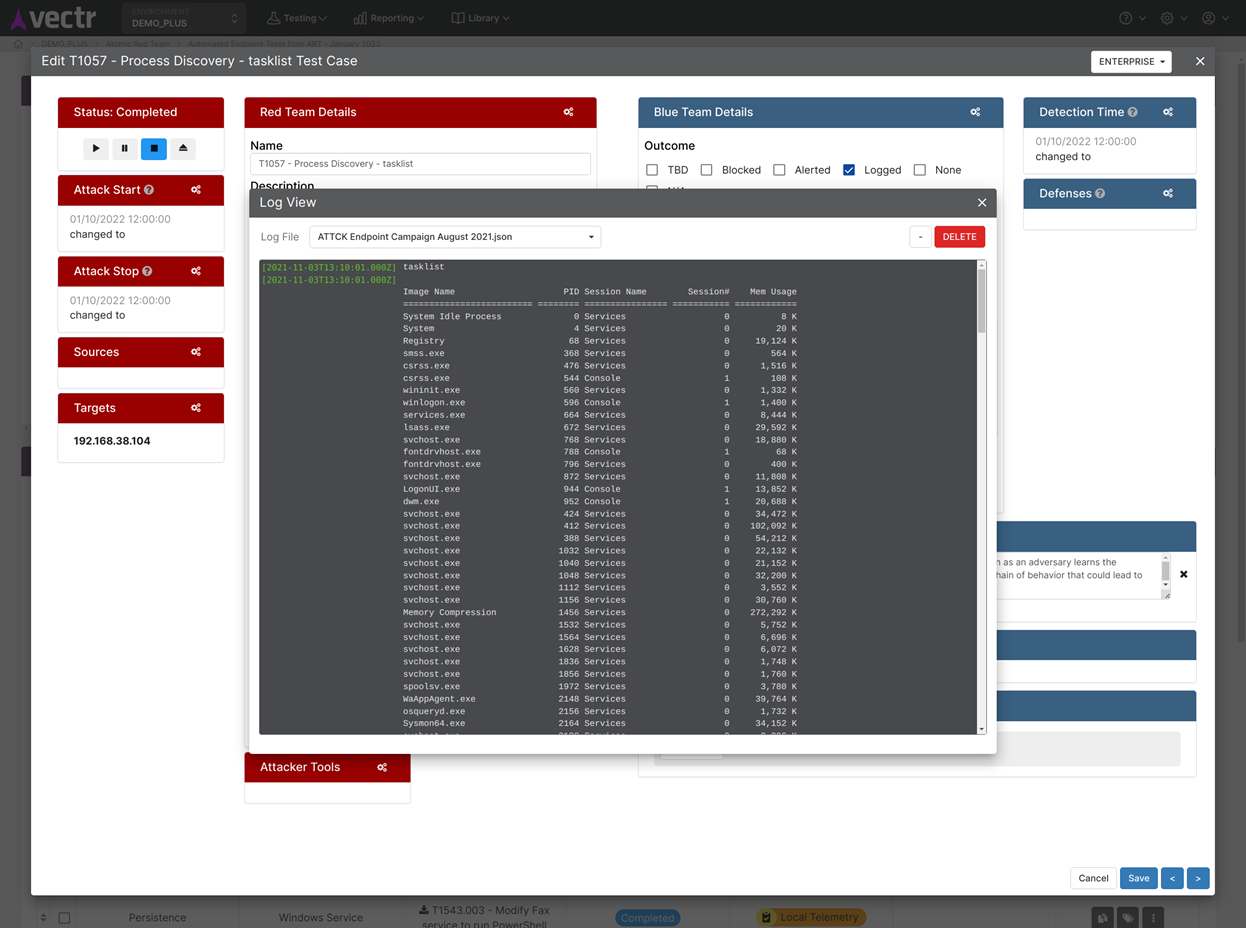
VECTR Heatmap

Resilience Trending

Data Import

Attack Escalation Graph

Attack Automation

Getting Started

See the Install Guide.

Supported Platforms

Server Operating Systems

  • Current Ubuntu LTS (22.04)

We limit community support to this runtime environment. If you encounter issues feel free to open an issue on GitHub or join us on Discord.

VECTR should run in most containerization environments. If in enterprise we recommend consulting your Infrastructure/Containerization team for guidance. Or reach out directly via the contact form for our SaaS offerings.

Please read the instructions carefully for Upgrading a VECTR instance.

Browsers

Most modern browsers, such as Chrome, Firefox, Edge (Chromium) up to two prior releases are supported. We recommend using the latest of either:
  • Chrome
  • Firefox

General

  • Presentation layer built on Vue 3 with some legacy AngularJS components.
  • GraphQL API
  • Support for TLS endpoints (VECTR Community Edition will auto-generate an untrusted self-signed cert or can be supplied with certs).

Security Risk Advisors

License

Please see the EULA

Atomic Red LICENSE

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →