#1

 mevislobo2006/threatripper
Offline heuristic analyzer that scores suspicious SMS, chat messages and links for scam and phishing indicators, explaining each warning sign with…
 kaleth4/cve-2022-30190
Automated PoC exploit for CVE-2022-30190 (Follina) that generates malicious RTF/DOCX files abusing MSDT protocol to execute arbitrary commands and…
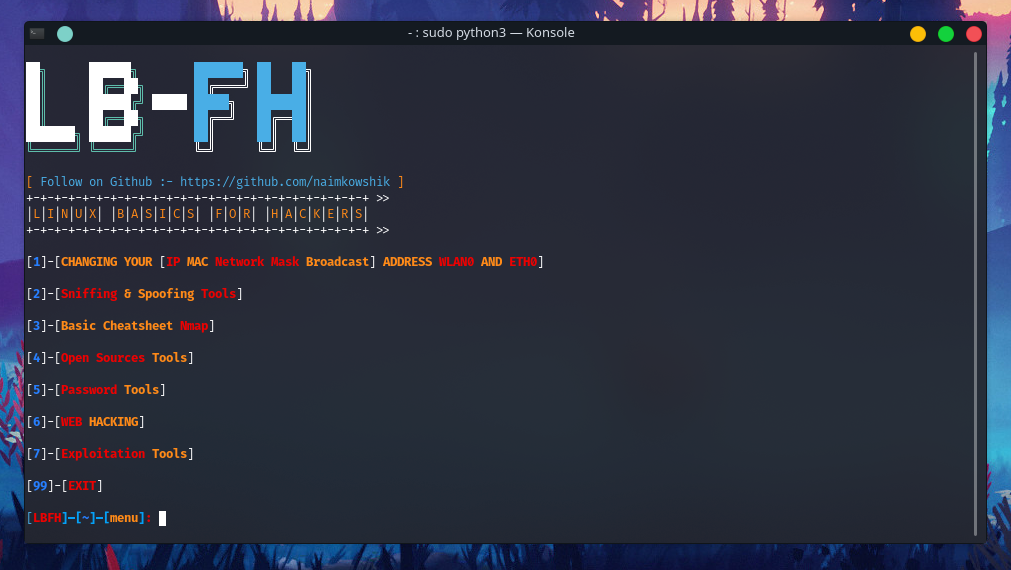 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 pauleprichna/cybersecurity
French cybersecurity lab coursework covering network recon, DDoS, brute force, phishing, Wi-Fi attacks, malware generation, MITM, and a librsvg…
 llcforge/cve-2026-117517
Python PoC for CVE-2026-117517, an Apache Tomcat jsessionid leading-slash open redirect (CWE-601); checks targets and generates crafted redirect URLs.
 llcforge/cve-2026-124194
Python PoC for CVE-2026-124194: crafts Outlook .msg files with RTF INCLUDEPICTURE UNC paths to capture NetNTLMv2 hashes, with SMB server, relay, and…
 ghost-bx1/cve-2026-124194-outlook-ntlm-hash-leak
PoC and exploit for CVE-2026-124194: generates crafted Outlook .msg files with UNC INCLUDEPICTURE references and runs an SMB listener to capture…
 sadaqaty/cve-2026-1277
Python 3 proof-of-concept for CVE-2026-1277, an unauthenticated open redirect in the WordPress URL Shortify plugin (<=1.12.1) via the redirect_to…
 sadaqaty/cve-2026-1296
Python 3 PoC and detection tool for CVE-2026-1296, an unauthenticated open redirect in the WordPress Frontend Post Submission Manager Lite plugin (<=…
 geopetro/anglerphish
Feature-rich Gophish fork for managing phishing simulation campaigns, with expanded phishing vectors, improved reporting, and API enhancements for…
 maxprog-svg/cve-2026-21509
Exploit toolkit for CVE-2026-21509 Microsoft Office RTF/OLE RCE: builds crafted RTF payloads, serves OLE stage resources, and captures reverse TCP…
 0xanalyst/email-security-header-analyzer
Email header & .eml analyzer for SPF/DKIM/DMARC, spoofing and phishing. Runs 100% in your browser, so your emails are never uploaded.
 novacode1337/eviltwin
Practical defense guidelines against Evil Twin attacks in public Wi-Fi — full research cycle: threat analysis, isolated lab simulation (Kali Linux /…
 entropq2/eviltwin
Practical defense guidelines against Evil Twin attacks in public Wi-Fi — full research cycle: threat analysis, isolated lab simulation (Kali Linux /…
 0-am-x/huntbug-behind_the_curtain
Passive OSINT and evidence archive for huntbug.com - observed fraud indicators on a suspected fake bug-bounty platform (not a legal verdict).
 brn1337/mailauthcheck
Bash script that audits SPF, DKIM, DMARC, DNSSEC, MTA-STS and DNS hygiene to grade a domain's exposure to email spoofing and phishing.
 cybersecurity91/redforge
Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.