
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
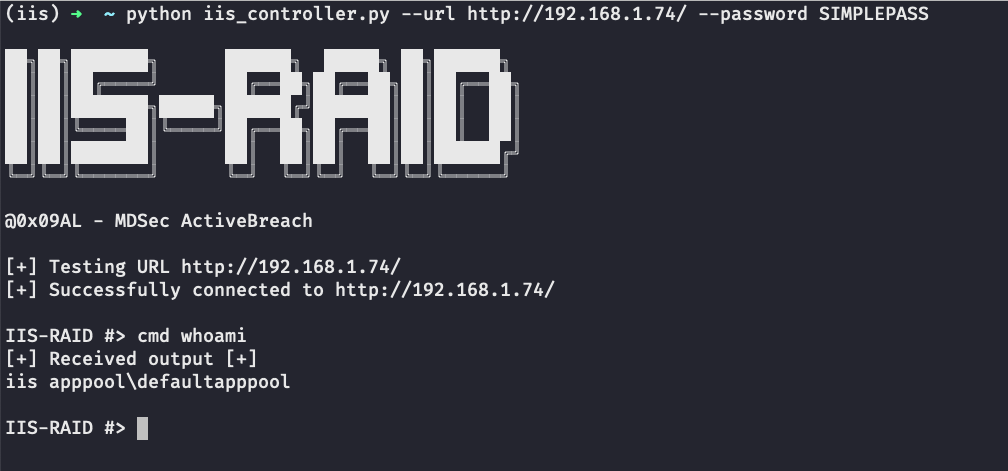 0x09al/iis-raid
A native backdoor module for Microsoft IIS (Internet Information Services)
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 kkevsterrr/backdoorme
powerful auto-backdooring utility
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 quantumcore/paradoxiarat
ParadoxiaRat : Native Windows Remote access Tool.
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 mwsrc/plasmarat
Remote Access Trojan(RAT), Miner, DDoS
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 mvelazc0/purplesharp
PurpleSharp is a C# adversary simulation tool that executes adversary techniques with the purpose of generating attack telemetry in monitored Windows…
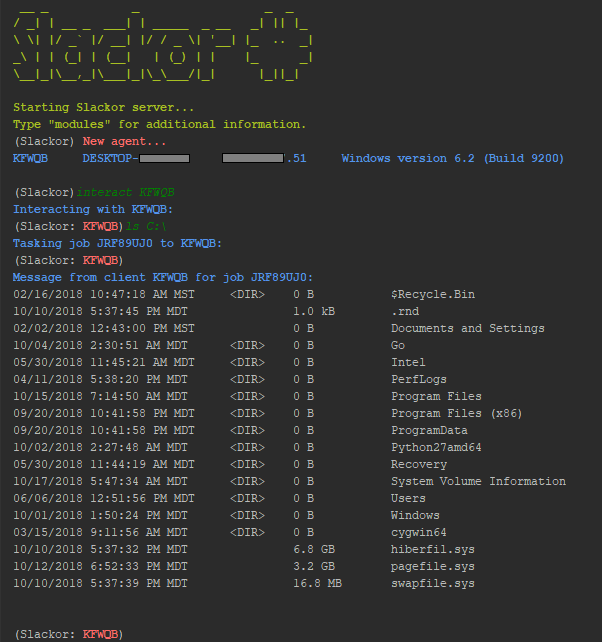 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 nickvourd/com-hunter
Windows COM hijacking persistence tool with search, classic, Task Scheduler, and TreatAs modes. Available as .NET executable and Cobalt Strike BOF…
 outflanknl/sharphide
Tool to create hidden registry keys.
 0xthirteen/sharpstay
.NET tool for installing Windows persistence via registry keys, scheduled tasks, services, WMI events, COM hijacks, and LNK backdoors, supporting…








