
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 aaaddress1/skrull
Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
 bobtheshoplifter/spring4shell-poc
Spring4Shell Proof Of Concept/And vulnerable application CVE-2022-22965
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 d00mfist/mystikal
macOS Initial Access Payload Generator
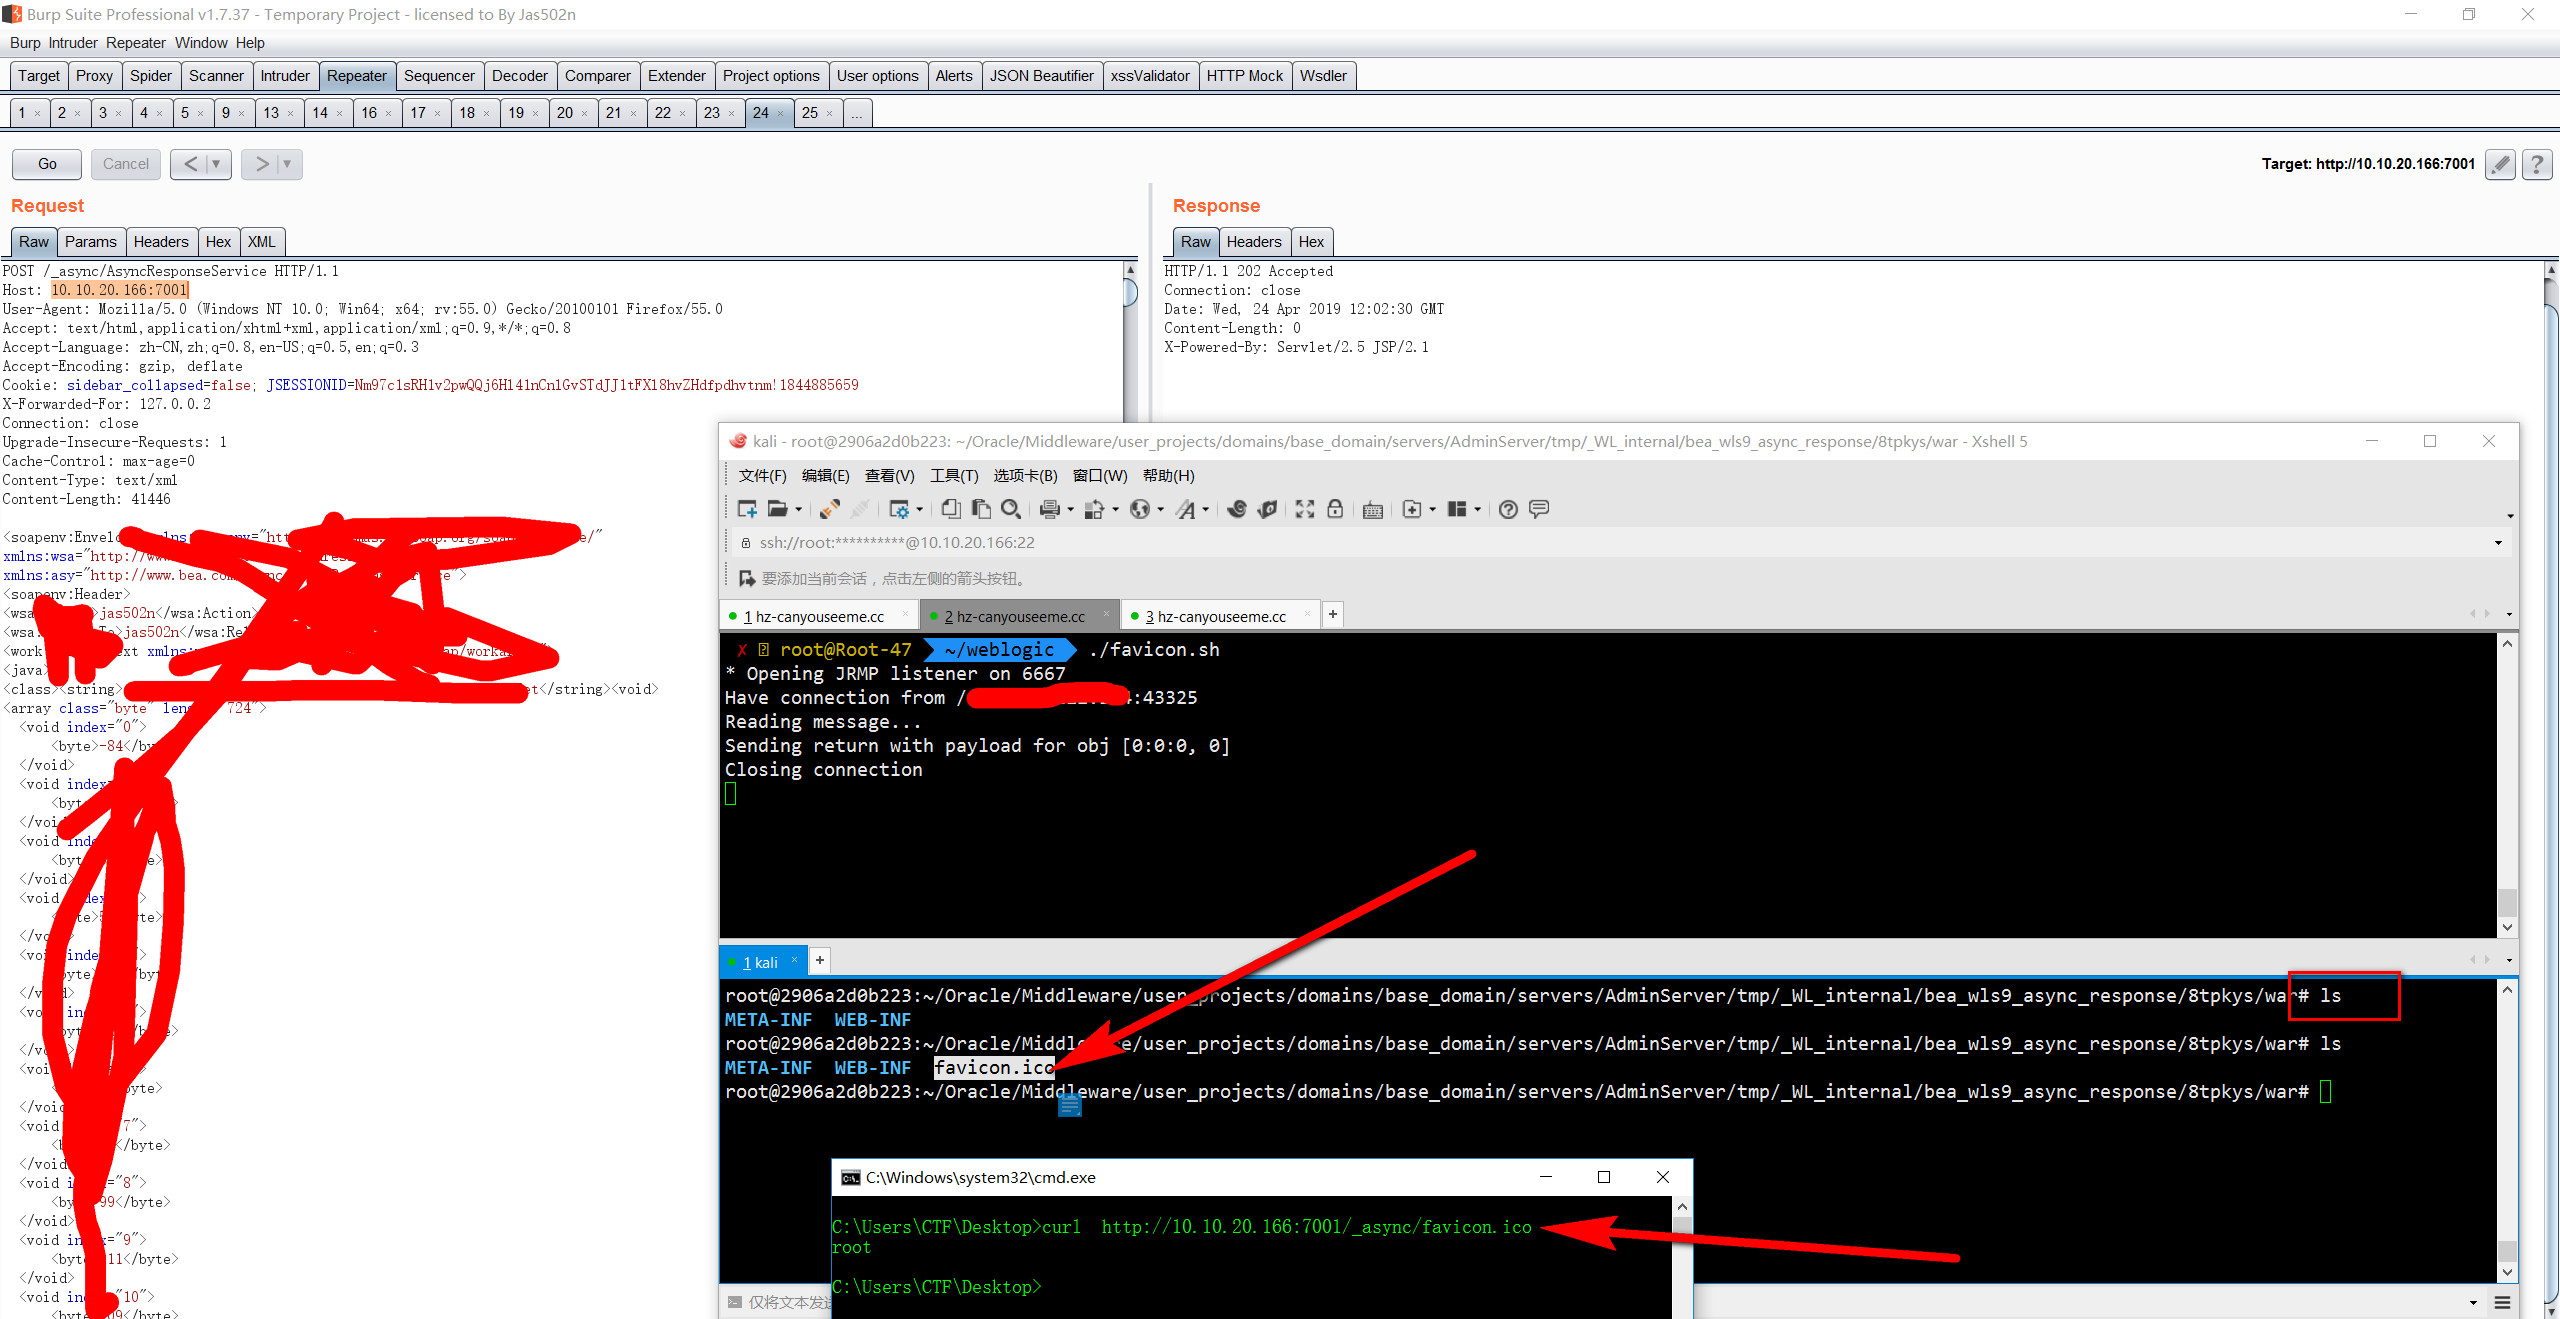 jas502n/cnvd-c-2019-48814
WebLogic wls9-async反序列化远程命令执行漏洞
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 thegejr/springshell
Spring4Shell - Spring Core RCE - CVE-2022-22965
 awakened1712/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 yt1g3r/cve-2020-0688_exp
CVE-2020-0688_EXP Auto trigger payload & encrypt method
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 cyberstruggle/l4sh
Log4Shell RCE Exploit - fully independent exploit does not require any 3rd party binaries.
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
 hackerschoice/bincrypter
Pack/Encrypt/Obfuscate ELF + SHELL scripts
 bhdresh/cve-2017-8759
Exploit toolkit CVE-2017-8759 - v1.0 is a handy python script which provides pentesters and security researchers a quick and effective way to test…








