
 #1
Tools for analyzing network traffic and communication logs to investigate security incidents.
Kitploit recommended

 google/gopacket
Provides packet processing capabilities for Go
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
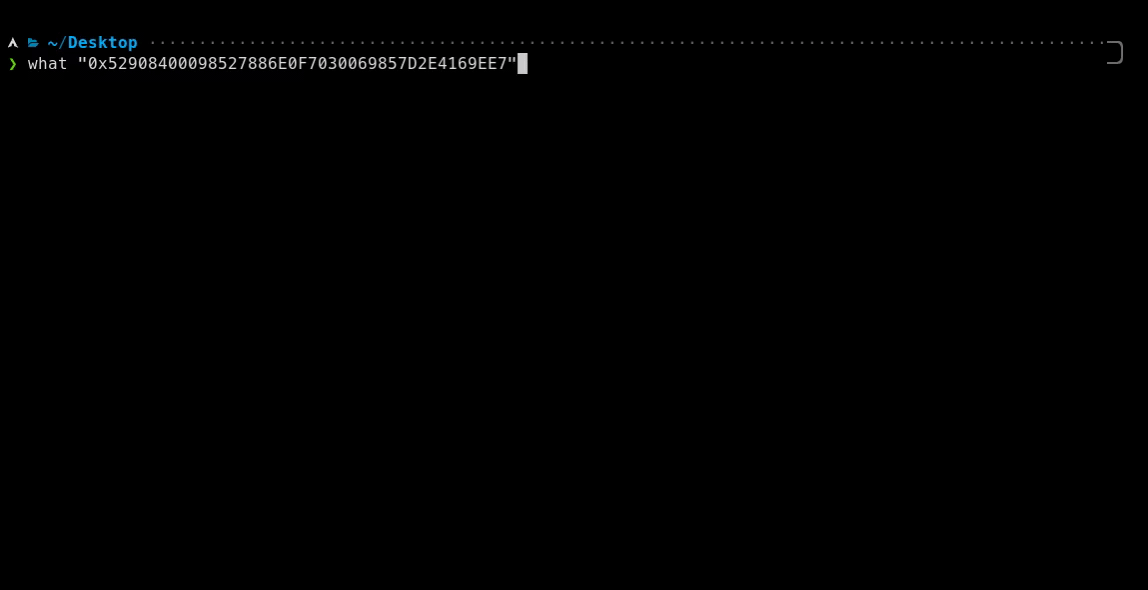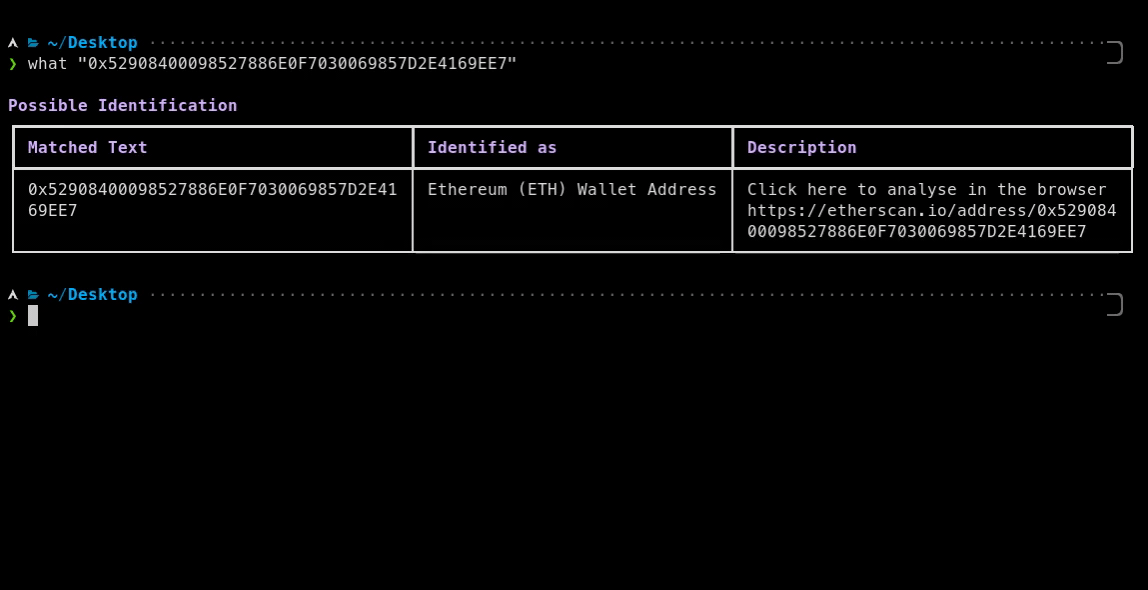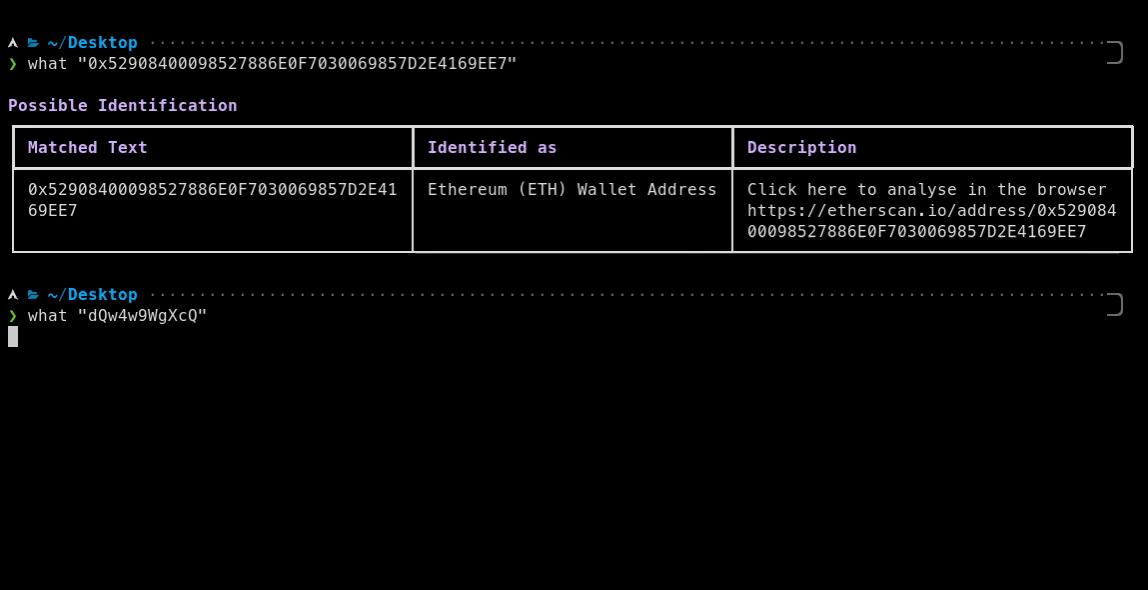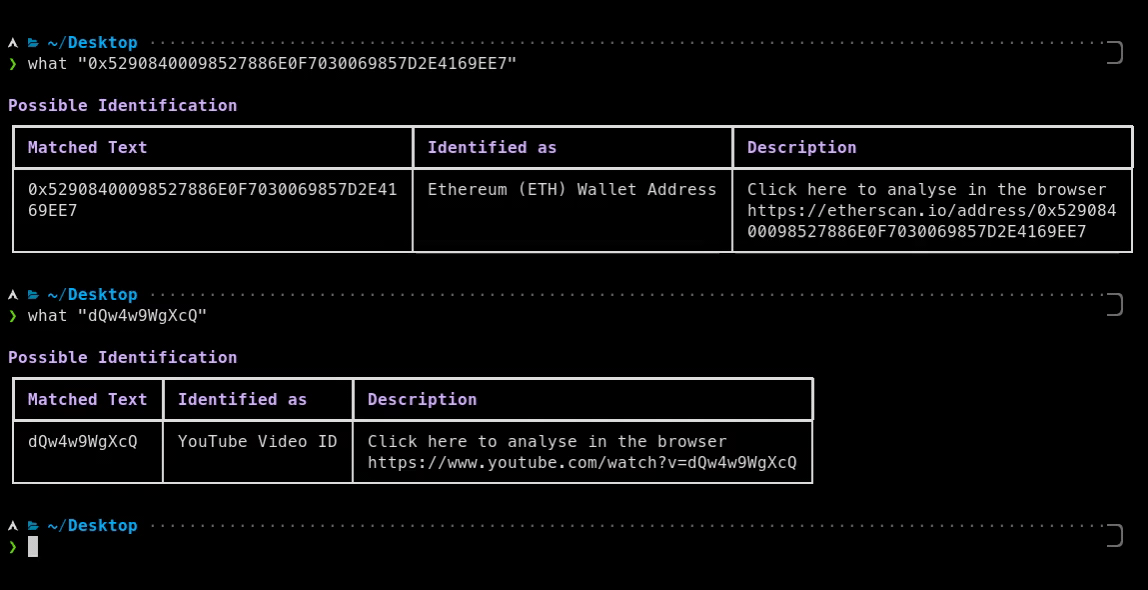 bee-san/pywhat
🐸 Identify anything. pyWhat easily lets you identify emails, IP addresses, and more. Feed it a .pcap file or some text and it'll tell you what it…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 p1sec/qcsuper
QCSuper is a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G radio frames, among other things.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 mattnotmax/cyberchef-recipes
A list of cyber-chef recipes and curated links
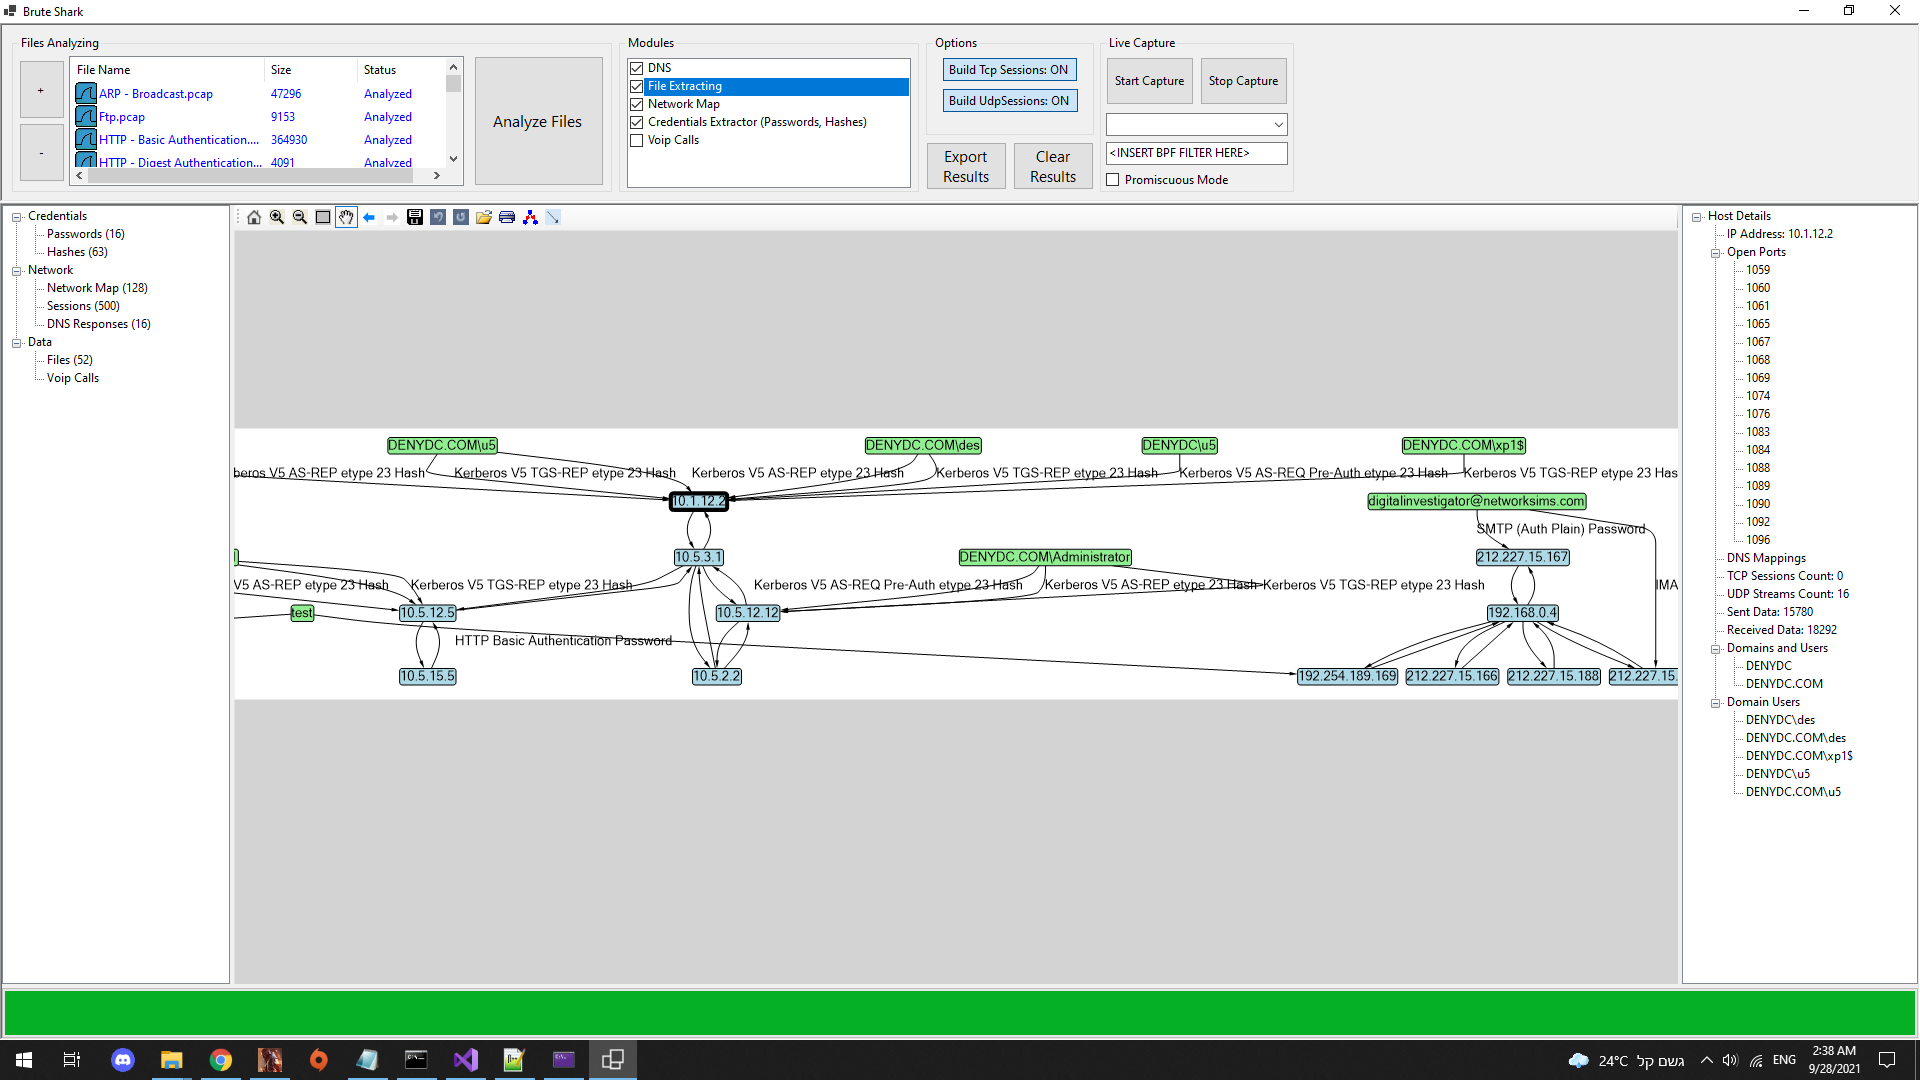 odedshimon/bruteshark
Network Analysis Tool
 kiminewt/pyshark
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
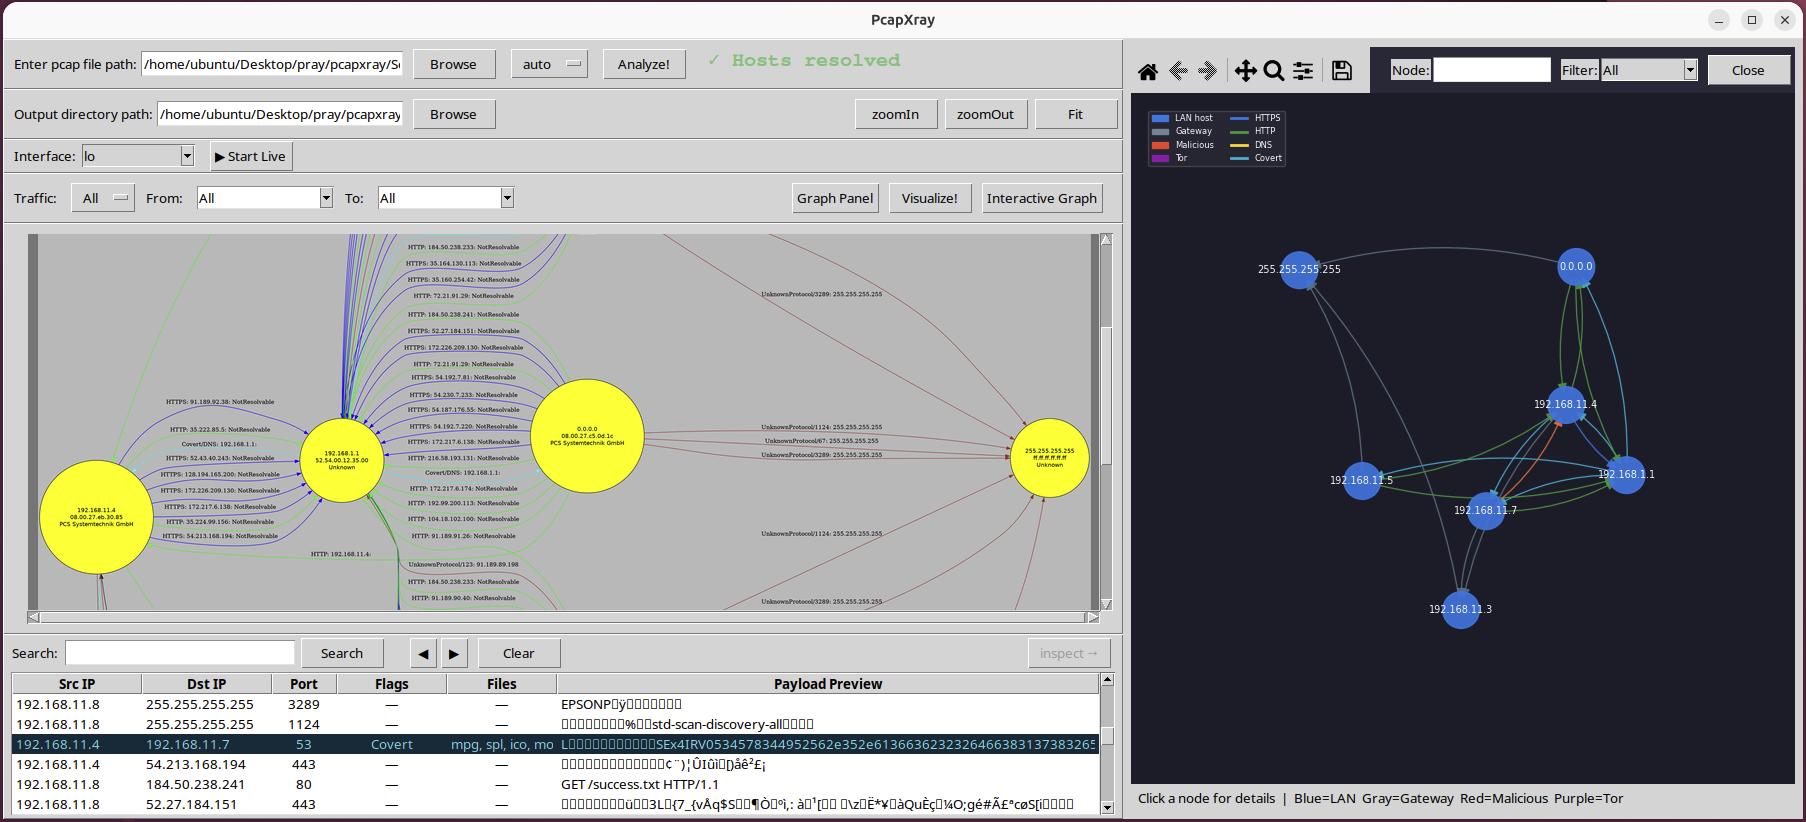 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
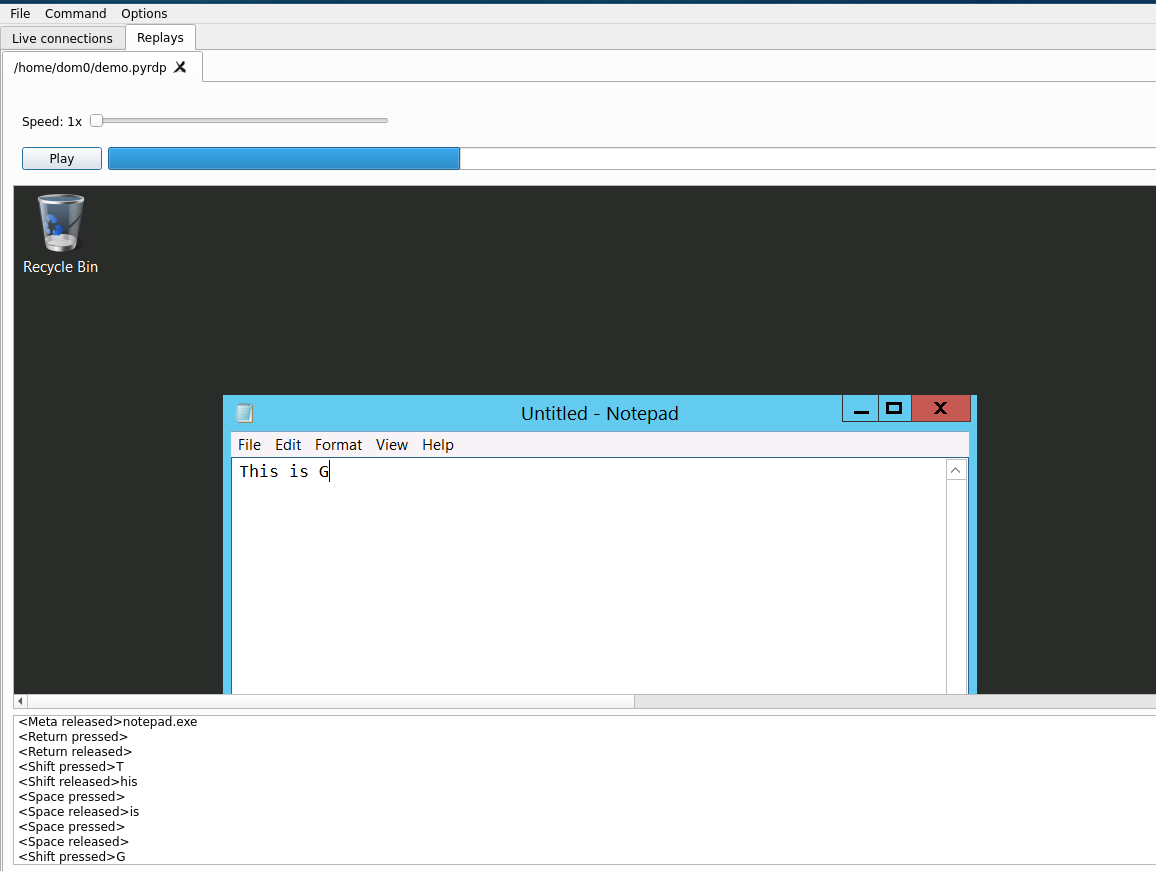 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup






