#1
Tools for analyzing RAM dumps to find running processes, network connections, and hidden malware.
Kitploit recommended
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 peterpan0927/cve-2017-2370
on Mac 10.12.2
 jailbreaks/empty_list
empty_list - exploit for p0 issue 1564 (CVE-2018-4243) iOS 11.0 - 11.3.1 kernel r/w
 robertmotr/zirconium
DLL-injectable internal game cheat for Plutonium BO2 zombies
 spawn451/cve-2025-8061-exploit
Exploit LnvMSRIO.sys vulnerable driver
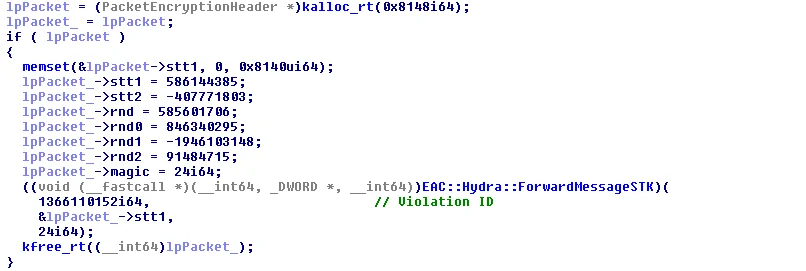 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
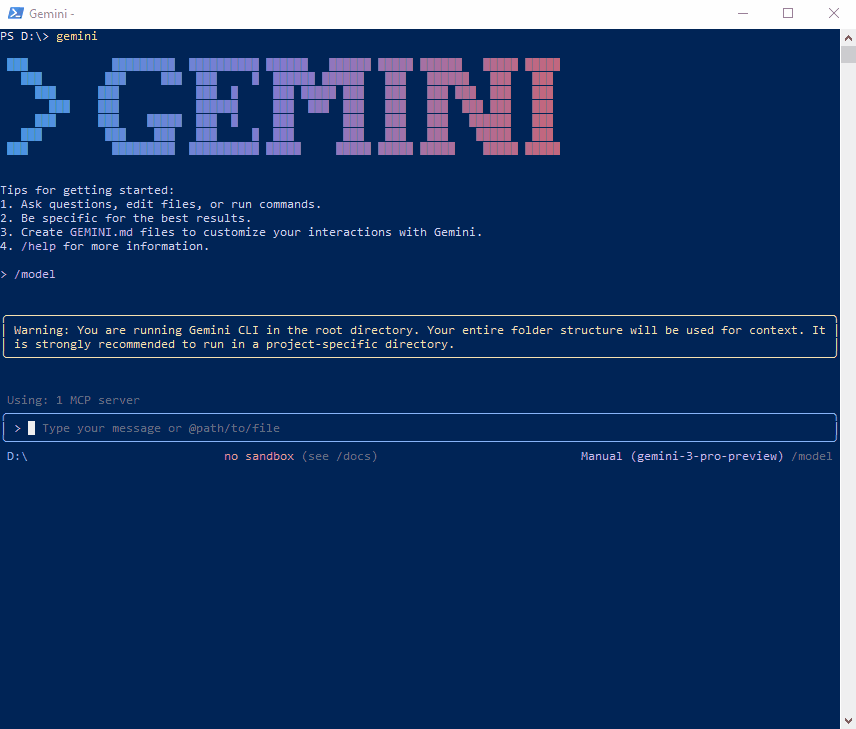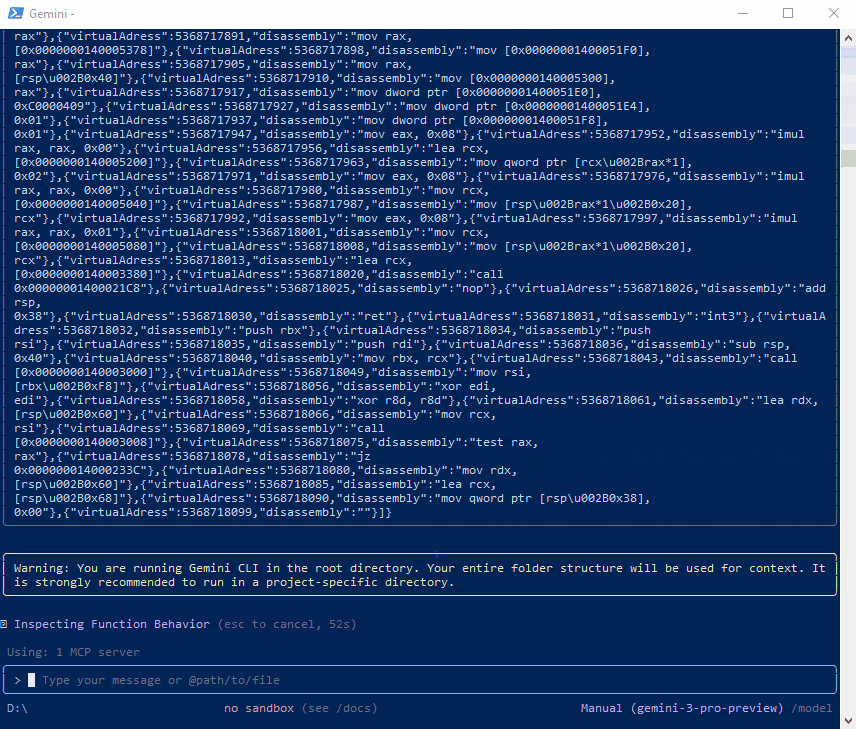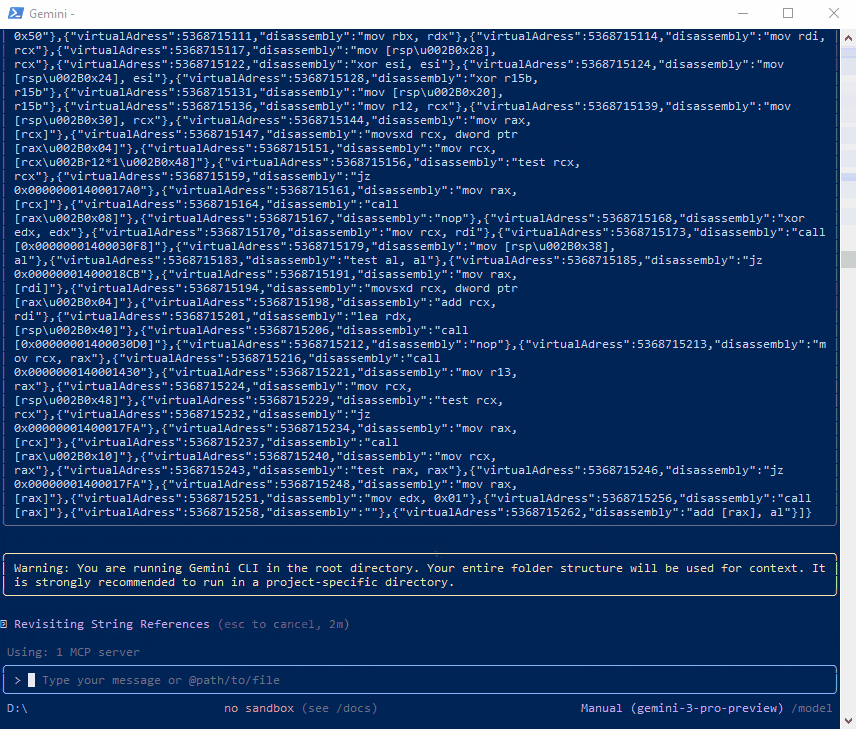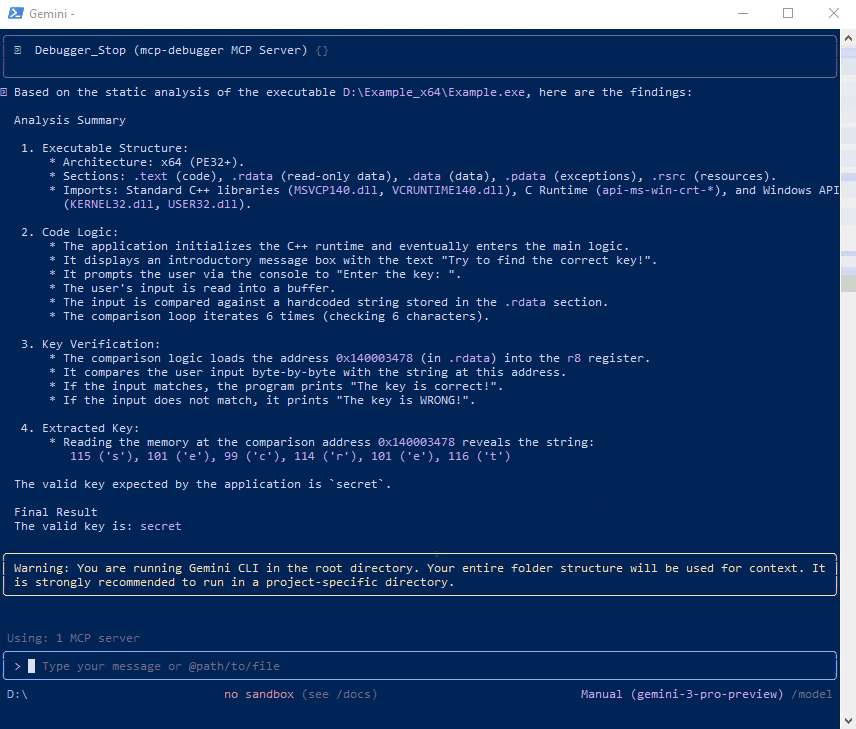 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 nccgroup/libmempool
Heap analysis tooling for mempool
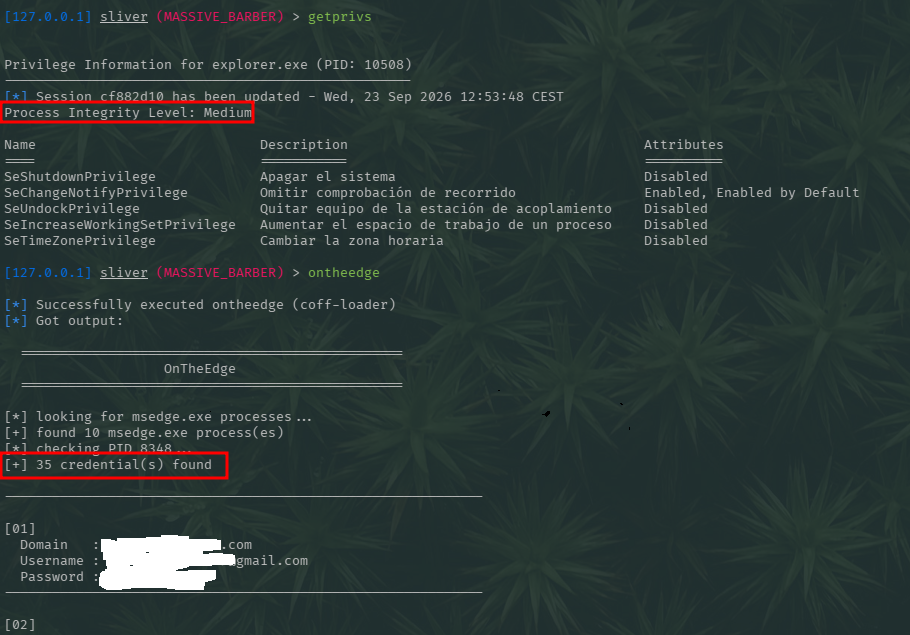 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 watchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451
Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
 whu-enjoy/cve-2016-5195
这里保留着部分脏牛漏洞的利用代码
 s1lkys/cve-2023-30367-mremoteng-password-dumper
Original PoC for CVE-2023-30367
 0xcyberstan/cve-2026-46215-poc
Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…
 manizada/pppoeject
Linux kernel local privilege escalation PoC for CVE-2026-68121, chaining PPPoE, FUSE, and IP6GRE to corrupt kernel memory and gain root.
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC