
 #1
Tools for analyzing RAM dumps to find running processes, network connections, and hidden malware.
Kitploit recommended
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 t-tani/yama-dev
Yet Another Memory Analyzer for malware detection
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
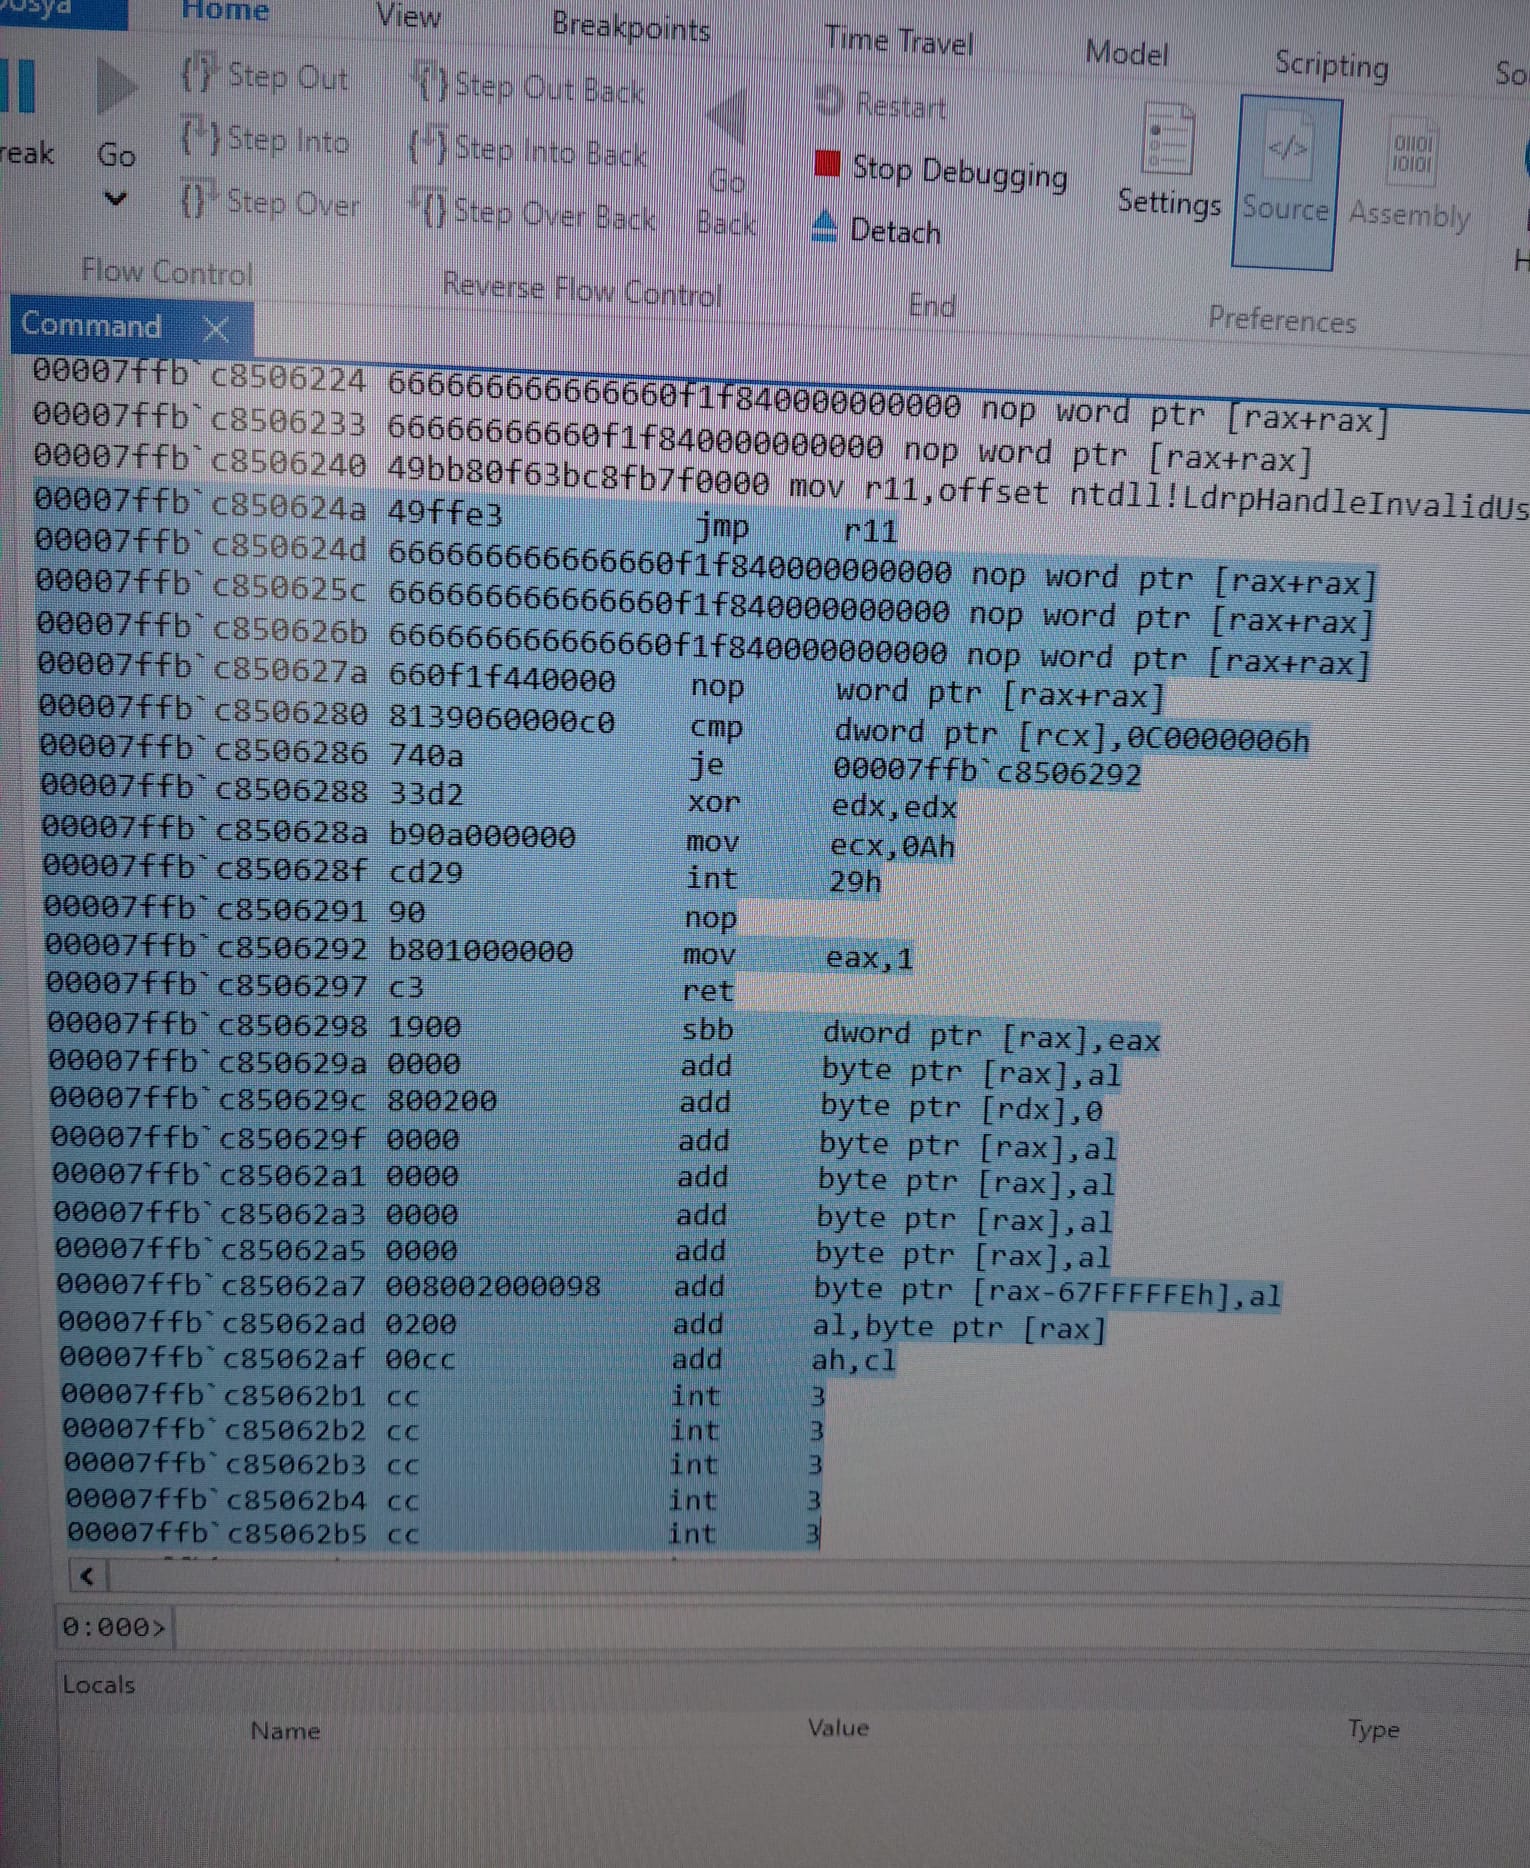 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 hdbreaker/webkit-cve-2016-4622
Deep-dive analysis and exploitation walkthrough of CVE-2016-4622, a WebKit JavaScriptCore memory disclosure vulnerability via Array.slice TOCTOU race…
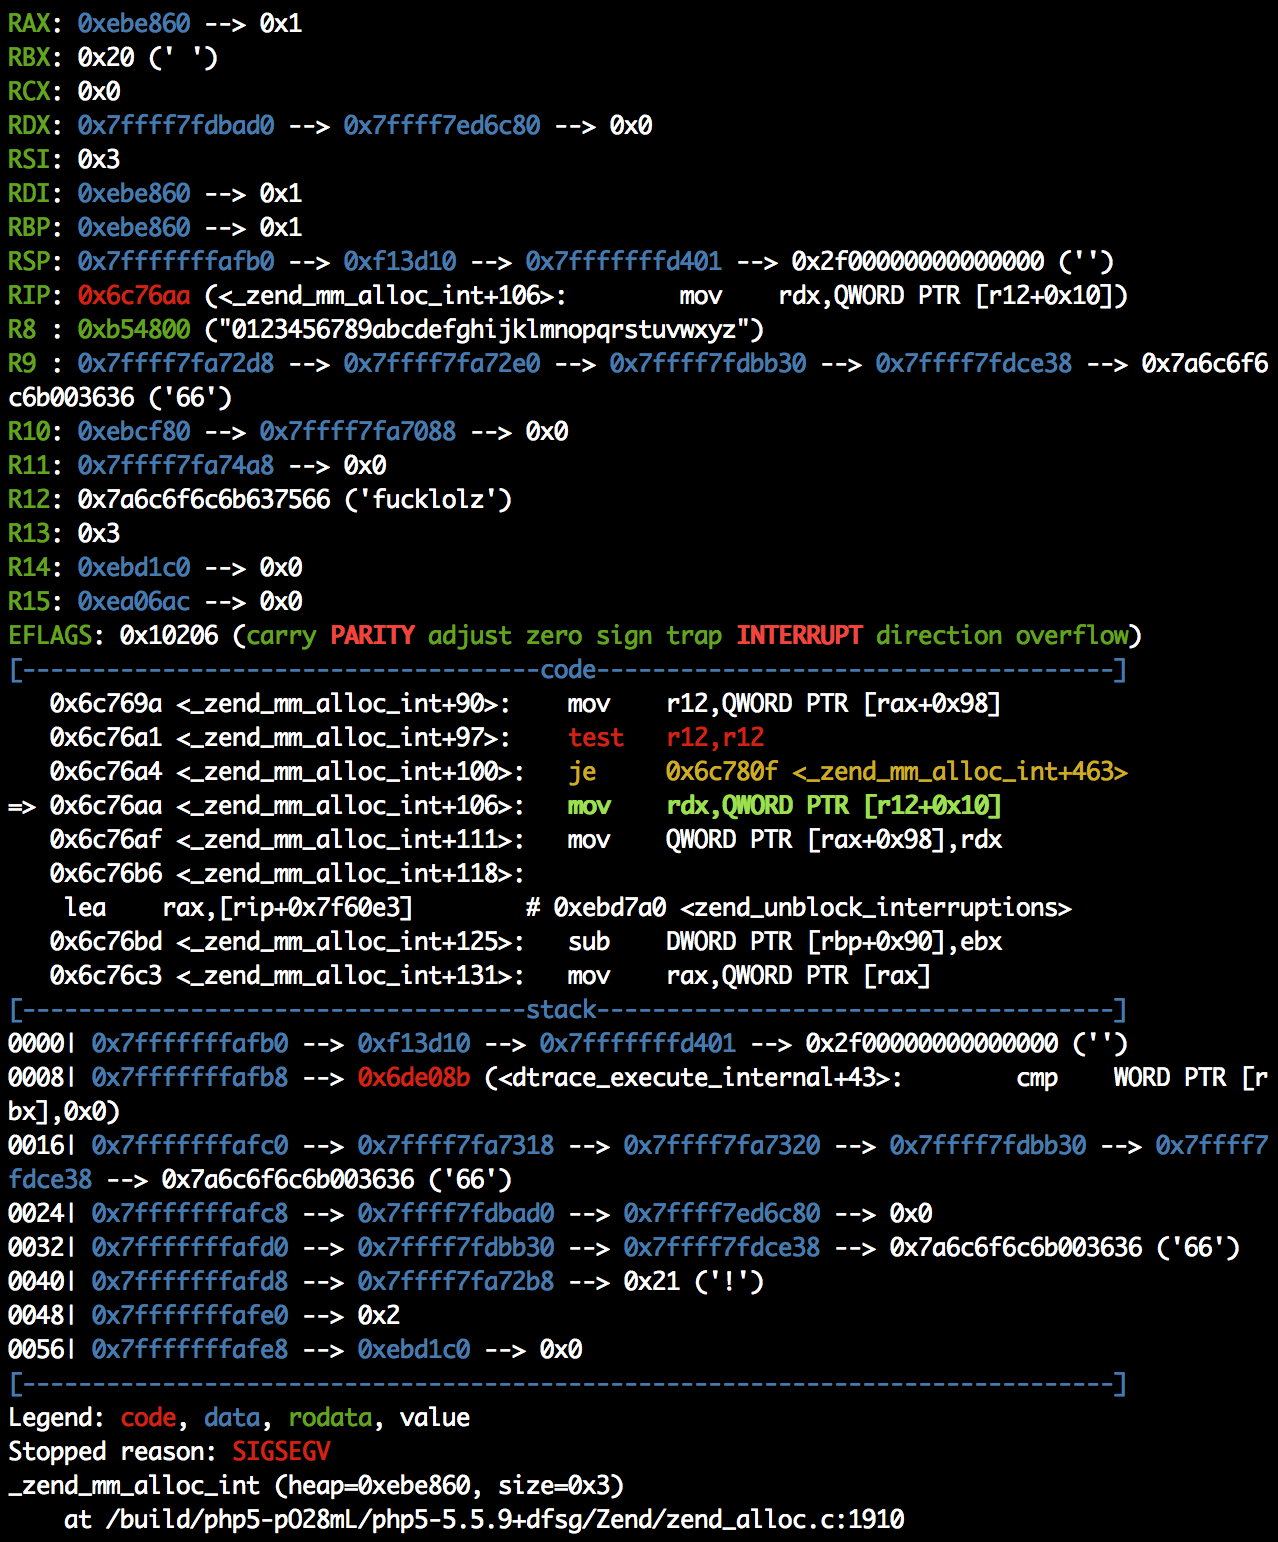 peternguyen93/cve-2016-3141
CVE-2016-3141
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 ping-2o/ios.cve-2026-84616-84607
research on finding the bug and fix of CVE-2026-84616 and CVE-2026-84607
 xyjl-ly/cve-2021-22555-exploit
CVE-2021-22555 Exploit
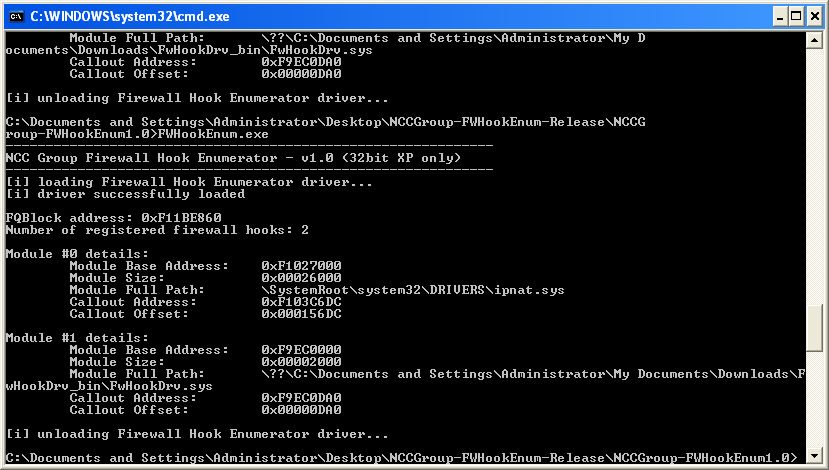 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 ntfargo/uaf-2023-28205
PoC CVE-2023-28205: Apple WebKit Use-After-Free Vulnerability
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 nccgroup/memaddressanalysis
Research project related to memory address analysis
 alonhr/notsecdrv
A PoC for CVE-2018-7249
 feliam/cve-2013-2730
Proof-of-concept exploit for CVE-2013-2730, demonstrating a memory corruption vulnerability with a C-based implementation for security research and…








