
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Malware Analysis — Page 84 | Kitploit
Categories

Malware Analysis

Tools for dissecting, understanding, and reverse engineering malicious software behavior.

Kitploit recommended
Top tools

10 selected
yara-x preview#1

yara-x

GitHubvirustotal/yara-x
1.2k11h 12m ago
capa preview#3

capa

GitHubmandiant/capa
6.1k2 days ago
flare-floss preview#4

flare-floss

GitHubmandiant/flare-floss
4.1k1 day ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k5 days ago
radare2 preview#6

radare2

GitHubradareorg/radare2
24.5k7h 56m ago
ghidra preview#7

ghidra

GitHubnationalsecurityagency/ghidra
71.1k2 days ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k8h 21m ago
theZoo preview#9

theZoo

GitHubytisf/thezoo
13.3k1 month ago
flare-vm preview#10

flare-vm

GitHubmandiant/flare-vm
8.9k16 days ago
IntelOwl preview#11

IntelOwl

GitHubintelowlproject/intelowl
4.7k1 month ago
NewestRelevanceMost popularRecently updated
3803 results
functrace preview

functrace

GitHubinvictus1306/functrace

A function tracer
dynamic-analysis-sandboxingvulnerability-analysisreverse-engineering+2
927 years ago
lst2x64dbg preview

lst2x64dbg

GitHubutkonos/lst2x64dbg

Extract labels from IDA, Ghidra, Binary Ninja, and Relyze files and export x64dbg database. Including radare2 main address.
reverse-engineeringdebuggersutilities-frameworks+1
1142 years ago
Vol3xp preview

Vol3xp

GitHubmemoryforensics1/vol3xp

Volatility Explorer Suit (volatility 3)
memory-forensicsreverse-engineeringforensics+3
703 years ago
CVE-2018-14442 preview

CVE-2018-14442

GitHubpayatu/cve-2018-14442

PoC for Foxit Reader CVE-2018-14442

exploit-frameworksvulnerability-analysisexploitation+3
587 years ago
REW-sploit preview

REW-sploit

GitHubrew-sploit/rew-sploit

Emulate and Dissect MSF and *other* attacks
defensive-toolsbluetooth-securitydynamic-analysis-sandboxing+6
1442 years ago
CodeCut preview

CodeCut

GitHubjhuapl/codecut

A Ghidra plugin for locating object file boundaries.
static-analysisreverse-engineeringbinary-analysis+1
1319 months ago
spybrowse preview

spybrowse

GitHub1d8/spybrowse

Code developed to steal certain browser config files (history, preferences, etc)
persistence-mechanismsdata-exfiltrationinformation-gathering+2
636 years ago
FstHook preview

FstHook

GitHubmalwaretech/fsthook

A library for intercepting native functions by hooking KiFastSystemCall

exploitationreverse-engineeringdebuggers+1
7411 years ago
AntiOreans-CodeDevirtualizer preview

AntiOreans-CodeDevirtualizer

GitHub67-6f-64/antioreans-codedevirtualizer

IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
static-analysiscode-analysisreverse-engineering+5
813 years ago
ccs preview

ccs

GitHubnccgroup/ccs

Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…
static-analysisvulnerability-scannerscode-analysis+2
1143 years ago
Pishi preview

Pishi

GitHubr00tkitsmm/pishi

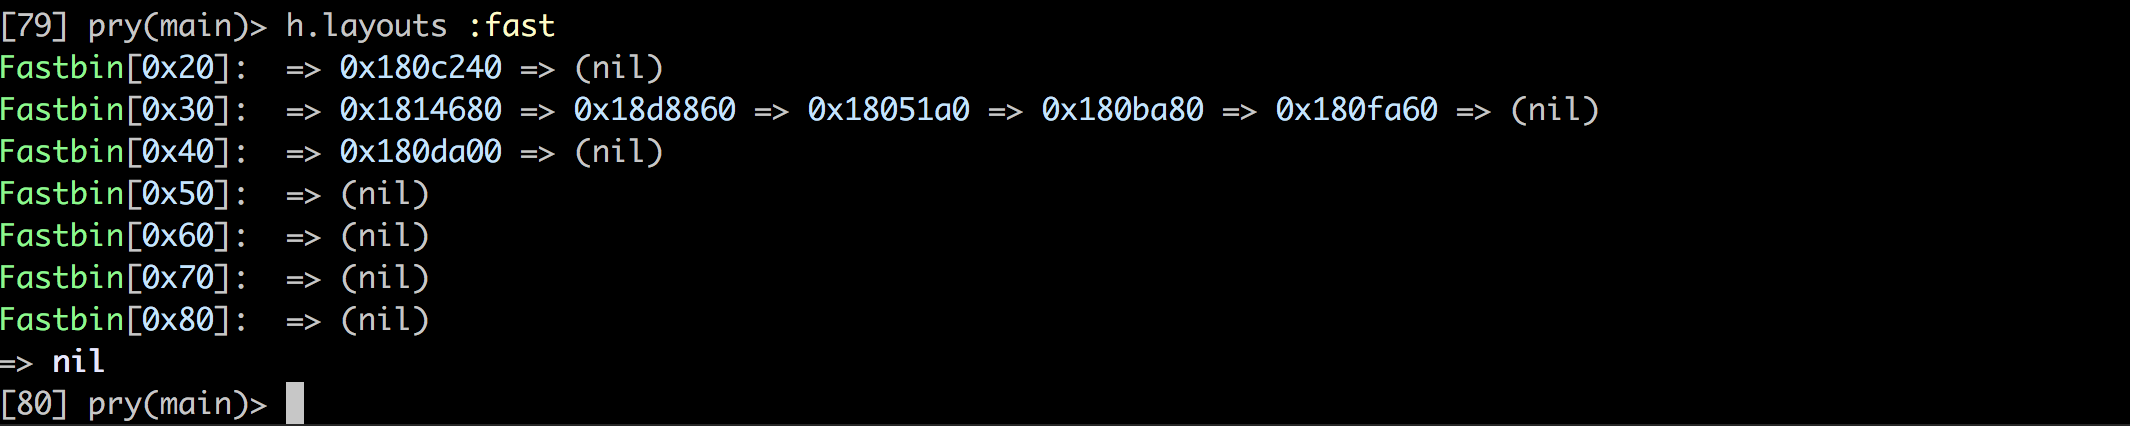
Pishi is a code coverage tool like kcov for macOS.
vulnerability-analysiscode-analysisdynamic-code-analysis+3
762 months ago
heapinfo preview

heapinfo

GitHubdavid942j/heapinfo

An interactive memory info for pwning / exploiting

memory-forensicsexploitationdebuggers+3
983 years ago
SPiCa preview

SPiCa

GitHub0xkirisame/spica

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
defensive-toolsioc-managementforensics+7
1043 months ago
HallWatch preview

HallWatch

GitHubzypherion-technologies/hallwatch

Usermode detector that catches indirect syscalls. Traps Hell's Hall, Tartarus' Gate, RecycledGate, and VEH syscalls & Many more.
defensive-toolsmalware-analysisbinary-analysis+2
874 months ago
cachegrab preview

cachegrab

GitHubnccgroup/cachegrab

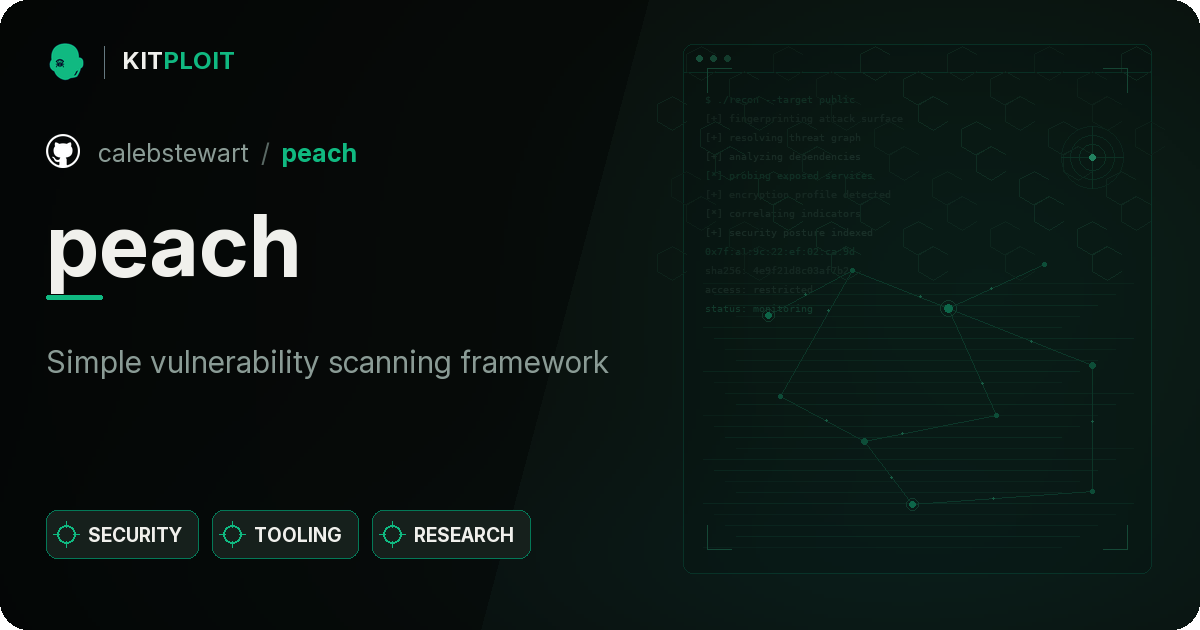
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
embedded-systems-securityexploitationreverse-engineering+3
878 years ago
peach preview

peach

GitHubcalebstewart/peach

Simple vulnerability scanning framework
static-analysisvulnerability-scannerscode-analysis+1
519 years ago
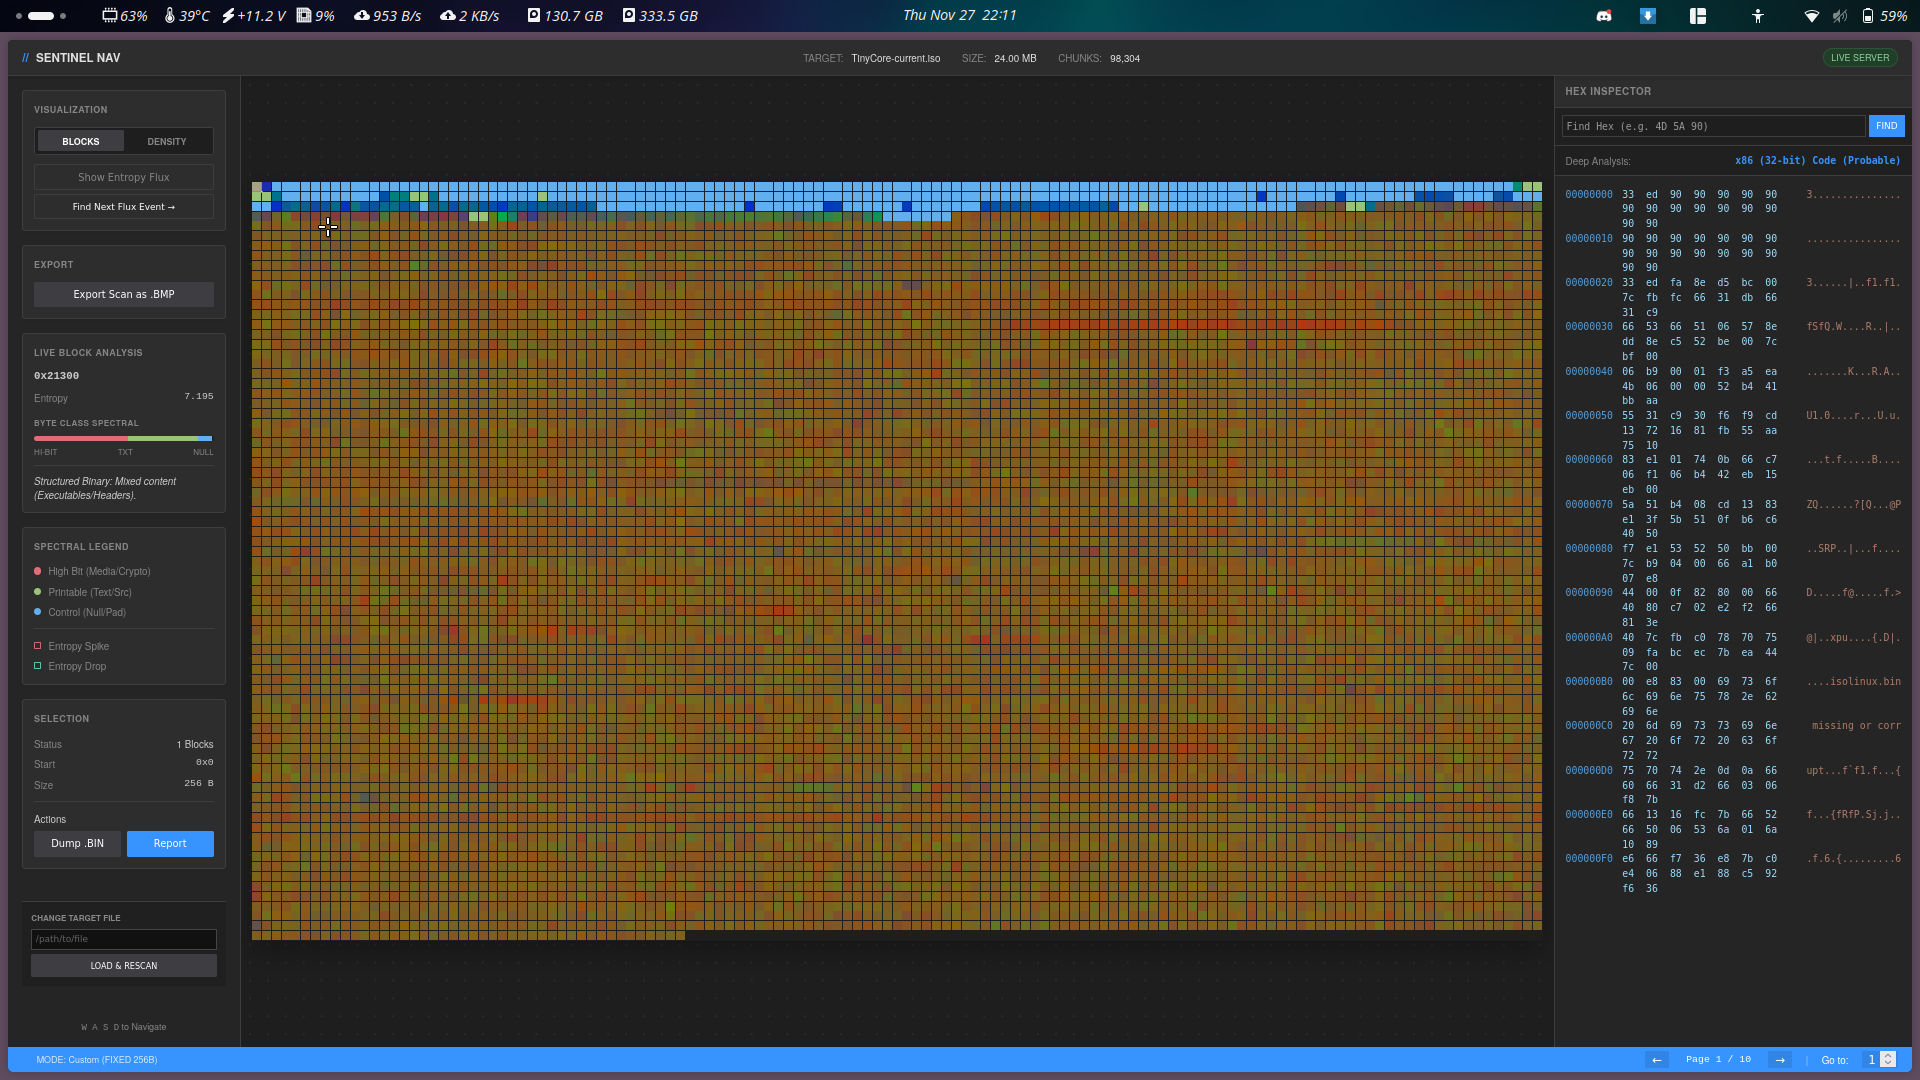
SentinelNav preview

SentinelNav

GitHubsmolfiddle/sentinelnav

SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
memory-forensicsreverse-engineeringforensics+4
14610 months ago
tp-link-decrypt preview

tp-link-decrypt

GitHubwatchfulip/tp-link-decrypt

Decrypt TP-Link Firmware

embedded-systems-securityencryption-decryption-toolsreverse-engineering+4
821 year ago
Previous1…838485…100Next








