#1
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 livecvebench/cve-factory
CVE-Factory
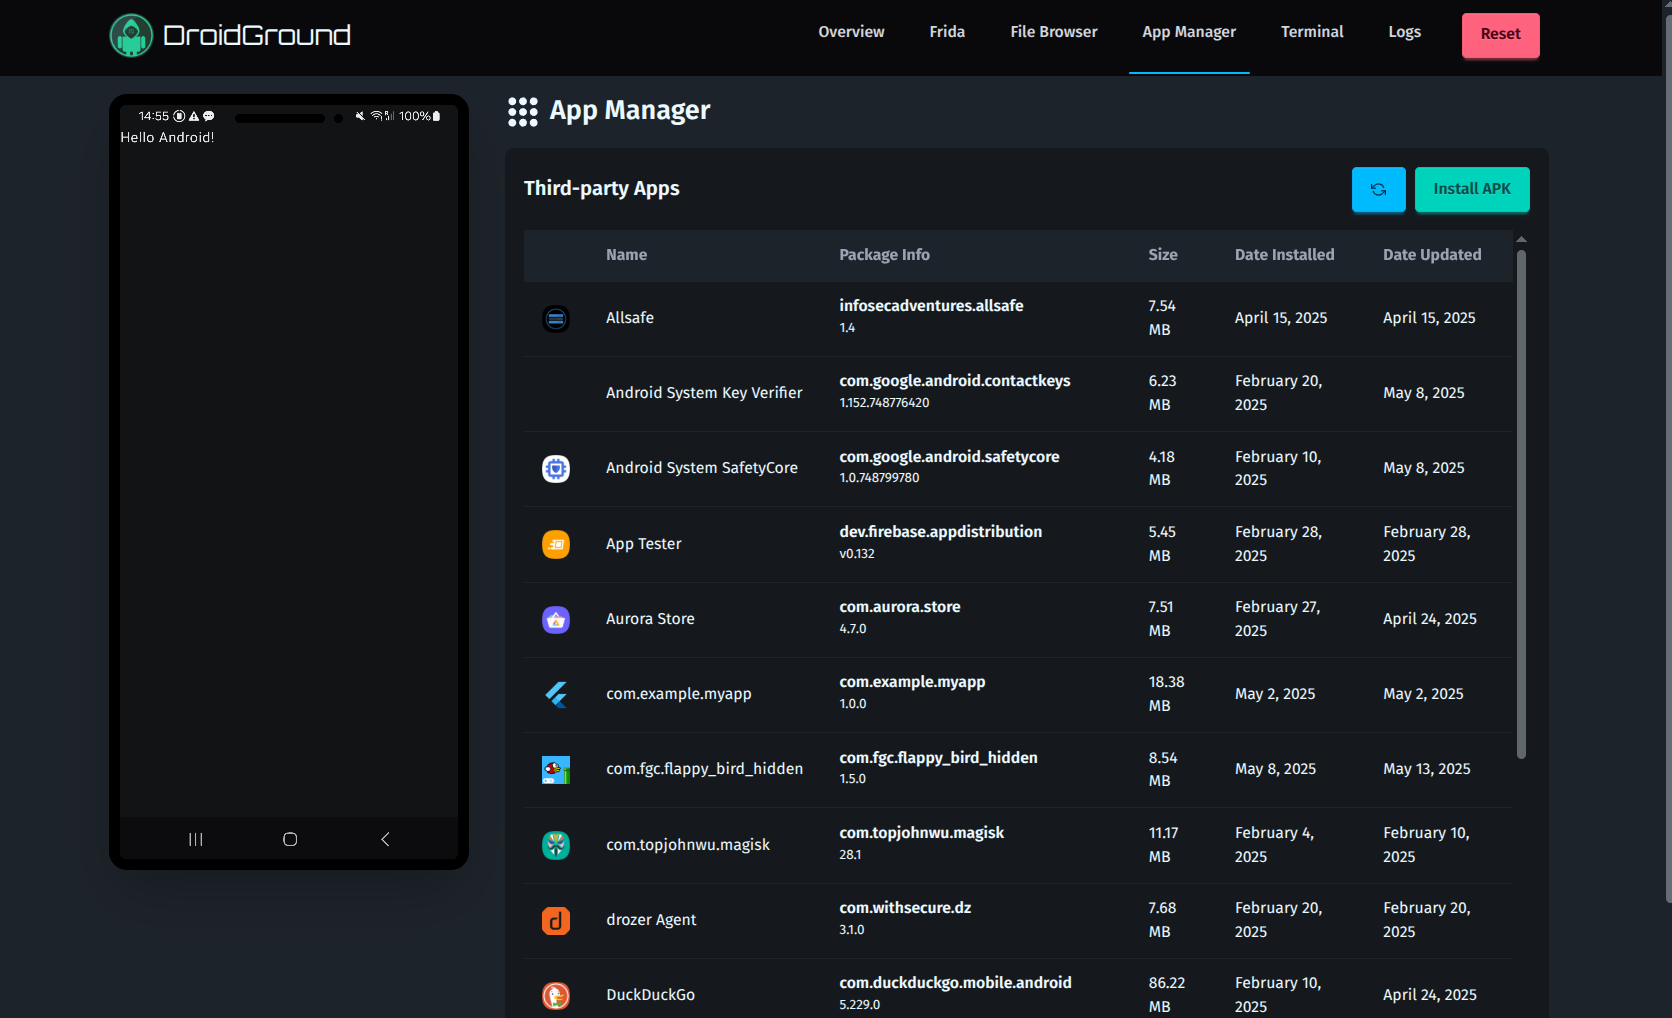 secforce/droidground
A flexible playground for Android CTF challenges.
 deputation/instrumentation_callbacks
A proof of concept demonstrating instrumentation callbacks on Windows 10 21h1 with a TLS variable to ensure all syscalls are caught.
 internetangel/zerocrumb
Dumping App Bound Protected Credentials & Cookies Without Privileges.
 blacknbunny/shellcode2assembly
💻 ARCH : ARM, ARM64, MIPS, PPC, X86
 nccgroup/asafw
Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
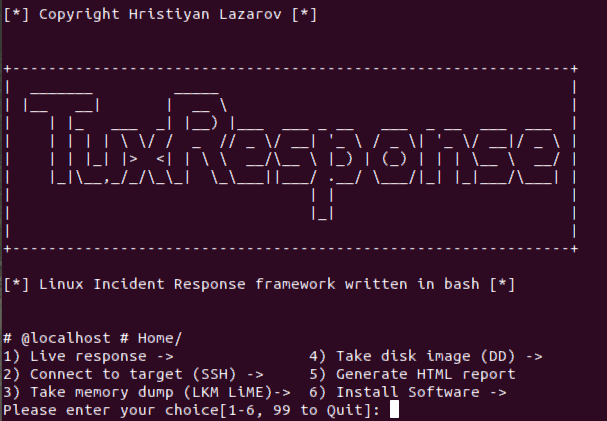 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 sfaci/masc
A Web Malware Scanner
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 security-prince/resources-for-application-security
Some good resources for getting started with application security
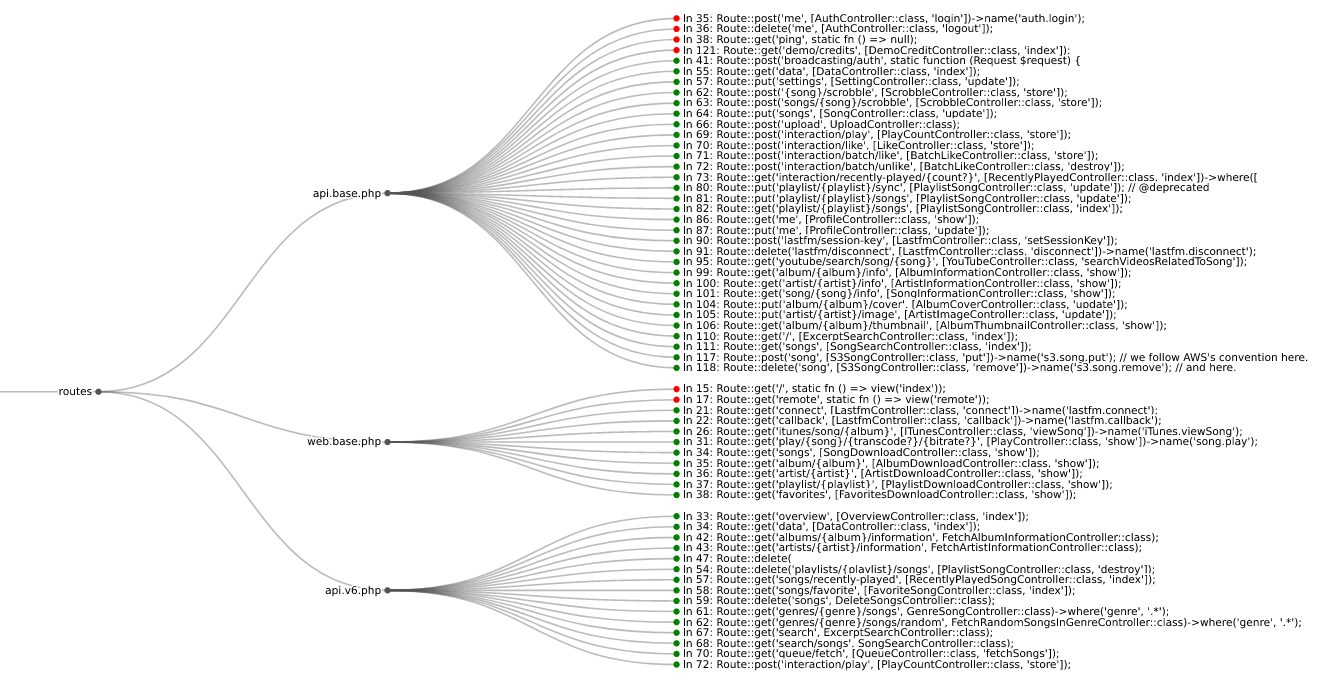 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer