#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 perl-code/cve-2026-5000
Proof-of-concept demonstrating a Windows Defender bypass technique for CVE-2026-5000, intended for controlled testing and defensive research.
 bcoles/rootkit-signal-hunter
Detect Linux rootkits which use signals to elevate process privileges.
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
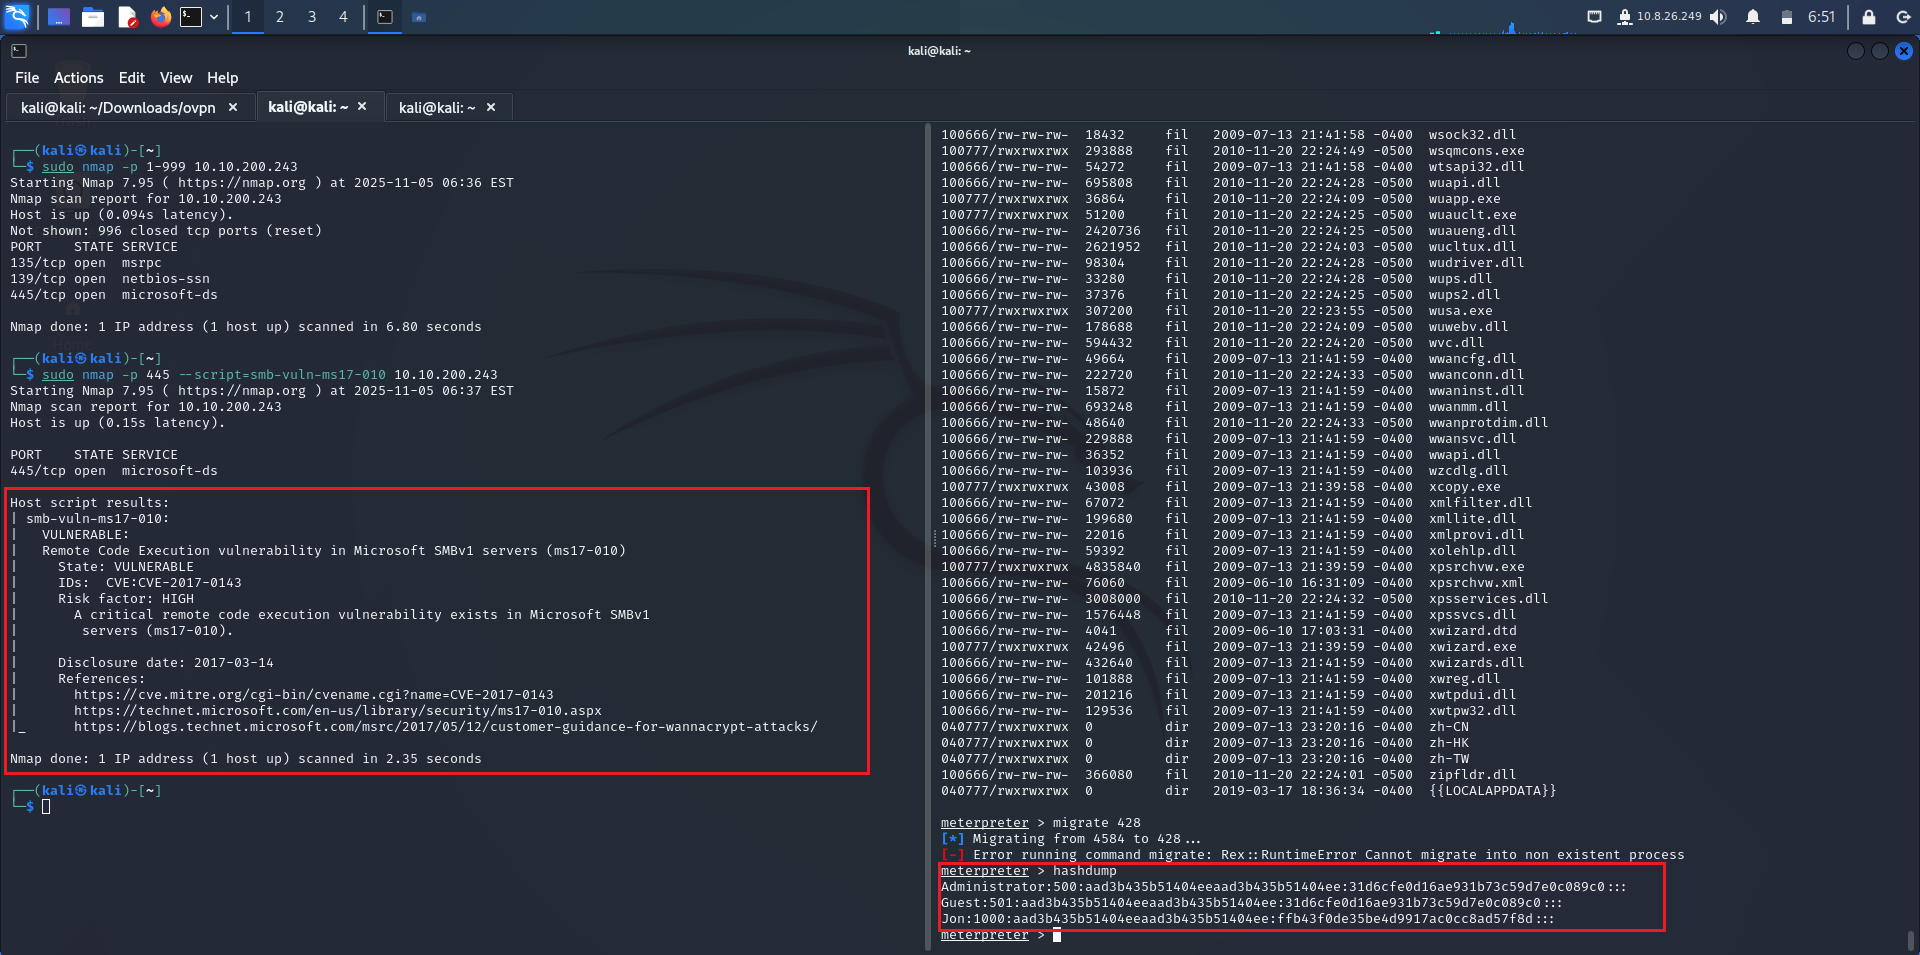 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
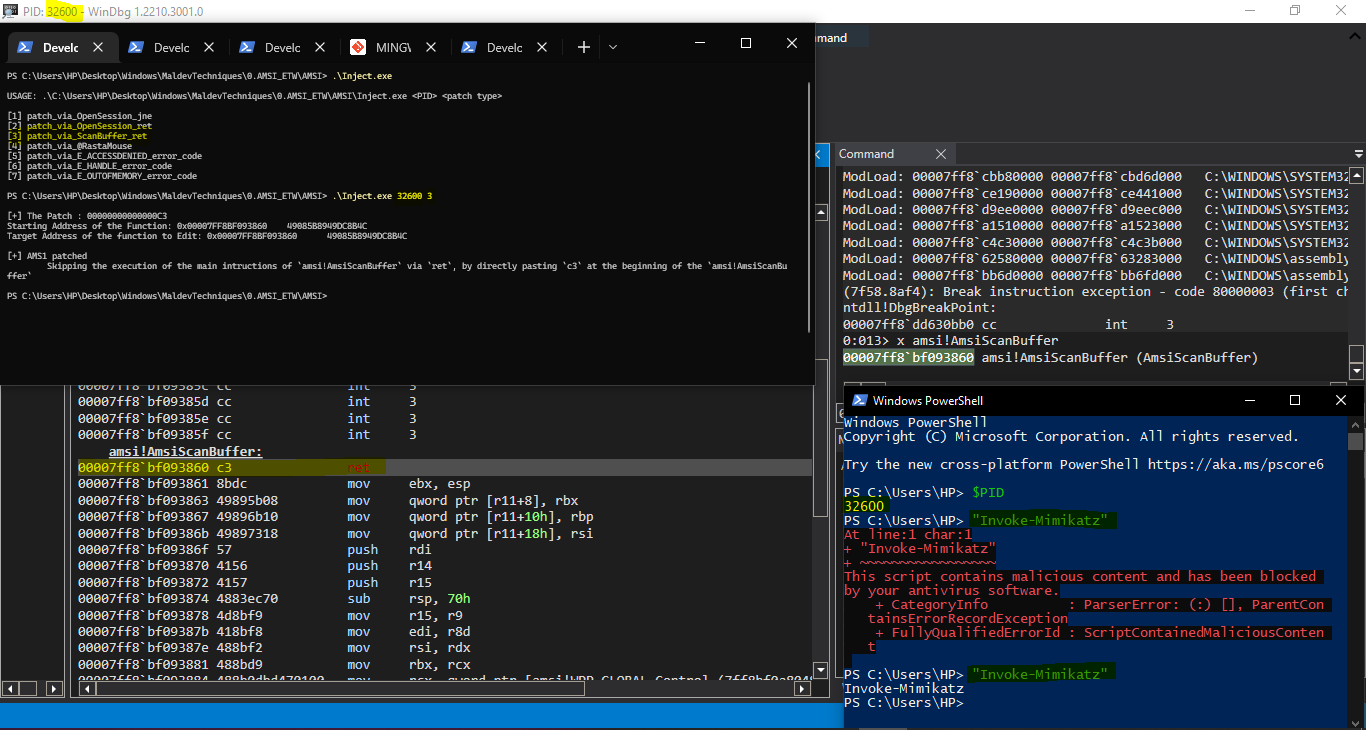 reveng007/amsi-patches-learned-till-now
I have documented all of the AMSI patches that I learned till now
 tigr78/cve-2025-53964
Proof-of-concept exploit for CVE-2025-53964: remote file read/write via malicious XDXF dictionary in GoldenDict 1.5.0/1.5.1, leveraging unsanitized…
 prodaft/malware-ioc
This repository contains indicators of compromise (IOCs) of our various investigations.
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
 nuky-alt/cve-2025-8088
Proof-of-concept exploit and technical analysis for a WinRAR path traversal vulnerability enabling code execution via crafted archives with binary…
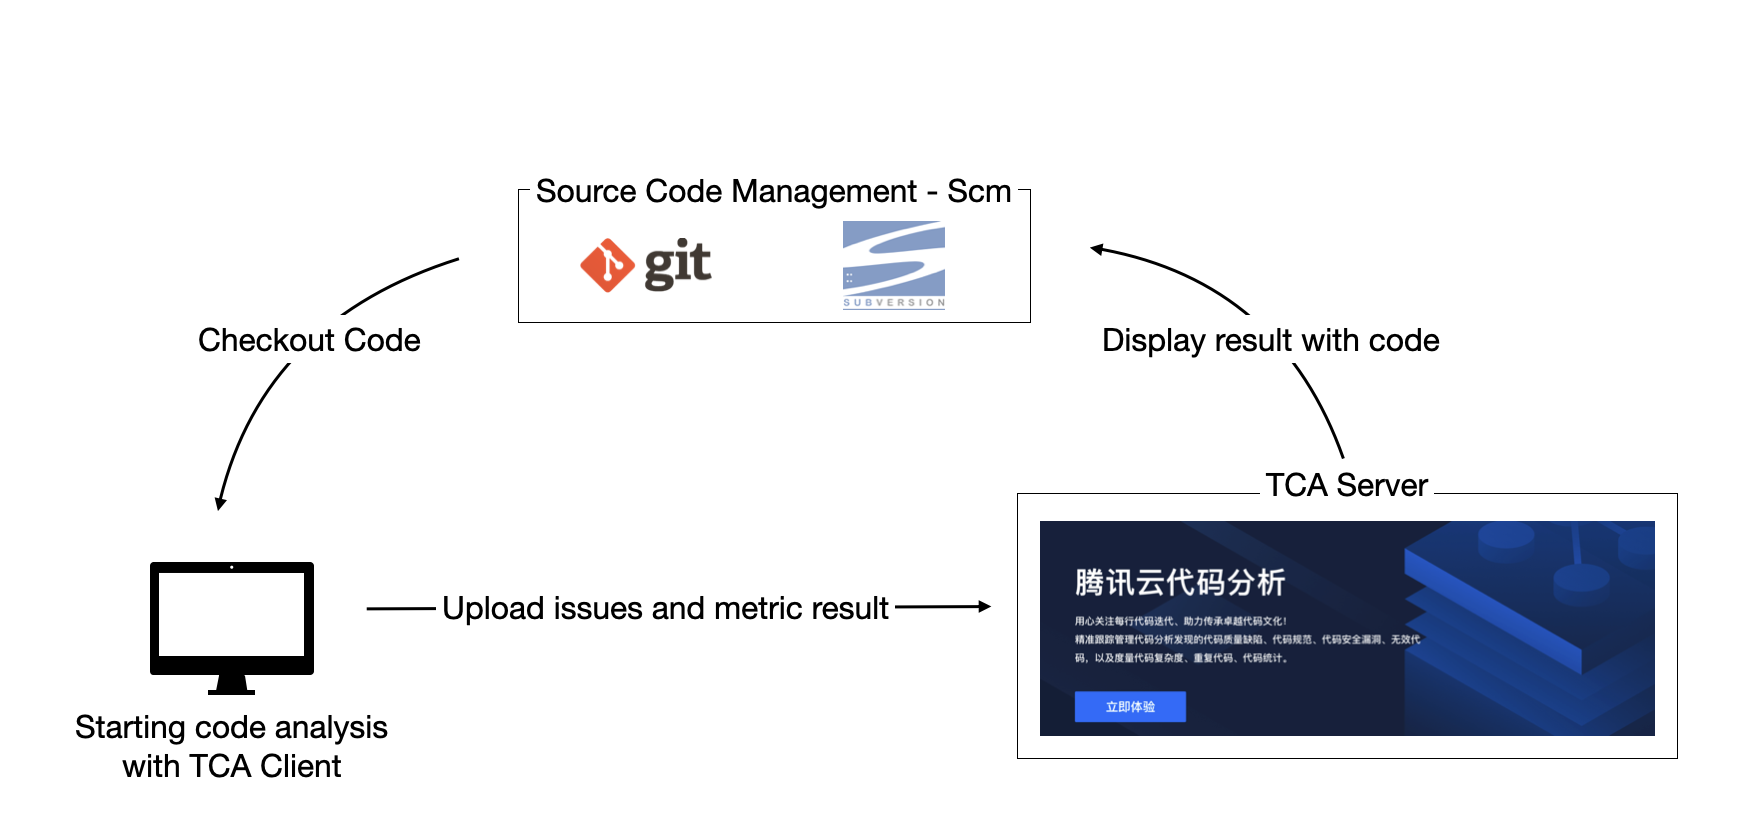 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 federicodotta/brida
The new bridge between Burp Suite and Frida!
 virustotal/vt-py
The official Python 3 client library for VirusTotal
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 virustotal/vt-go
The official Go client library for VirusTotal API
 shoucheng3/xwiki__xwiki-commons_cve-2023-29201_14-5
Technical libraries for XWiki projects, providing reusable components for vulnerability analysis, code analysis, and static analysis across…
 papcaii2004/cve-2025-8088-winrar-builder
A POC exploit for WinRAR vulnerability (CVE-2025-8088) affecting versions 7.12 and lower