
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 bekwiner/cve-2026-47777
Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…
 redteamfortress/cve-2026-36425
CVE-2026-36425 OPSWAT AppRemover (ardrv.sys) improper access control advisory
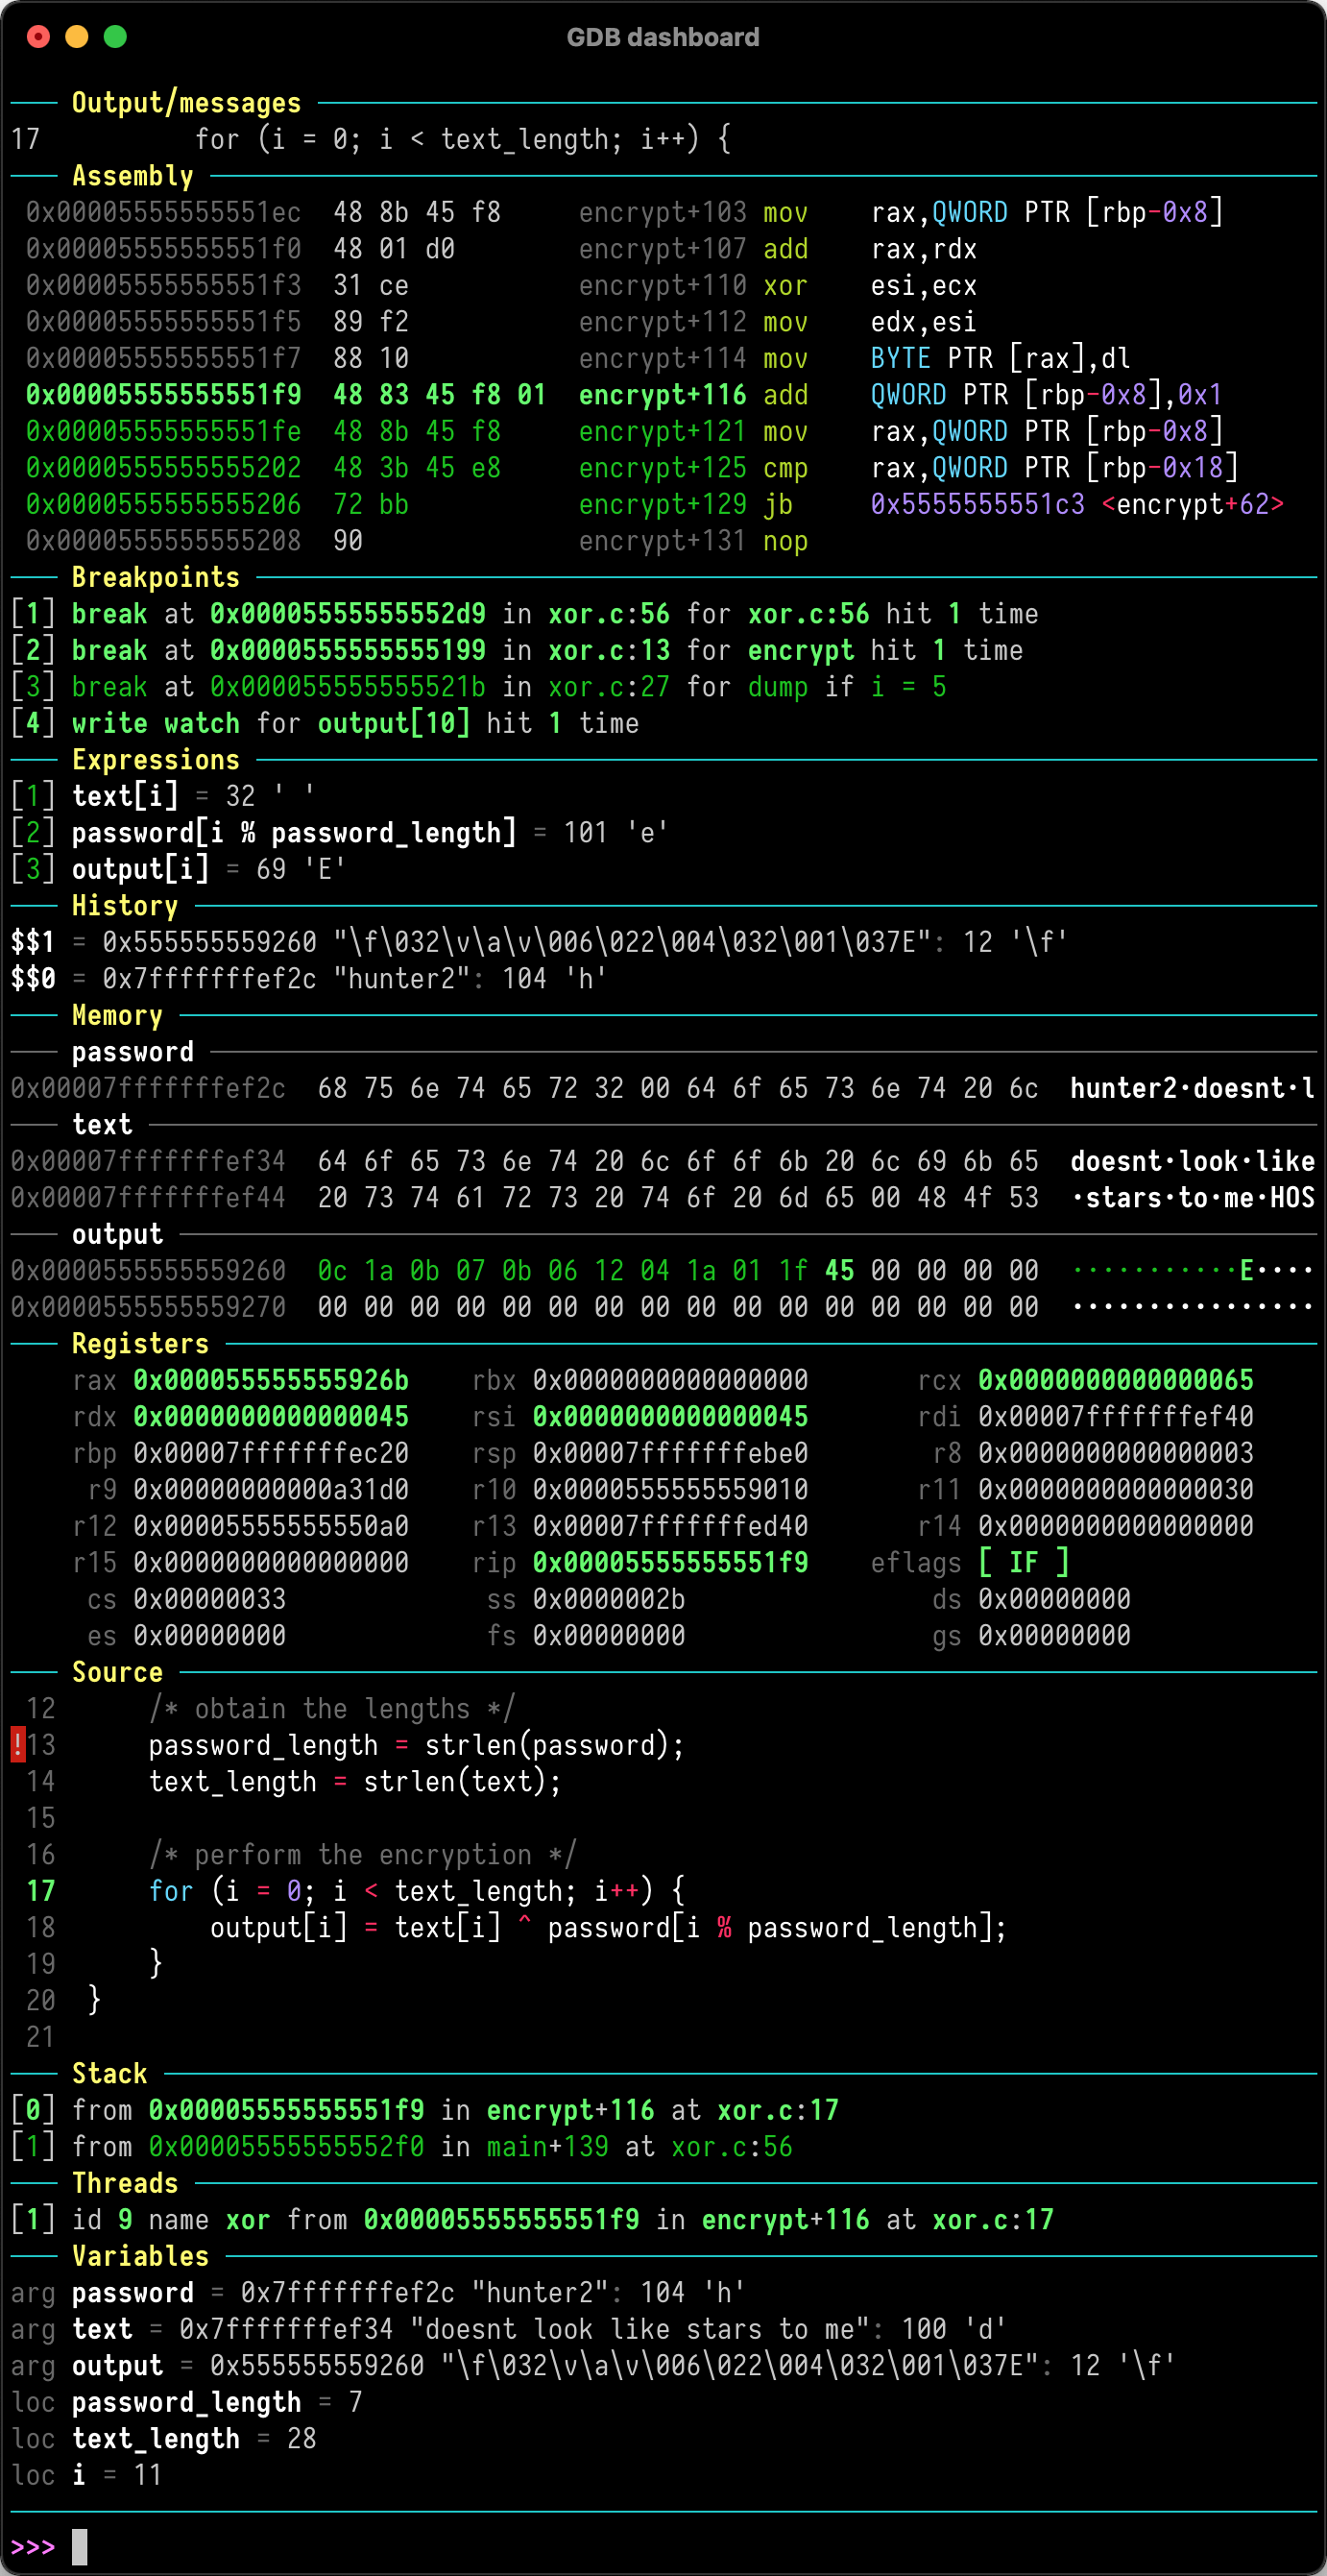 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
 sharif-bot-cmd/quantum-silicon-core-loader
Executes at the silicon boundary
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 byteray-ai/drift-corpus
Curated repository of Windows kernel patch diffs with automated vulnerability analysis, exploit primitive mapping, and debugging aids for security…
 omgrant/ft9201-libfprint
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
 seqra/cve-2026-58138
Reproduction kit for CVE-2026-58138, an unauthenticated RCE in Conductor. Includes OpenTaint static analysis rules, isolated tests, SARIF results,…

 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
 ctn-qvo/auto_extract_offsets
Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.








