#1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
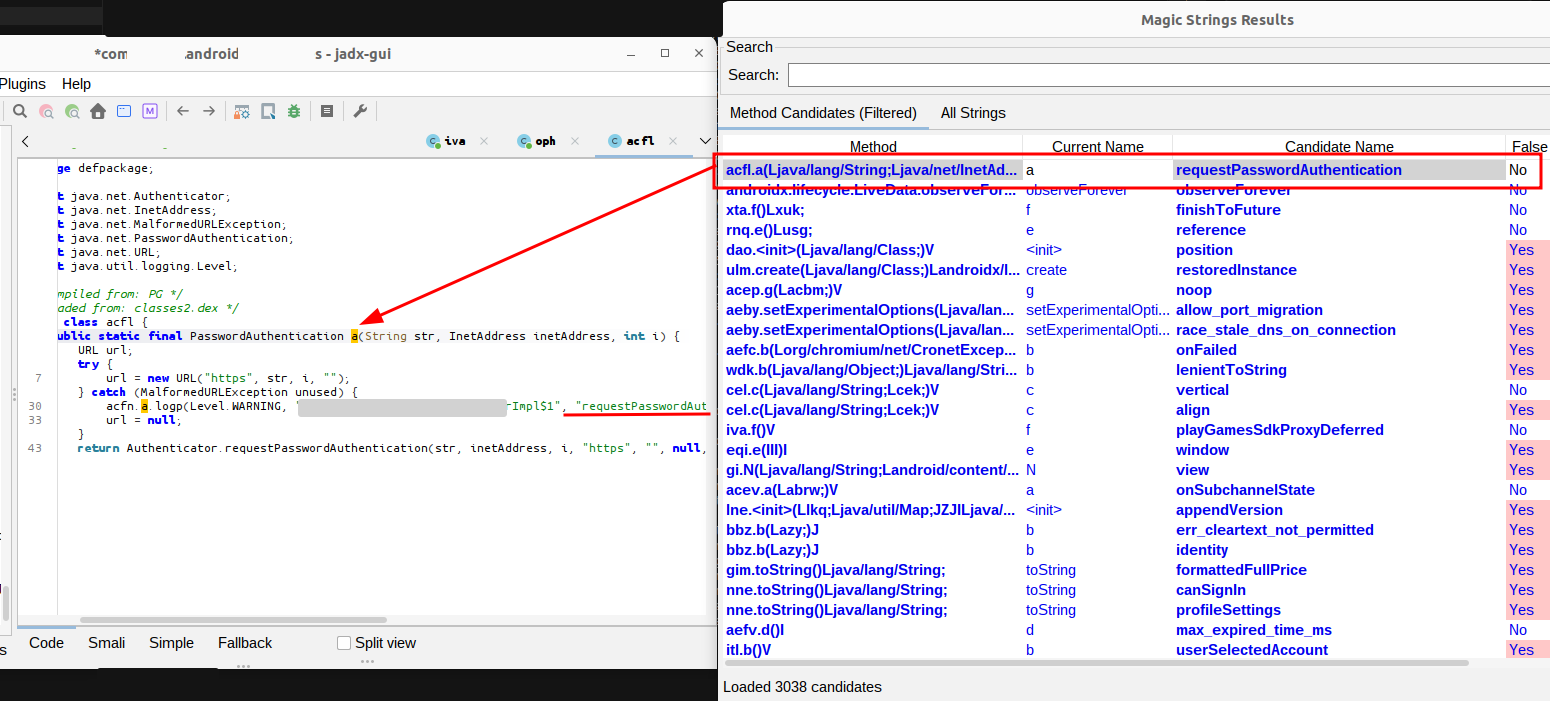 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
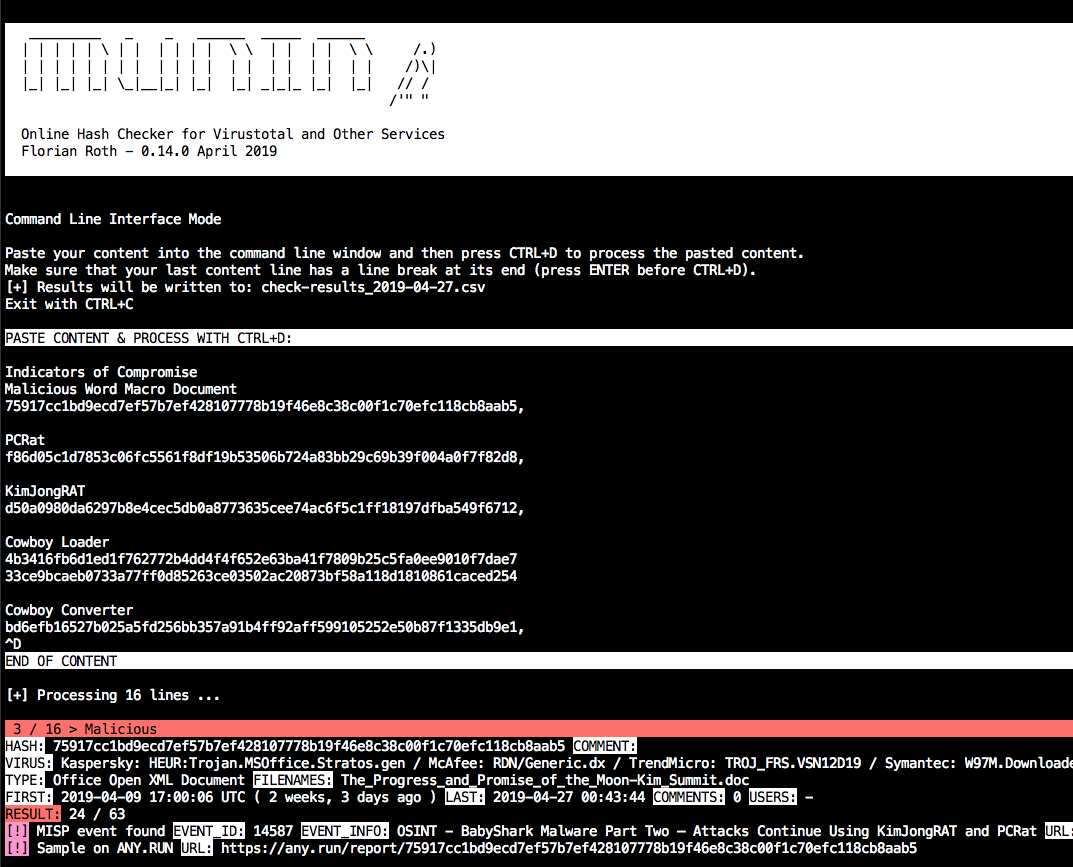 neo23x0/munin
Online hash checker for Virustotal and other services
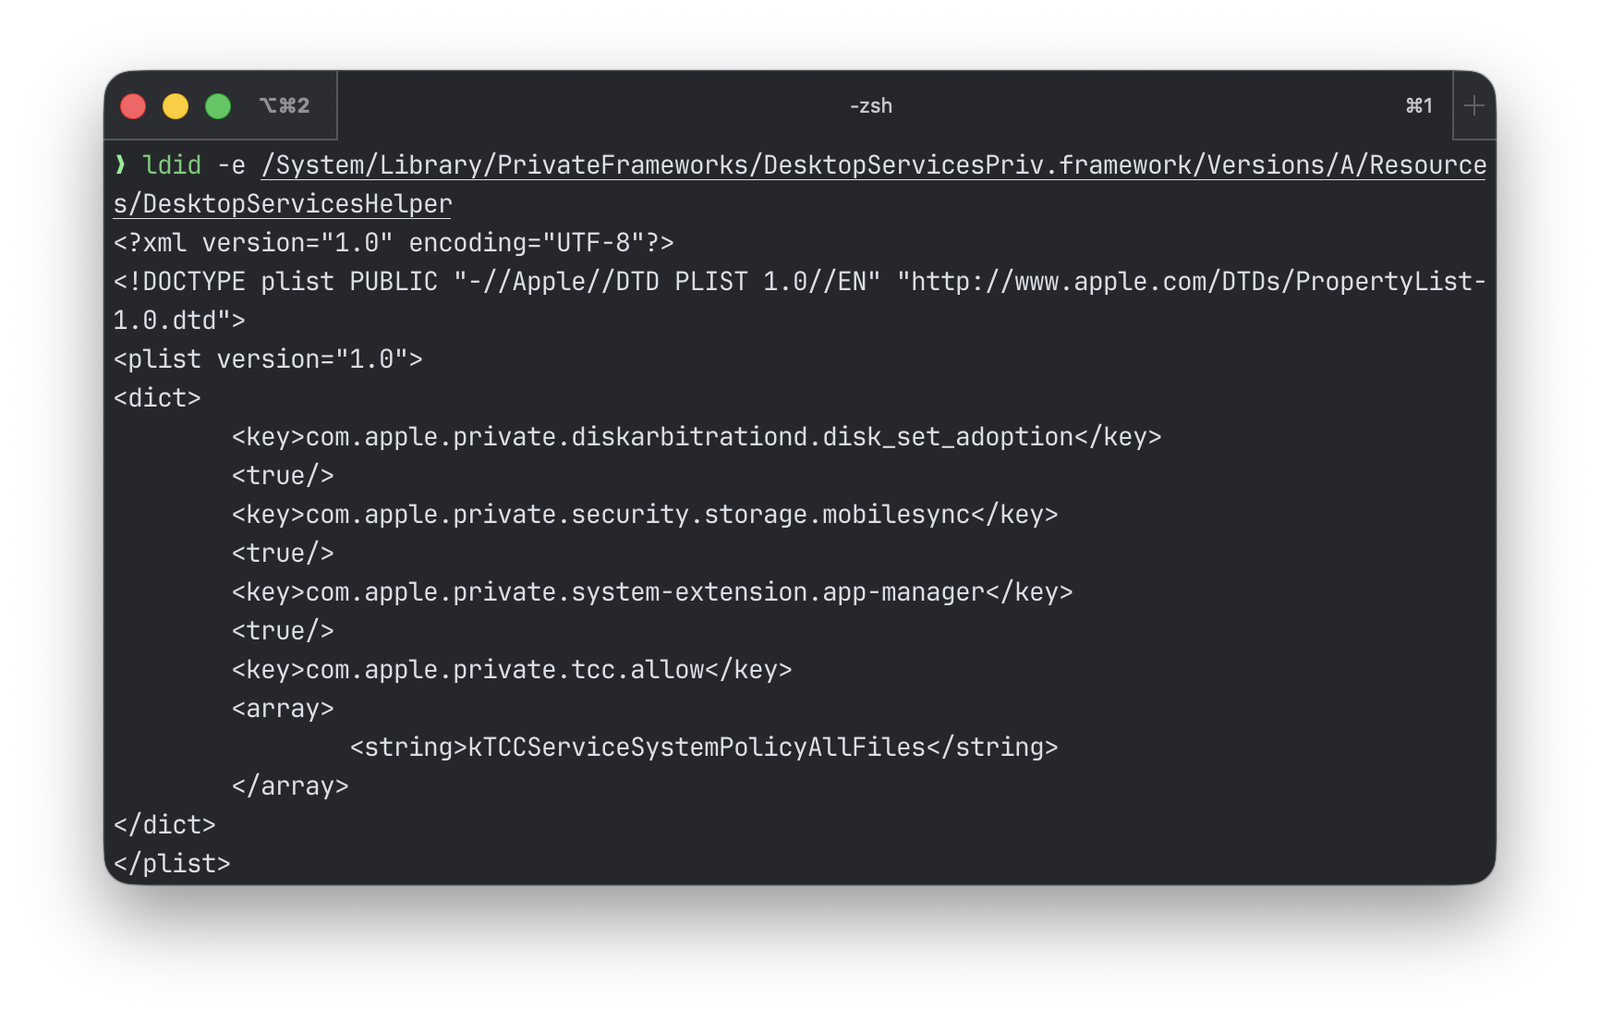 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 bronils/aotopsy
Static analyzer for Flutter/Dart AOT snapshots — recovers function names, class hierarchies, call graphs, and behavioral signals from libapp.so…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 timb-machine/linux-malware
Tracking interesting Linux (and UNIX) malware. Send PRs
 openocd-org/openocd
Official OpenOCD Read-Only Mirror (no pull requests)
 lgranadoi/sift-hardened
Security-hardened fork of sift 17.1.3 for CVE-2026-85625. Not affiliated with crcn/sift.js.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 halahajyahia/cve-2022-2869-detector
CodeQL detector for CVE-2022-2869 root cause (CWE-191 unsigned underflow) using control-flow/range analysis to identify vulnerable patterns without…
 capesandbox/cape-parsers
CAPE core and community parsers
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
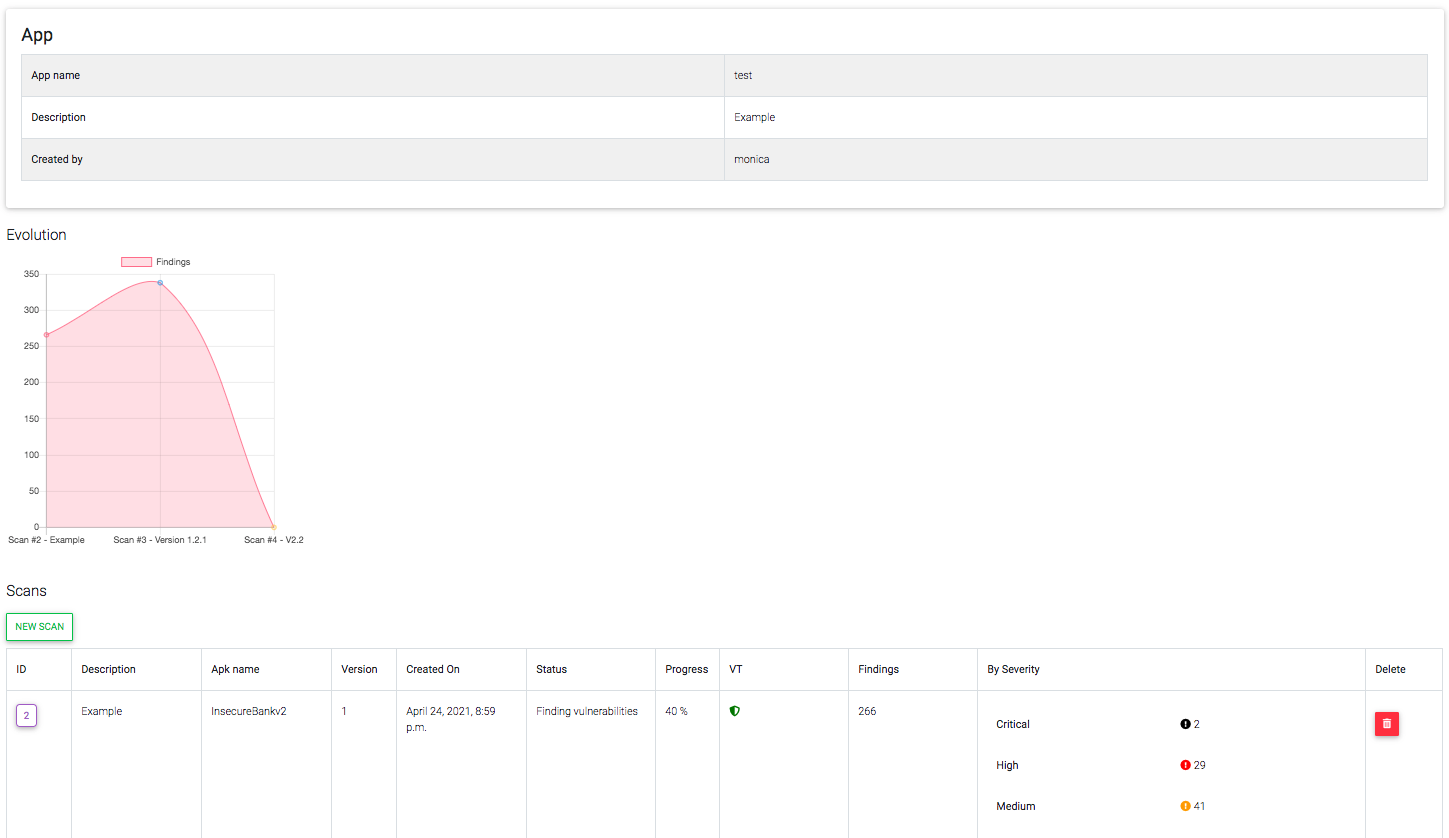 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation