
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 onekey-sec/unblob
Extract files from any kind of container formats
 lintsinghua/deepaudit
DeepAudit:人人拥有的 AI 黑客战队,让漏洞挖掘触手可及。国内首个开源的代码漏洞挖掘多智能体系统。小白一键部署运行,自主协作审计 + 自动化沙箱 PoC 验证。支持 Ollama 私有部署 ,一键生成报告。支持中转站。让安全不再昂贵,让审计不再复杂。
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 theauditortool/benchproctor
Open SAST benchmark corpus: 2,938,418 balanced cases, 11 languages, 21 framework targets, 242 emitted categories, and 231 distinct CWE IDs. Score…
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
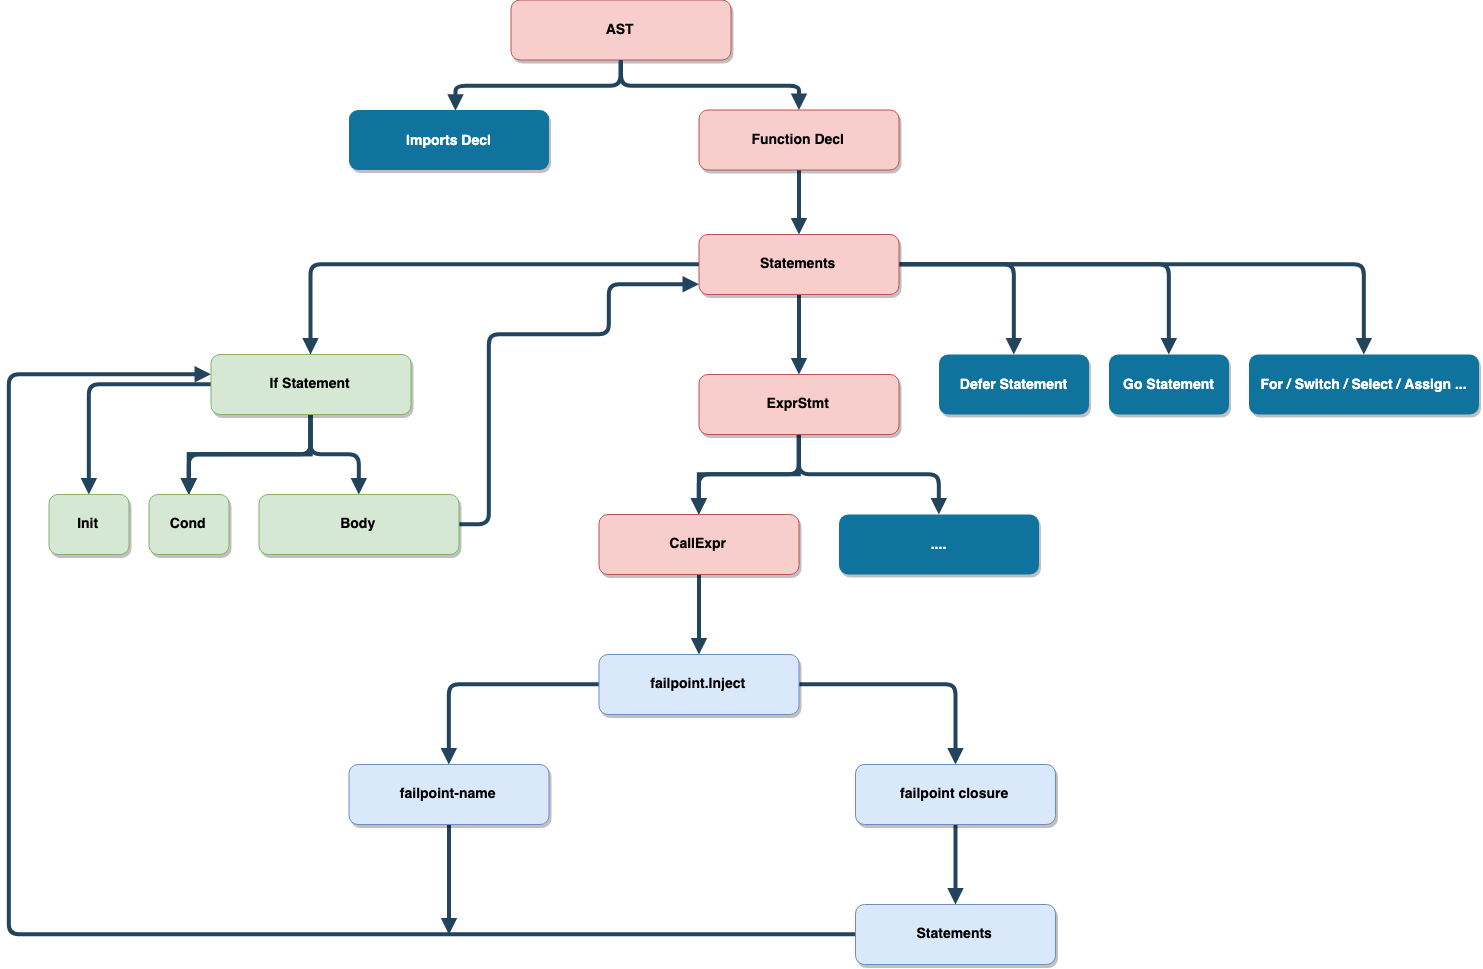 pingcap/failpoint
Fault-injection library for Go that adds runtime-controllable failpoints to trigger panics, sleeps, returns, and conditional error paths via…
 strace/strace
Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...

 droncito/aquadecomp
Orchestrates JADX, CFR, Procyon and Vineflower to decompile Android APK/AAB/XAPK/APKS files, with hidden DEX extraction, deobfuscation, signed APK…
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…

 rjzak/malware-modeler-rs
Generate training data and models for benign vs. malicious files plus related tools.
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 structio-labs/n0xis
Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…








