
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended

 d4rksystem/evasive_malware_book_samples
The samples referenced in my book, Evasive Malware (No starch Press)
 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 mr-r3b00t/cyber_rss
a list of useful feeds
 vulhunt-re/vulhunt
Vulnerability detection framework by Binarly's REsearch team
 binref/agent
Language Model Agent Instructions for Binary Refinery
 huhusmang/awesome-llms-for-vulnerability-detection
The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 capesandbox/cape-parsers
CAPE core and community parsers
 yo-yo-yo-jbo/macos_xprotect
Educational deep dive into Apple's built-in malware protection: signature databases, YARA rules, Gatekeeper integration, remediation binaries, and…
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
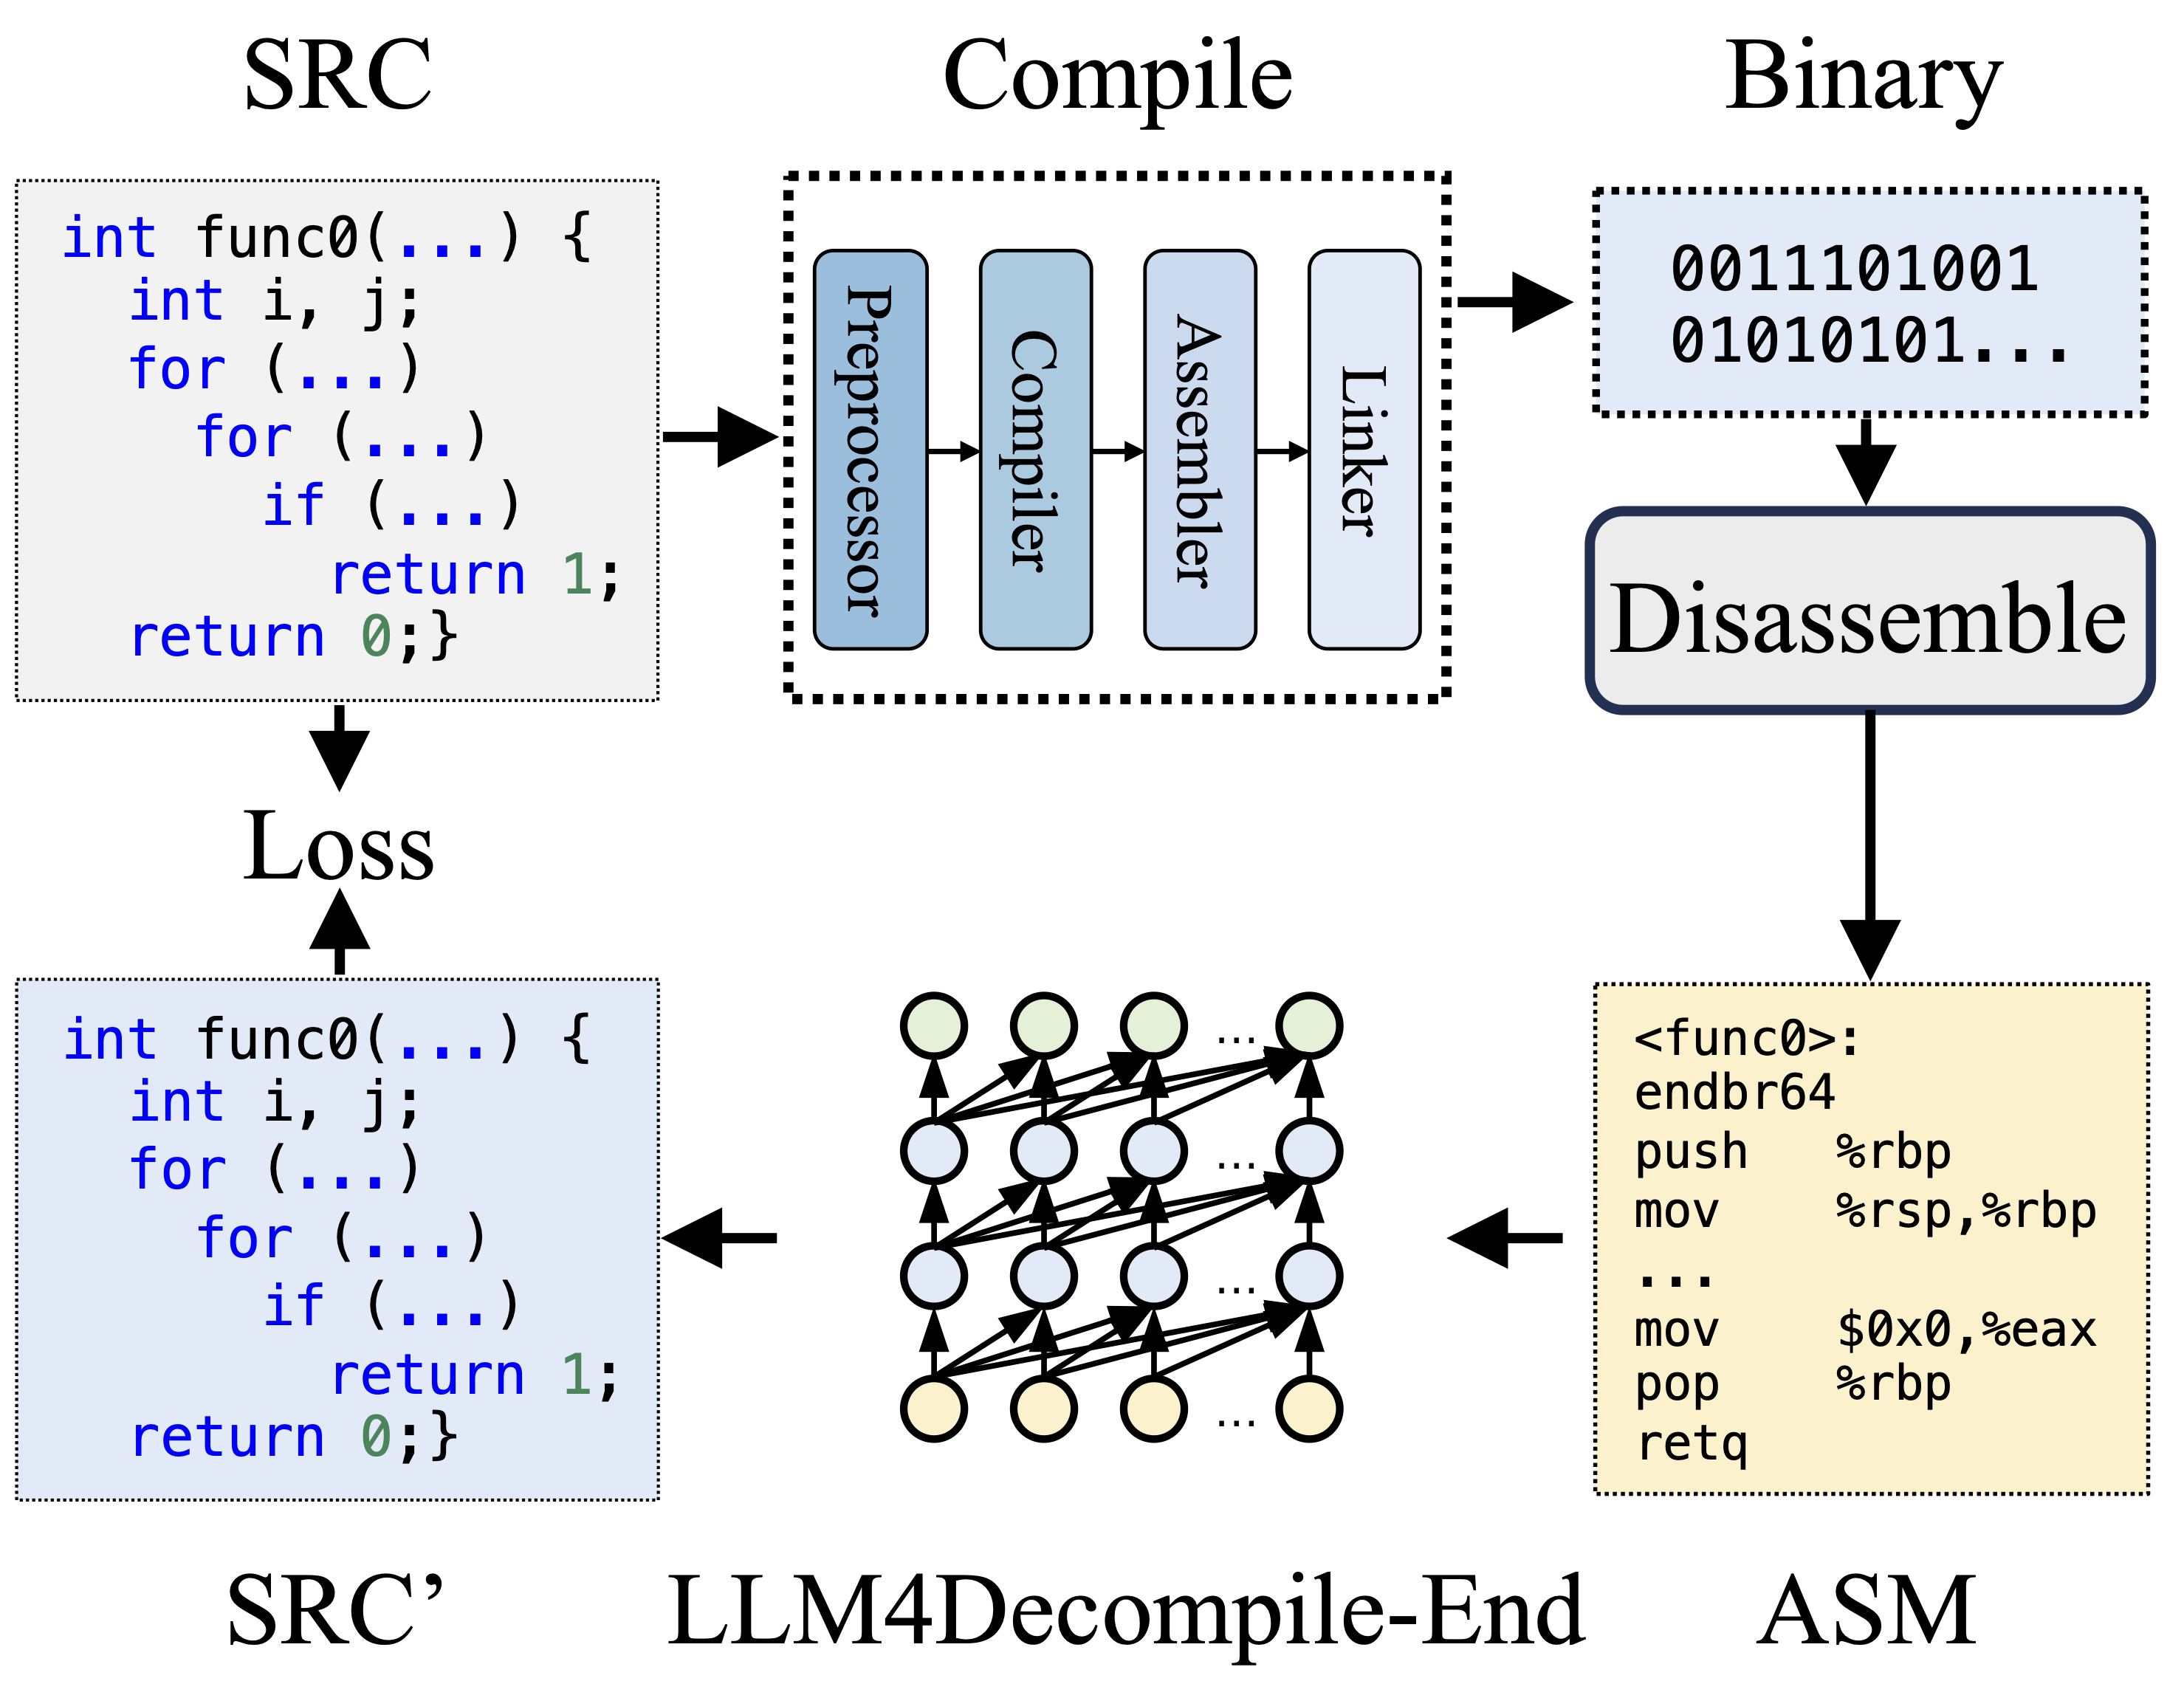 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…
 ps5dev/byepervisor
A PS5 hypervisor exploit for 1.xx-2xx firmwares.
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 hasherezade/flareon2024
Solutions and write-ups for Flare-On 11 CTF challenges, showcasing reverse engineering, binary analysis, and malware analysis techniques with…
 paddycahil/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…








