

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Categories

Malware Analysis

Tools for dissecting, understanding, and reverse engineering malicious software behavior.

Kitploit recommended

Top tools

10 selected
yara-x preview#1

yara-x

GitHubvirustotal/yara-x
1.2k2h 30m ago
capa preview#3

capa

GitHubmandiant/capa
6.1k10 days ago
flare-floss preview#4

flare-floss

GitHubmandiant/flare-floss
4.1k29 days ago
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1k2 days ago
radare2 preview#6

radare2

GitHubradareorg/radare2
24.5k1h 52m ago
ghidra preview#7

ghidra

GitHubnationalsecurityagency/ghidra
71.1k1 day ago
Detect-It-Easy preview#8

Detect-It-Easy

GitHubhorsicq/detect-it-easy
11.3k1 day ago
theZoo preview#9

theZoo

GitHubytisf/thezoo
13.3k2 months ago
flare-vm preview#10

flare-vm

GitHubmandiant/flare-vm
8.9k1 month ago
IntelOwl preview#11

IntelOwl

GitHubintelowlproject/intelowl
4.7k2 months ago
NewestRelevanceMost popularRecently updated
4060 results
python-inquestlabs preview

python-inquestlabs

GitHubinquest/python-inquestlabs

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

ioc-managementosinthash-analysis+4
361 year ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.

memory-forensicsforensicsmalware-analysis+2
2674 years ago
Awesome-Pentest preview

Awesome-Pentest

GitHubkc57/awesome-pentest

A list of awesome penetration testing tools and resources.

password-crackingprivilege-escalationstatic-code-analysis+9
843 years ago
YARA_Rules preview

YARA_Rules

GitHubmalgamy/yara_rules

Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
defensive-toolsstatic-analysismalware-analysis+3
653 years ago
2022 preview

2022

GitHub100daysofyara/2022

Daily YARA rule challenge and community collection where malware analysts share detection patterns, tips, and unconventional YARA uses to advance…

malware-analysiseducationcurated-resources+1
233 years ago
conf-presentations preview

conf-presentations

GitHubquarkslab/conf-presentations

Quarkslab conference talks

bluetooth-securityvulnerability-analysisreverse-engineering+6
31828 days ago
weightBufs preview

weightBufs

GitHub0x36/weightbufs

ANE kernel r/w exploit for iOS 15 and macOS 12

privilege-escalationios-securityvulnerability-analysis+4
3054 years ago
pocs_slides preview

pocs_slides

GitHubcq674350529/pocs_slides

my advisory, poc, slides and scripts related to IoT/protocol security

packet-sniffing-analysisiot-securityvulnerability-analysis+4
711 year ago
Yara-rules preview

Yara-rules

GitHubbartblaze/yara-rules

Collection of private Yara rules.

defensive-toolsmalware-analysisdigital-forensics+3
3889 months ago
hyperpom preview

hyperpom

GitHubimpalabs/hyperpom

AArch64 fuzzer based on the Apple Silicon hypervisor

dynamic-analysis-sandboxingvulnerability-analysissecurity-virtualization+2
2022 years ago
cyberchef-recipes preview

cyberchef-recipes

GitHubmattnotmax/cyberchef-recipes

A list of cyber-chef recipes and curated links

disk-forensicsencryption-decryption-toolsnetwork-forensics+8
2.2k4 years ago
GoTEE-example preview

GoTEE-example

GitHubusbarmory/gotee-example

GoTEE - example application

embedded-systems-securitymemory-forensicsdebuggers+2
172 days ago
FirmAE preview

FirmAE

GitHubpr0v3rbs/firmae

Towards Large-Scale Emulation of IoT Firmware for Dynamic Analysis

embedded-systems-securitydynamic-analysis-sandboxingiot-security+3
8944 months ago
PR0CESS preview

PR0CESS

GitHubaaaddress1/pr0cess

some gadgets about windows process and ready to use :)

exploitationpost-exploitationmalware-analysis+3
6163 years ago
Endurance-Wiper preview

Endurance-Wiper

GitHubintelbroker/endurance-wiper

a small wiper malware programmed in c#

malware-analysispayload-developmentadversarial-attack
714 years ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?
memory-forensicsnetwork-forensicsmalware-analysis+5
1.8k8 days ago
pics preview

pics

GitHubcorkami/pics

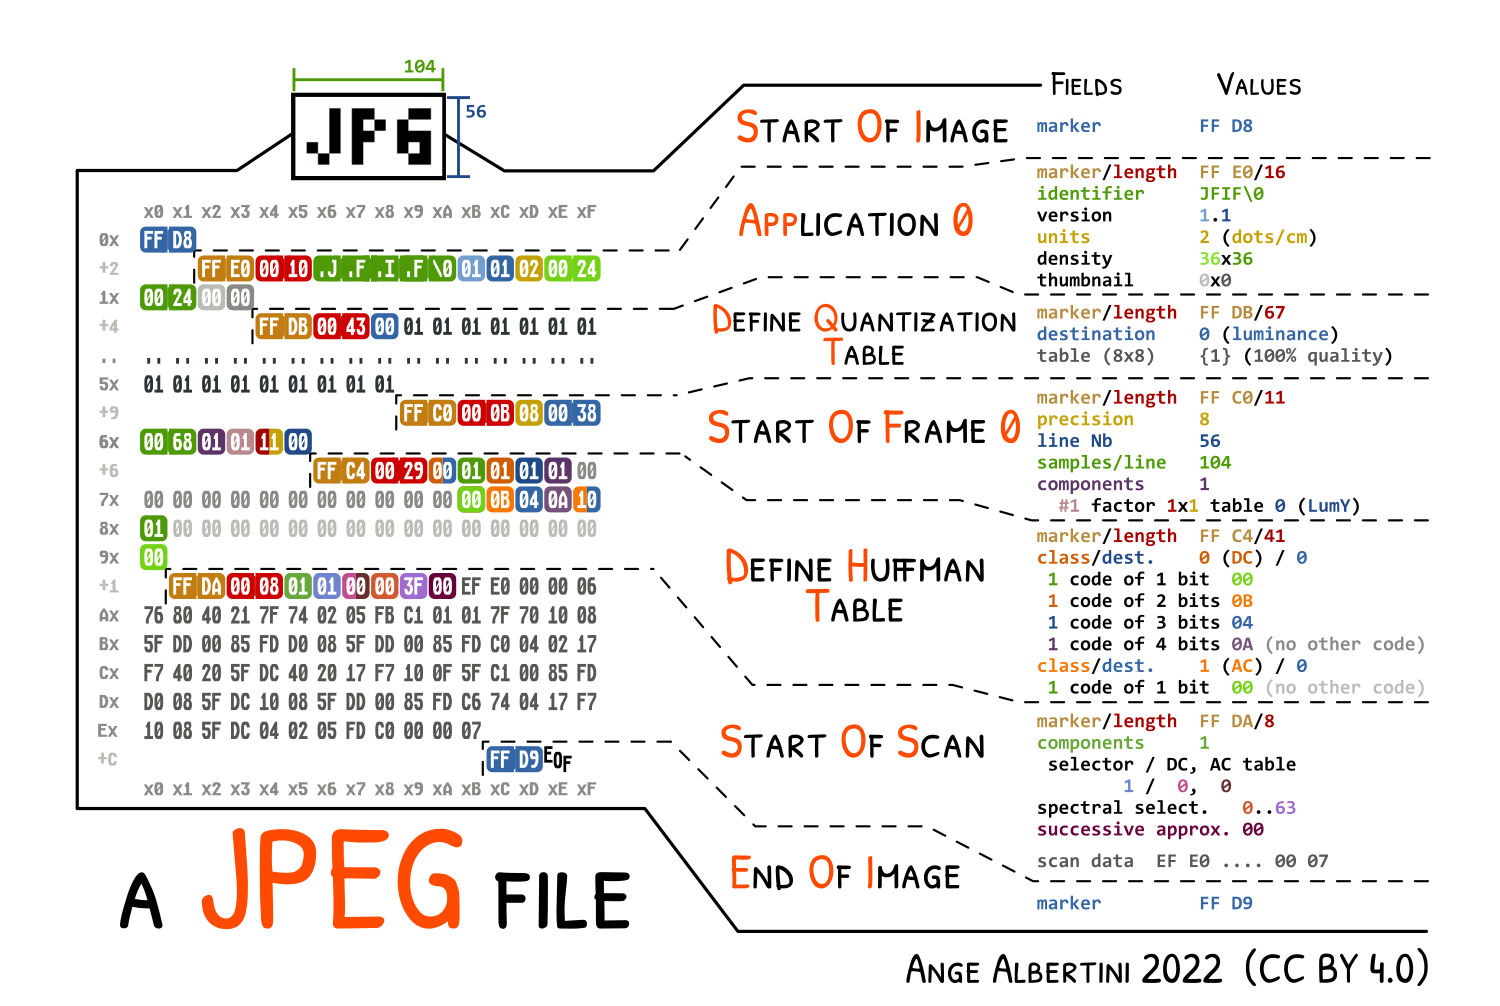
File formats dissections and more...

reverse-engineeringbinary-analysiseducation+1
11.5k2 years ago
unidbg preview

unidbg

GitHubzhkl0228/unidbg

Allows you to emulate an Android native library, and an experimental iOS emulation

android-securitydynamic-analysis-sandboxingios-security+5
5.1k1 day ago
Previous1…616263…100Next









