
 #1
Tools for dissecting, understanding, and reverse engineering malicious software behavior.
Kitploit recommended
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 torvalds/linux
Linux kernel source tree
 arachni/arachni
Web Application Security Scanner Framework
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 tkmru/awesome-edr-bypass
Curated collection of EDR bypass resources including PoCs, tools, workshops, presentations, and blogs for ethical hacking and red team operations.
 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
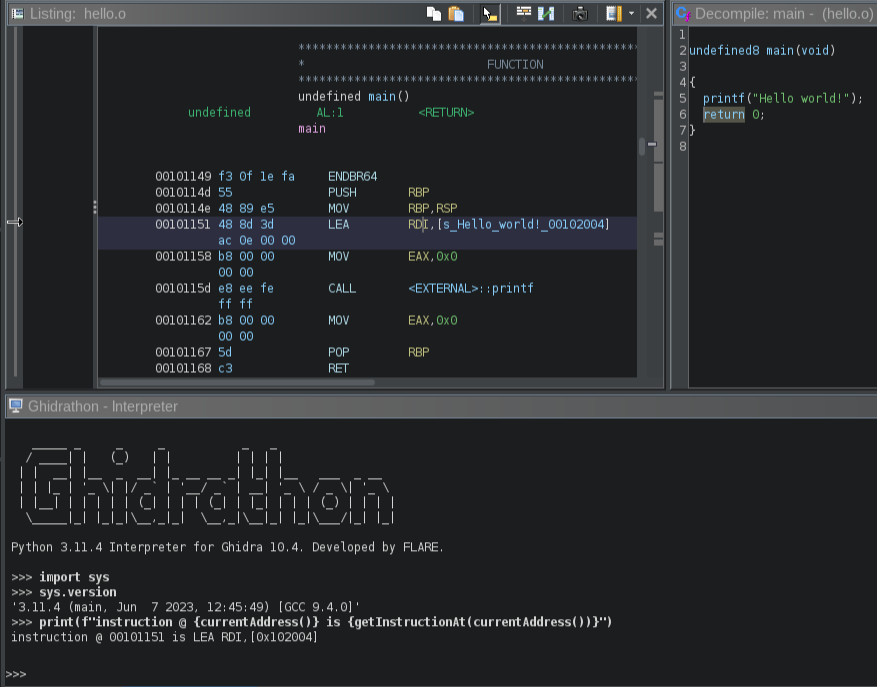 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 blakebratcher/wcw-cyberring-pav-decryptor
Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…
 inartin/365cam-stream
Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…
 shurikgo/cve-2026-25262-sm8450-research
CVE-2026-25262 applicability to Snapdragon 8 Gen 1 — experimental results
 spiralbl0ck/blacklotus-z2a-challenge
BlackLotus-Z2A-Challenge, Nothing to see here 4 now , please move along










