
 #1
Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.
Kitploit recommended

 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
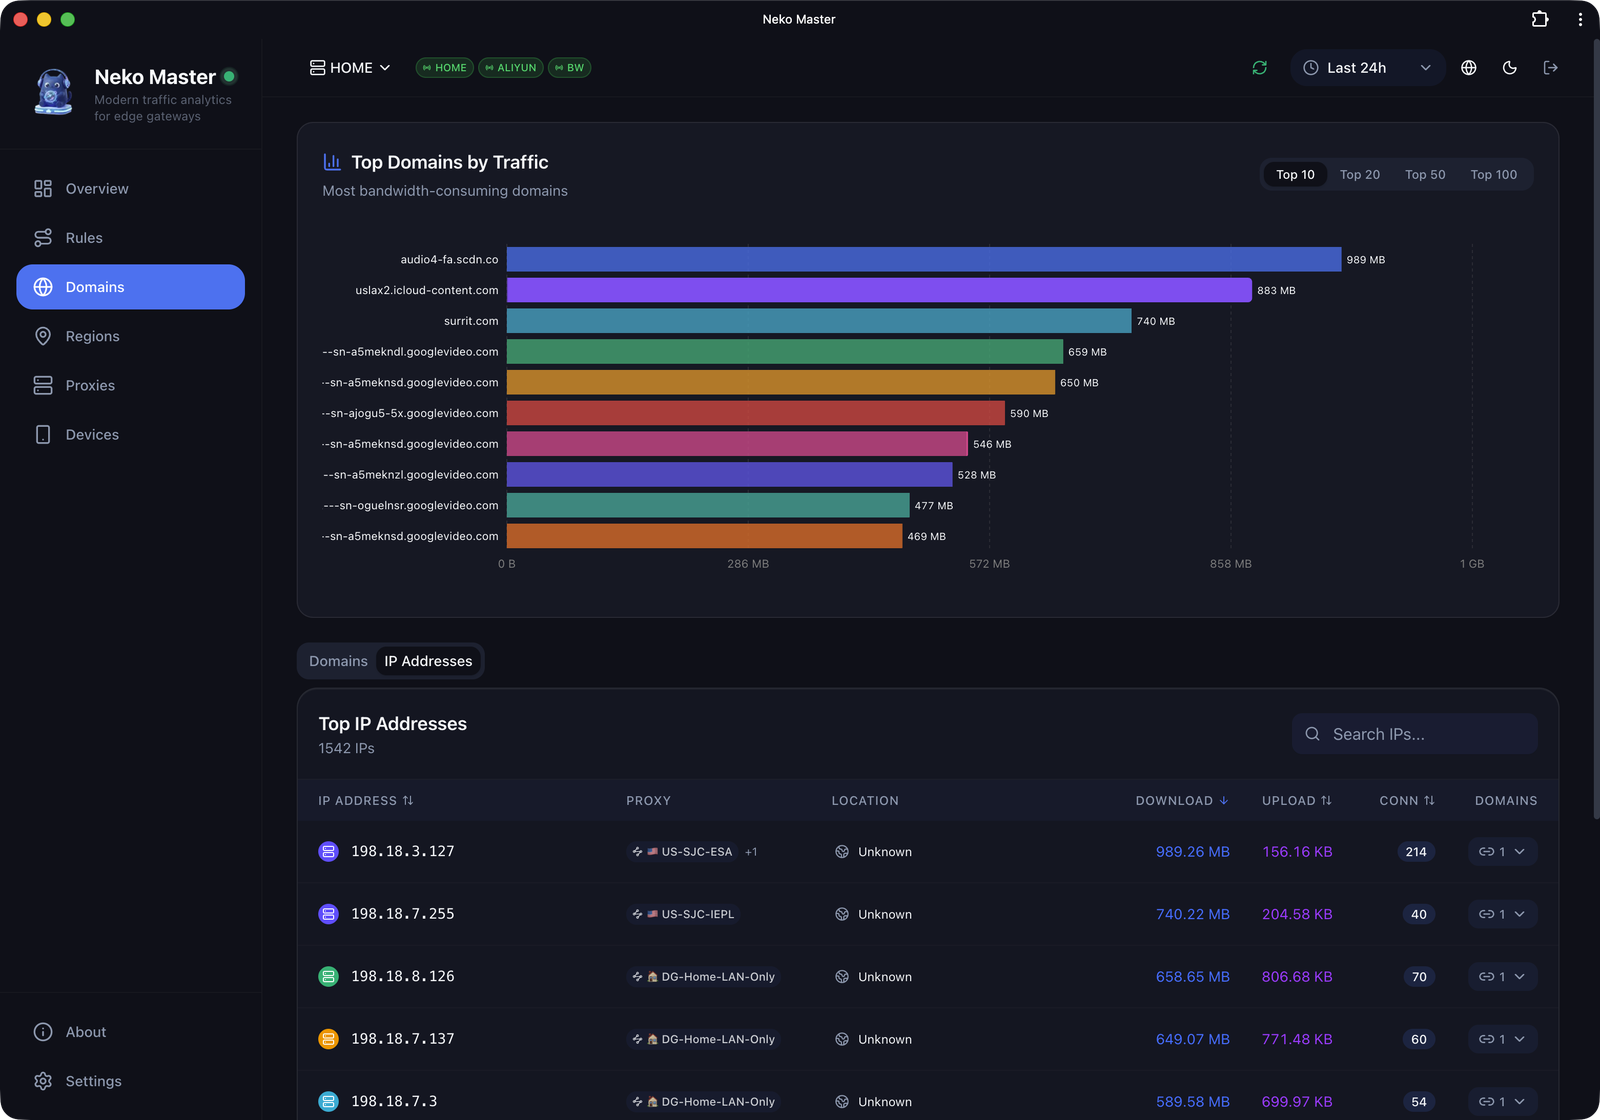 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
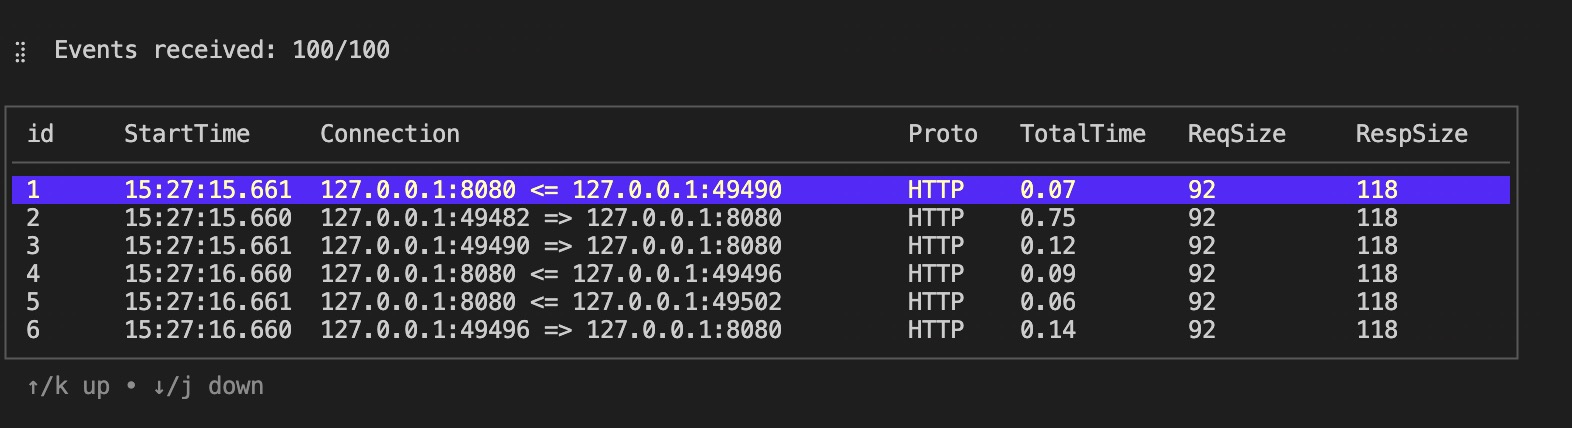 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 tsale/edr-telemetry
This project aims to compare and evaluate the telemetry of various EDR products.








