
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended

 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
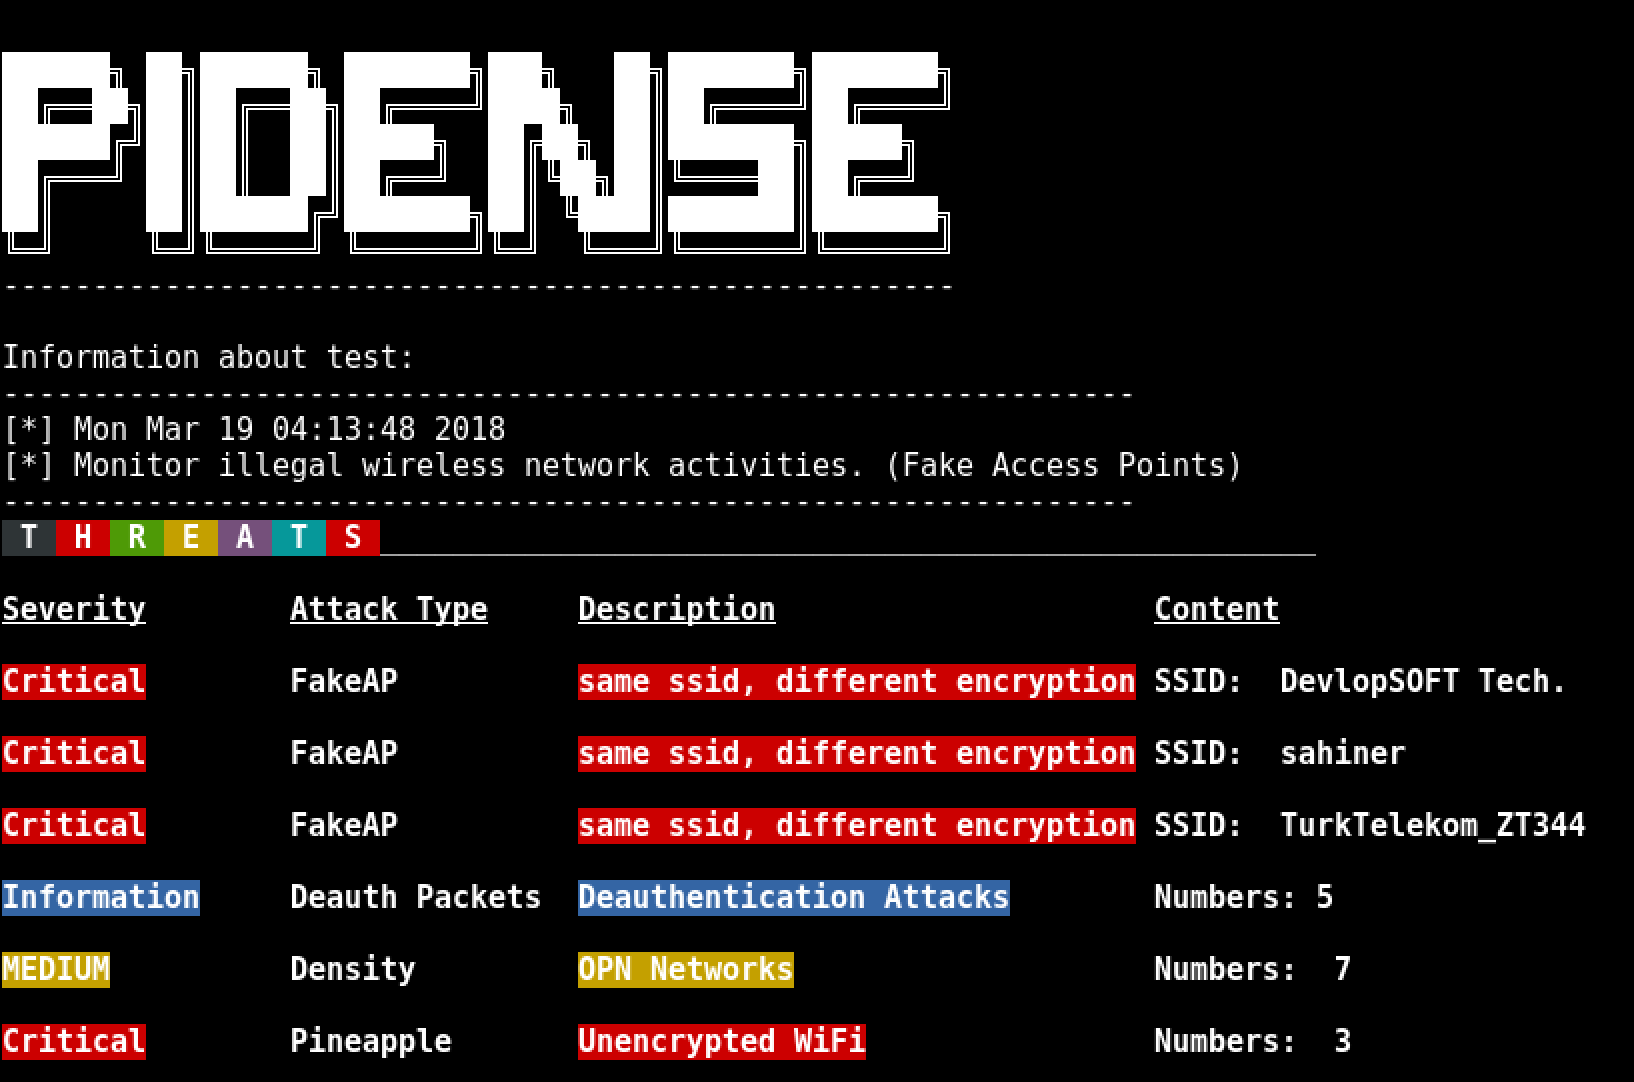 wipi-hunter/pidense
🍓📡🍍Monitor illegal wireless network activities. (Fake Access Points), (WiFi Threats: KARMA Attacks, WiFi Pineapple, Similar SSID, OPN Network…
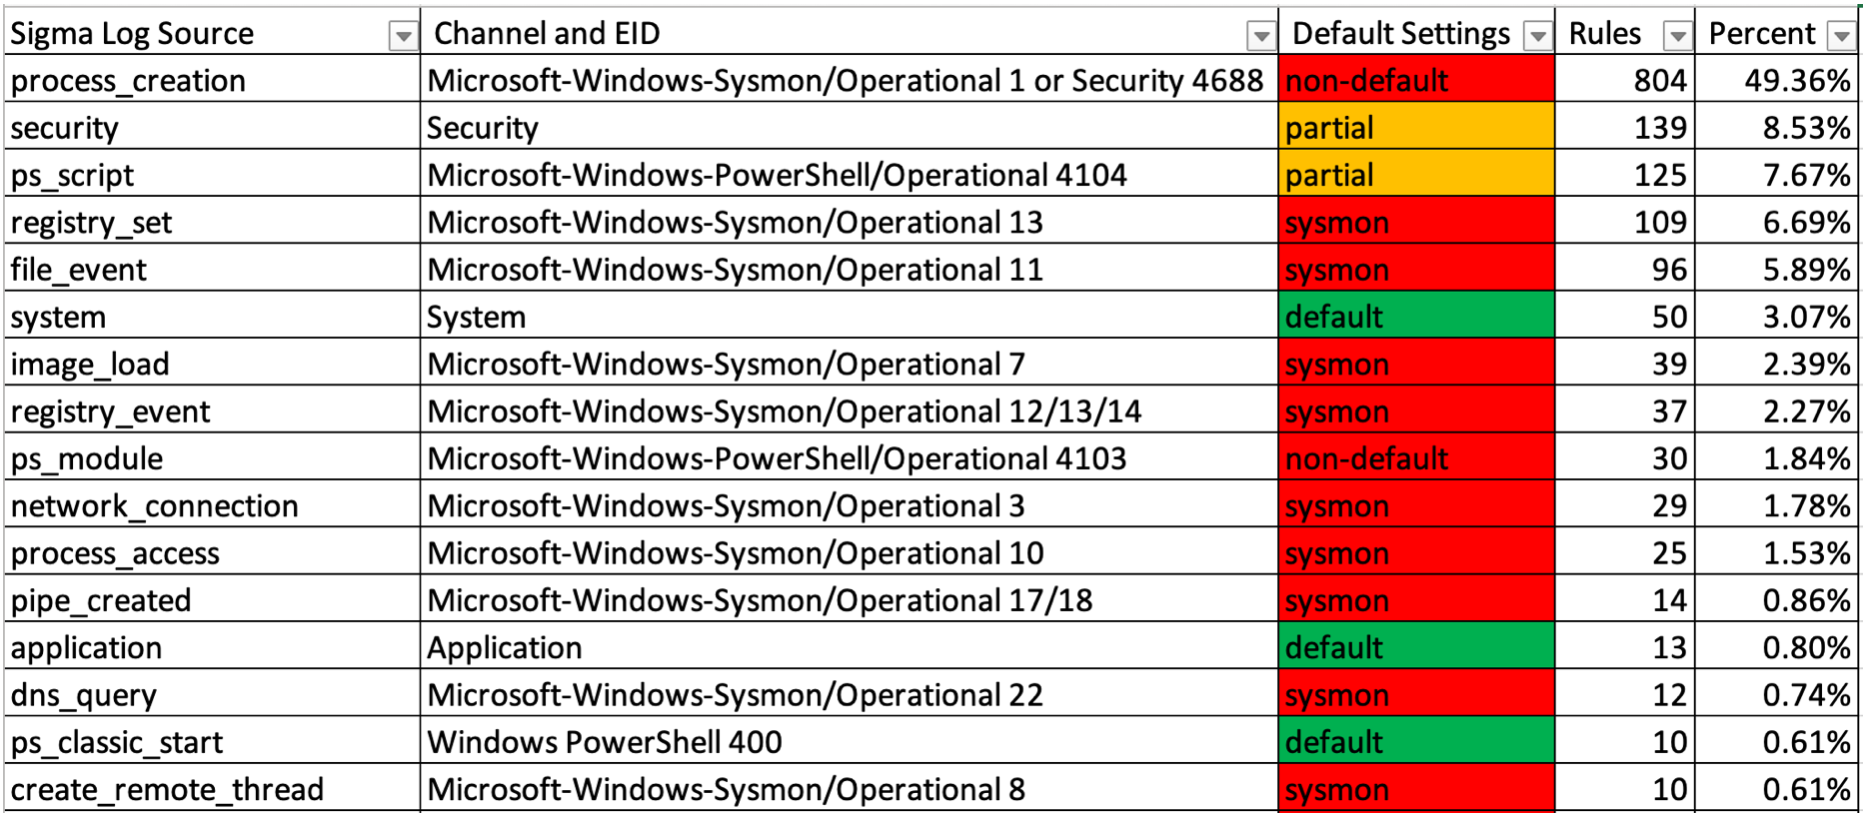 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
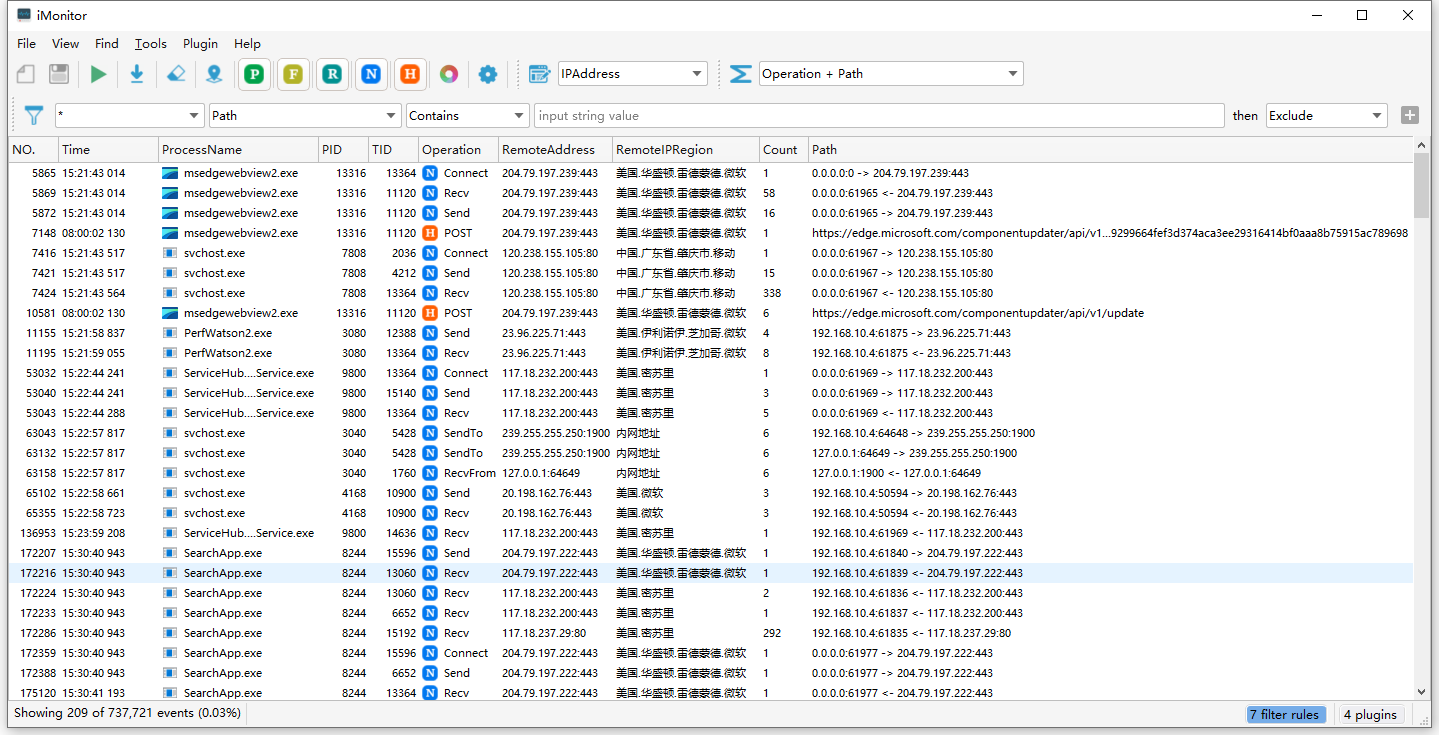 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 objective-see/donotdisturb
Detect Evil Maid Attacks
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
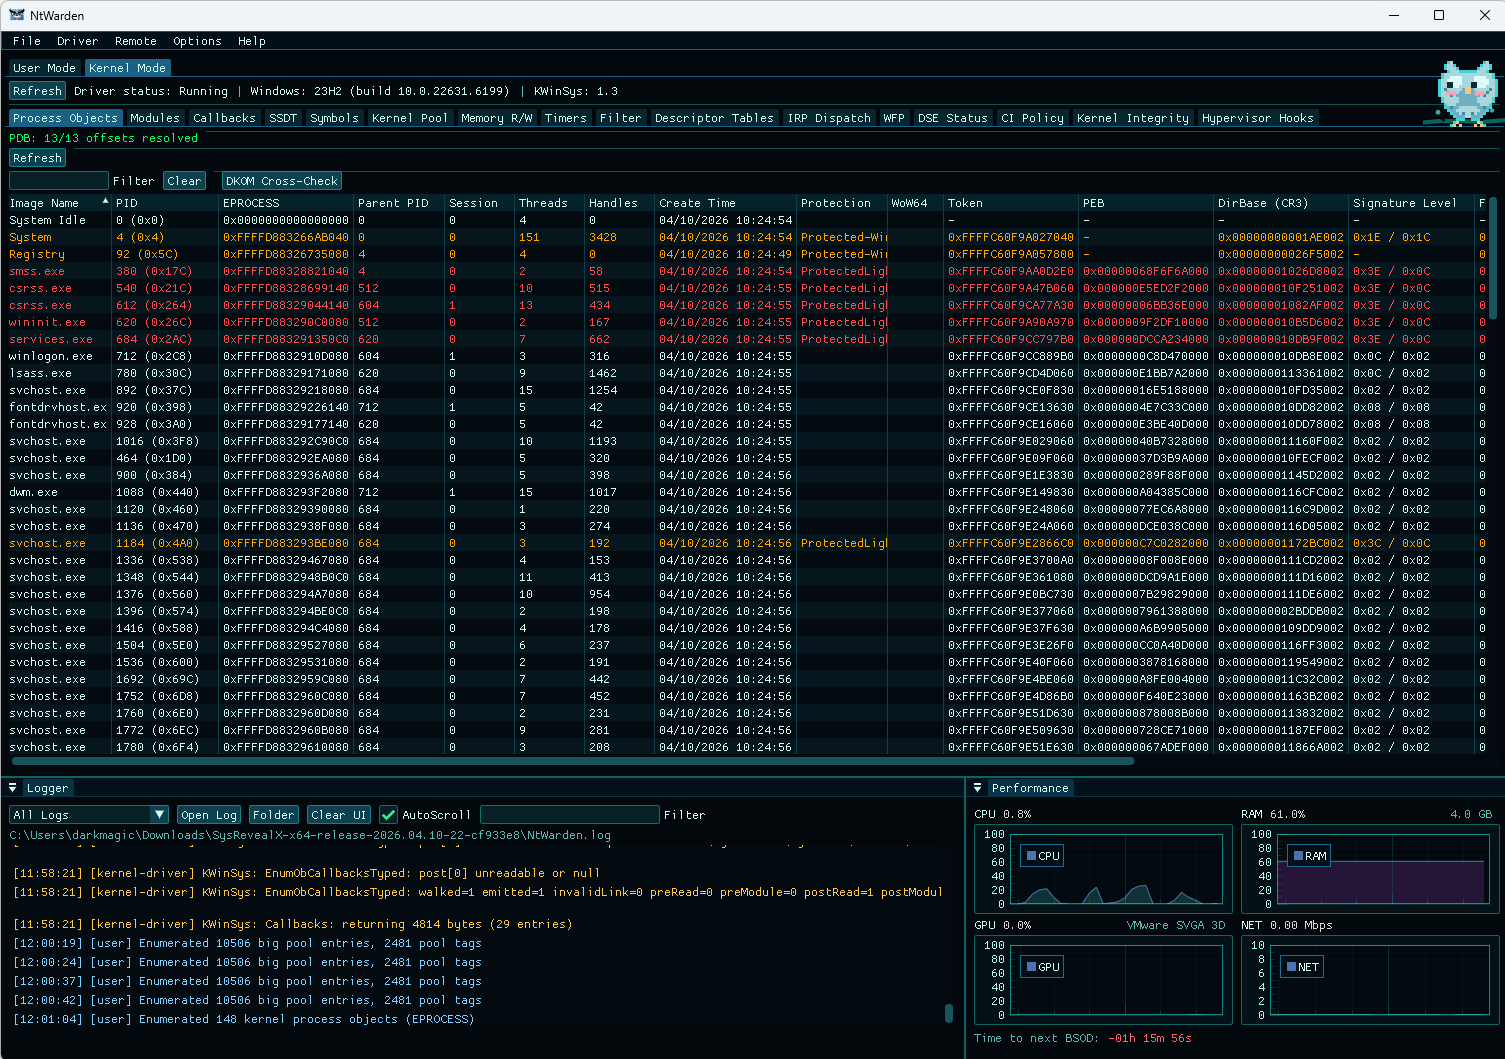 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 chainguard-dev/osquery-defense-kit
Production-ready detection & response queries for osquery
 nextronsystems/sysmon-config
Sysmon configuration file template with default high-quality event tracing
 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
 bartblaze/yara-rules
Collection of private Yara rules.
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.








