
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended

 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 gossithedog/threathunting
Tools for hunting for threats.
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
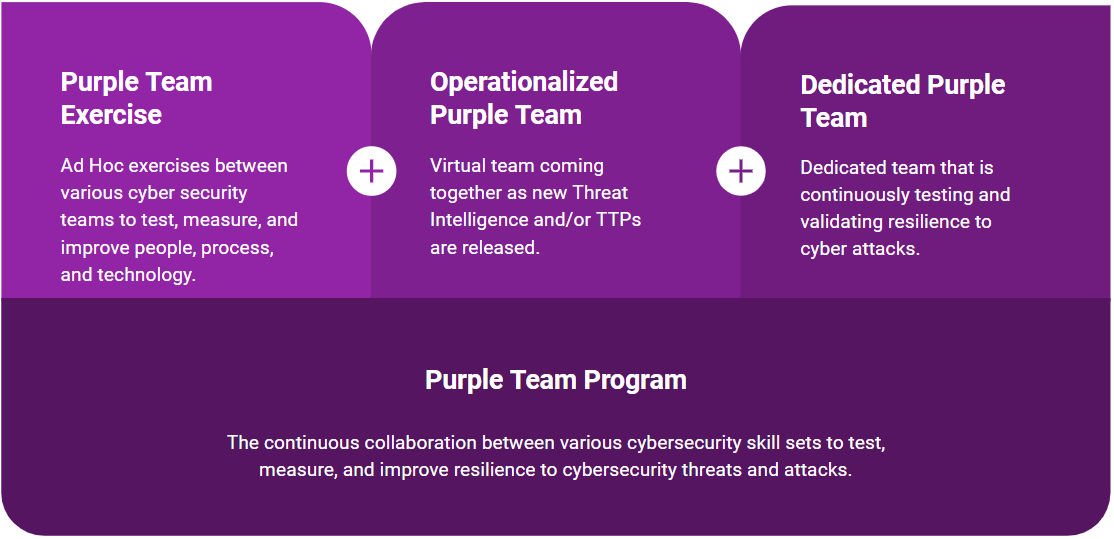 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
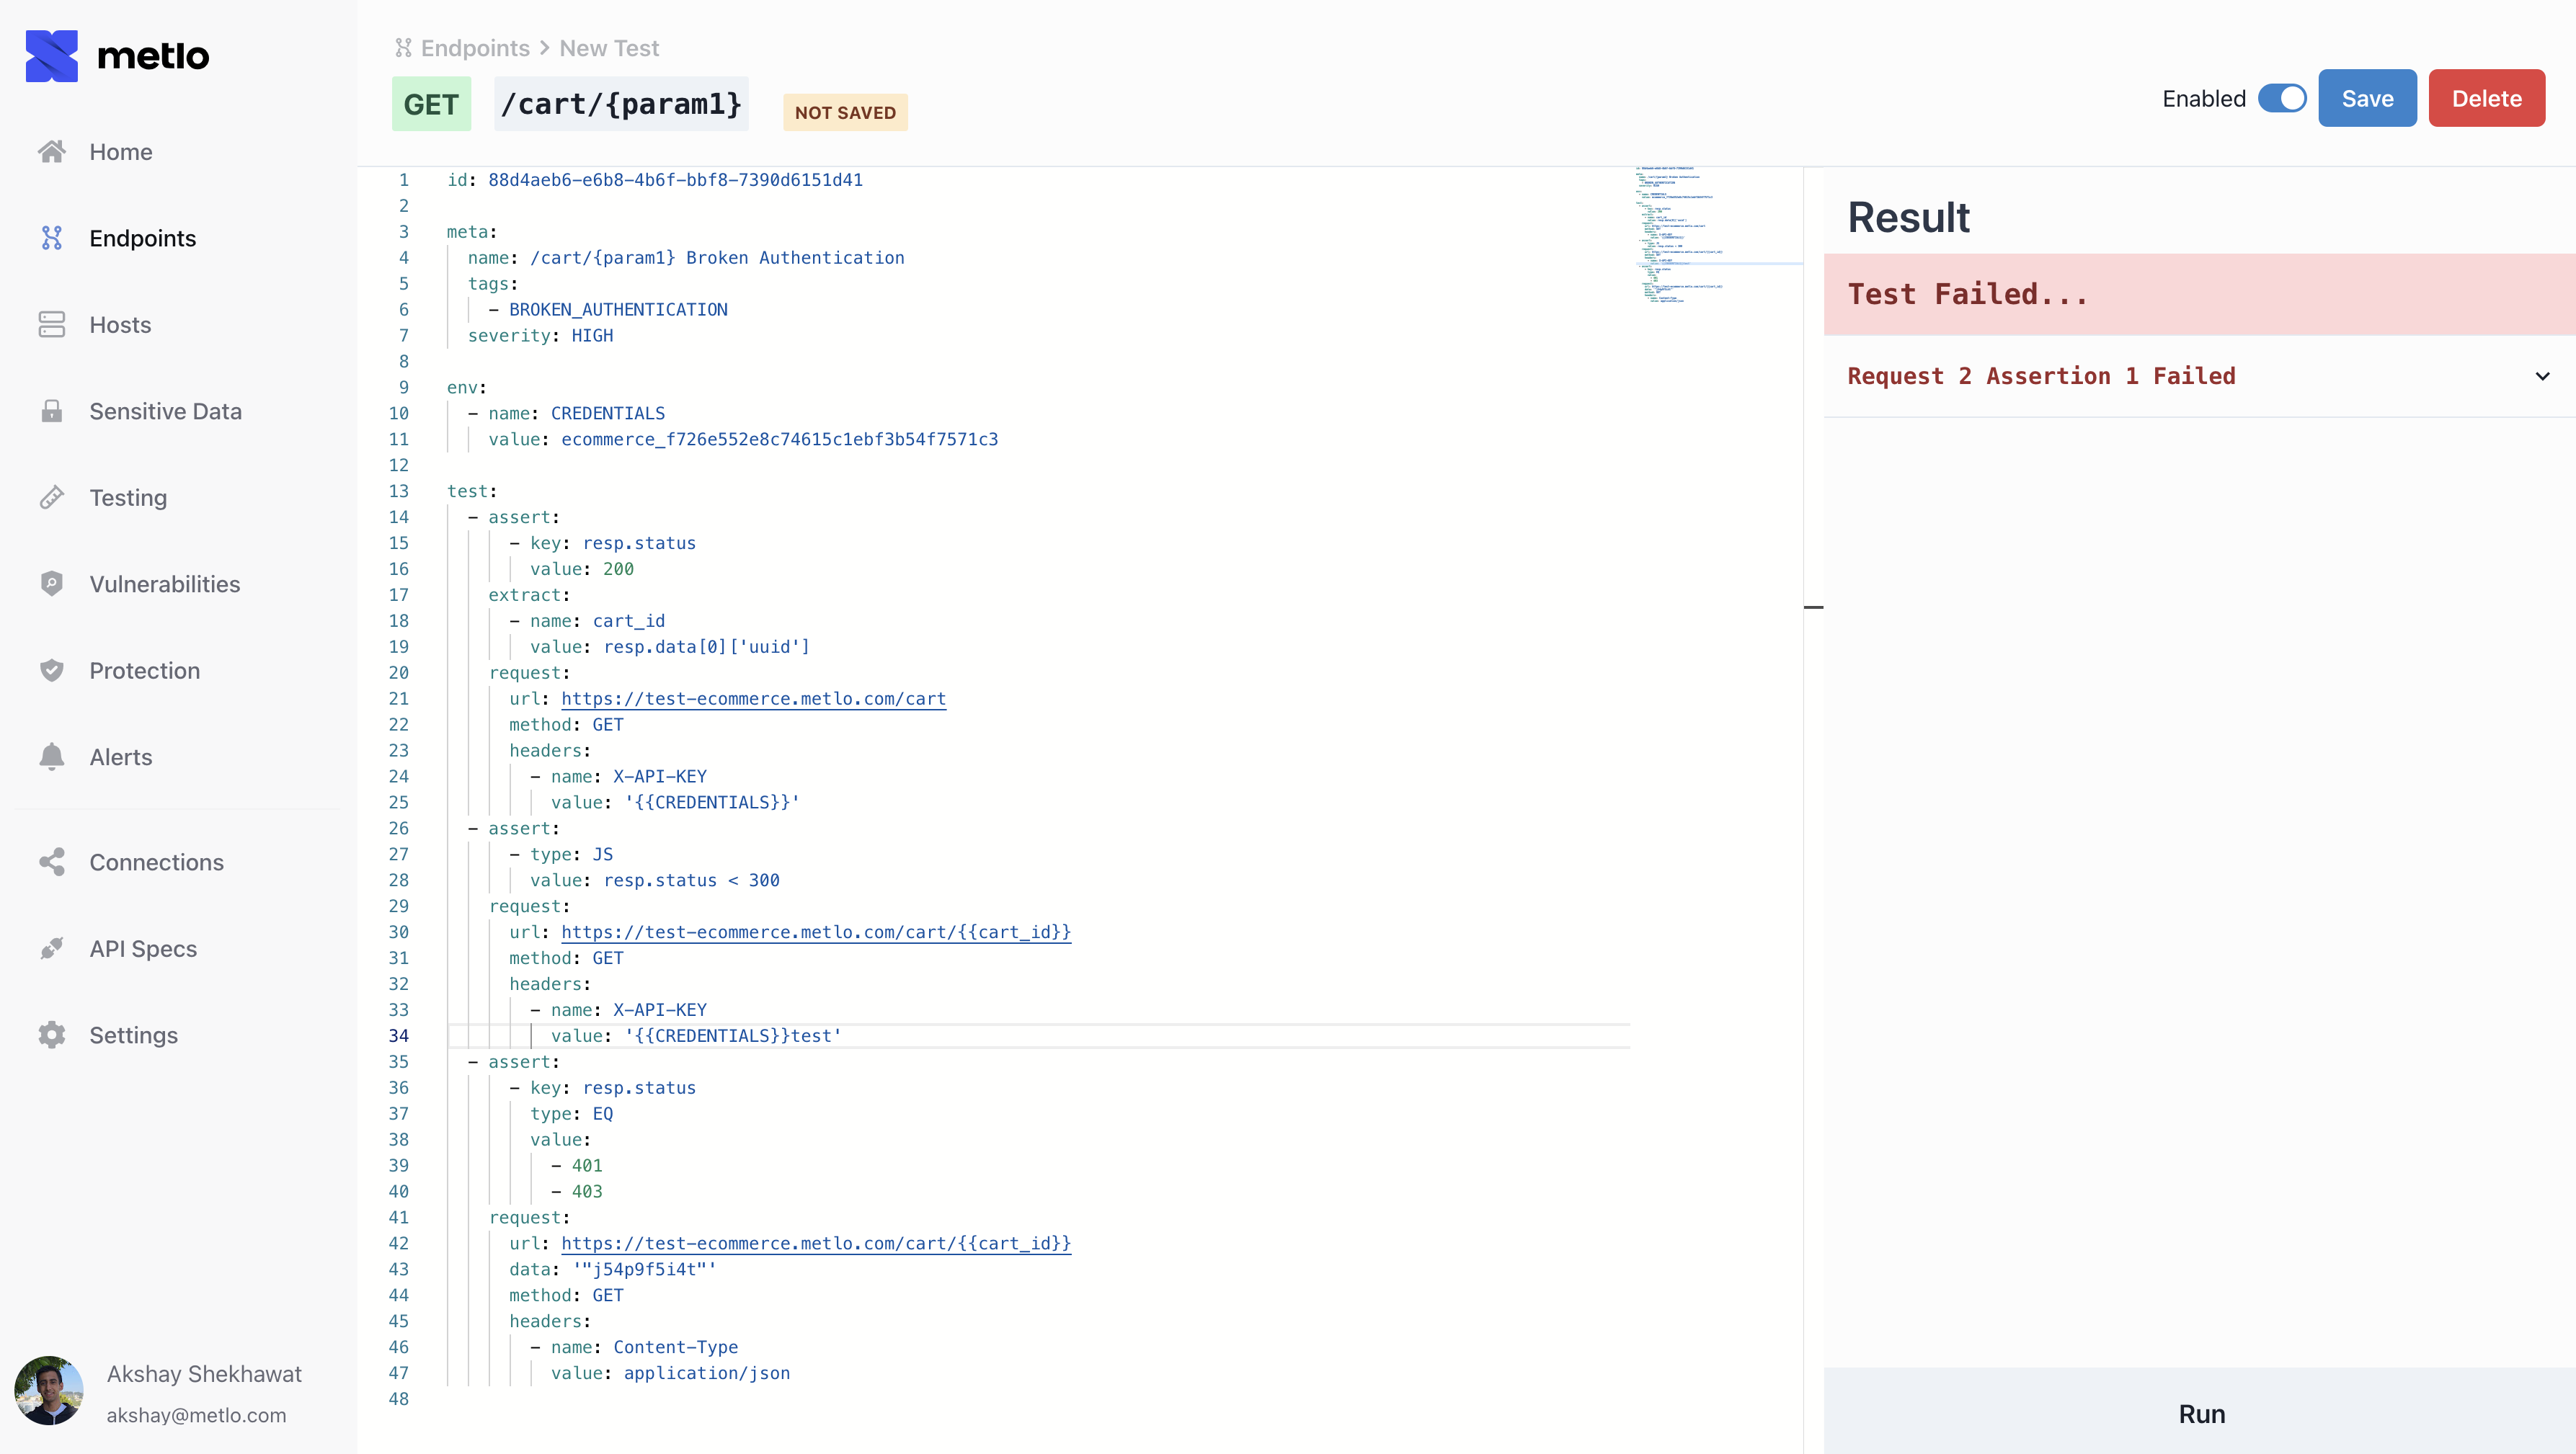 metlo-labs/metlo
Metlo is an open-source API security platform.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 syworks/waidps
Wireless Auditing, Intrusion Detection & Prevention System
 neo23x0/raccine
A Simple Ransomware Vaccine
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…








