

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/antiwar3/py
Defensive ToolsMemory ForensicsMalware AnalysisDigital ForensicsIntrusion DetectionIncident Response
GitHubantiwar3/py

py

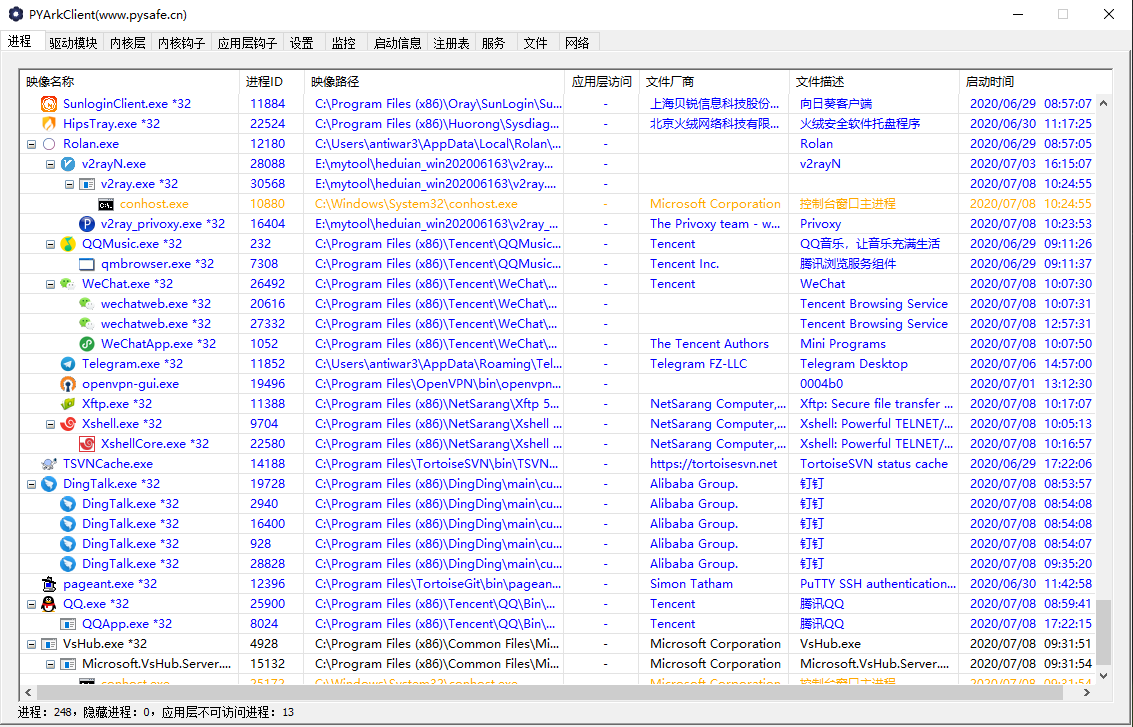
飘云ark(pyark)

View Repository
52972402 months agoReviewed by Kitploit
Share
Website

if you find any bugs report it at Github user issues

Still in development

Support win7 to win11(last)

image

MCP 配置 / MCP 使用方法

PYArkClient 内置一个 MCP Streamable HTTP 服务端,任意 MCP 客户端(Claude Code / Claude Desktop / CodePilot 等)都能调用它提供的内核级 ARK 工具(进程 / 线程 / 模块 / 内存 / SSDT / 回调 / 注入 / dump 等)。

1. 前置条件

  • 以 管理员 身份运行 PYArkClient.exe(工具需要驱动连接;未连接时调用工具会返回 driver not connected, restart PYArkClient as admin)。

  • 打开应用内的「AI 对话 / Chat」面板,勾选 「开启MCP接口」 复选框(默认关闭)。勾选后写入 McpConfig.ini 并启动 MCP 服务。

  • 或手动在 exe 同目录写 McpConfig.ini:

    [MCP]
    Enable=1
    
  • MCP 服务地址:http://127.0.0.1:8765/mcp(JSON-RPC 2.0 · Streamable HTTP)。

2. 客户端配置

Claude Code

claude mcp add --transport http pyark http://127.0.0.1:8765/mcp

启动 Claude Code 前,先以管理员启动 PYArkClient 并勾选「开启MCP接口」。

Claude Desktop(claude_desktop_config.json)

{
  "mcpServers": {
    "pyark": {
      "type": "http",
      "url": "http://127.0.0.1:8765/mcp"
    }
  }
}

其它客户端:新增一个 http(Streamable HTTP)传输的 MCP server,端点填 http://127.0.0.1:8765/mcp。

3. 手动自检

curl -X POST http://127.0.0.1:8765/mcp \
  -H "Content-Type: application/json" \
  -d '{"jsonrpc":"2.0","id":1,"method":"tools/list","params":{}}'

请求结构:

POST /mcp
{"jsonrpc":"2.0","id":1,"method":"tools/call","params":{"name":"list_processes","arguments":{}}}
  • 成功返回 result.content[0].text,是一个 JSON 字符串。
  • 无 id 的通知类消息返回 HTTP 202。
  • 服务端带 Access-Control-Allow-Origin: *,支持浏览器 / Electron 直接 fetch。

4. 可用工具(部分)

  • 进程:list_processes list_threads list_modules get_process_info get_process_peb kill_process suspend_process resume_process protect_process enum_process_handles enum_process_windows enum_process_privileges enum_process_hotkeys
  • 线程:kill_thread suspend_thread resume_thread
  • 模块:get_image_basic_info get_image_path unload_process_module unload_driver
  • 内存:query_memory enum_memory_regions read_memory write_memory protect_memory enum_process_pml4 / pdpt / pd / pt
  • 内核:enum_ssdt_hooks recover_ssdt enum_shadow_ssdt_hooks enum_idt_hooks enum_callbacks enum_filters enum_minifilters enum_io_timers scan_driver_routines enum_object_types enum_object_hooks
  • 注入 / Dump:dump_process dump_process_module dump_driver_memory bb_inject bb_map_driver


Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →





