#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 0x90n/infosec-black-friday
All the deals for InfoSec related software/tools this Black Friday
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 thinkst/canarytokens
Canarytokens helps track activity and actions on your network
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
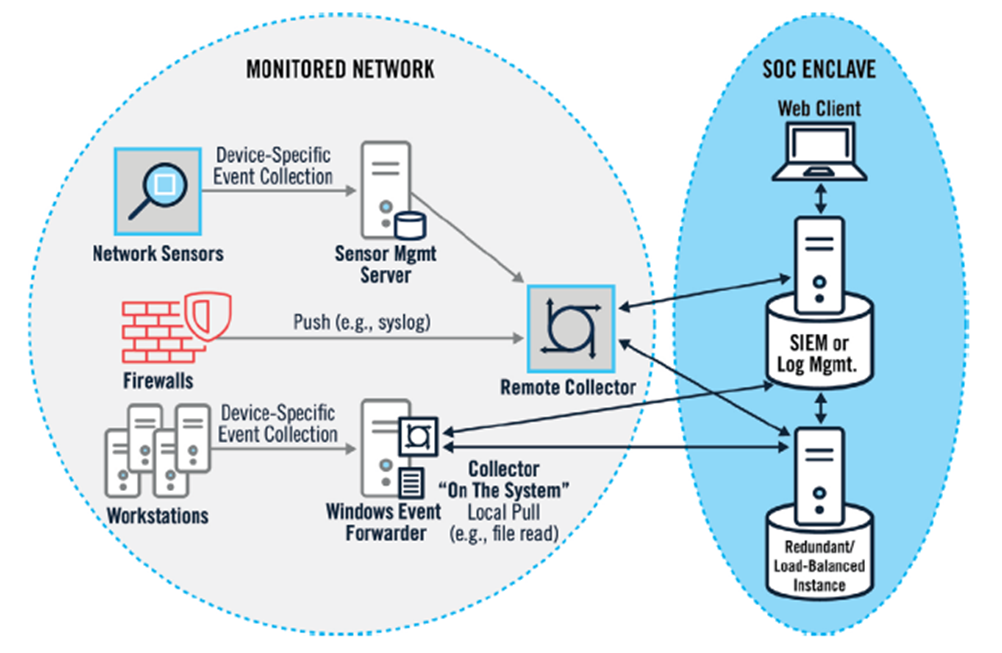 cyb3rxp/awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 freedomofpress/dangerzone
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
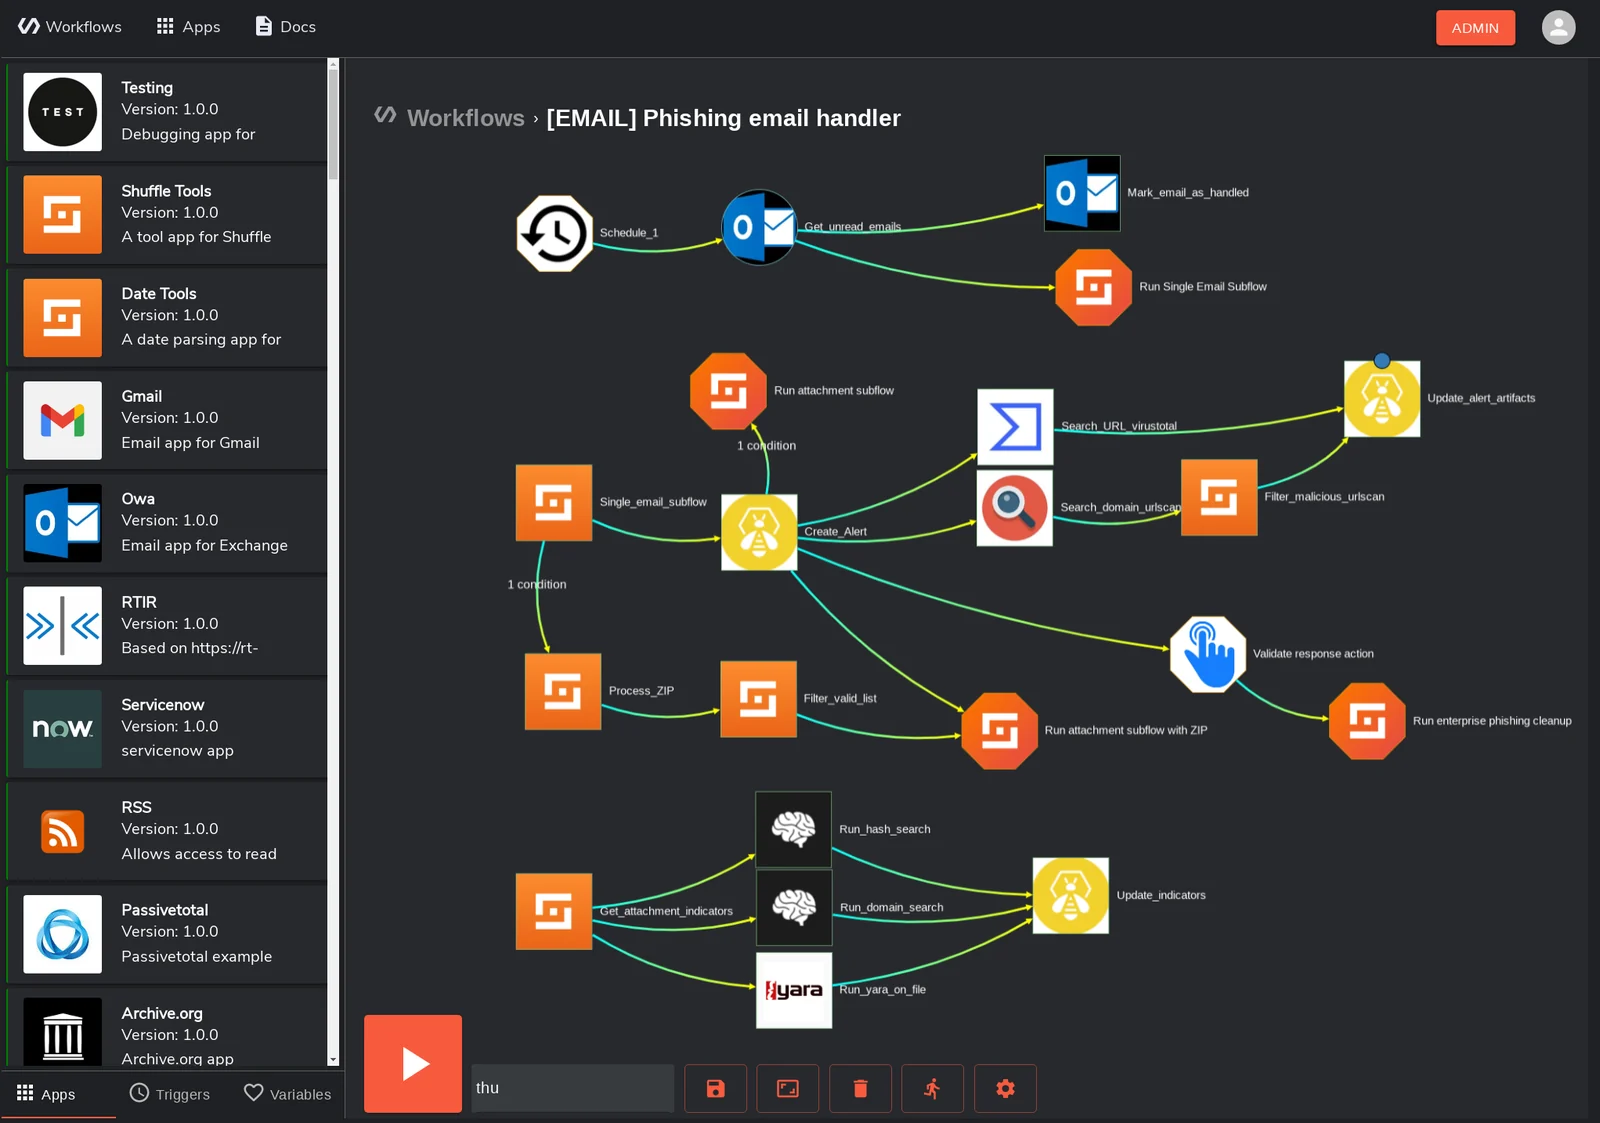 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
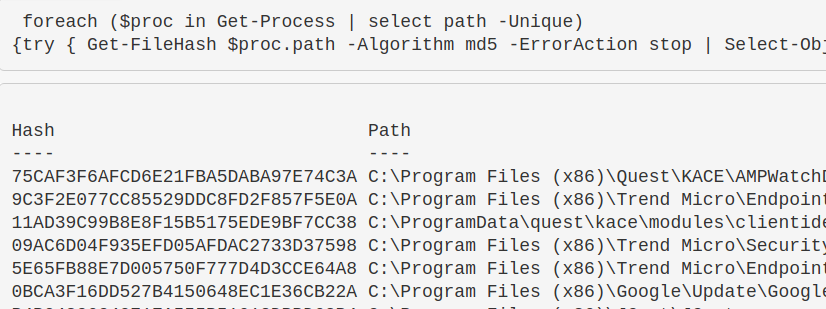 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool