#1
IR playbooks, triage, case management, evidence collection, and incident management tools.
Kitploit recommended
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 yeti-platform/yeti
Your Everyday Threat Intelligence
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
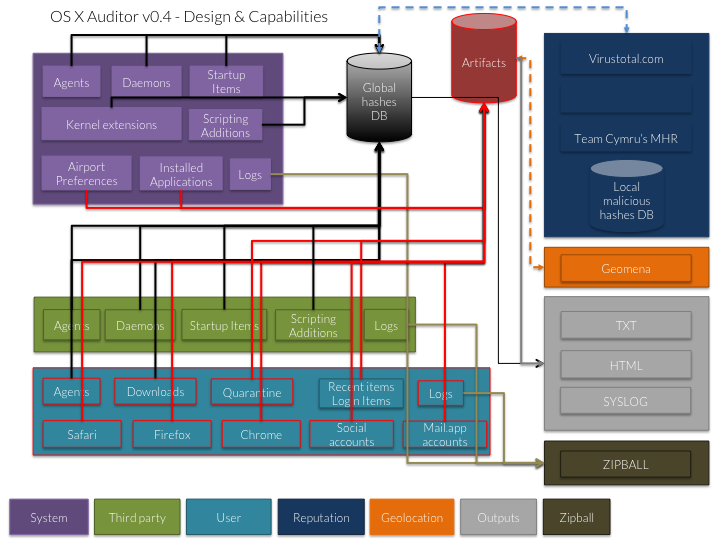 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 beenuar/aisoc
Open-source AI-powered Security Operations Center — alert fusion, purple-team drills, agent-assisted triage, MITRE ATT&CK investigation.…
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
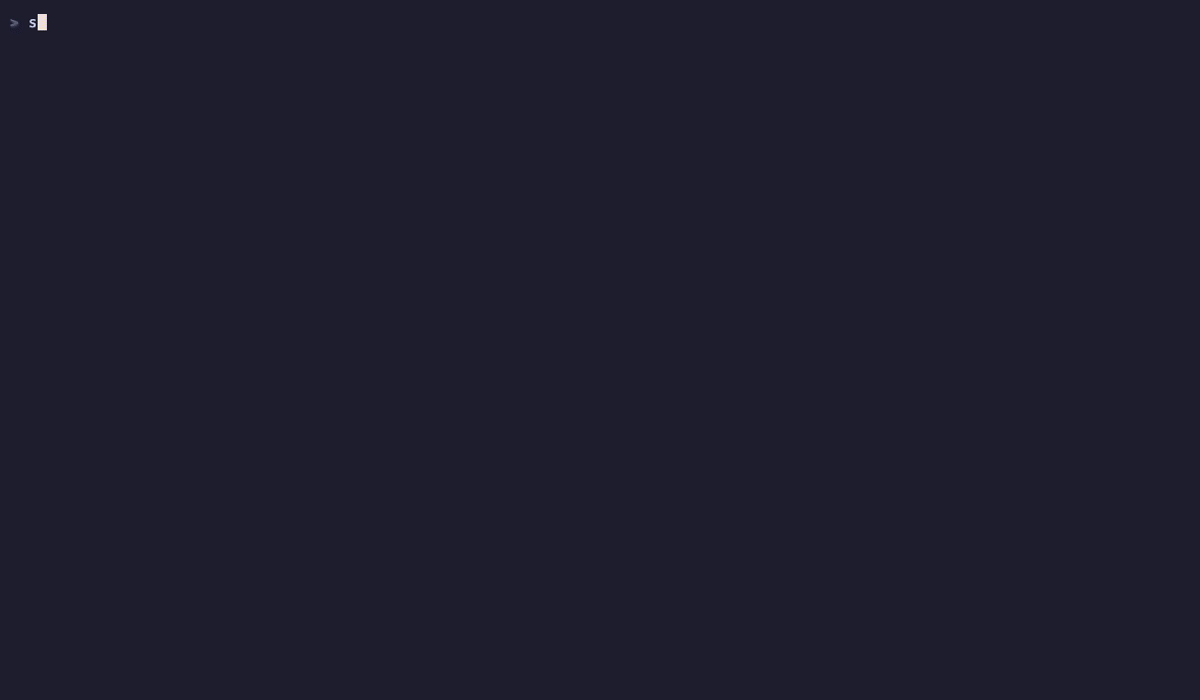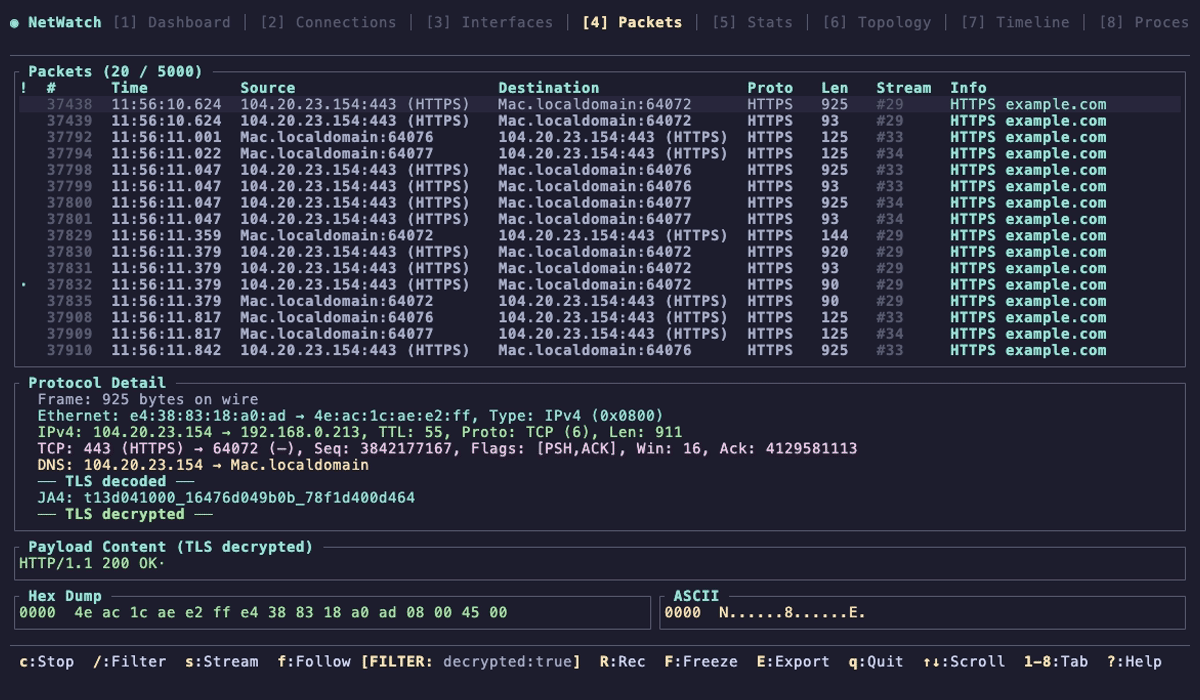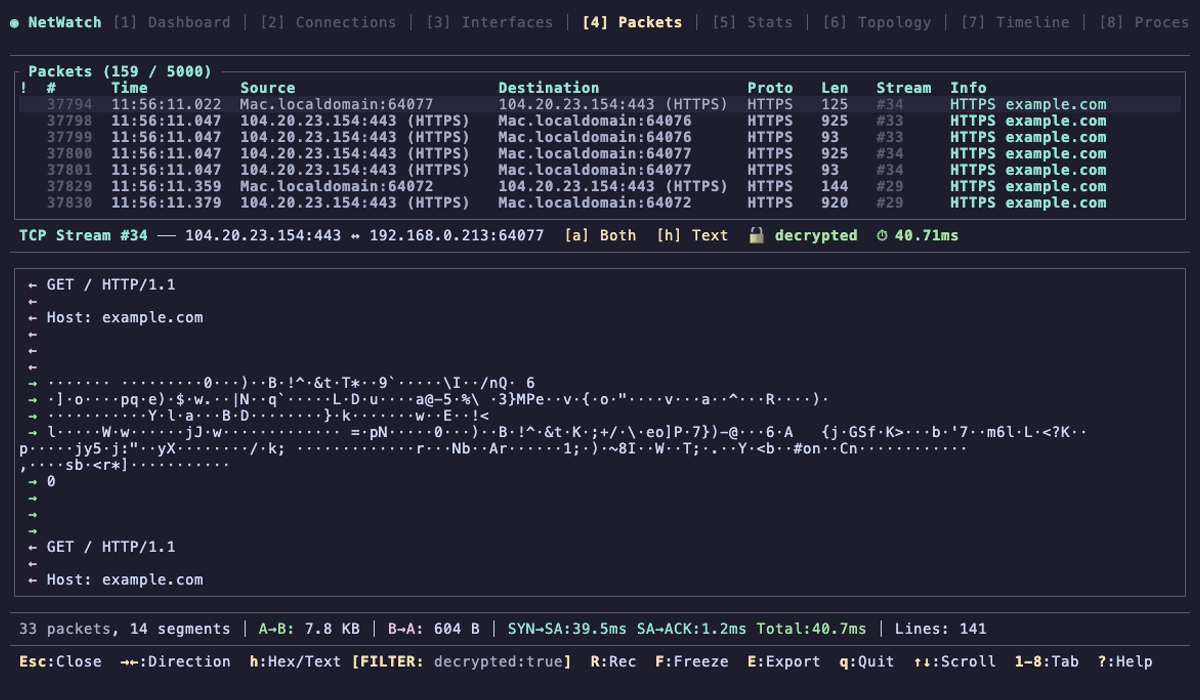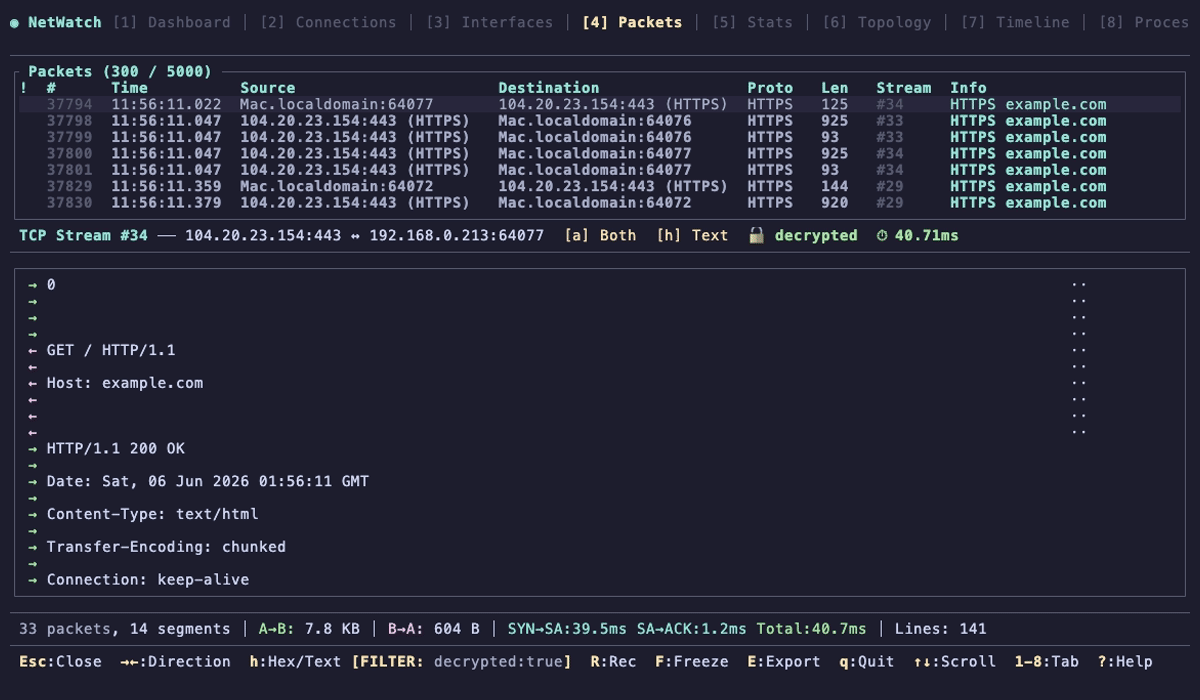 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.