
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability intelligence.


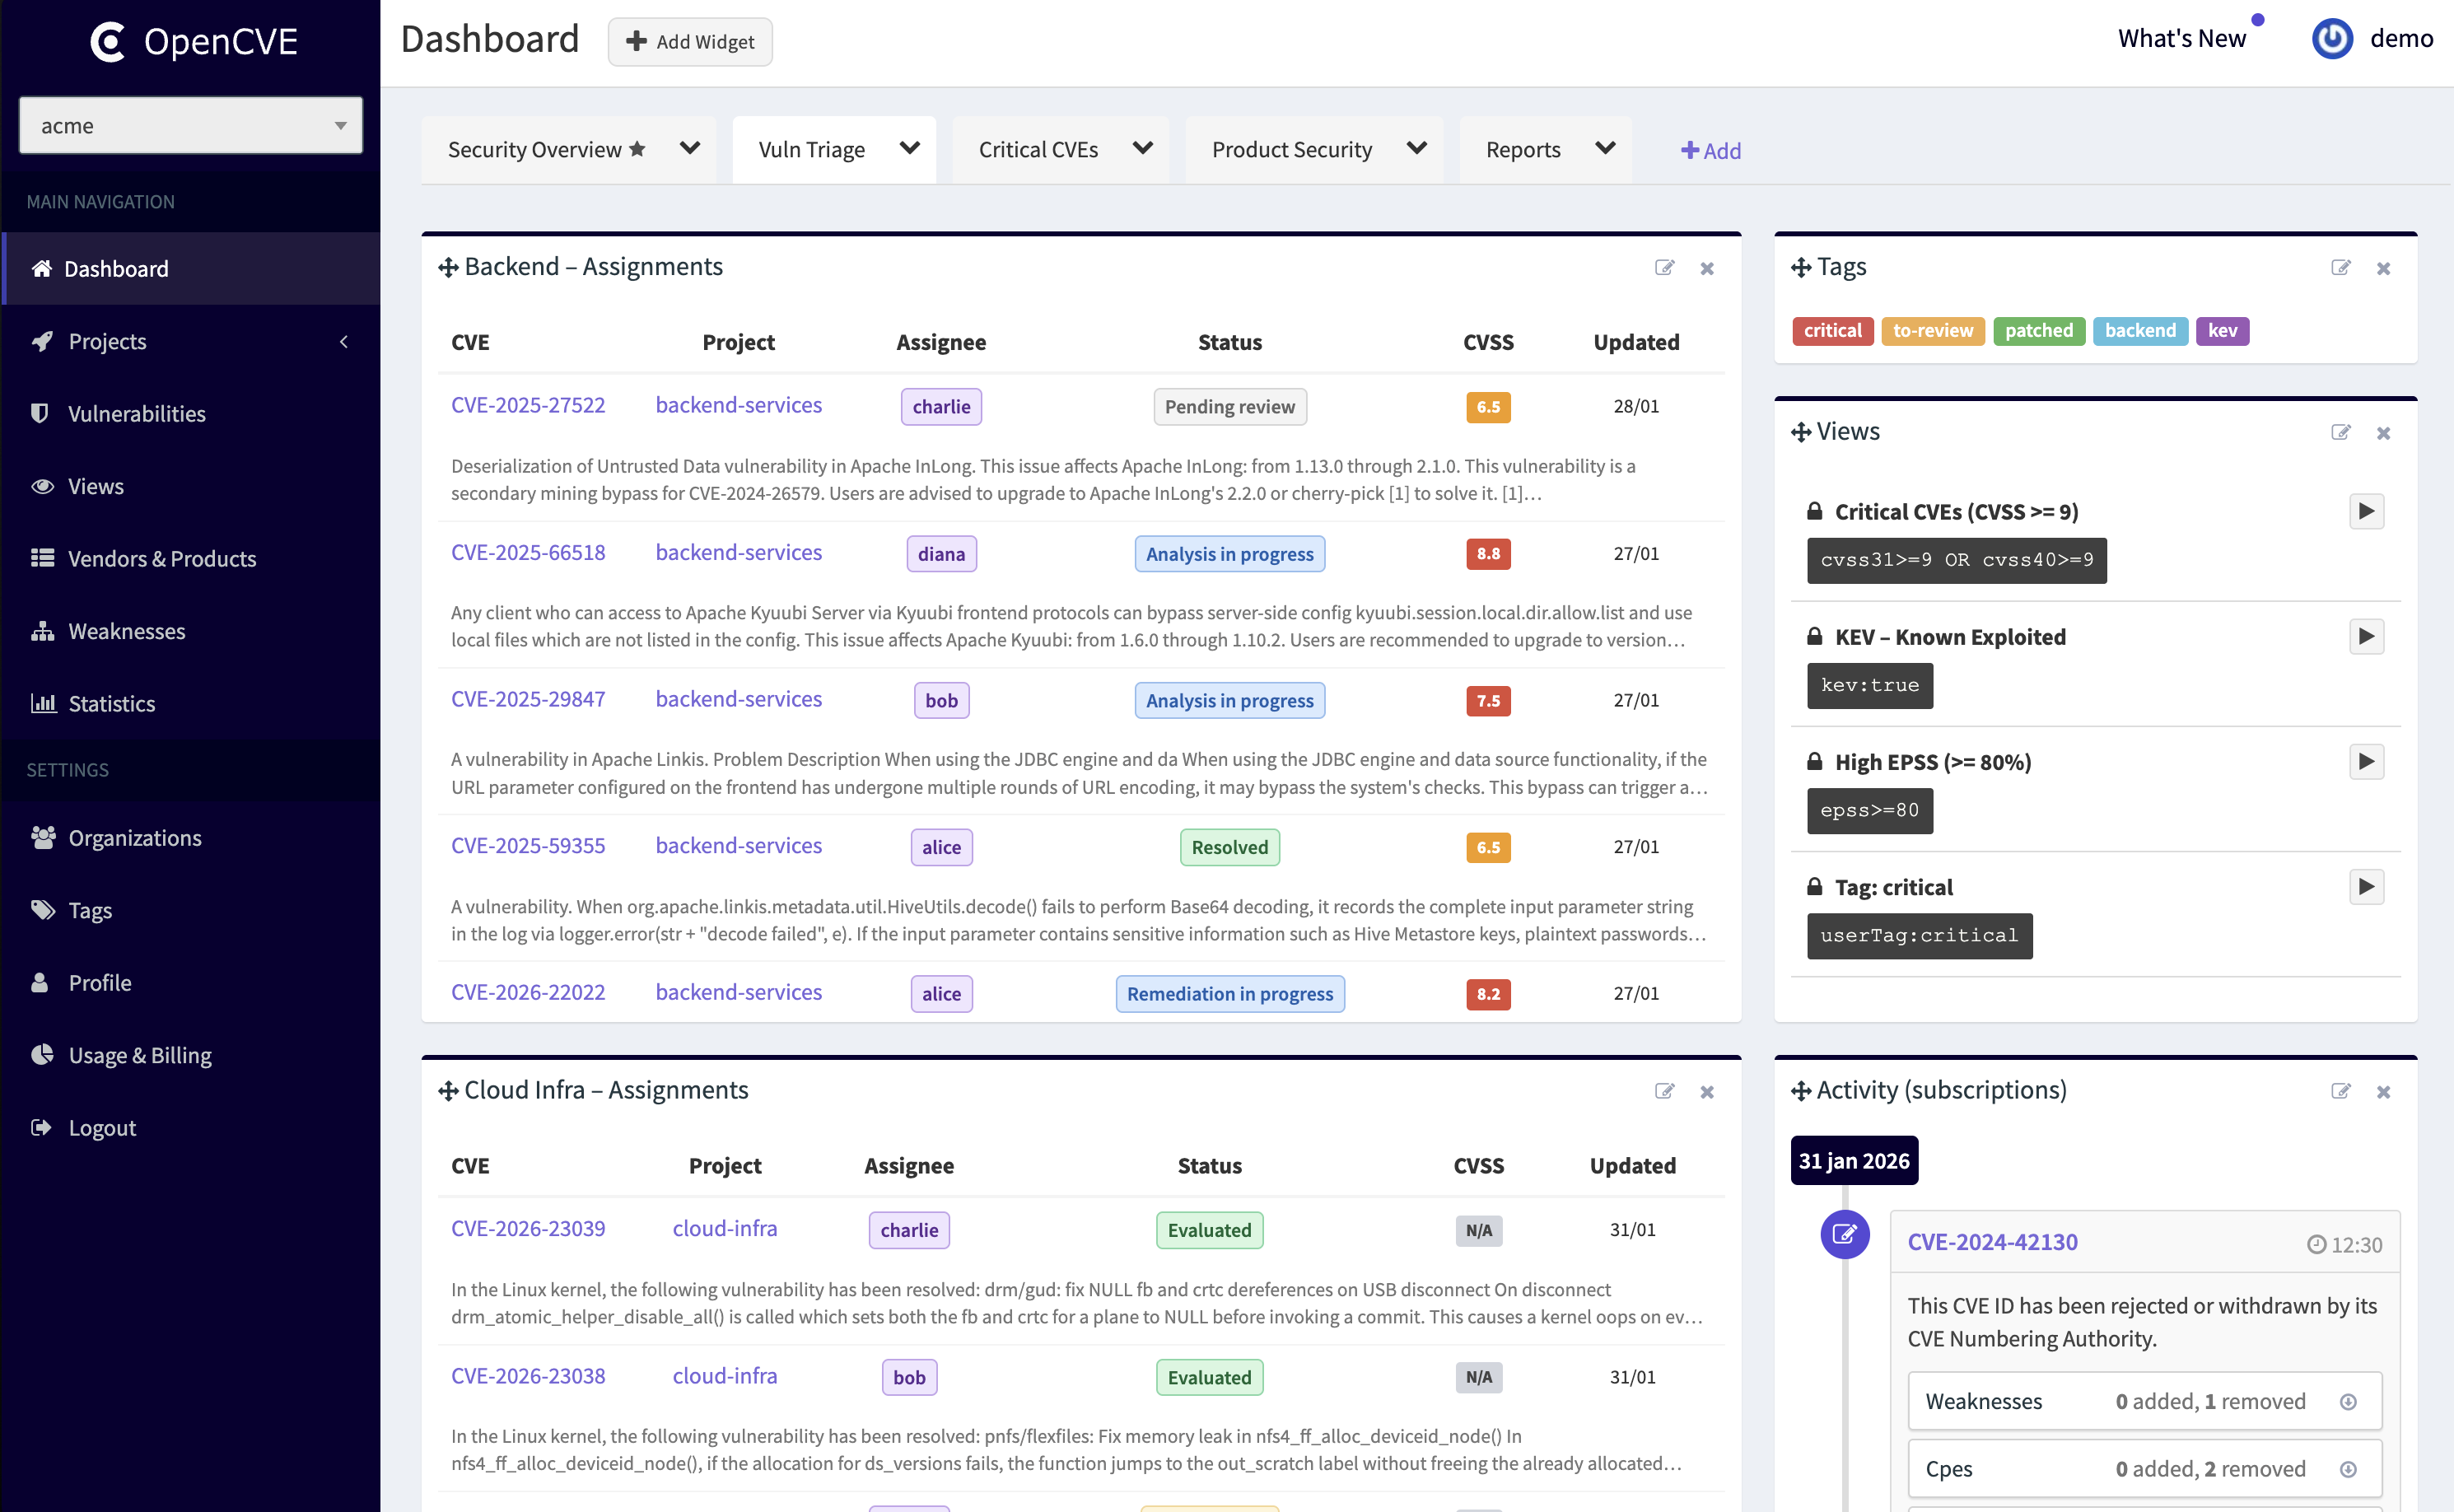
OpenCVE is a Vulnerability Intelligence Platform that helps you monitor and manage CVEs efficiently.
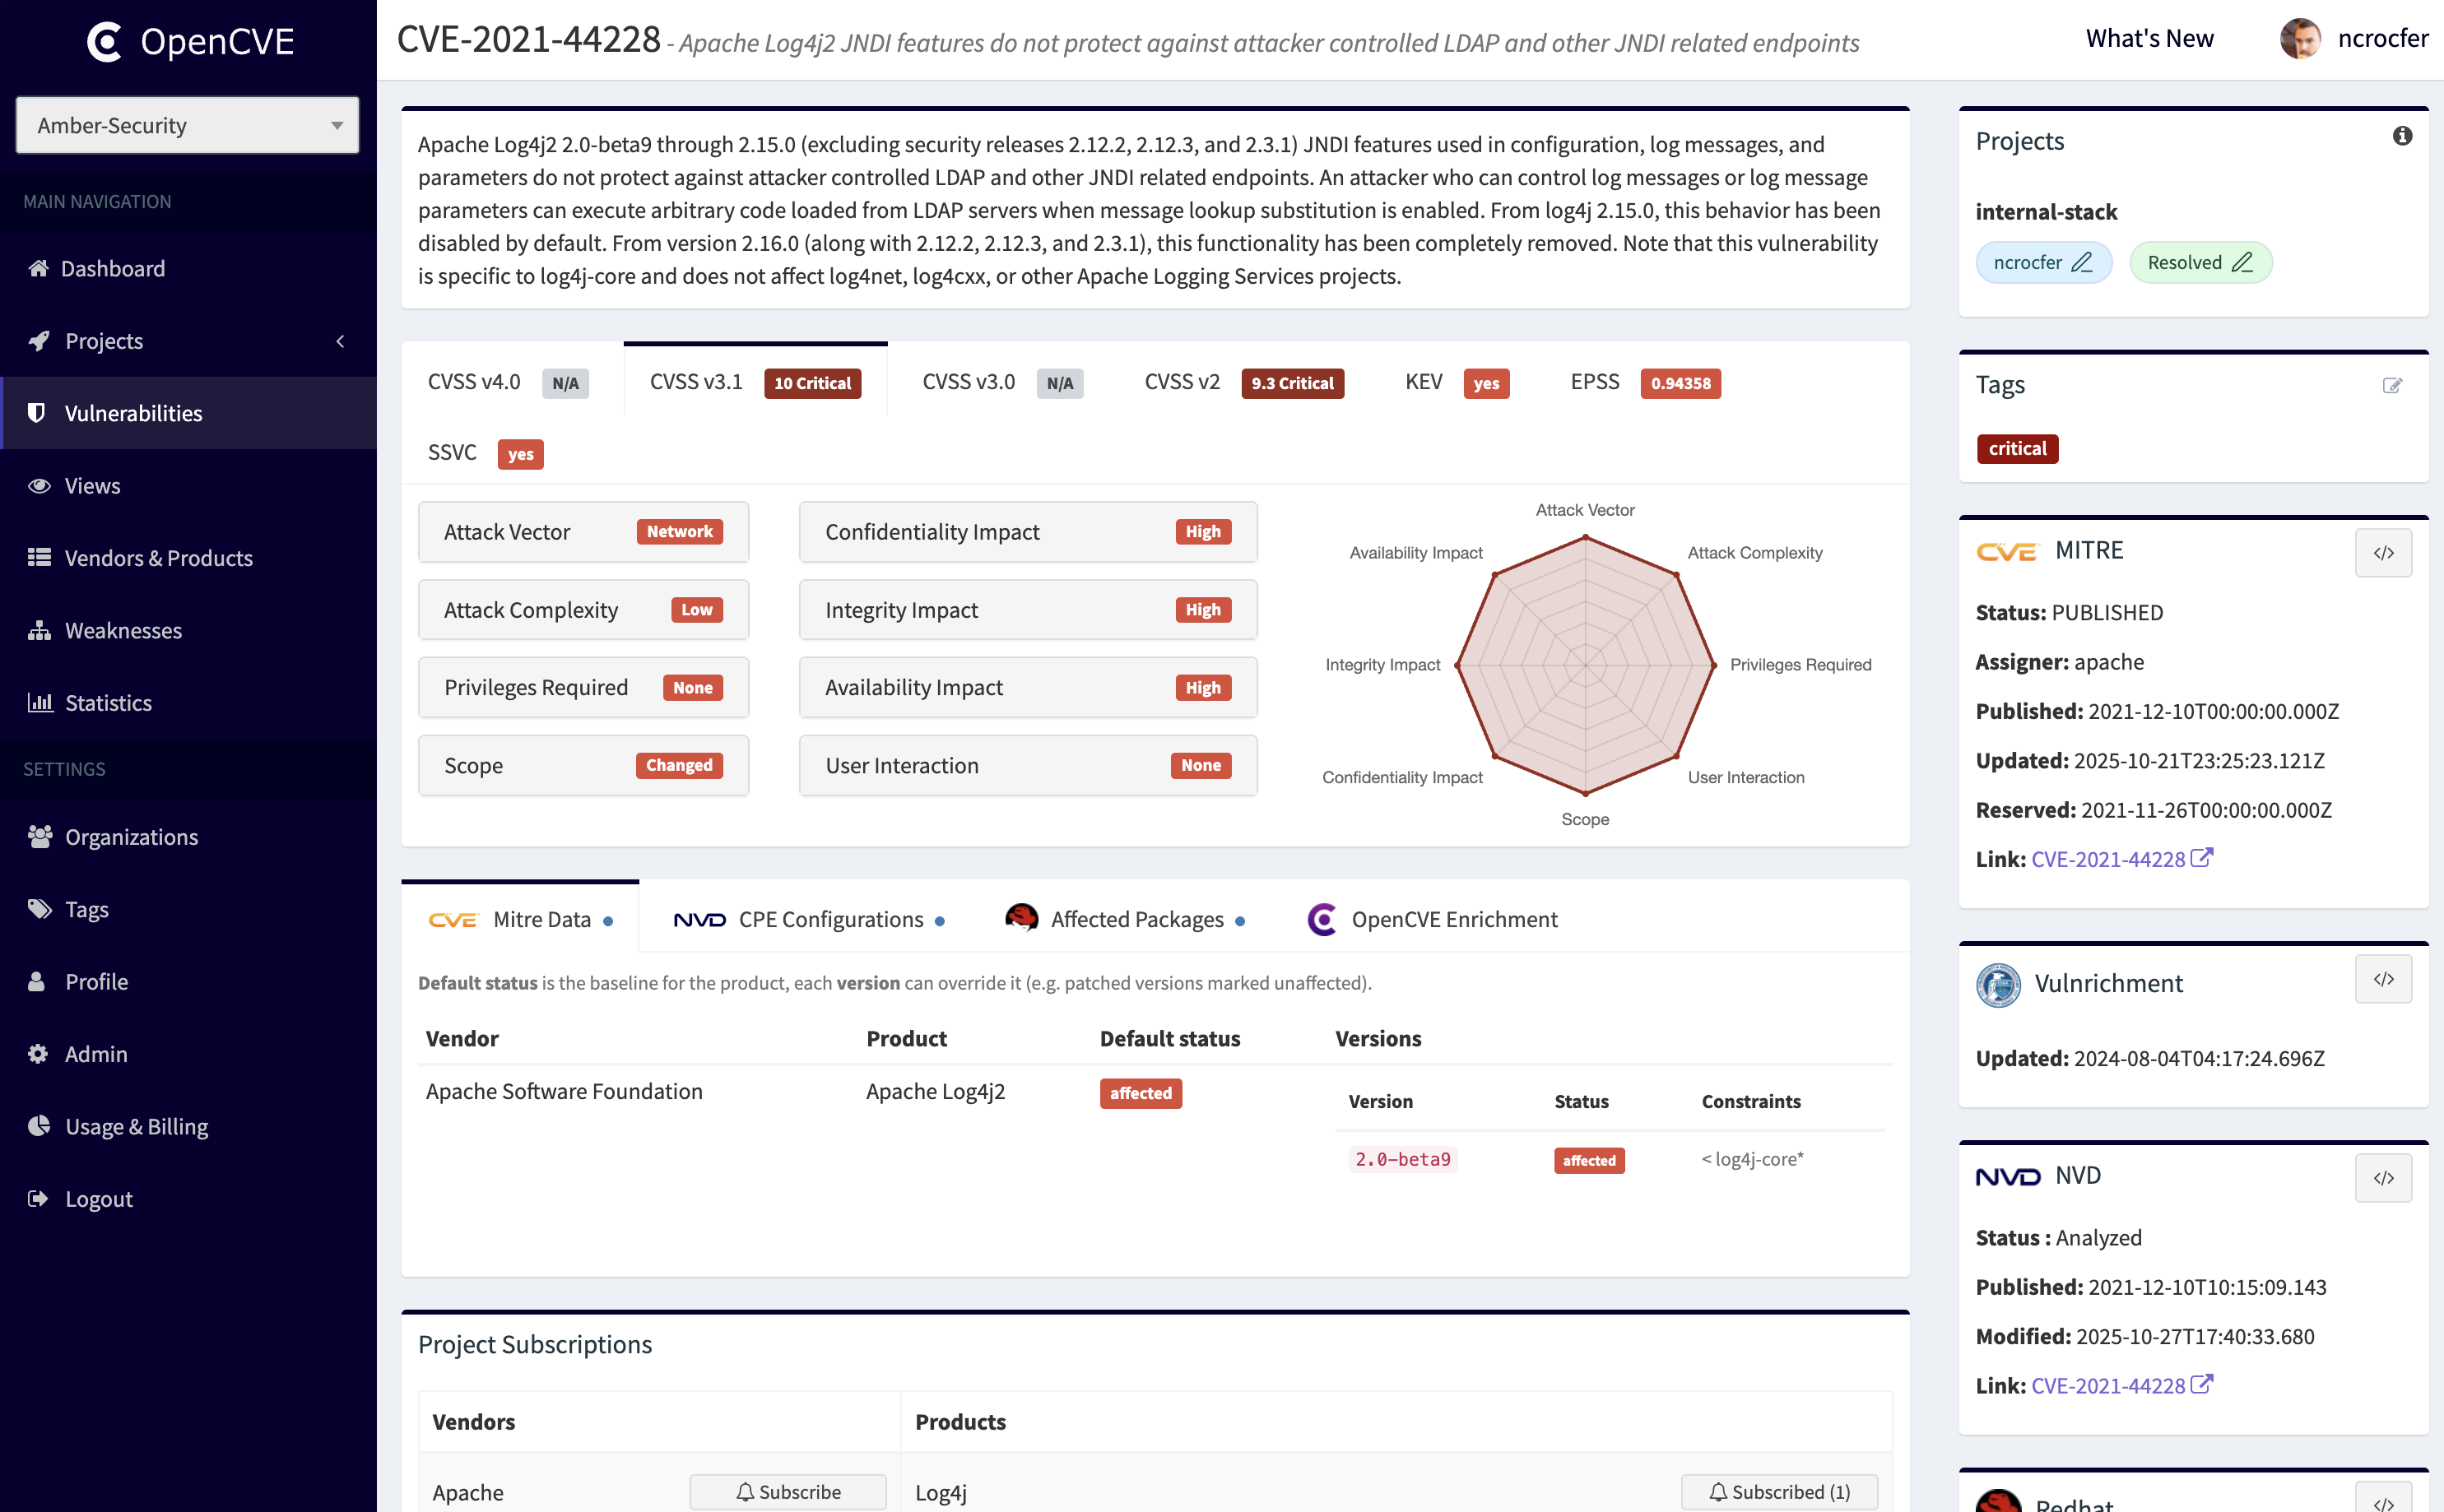
It aggregates vulnerabilities from multiple sources (MITRE, NVD, RedHat, Vulnrichment...) and lets you filter, track, and organize them by vendor, product, severity, and more.
You can subscribe to products, receive alerts, analyze changes, and collaborate with your team — all through a simple and powerful interface. Assign members to CVEs to track progress (e.g. under analysis, risk accepted) and keep everyone aligned.
OpenCVE is available as both a self-hosted Community edition and a hosted Cloud platform.
The Community edition allows you to track CVEs, organize your monitoring, and build your own workflows.
For teams that need more advanced capabilities, OpenCVE Cloud provides additional features such as:
👉 Learn more: https://www.opencve.io/pricing
Use the hosted version at https://www.opencve.io — no setup required, with access to advanced features and enterprise capabilities.
Run OpenCVE on your own infrastructure using Docker. See the installation guide for more details.


We warmly welcome contributions to OpenCVE!
We have recently received a substantial number of contributions, potentially in part due to AI coding tools. Every PR still needs human review and ongoing maintenance, and our capacity is limited.
Before starting work, please personally read our Contributing Guidelines, whether you use AI tools or not.
For features and significant behavior changes, discuss the need and proposed approach with the maintainers and wait for explicit agreement before implementation. An existing issue does not mean that a solution has been approved or prioritized.
Small, focused bug fixes and documentation corrections are welcome without prior discussion in most cases. Please coordinate before opening multiple unrelated PRs.
AI-assisted contributions are welcome, provided you understand, verify and take responsibility for your changes. Review and merge are subject to project priorities and maintainer availability.
OpenCVE is actively developed and regularly improved.
⭐ Star this repository and 🔔 watch releases to be notified of future updates.
OpenCVE Community is released under a Business Source License (BSL), allowing free usage with some limitations for commercial use.
See the LICENSE file for more details.
