#1
Firmware extraction, unpacking, emulation, vulnerability discovery, and binary analysis tools.
Kitploit recommended
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
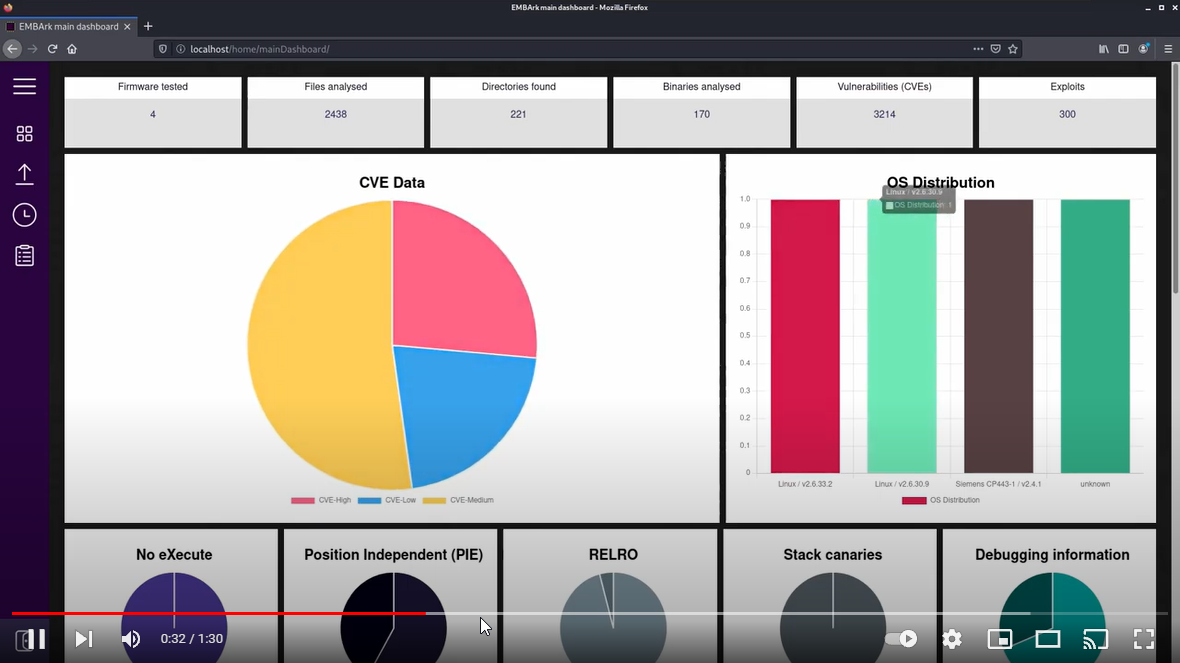 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 iceman1001/chameleonmini-rebooted
Chameleon Mini revE rebooted - Iceman Fork, the ChameleonMini is a versatile contactless smartcard emulator (NFC/RFID)
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
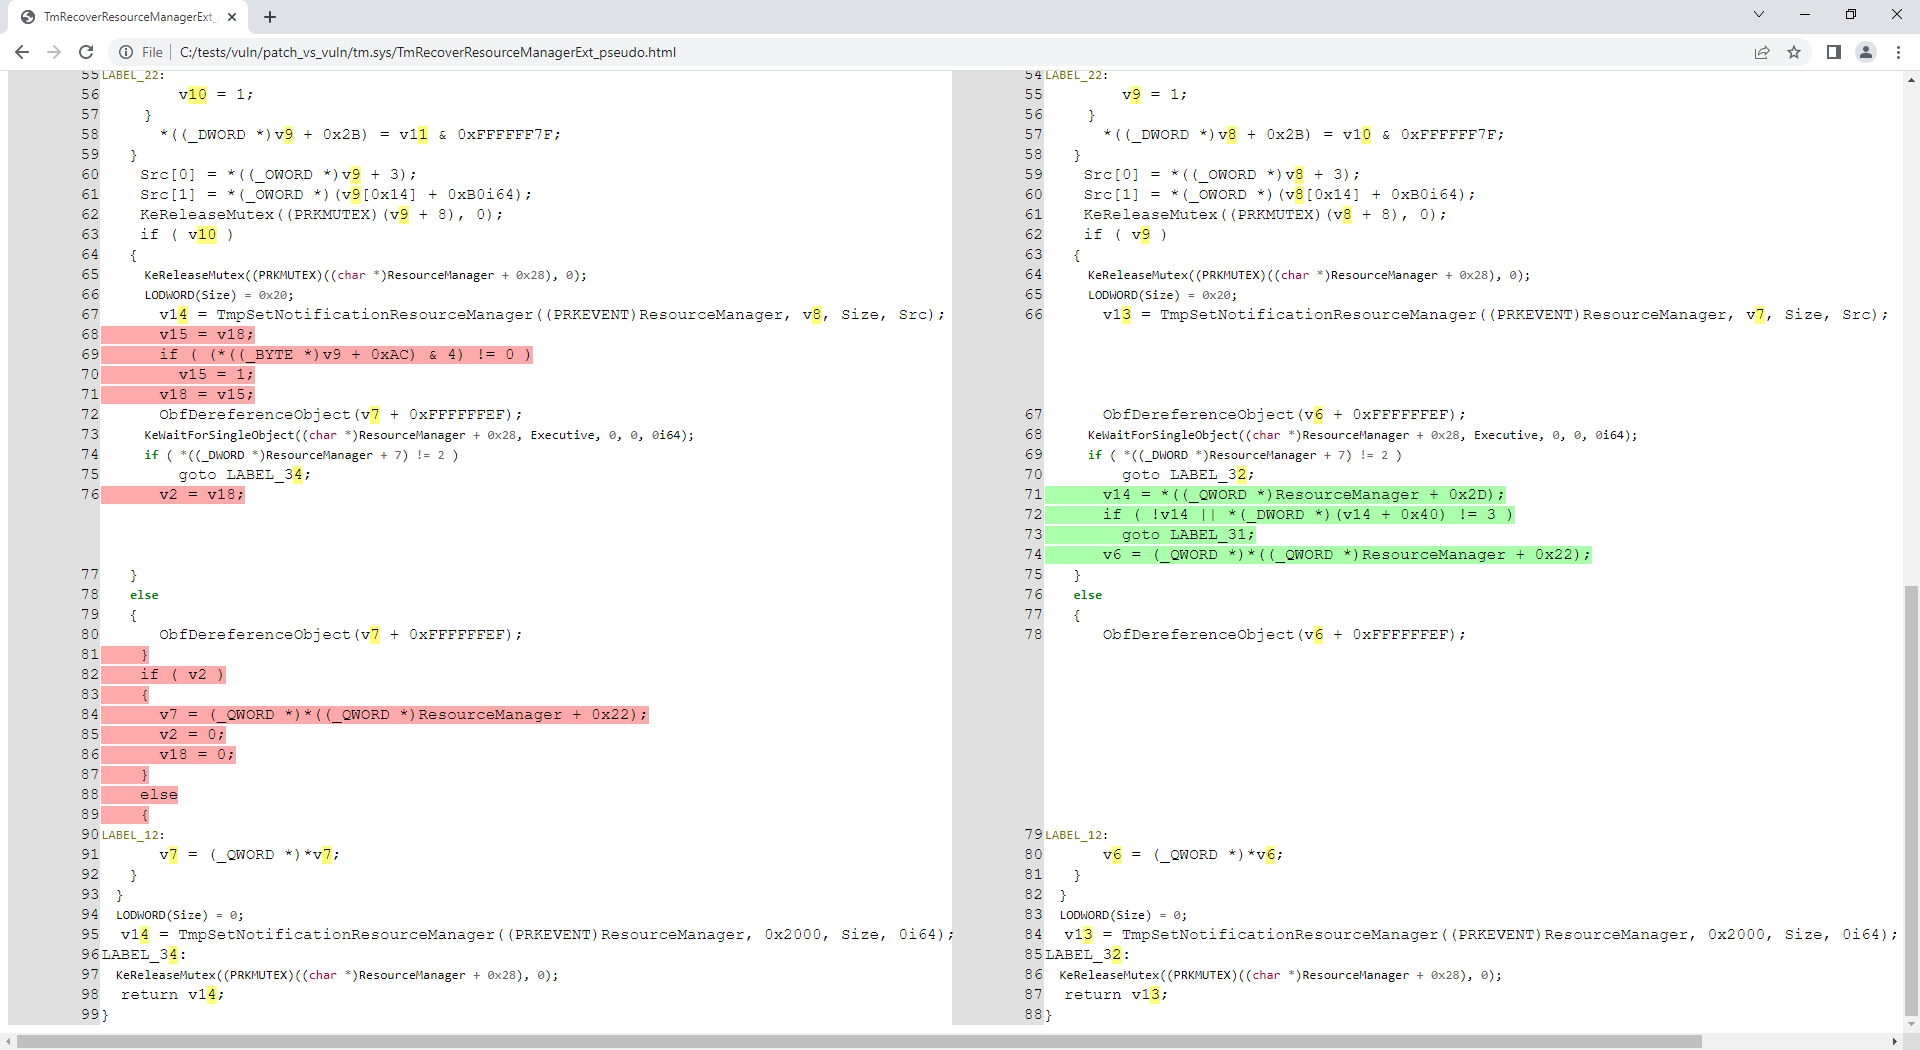 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
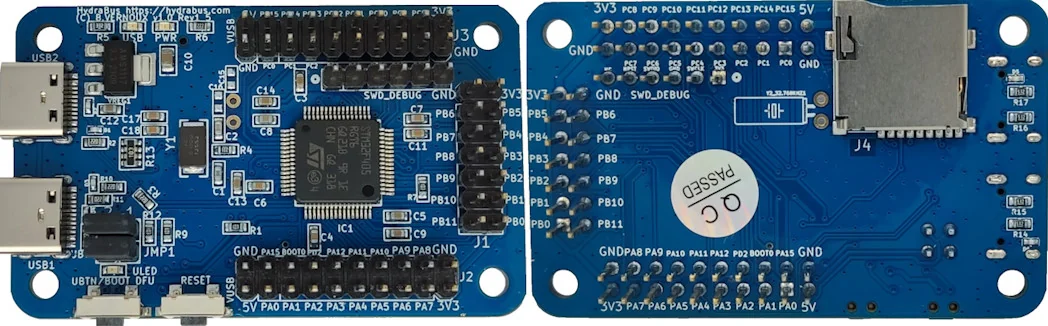 hydrabus/hydrafw
Open-source firmware for HydraBus, a multi-tool for embedded hardware debugging, hacking, and penetration testing, supporting protocols like SPI,…
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 colton1skees/dna
LLVM based static binary analysis framework
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
 bazad/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
 snare/ida-efiutils
Some scripts for IDA Pro to assist with reverse engineering EFI binaries
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…