
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 xairy/vmware-exploitation
A collection of links related to VMware escape exploits
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 dirkjanm/cve-2020-1472
PoC for Zerologon - all research credits go to Tom Tervoort of Secura
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
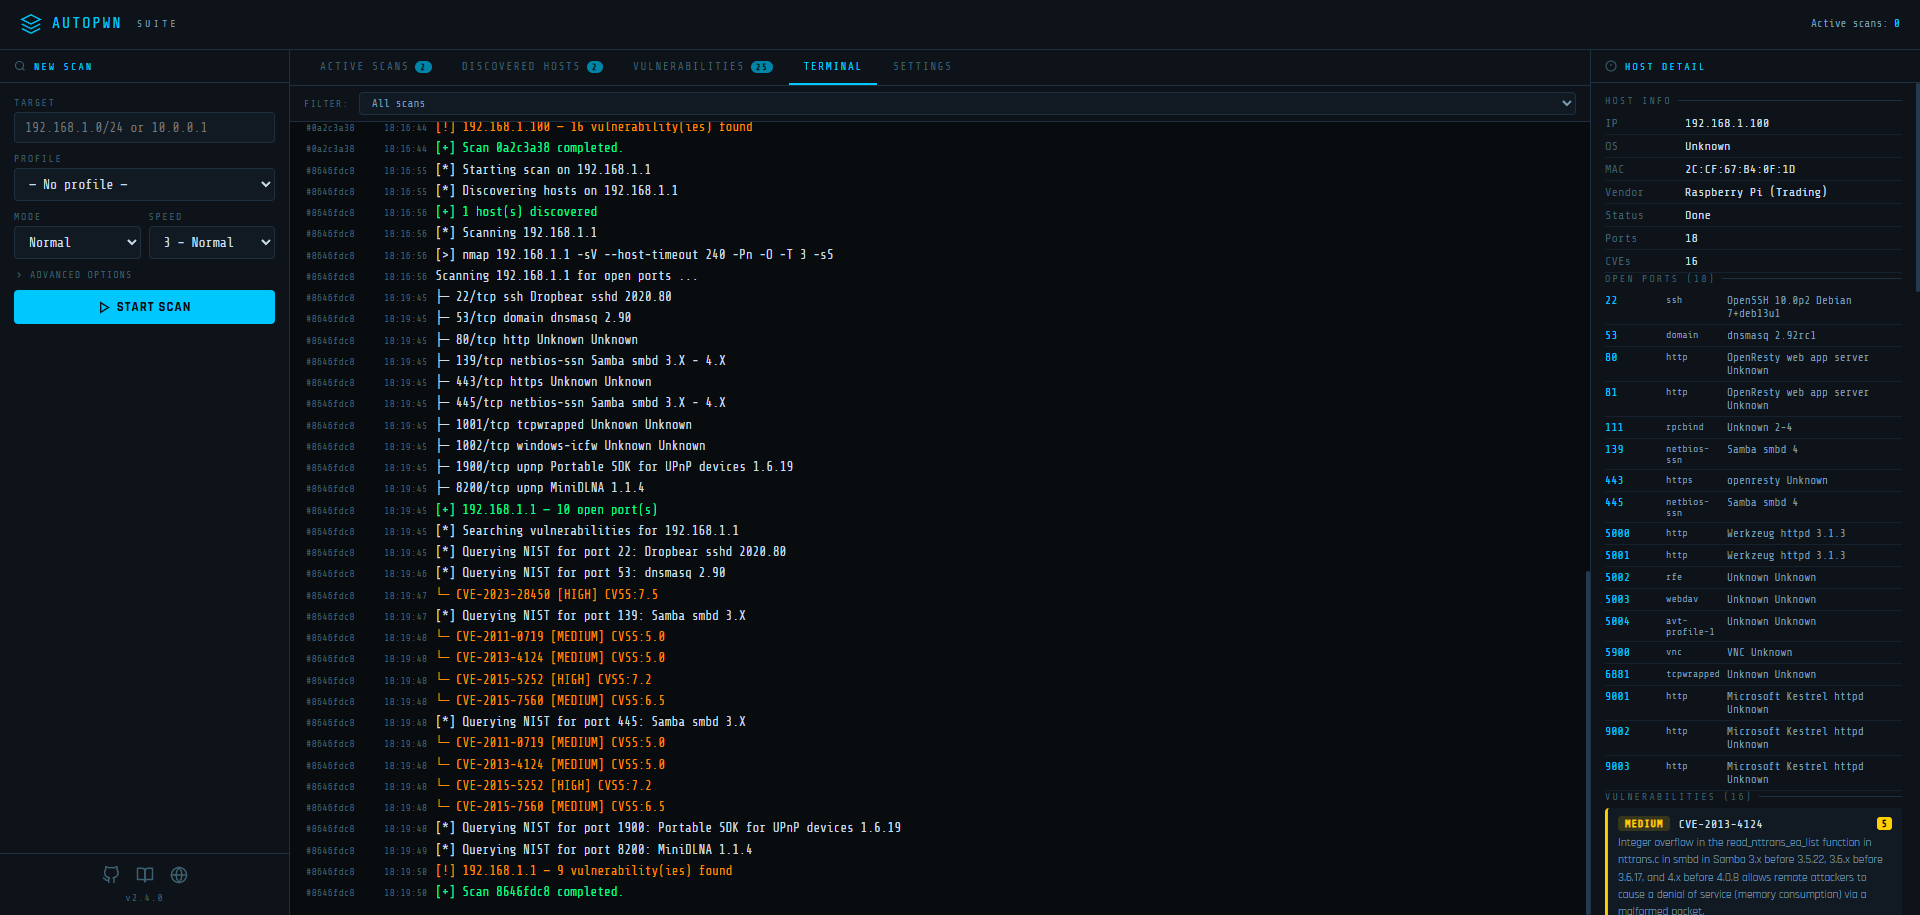 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 bohops/ultimatewdacbypasslist
A centralized resource for previously documented WDAC bypass techniques
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 sweetsoftware/ares
Python botnet and backdoor
 harishsg993010/damn-vulnerable-mcp-server
Damn Vulnerable MCP Server
 bats3c/shad0w
A post exploitation framework designed to operate covertly on heavily monitored environments
 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
 notselwyn/cve-2024-1086
Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including…
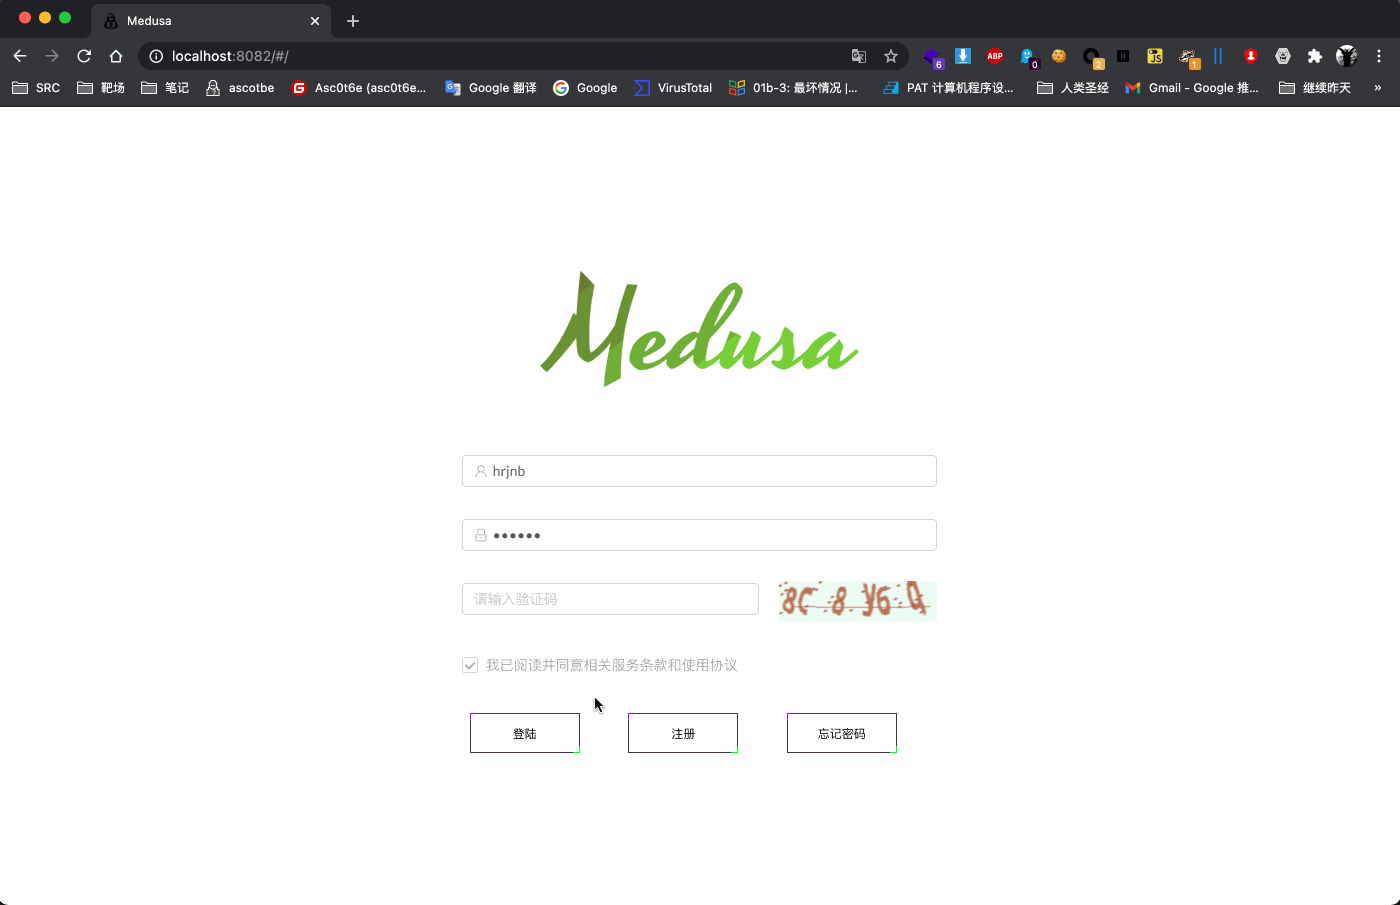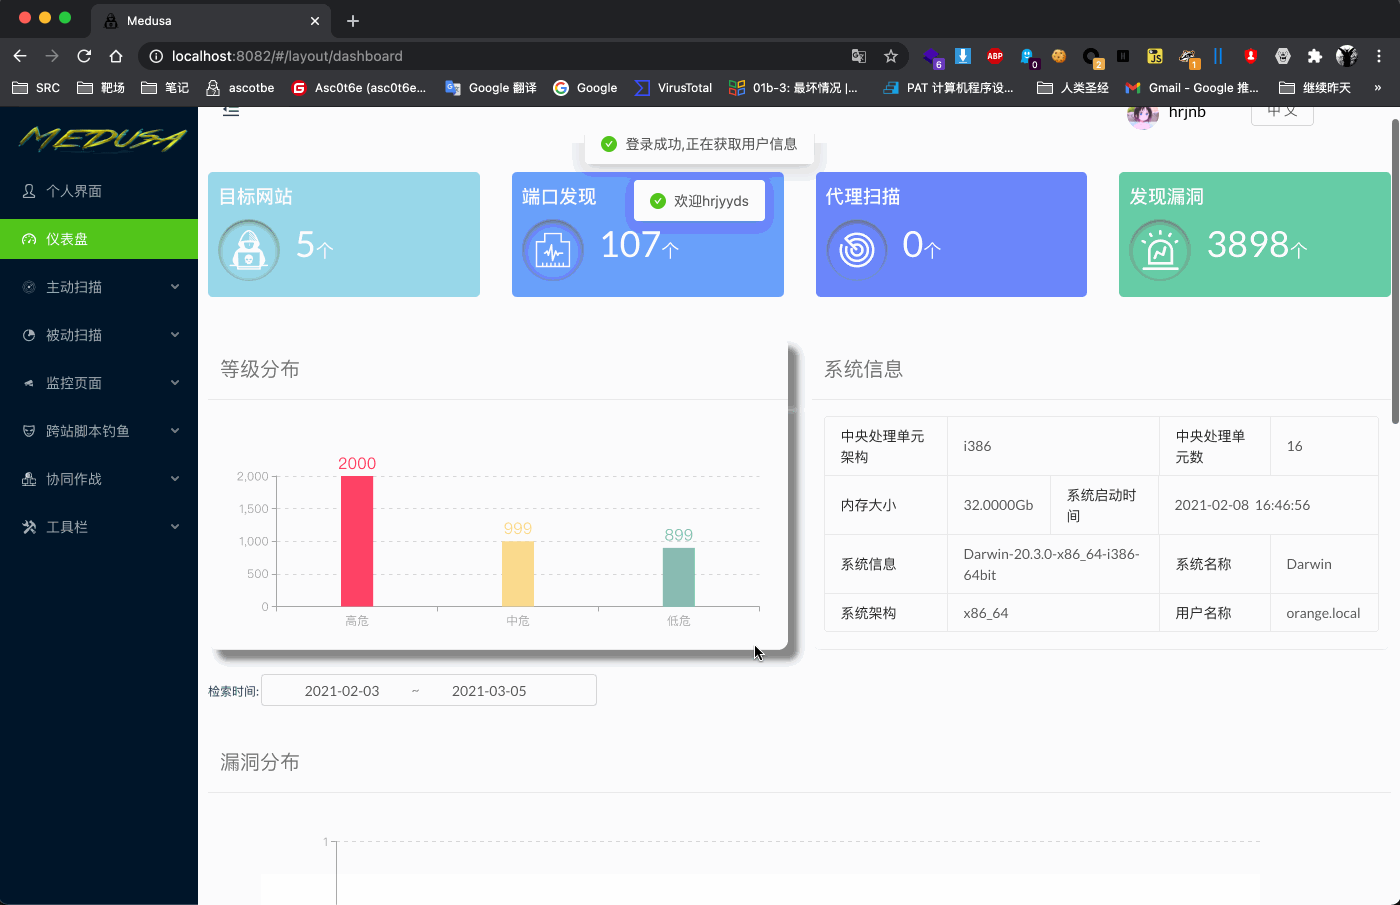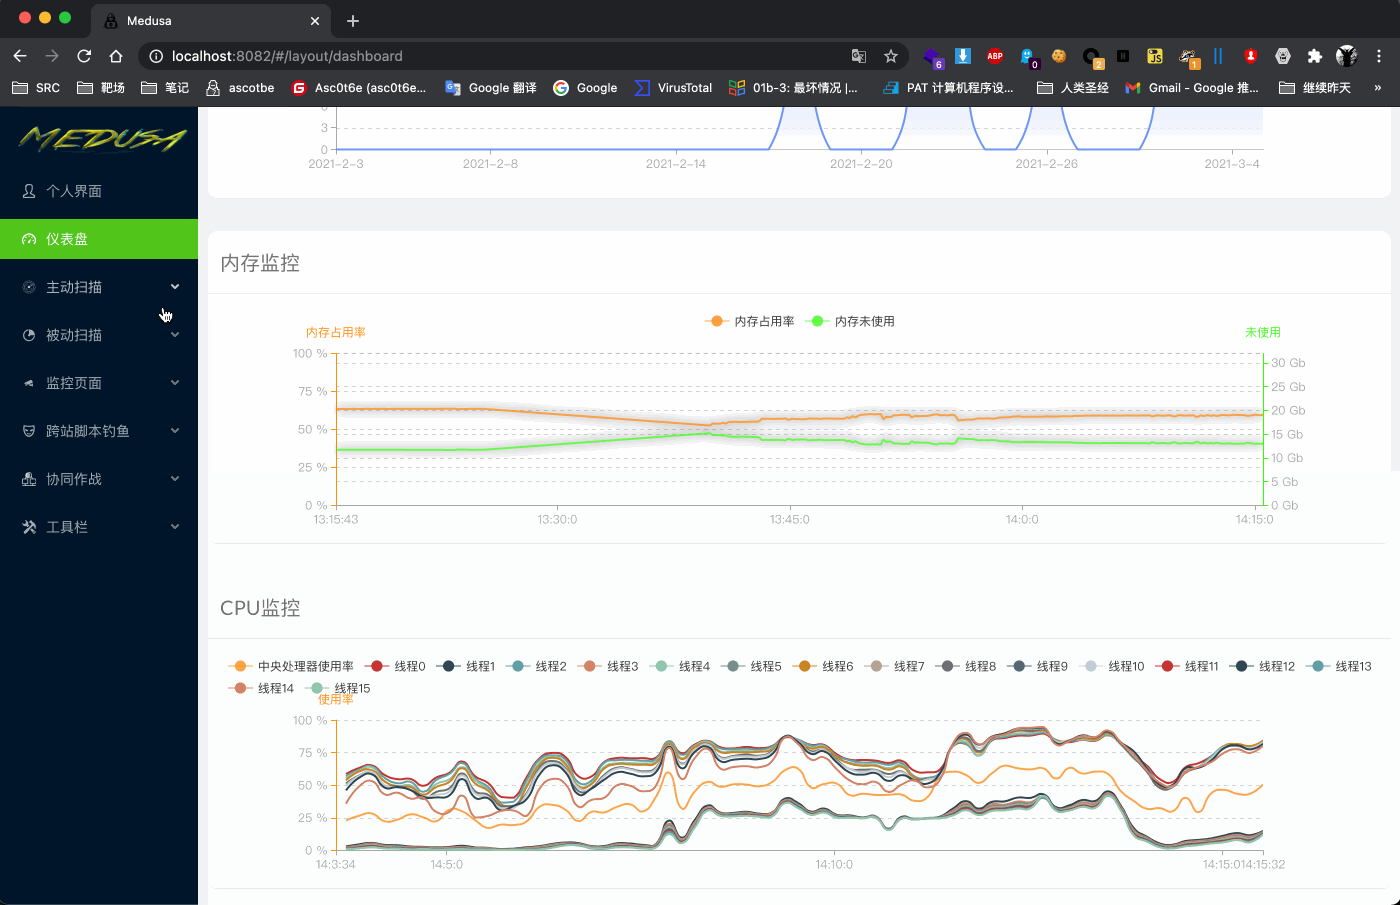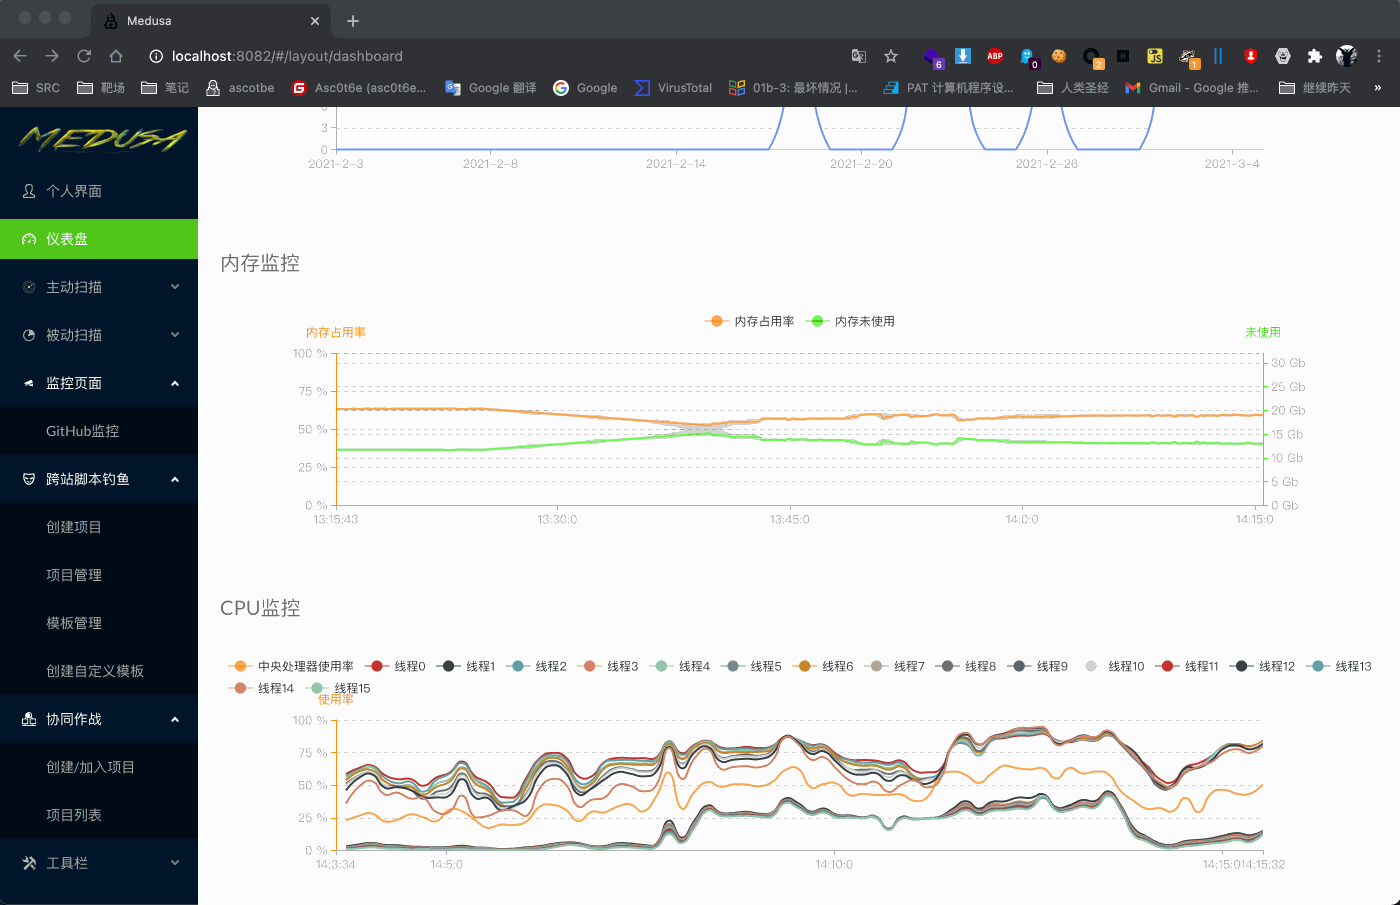 ascotbe/medusa
🐈Medusa是一个红队武器库平台,目前包括XSS平台、协同平台、CVE监控、免杀生成、DNSLOG、钓鱼邮件、文件获取等功能,持续开发中
 koutto/jok3r
Jok3r v3 BETA 2 - Network and Web Pentest Automation Framework
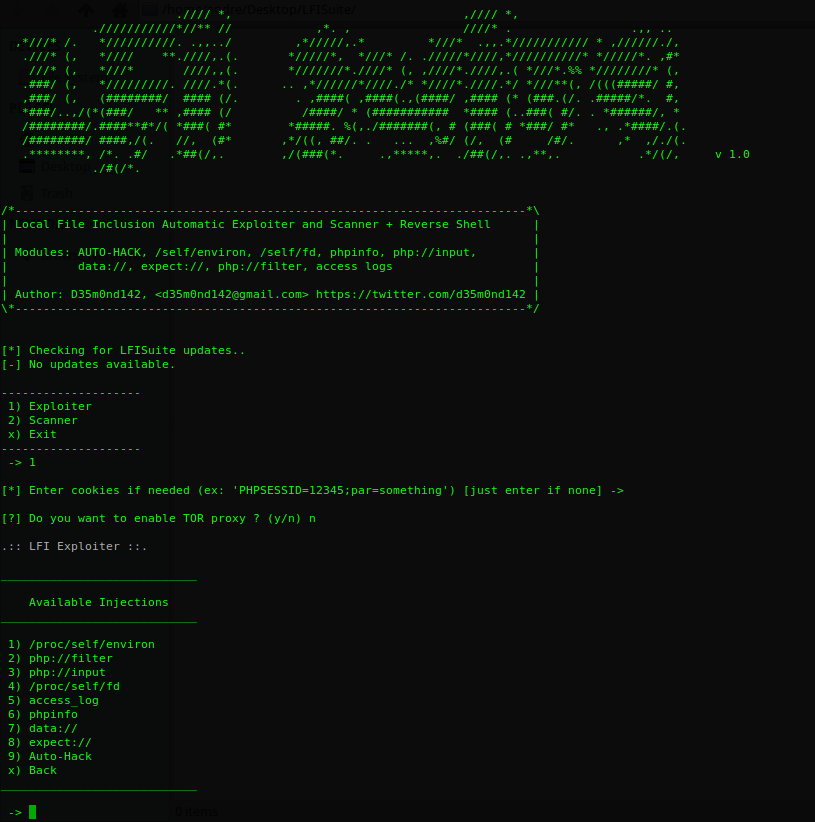 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…








