
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended

 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
 yasodginige/autopentester
This repository contains a tool that can be used for automated pentesting tasks.
 scriptingxss/embedos
EmbedOS - Embedded security testing virtual machine
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 thegejr/springshell
Spring4Shell - Spring Core RCE - CVE-2022-22965
 arinerron/heaptrace
helps visualize heap operations for pwn and debugging
 nomi-sec/nvd-exploit-list-ja
🔍NVD exploit & JVN(Japan Vulnerability Notes) easy description
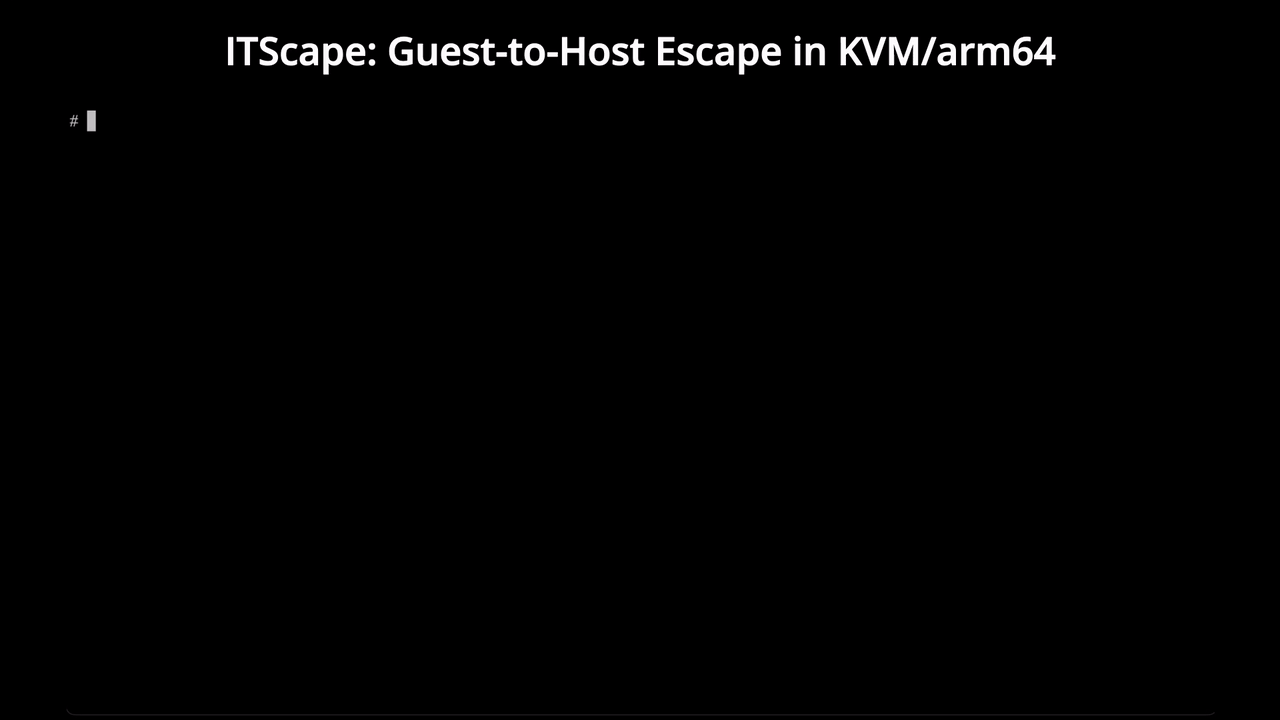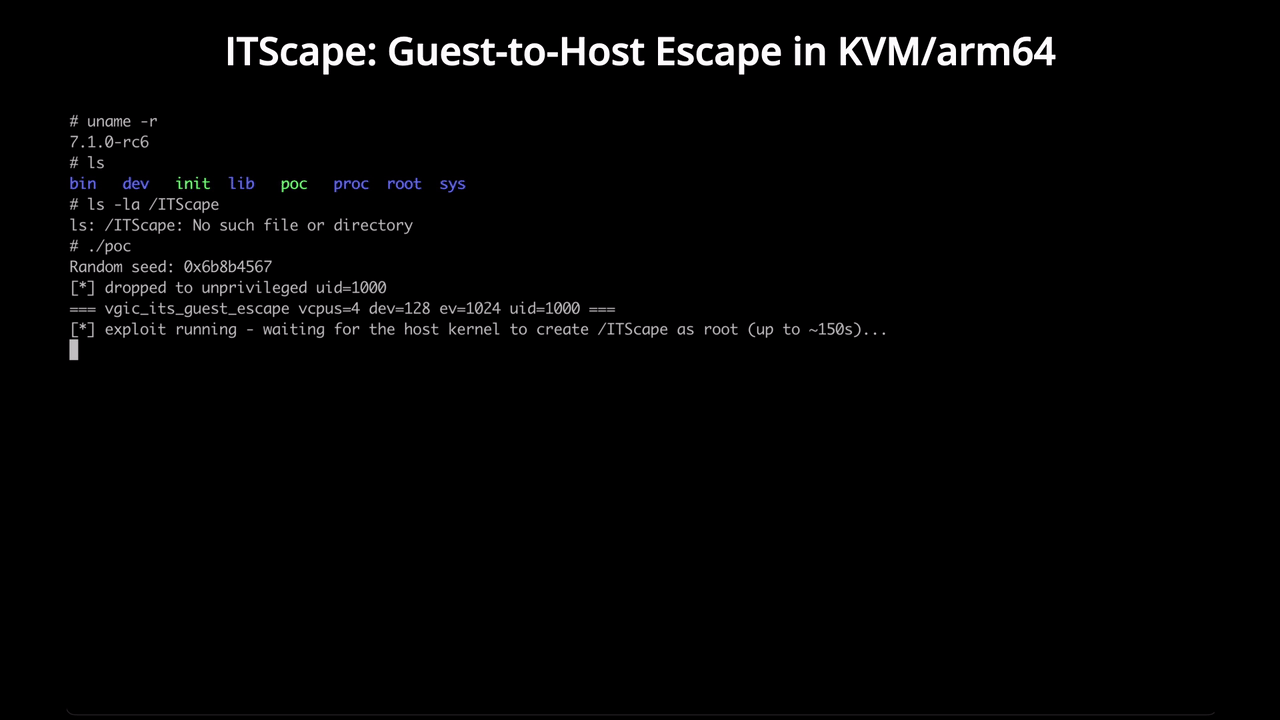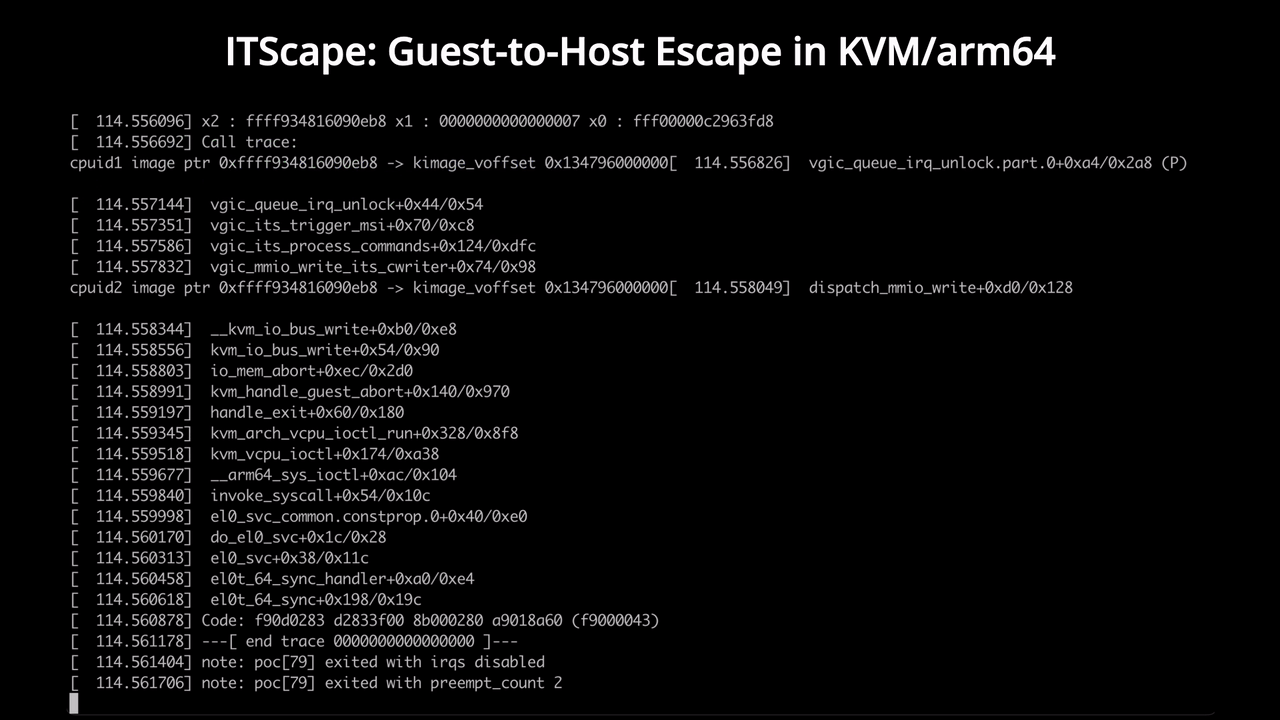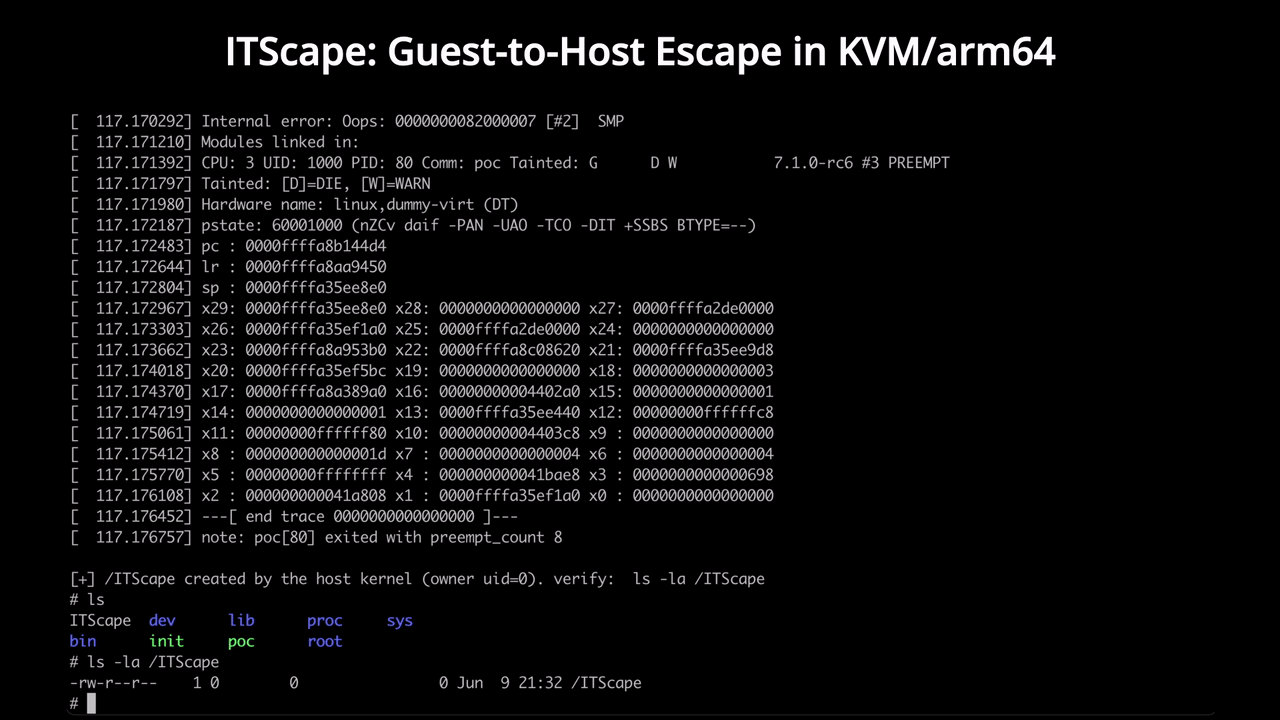 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 jenyraval/phishing-simulation
Phishing Simulation mainly aims to increase phishing awareness by providing an intuitive tutorial and customized assessment
 demonslay335/cryptotester
A utility for playing with cryptography, geared towards ransomware analysis.
 kn0x0x/cve-2025-32756-poc
Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products.
 vegabird/xvna
Extreme Vulnerable Node Application
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 g4sp4rcs/cve-2026-42980-poc
Public exploit and research material for CVE-2026-42980, a Windows kernel WMI integer-underflow vulnerability enabling local privilege escalation to…
 rub-softsec/onelogon
Code and data for our paper "Onelogon: Taking over Active Directory Accounts via Netlogon" (WOOT’26).








