
 #1
Cybersecurity research, materials, labs, and learning paths, including CTFs and curated educational resources.
Kitploit recommended
 owasp/agentic-evidence
OWASP reference project for agentic AI security evidence: correlates agent execution, identity, tool calls, and authorization decisions into…
 owasp/robotics-security-testing-guide
OWASP guide defining a standardized penetration testing methodology for humanoid, industrial, and autonomous robots, covering ROS/ROS2, DDS, CAN bus,…
 owasp/the-agents-epistemic-baggage
An audit-oriented risk model for how agent-generated inferences can change epistemic status, gain operational authority, and influence later…
 abraxas/php-oom-longjmp
PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…
 abraxas/php-stale-global-uaf
PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…
 k0keoyo/ssctf-pwn450-ms16-034-writeup
Writeup of an SSCTF pwn450 challenge covering Windows kernel exploitation of MS16-034, including vulnerability analysis and privilege escalation…
 eqstlab/cve-2026-109619
Proof-of-concept exploit for PHP session.upload_progress pre-auth RCE (PHP2Shell), with heap/ASLR leak, per-build offset profiles, and an all-in-one…
 gmh5225/obs-graphics-hook32-hook
Demonstrates hooking OBS graphics-hook32.dll's D3D9 Present pointer to achieve stream-proof rendering that evades anti-cheat game capture detection.
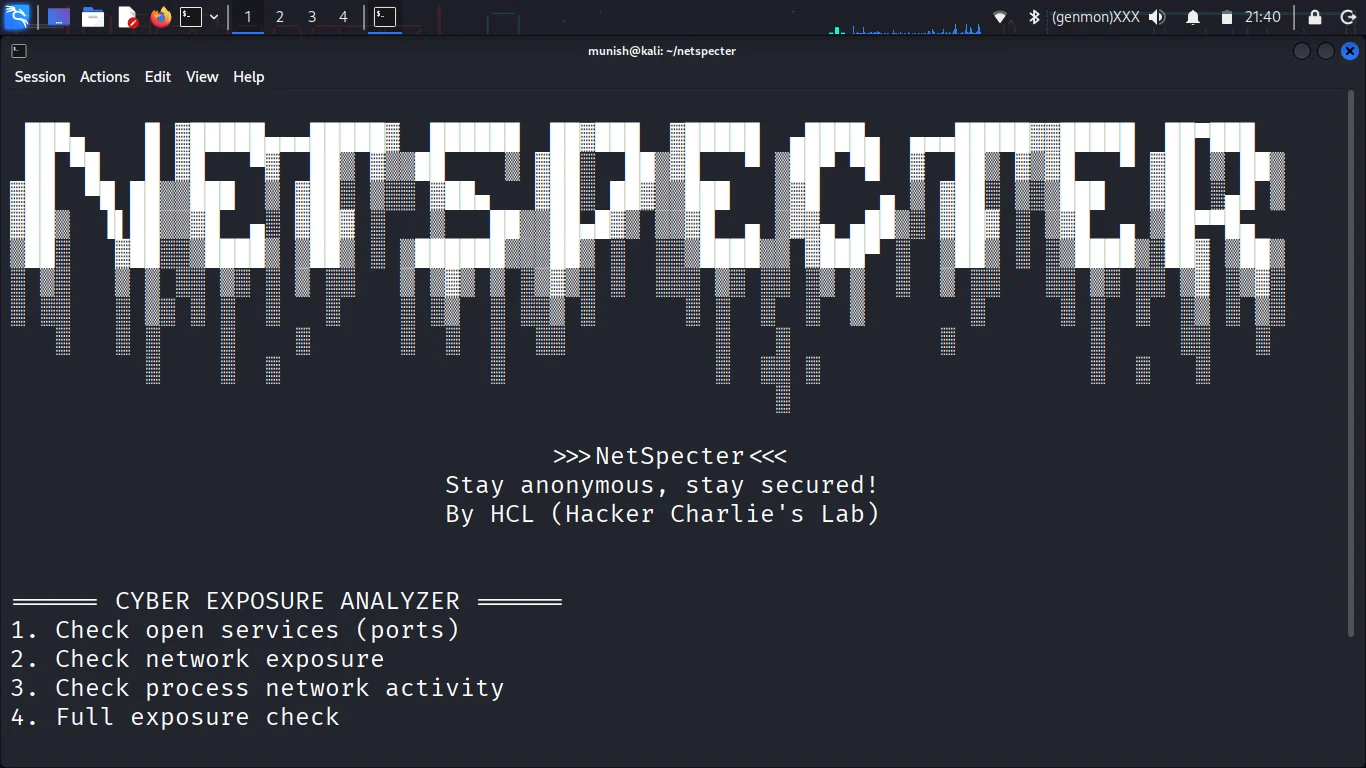 mrhackercharlie/netspecter
Real-time system monitoring tool for detecting process activity and network exposure!
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 thezdi/poc
Collection of proof-of-concept exploits and vulnerability research artifacts published by Trend Micro's Zero Day Initiative, covering SCADA, RPC, and…
 1llu50ry/mcp-gamehacking
MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 suels-group/beyond_asr
Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 bitcoindatalabs/ln-upgrade-dynamics
Code, aggregate data and LaTeX source for 'Who Patches the Lightning Network? Release Lines from Gossip, Node Platforms and Security Advisories,…








