
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended

 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
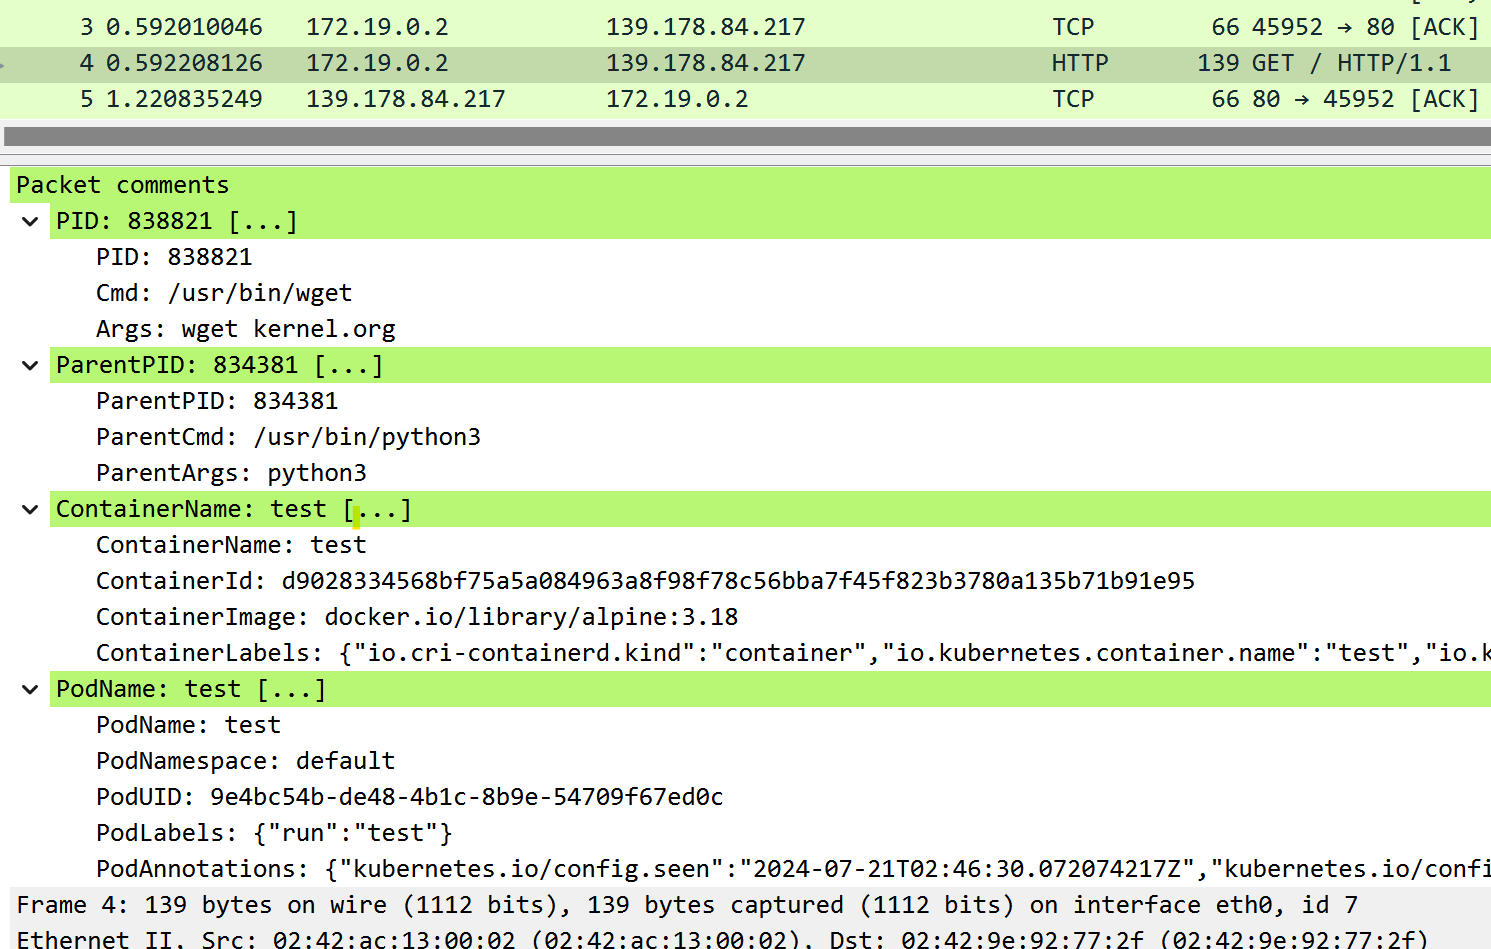 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
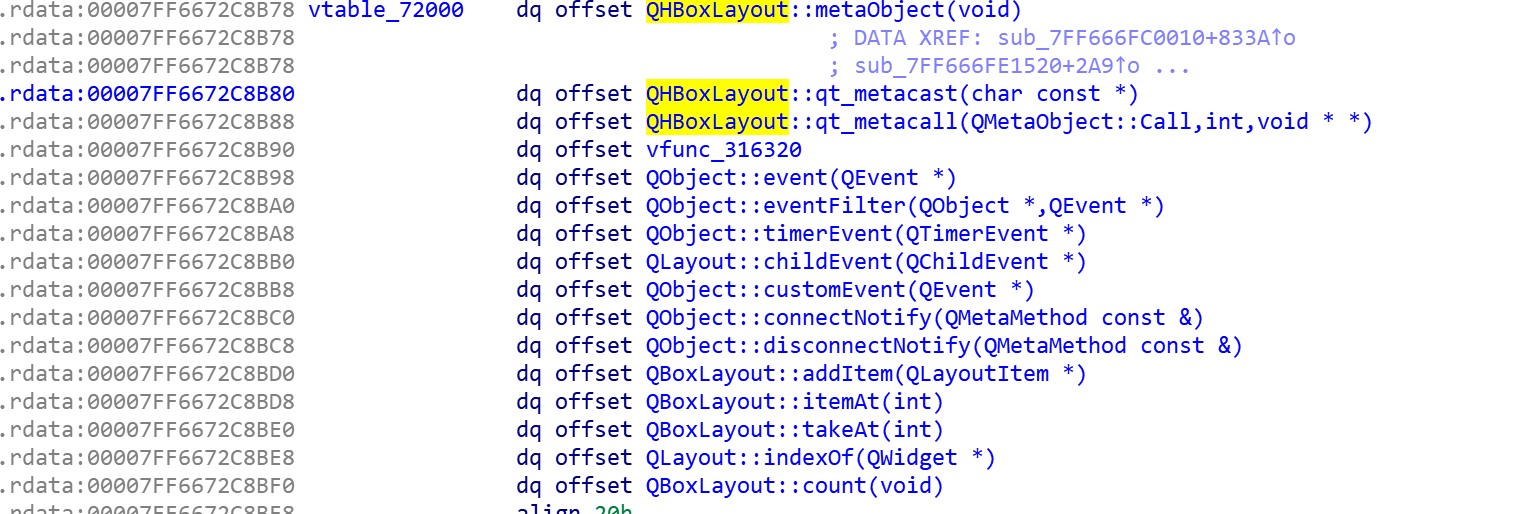 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
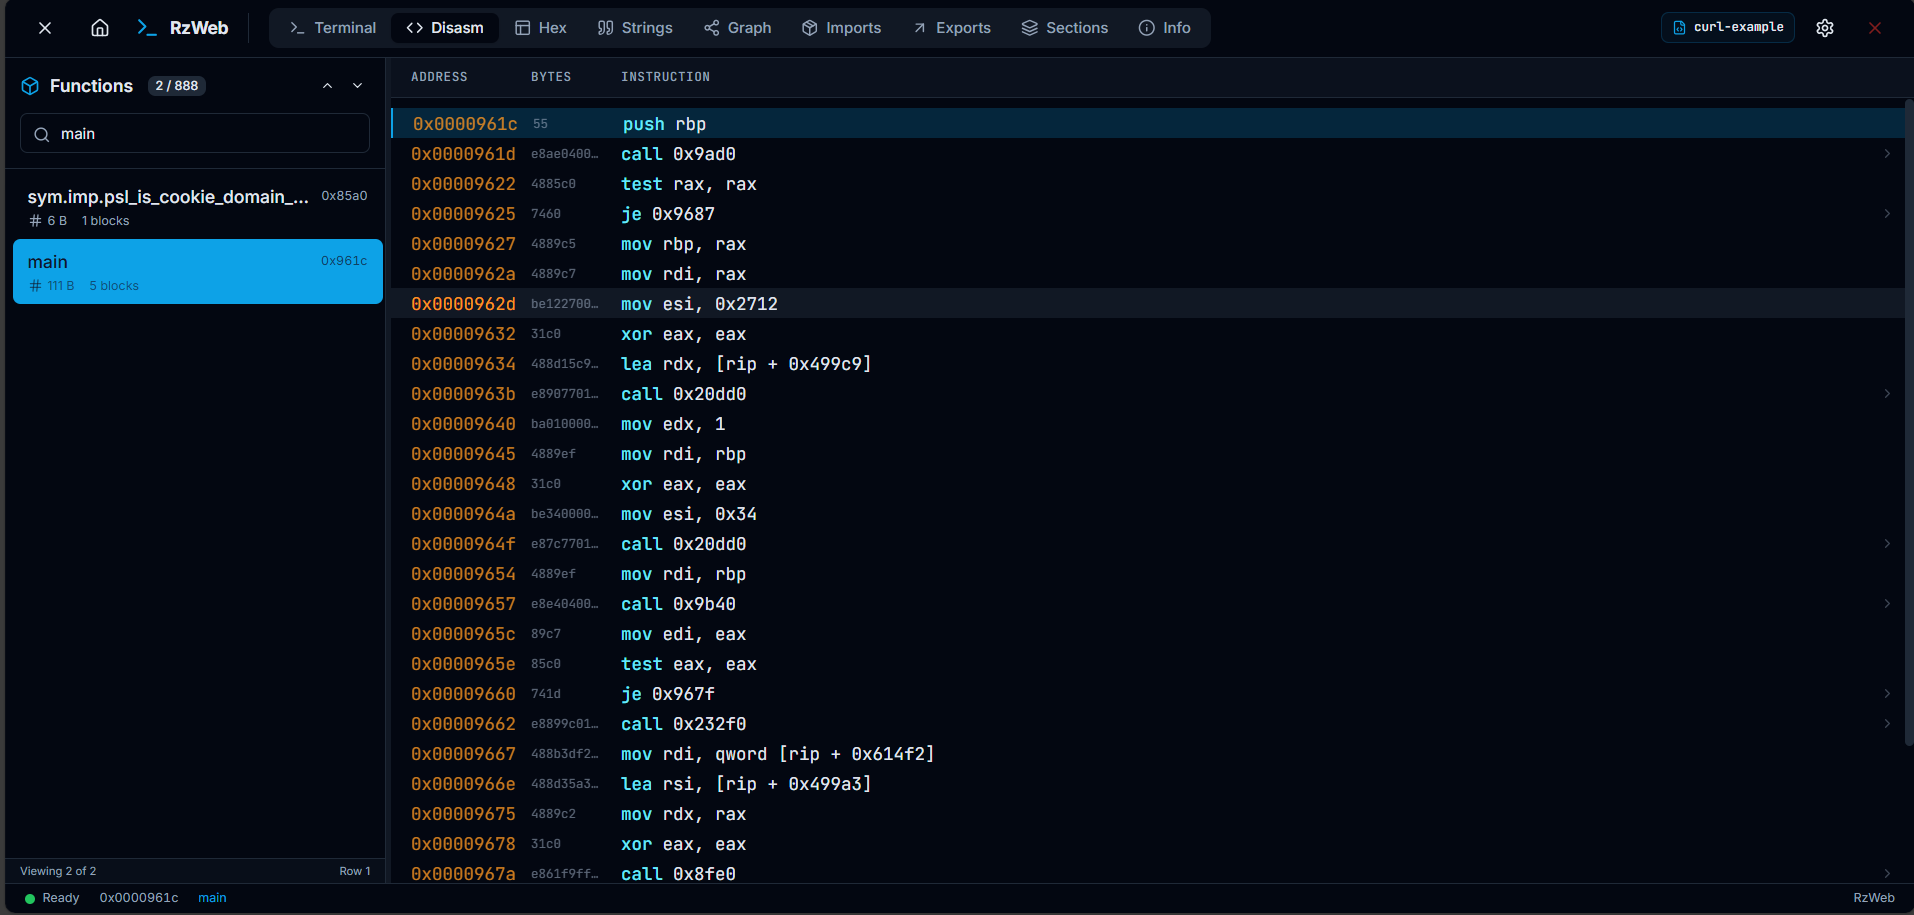 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 darthton/hyperbone
Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.
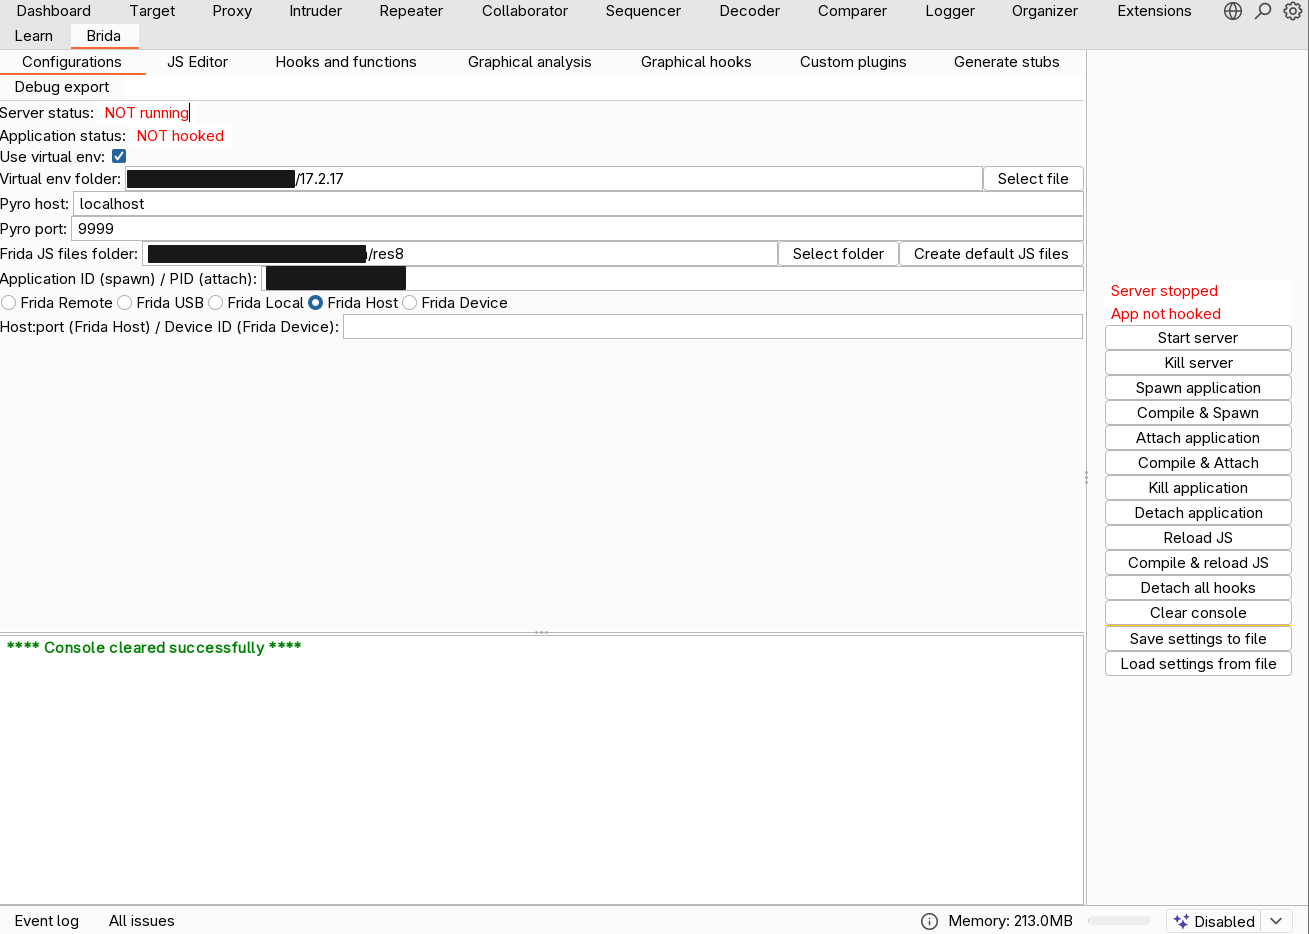 federicodotta/brida
The new bridge between Burp Suite and Frida!
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 openrce/sulley
A pure-python fully automated and unattended fuzzing framework.
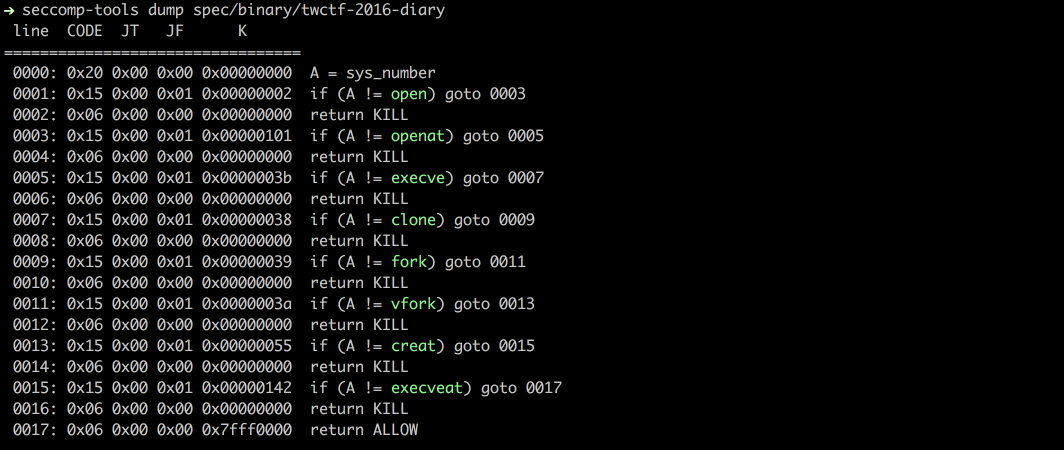 david942j/seccomp-tools
Provide powerful tools for seccomp analysis
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering








