
 #2
Tools for observing malware behavior in isolated environments to understand its actions and impact.
Kitploit recommended

 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 nowsecure/r2frida
Radare2 and Frida better together.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 ax/apk.sh
Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.

 gmh5225/awesome-llvm-security
Curated collection of LLVM security resources covering binary lifting, code obfuscation, static analysis, symbolic execution, sanitizers, and…
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
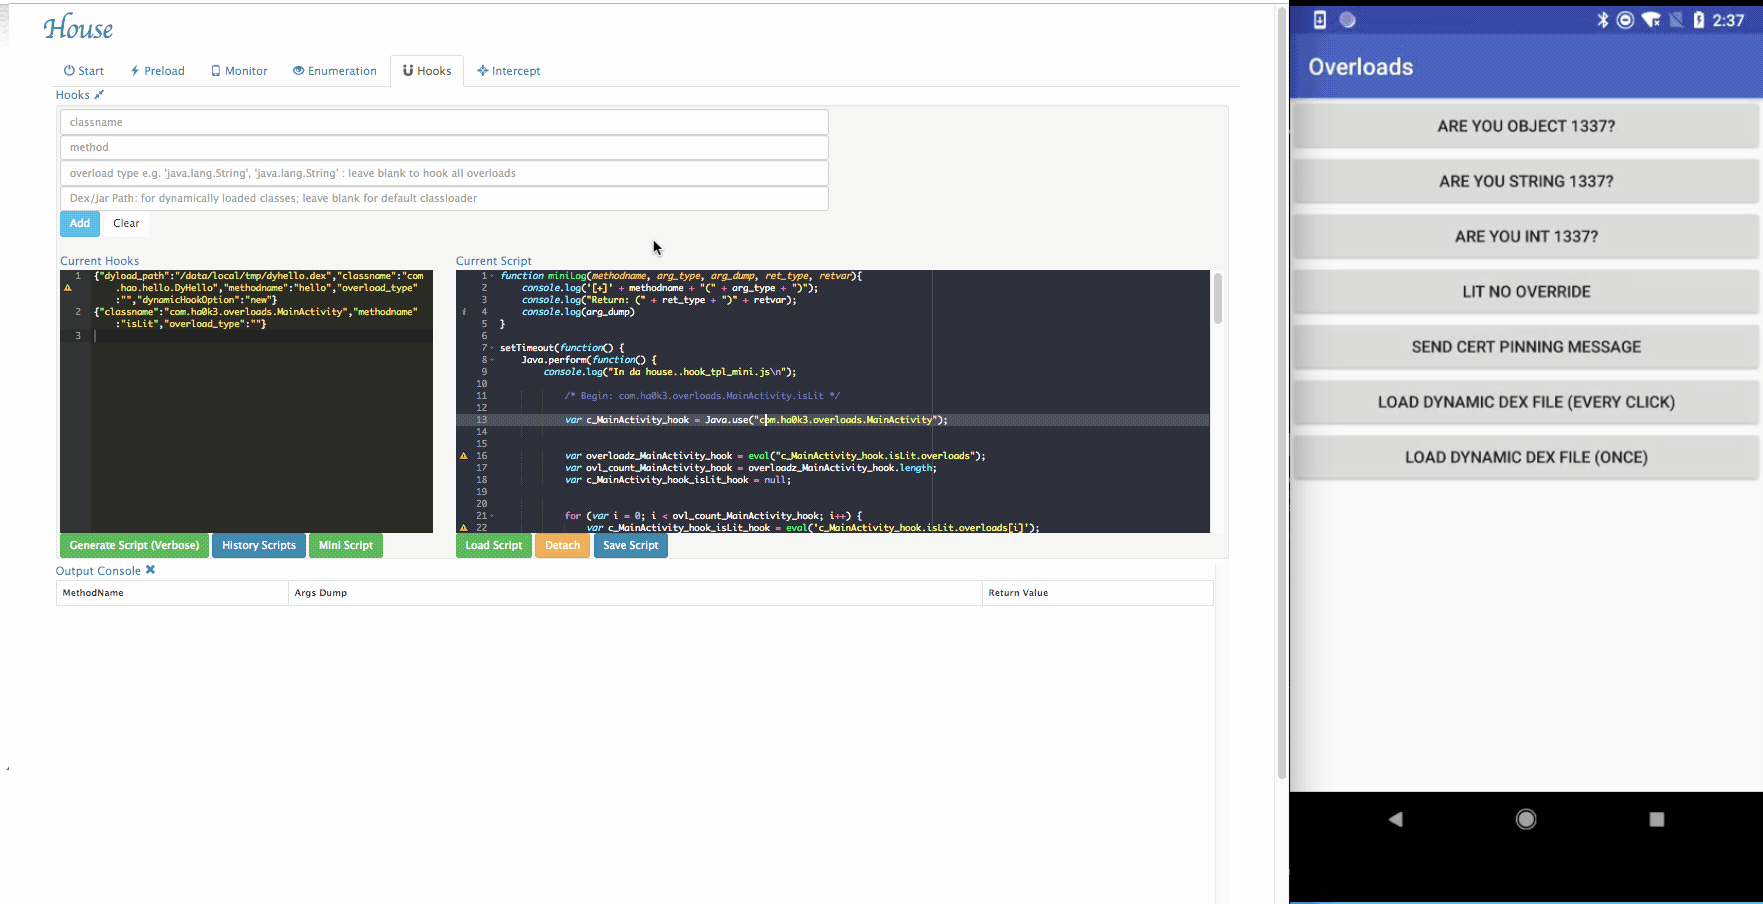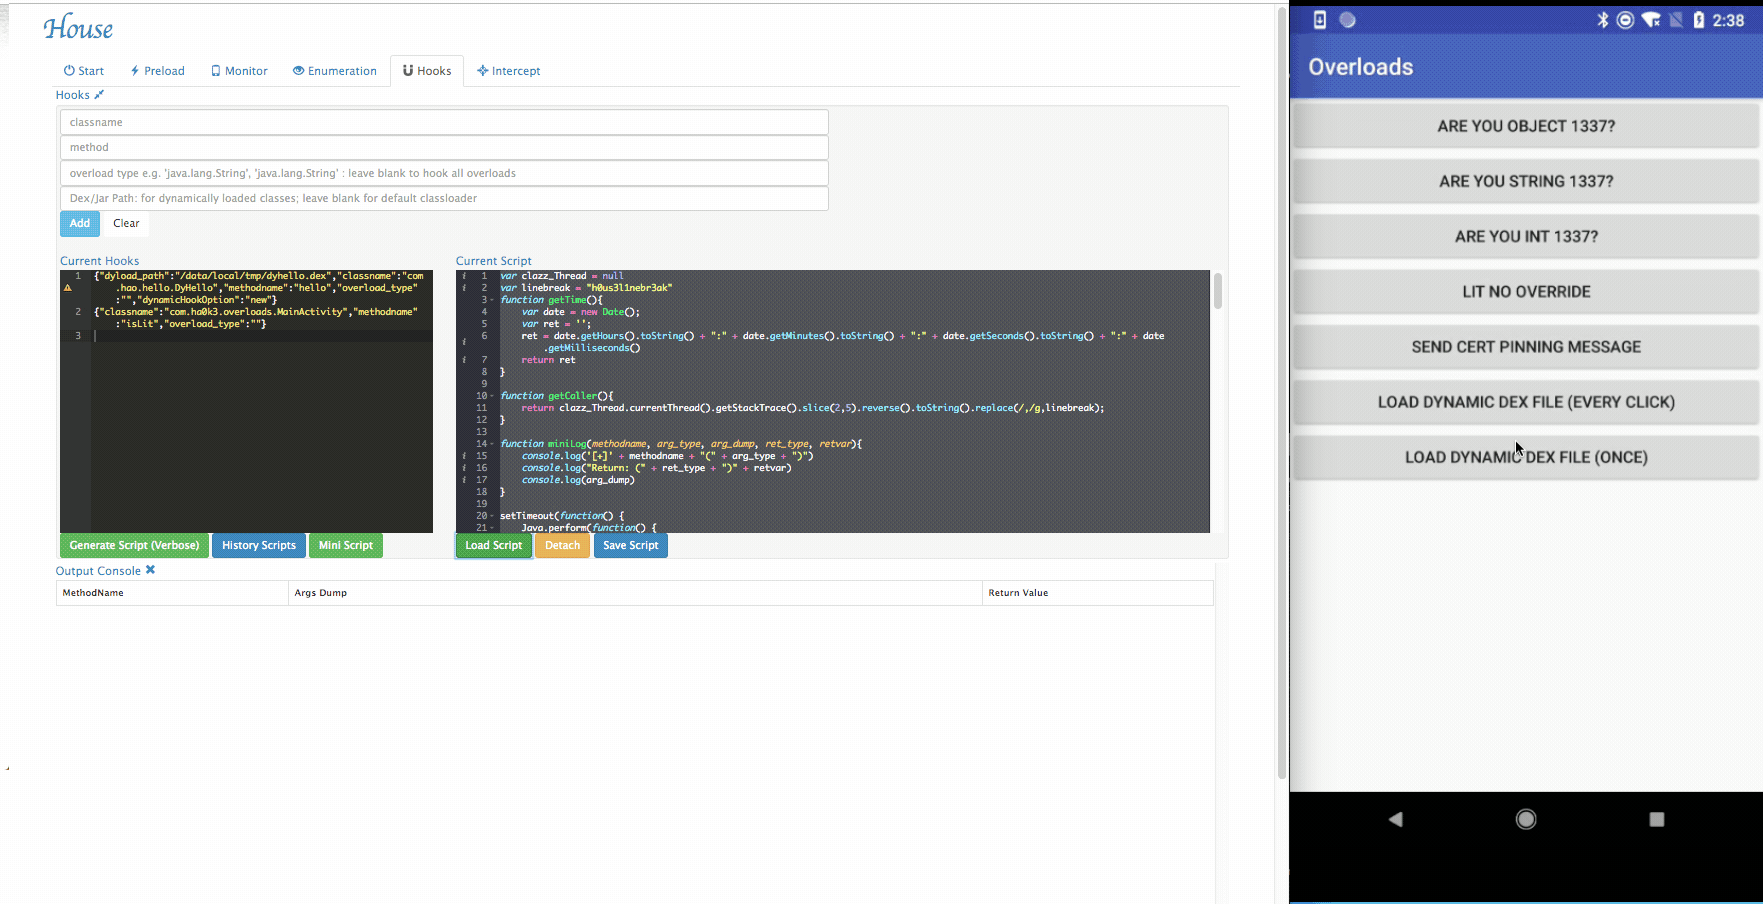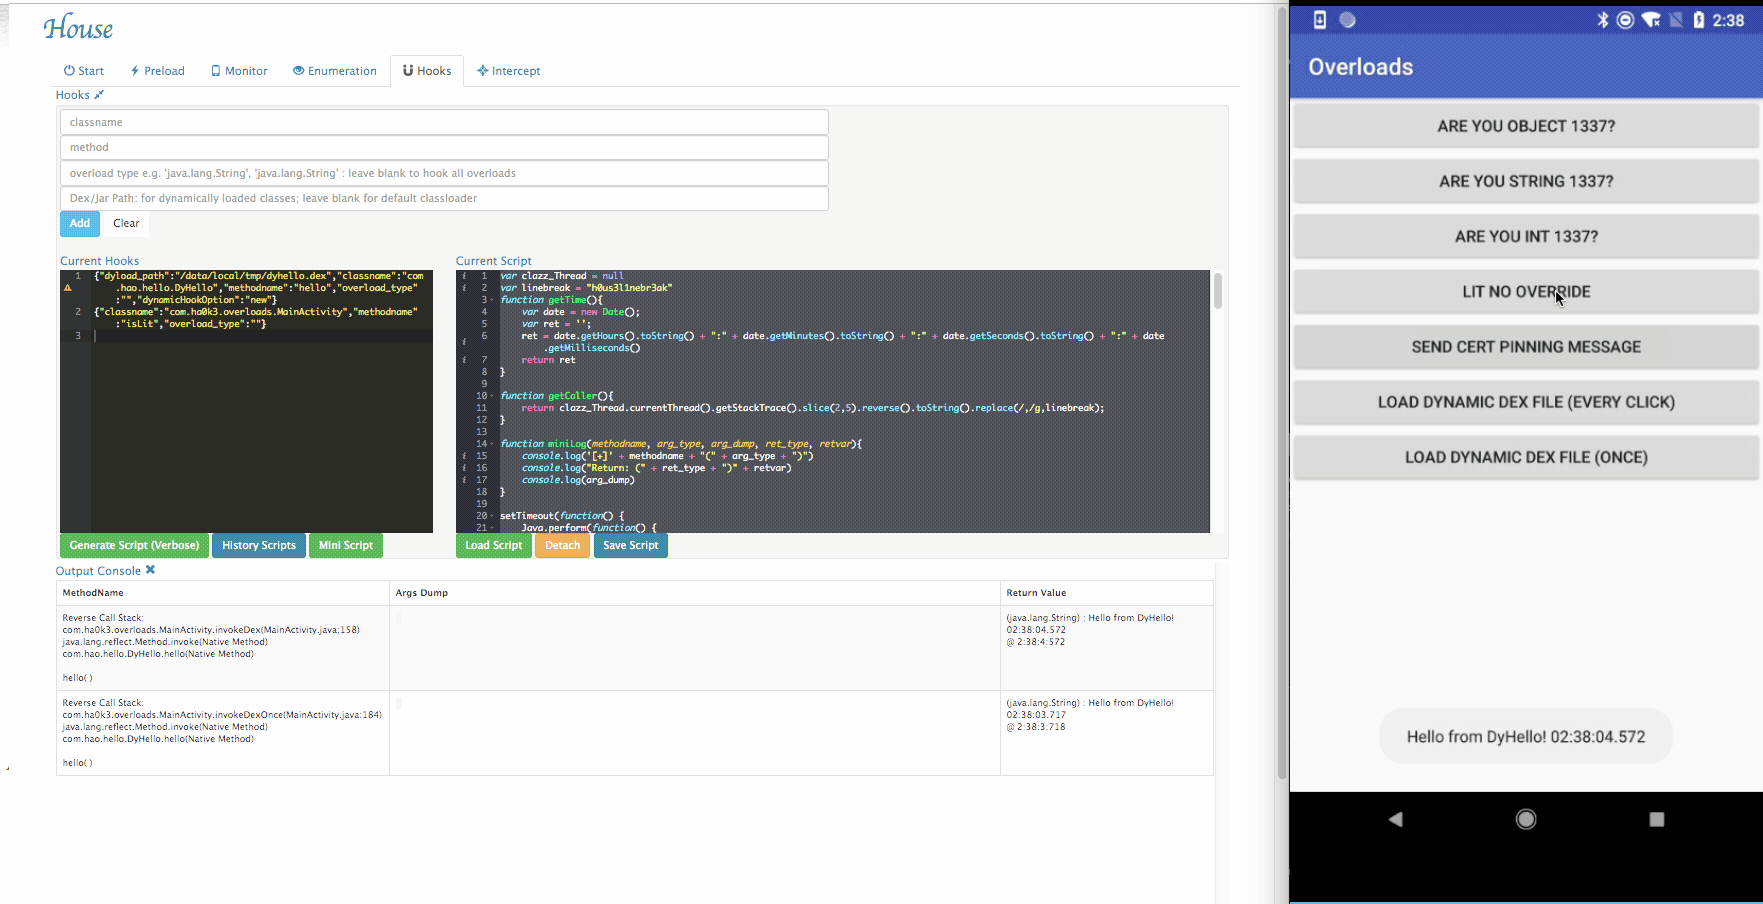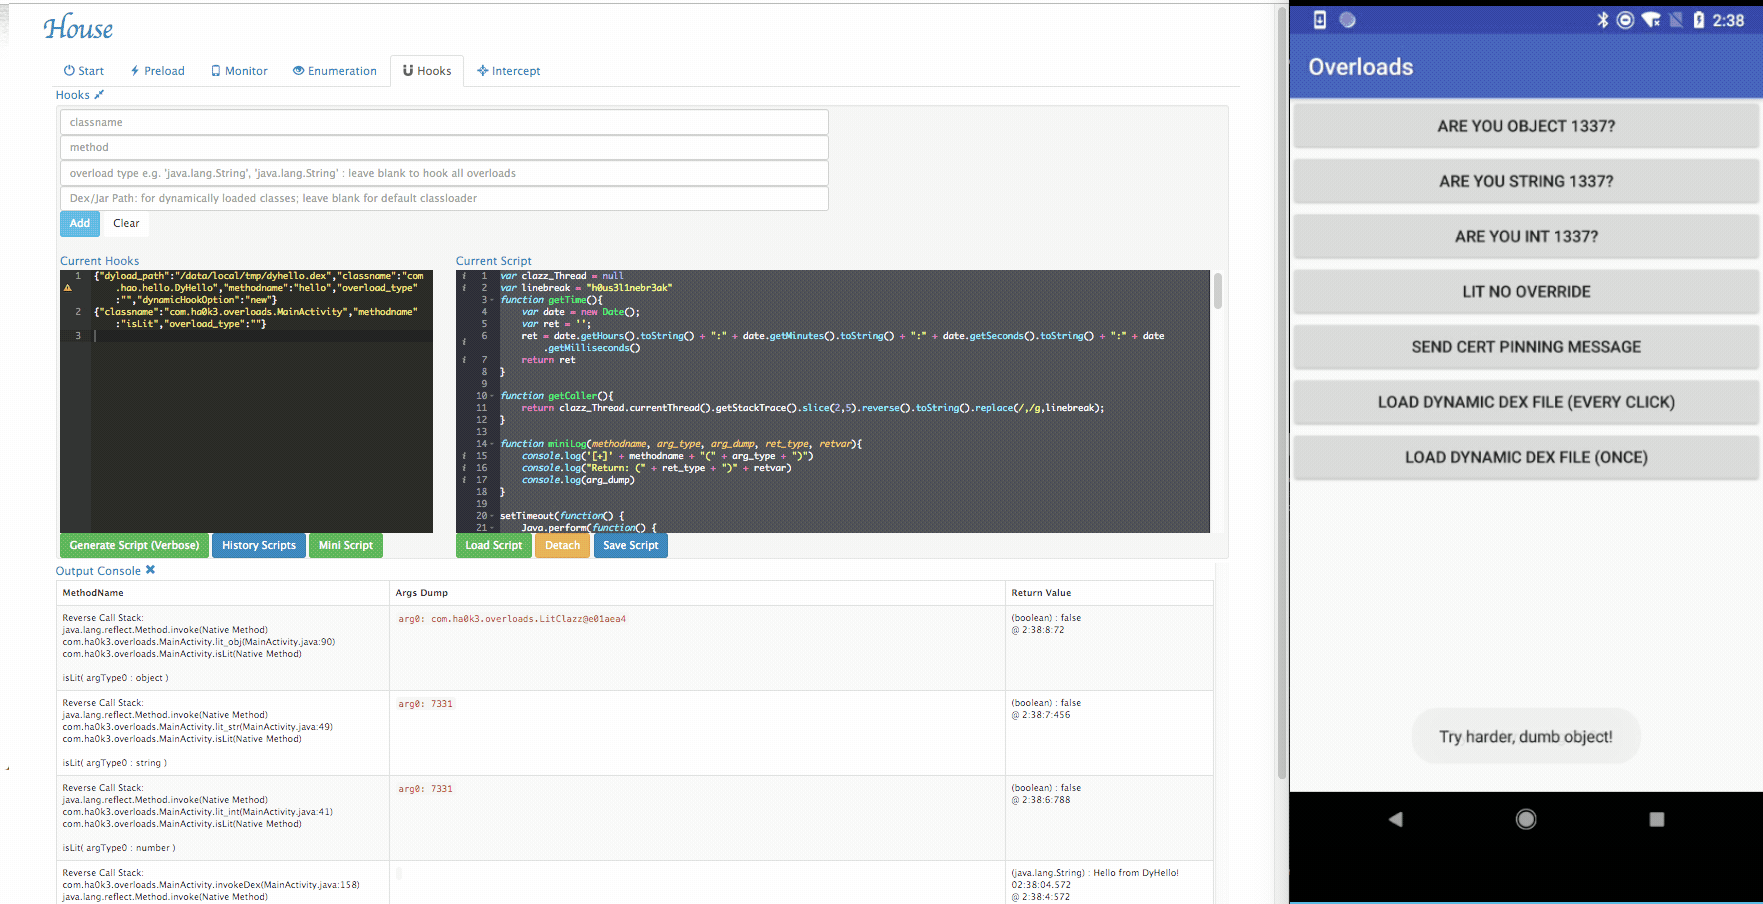 nccgroup/house
A runtime mobile application analysis toolkit with a Web GUI, powered by Frida, written in Python.
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…







